AnyDesk405 AnyPwn: AnyDesk Linux 8.0.2 Pre-auth Heap Overflow RCE
AnyPwn is a pre-approval remote code execution bug in AnyDesk Linux 8.0.2. The session protocol's mode-5 handler trusts a remote payload length,…
AnyDesk405 AnyPwn is a pre-approval remote code execution bug in AnyDesk Linux 8.0.2. The session protocol's mode-5 handler trusts a remote payload length,…
kernel1.1k Asim Manizada’s four Linux LPEs: DirtyAH6, TUNderflow, PPPoEject, DiagSpill. Decade-old bugs, userns for three, DiagSpill needs only SCTP. Patch 5.10.270 / 6.6.157…
Exploit Development790 USENIX Security 2026: KERAT mines atomicity rules for check-use pairs on Linux and FreeBSD shared fields, then FSM-walks LLVM IR. 351 real…
Linux499 How Singularity rootkit bypasses Elastic Defend 9.5's enhanced module load detection through source obfuscation, BPF hook manipulation, and exploitation of trusted process…
Exploit Development711 CVE-2026-53360 is a heap out-of-bounds read/write in KVM SEV-SNP Page State Change handler: the guest picks the scratch buffer size, the host…
Exploit Development982 Two nginx rewrite-engine bugs share one root cause: an is_args flag computed in one pass and consumed in another. Pointed at r->args…
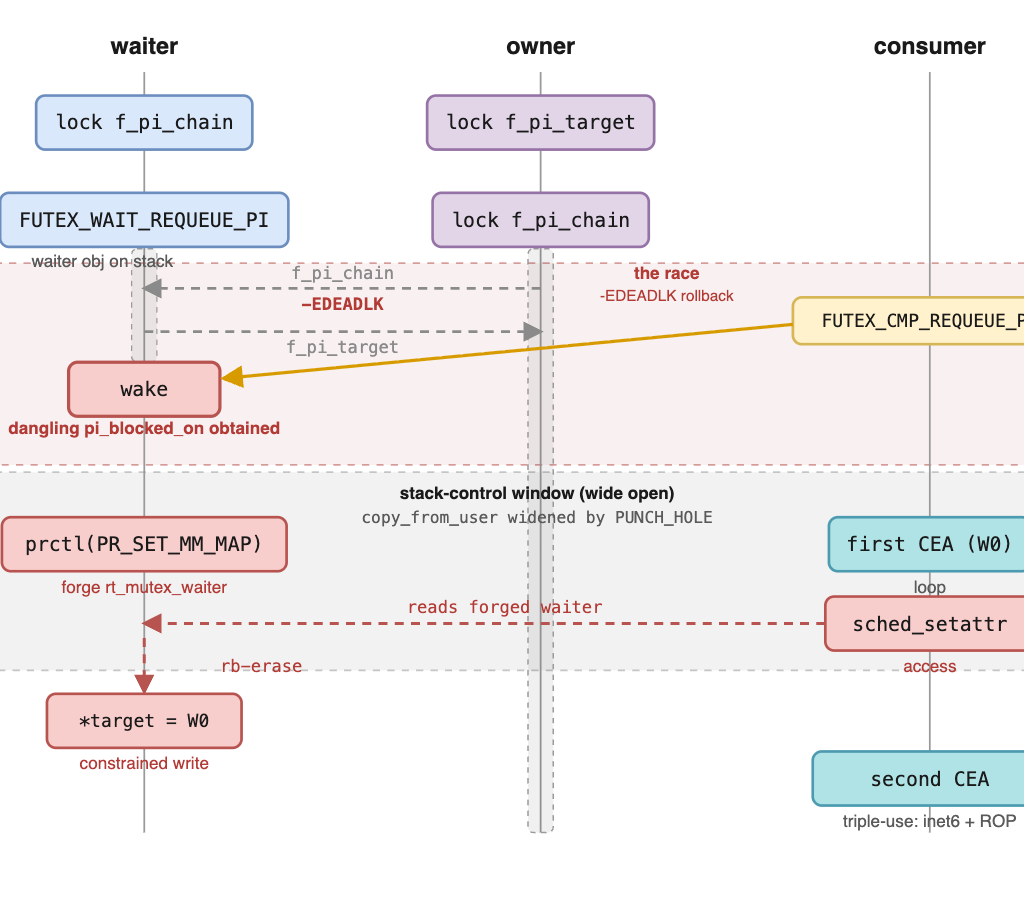
Exploit Development1.5k GhostLock (CVE-2026-43499) is a 15-year-old use-after-free in the Linux kernel's rtmutex/futex requeue-PI code. When a proxy lock hits a deadlock and rolls…
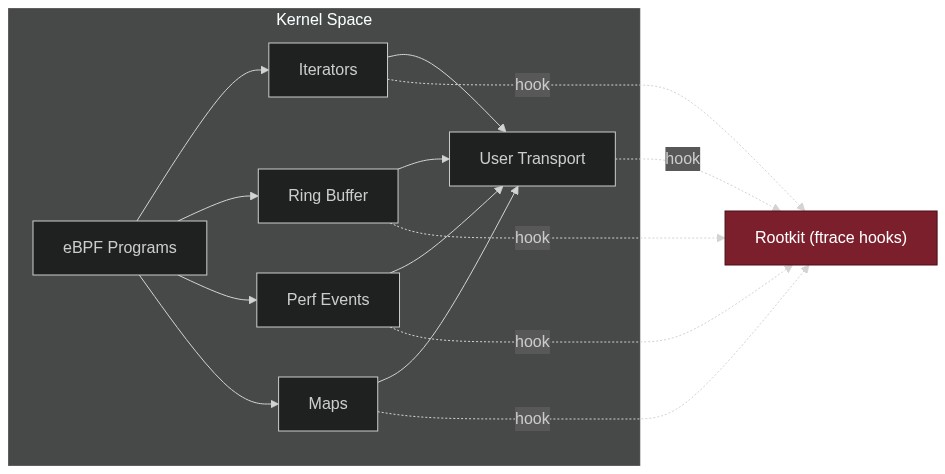
Linux665 A kernel rootkit using ftrace hooks can selectively blind Falco, Tracee, GhostScan, and Decloaker simultaneously by intercepting the BPF iterator, ringbuffer, perf…
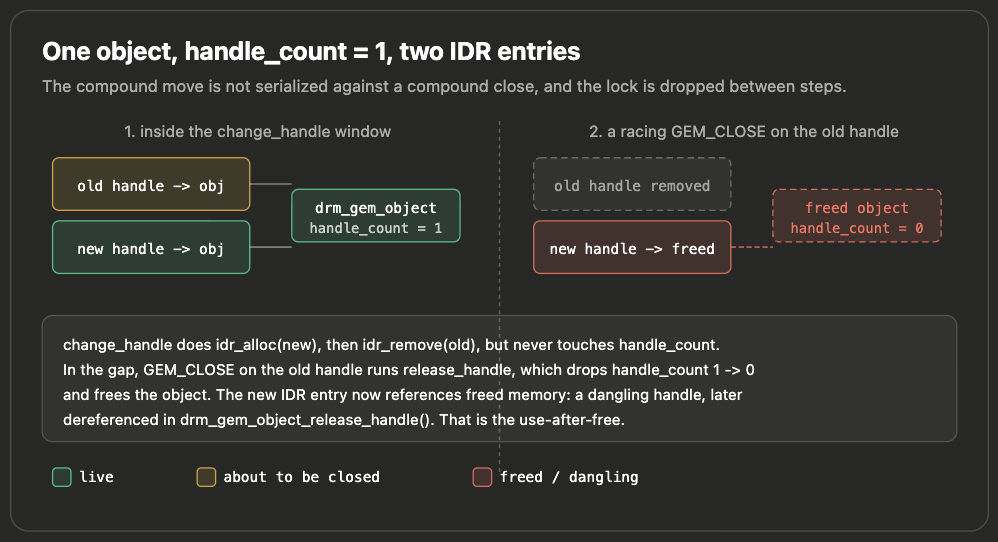
Linux521 CVE-2026-46215 is a use-after-free race in the Linux DRM GEM change_handle ioctl (v6.8–v6.14-rc2) that allows unprivileged LPE to root via pipe_buffer slab…
Linux603 Pack2TheRoot (CVE-2026-41651) is a high-severity local privilege escalation flaw in PackageKit that lets any unprivileged user win a race condition during InstallFiles…
Exploit Development574 DirtyClone (CVE-2026-43503) is a high-severity Linux LPE in the DirtyFrag family. A dropped SKBFL_SHARED_FRAG flag during __pskb_copy_fclone() skb cloning lets in-place IPsec…
Containers557 A deep technical walkthrough of ipv6_frag_escape, a public proof-of-concept exploit that converts a Linux kernel IPv6 fragmentation linear overflow into a reliable…