
 Active Directory114
Domain Credential Dumping via File Handle Redirection
S12 points a notepad.exe File handle at ntds.dit, SYSTEM, and SECURITY on a live DC via BYOVD LowQword patch. No LSASS, no…
oxfemale·
Sep 14·
15 min
·114
Active Directory114 S12 points a notepad.exe File handle at ntds.dit, SYSTEM, and SECURITY on a live DC via BYOVD LowQword patch. No LSASS, no…
 Active Directory178
Hope Walker's SpecterOps sequel to manual LDAP querying: OR parentheses that lie, nested Domain Admins, Kerberoastable SPNs, userAccountControl sticker-math, passwords in schema…
 Active Directory140
When BloodHound and PowerView will not load, Active Directory is still a phone book. Hope Walker's SpecterOps lab shows how to query…
 Active Directory382
Demonstrate a sophisticated privilege escalation technique exploiting Windows IIS AppPool identity elevation to obtain machine account certificates from AD CS, leading to…
 Active Directory521
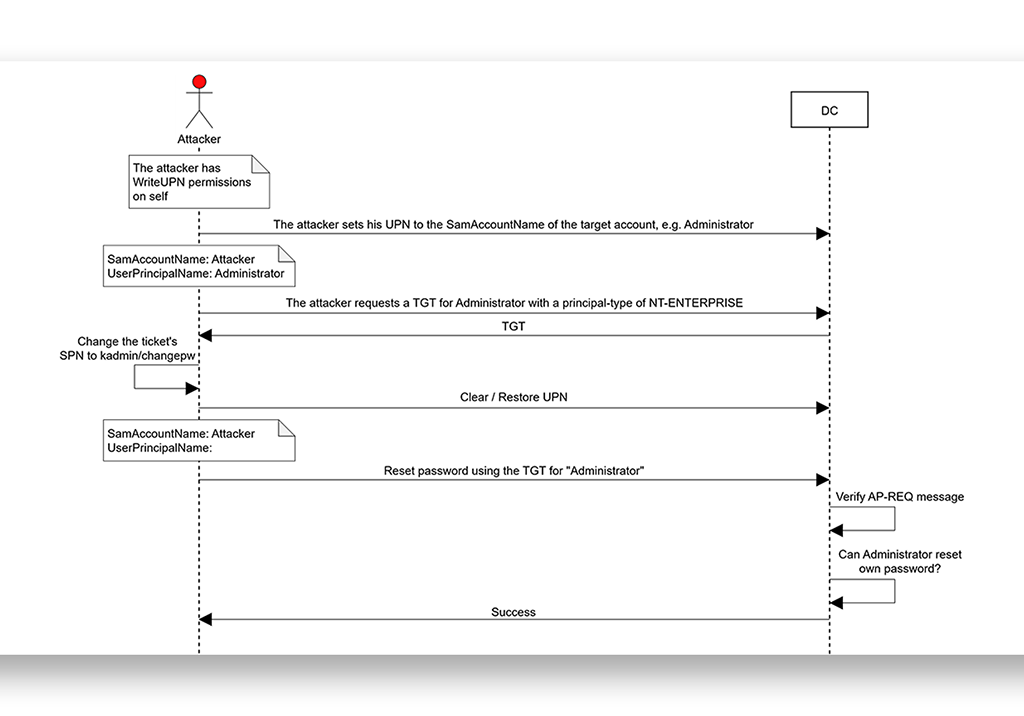
Active Directory stores Unicode characters its own LDAP server cannot search for. Semperis researcher Shai Laron turned that gap into KerberLoss (CVE-2026-25177)…
 Active Directory220
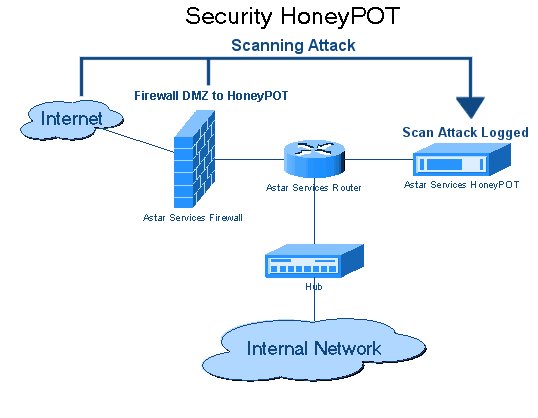
Decoy accounts in Active Directory look legitimate at the schema level but cannot fake behavioural history. This walkthrough shows how to read…
 Active Directory346
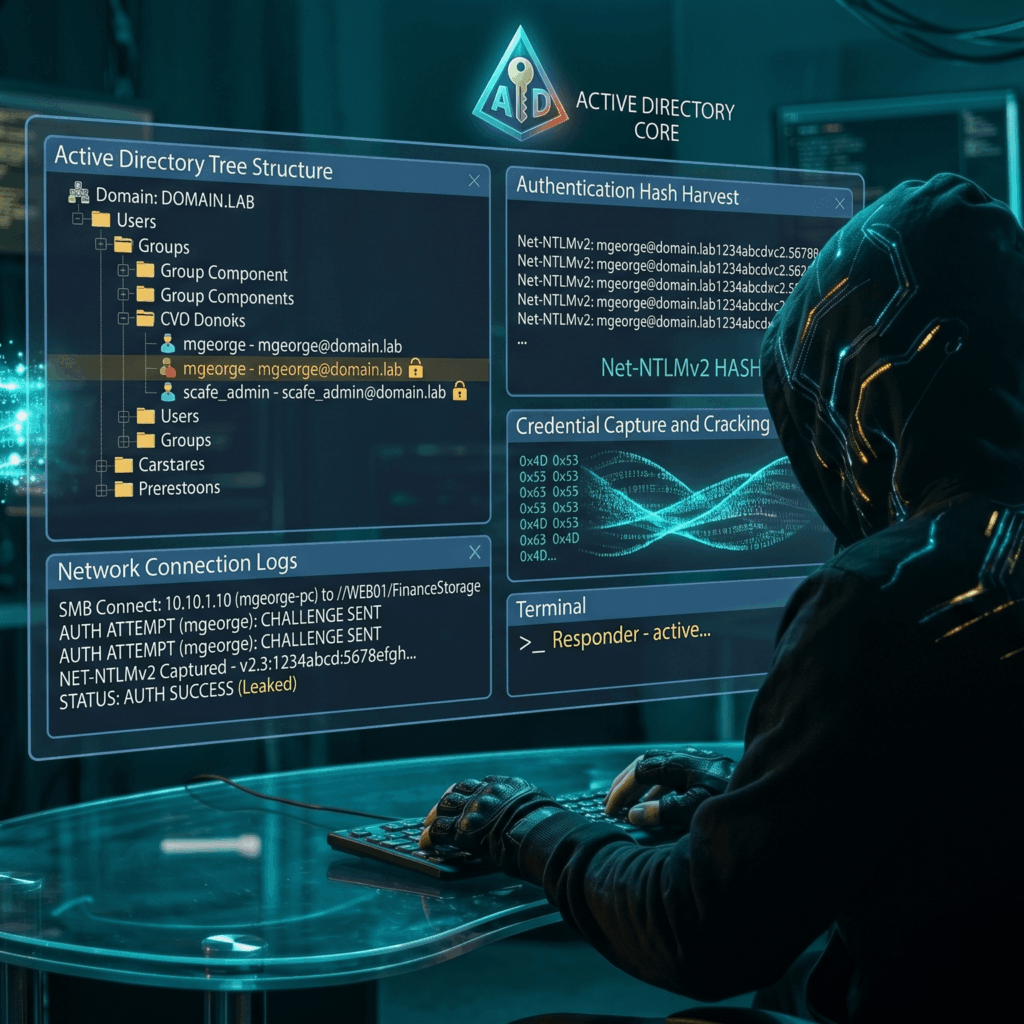
A walkthrough of a classic-but-still-effective Active Directory attack: how write access to an SMB share — plus a single .lnk file —…
 Active Directory176
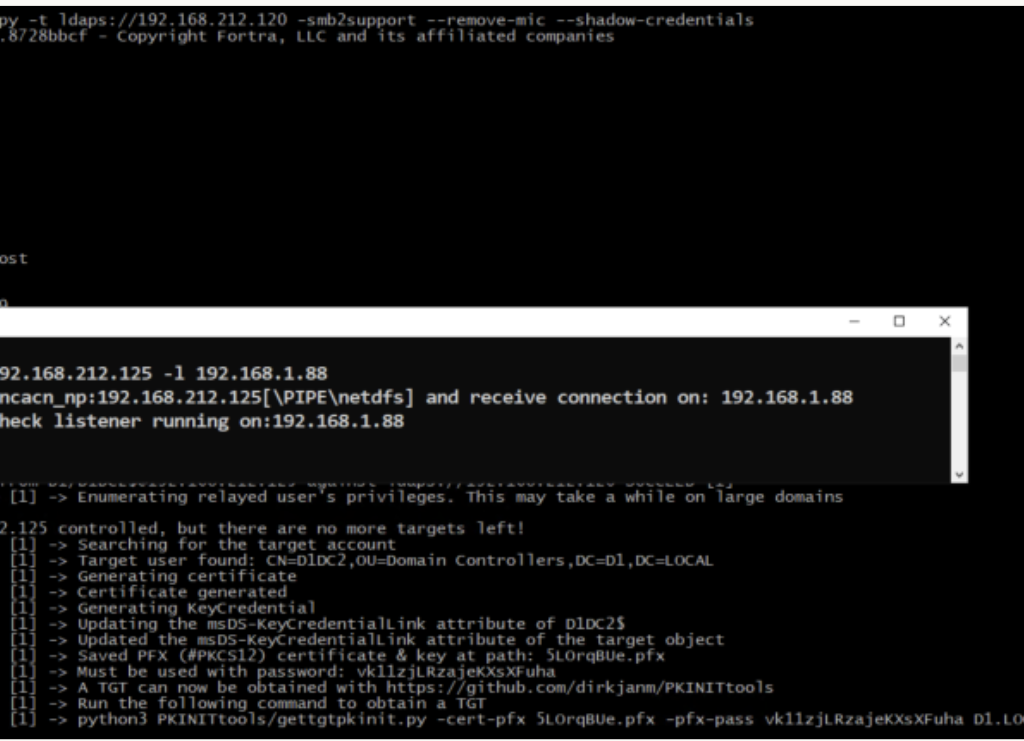
Windows Server 2025 quietly breaks a classic NTLM relay technique by enforcing changes inside msv1_0.dll. The update prevents attackers from abusing NTLMv1…
 Active Directory201
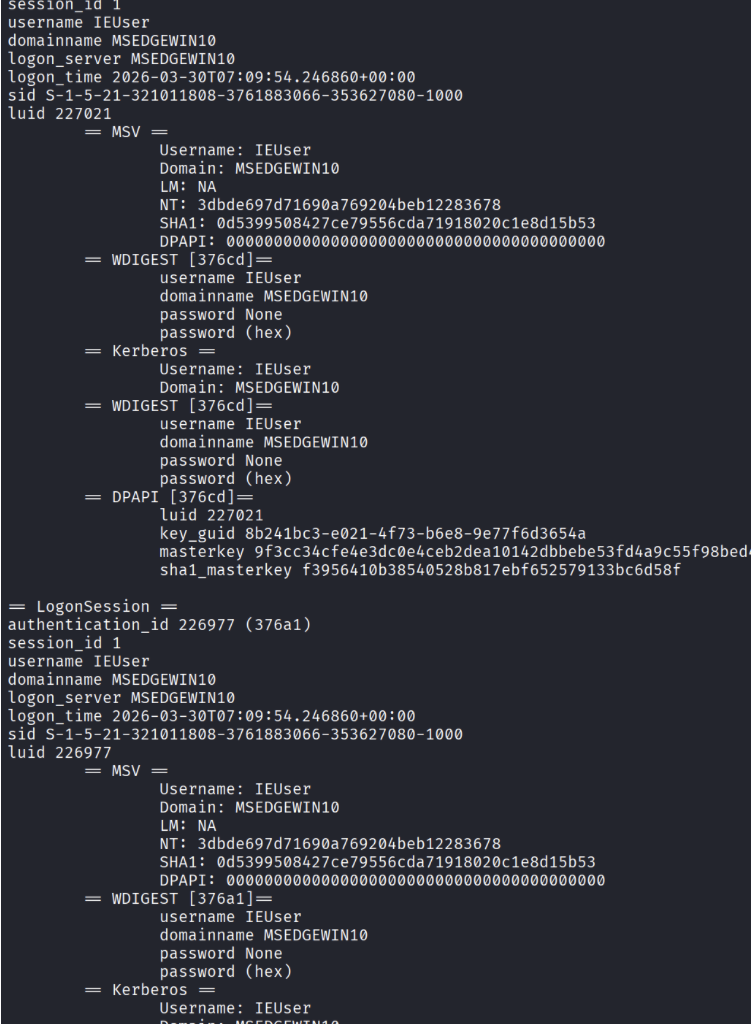
The article explains how attackers dump credentials from the Windows LSASS process using tools like Mimikatz and ProcDump, extracting password hashes and…
 Active Directory190
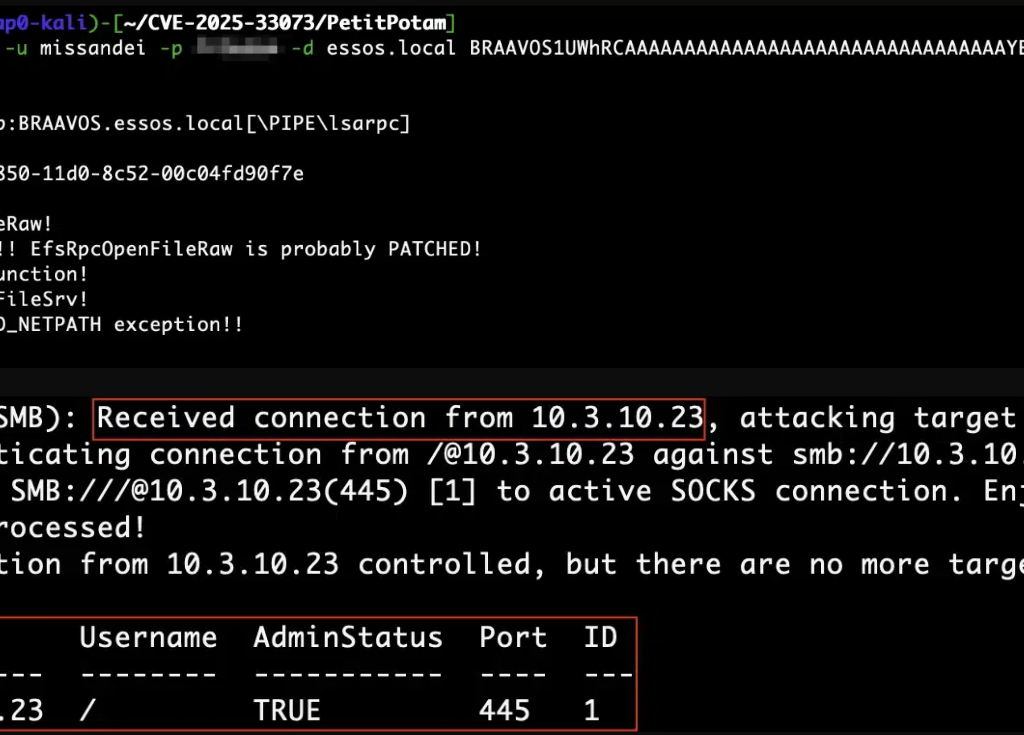
CVE-2025-33073 enables NTLM reflection attacks that give attackers SYSTEM access on vulnerable Windows hosts. When combined with unconstrained delegation, a single compromised…
 Active Directory208
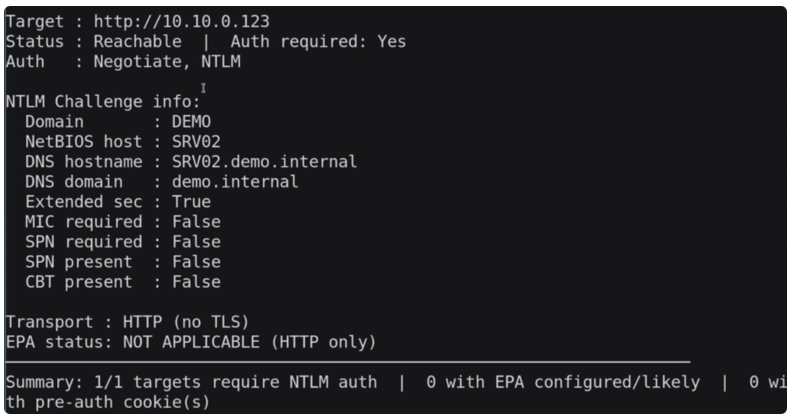
he article demonstrates an NTLM relay attack against Active Directory using tools like ntlmrelayx and PetitPotam. By relaying authentication to LDAP, attackers…
 Active Directory246
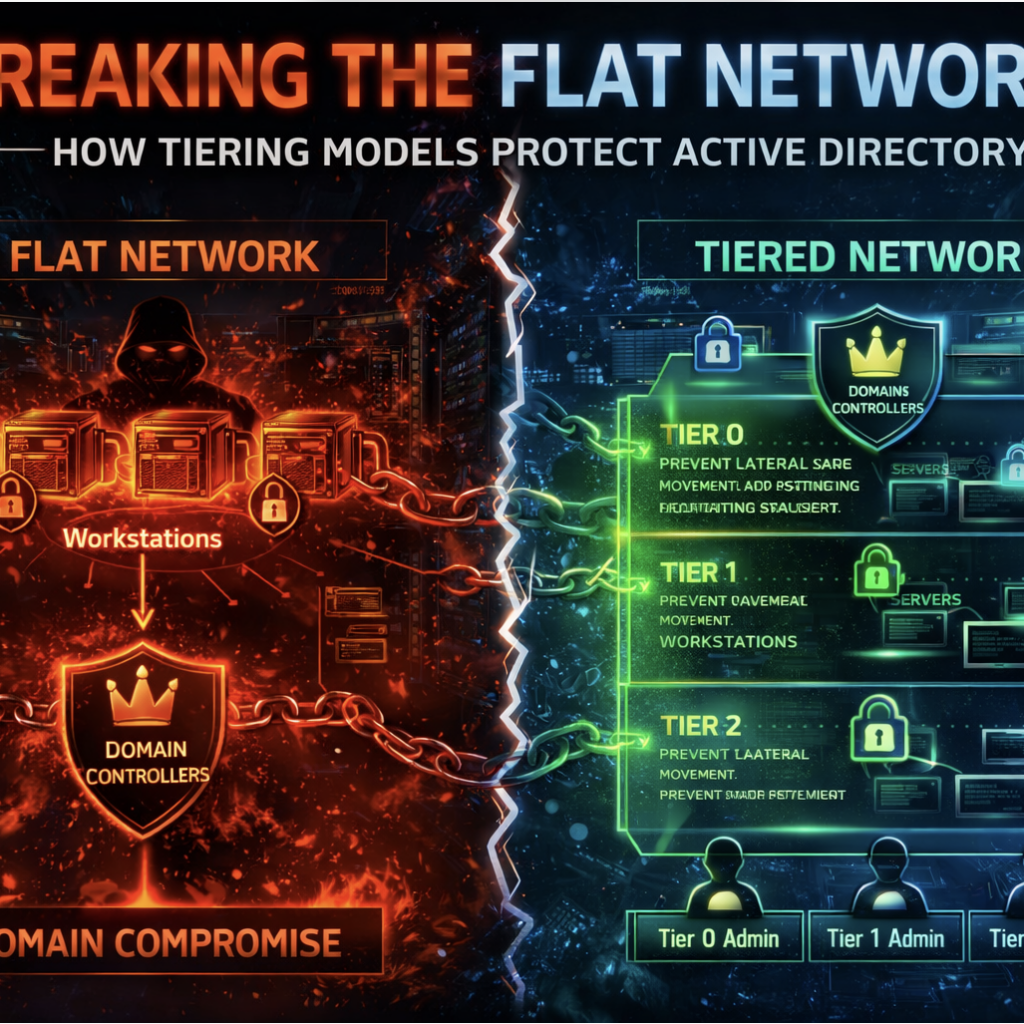
The article explains how flat enterprise networks enable easy lateral movement and domain compromise. It shows how Active Directory tiering models segment…