Linux520 Linux Scales eBPF Rootkit: Detection and Forensic Analysis
Scales is a Linux supply-chain malware that pairs an embedded eBPF rootkit with a built-in Tor client and aggressive credential theft. This…
Linux520 Scales is a Linux supply-chain malware that pairs an embedded eBPF rootkit with a built-in Tor client and aggressive credential theft. This…
kernel369 Walk-through of Lukas Maar’s page-level use-after-free in the Linux kernel’s QAIC (Qualcomm AI Accelerator) DRM driver: the missing VMA boundary check in…
kernel353 A walk-through of zolutal’s revival of the 2017 Project Zero “native_write_cr4” trick on a modern Linux kernel with CR Pinning enabled. The…
Exploit Development384 Deep-dive writeup on a Linux kernel use-after-free in "fs/eventpoll.c". A 2023 optimisation traded a global "epmutex" for per-instance reference counting in epoll’s…
Escalation340 A full walkthrough of CVE-2024-27398, a race-induced use-after-free in the Linux 6.8 Bluetooth SCO subsystem. The exploit races two connect() threads on…
Cybersecurity462 A structured walkthrough of how virtual memory really works on modern operating systems — from contiguous allocation and external fragmentation to paging,…
Linux323 NGINX Rift is a heap overflow in the rewrite module that may crash workers or enable RCE under specific configs. Public PoC…
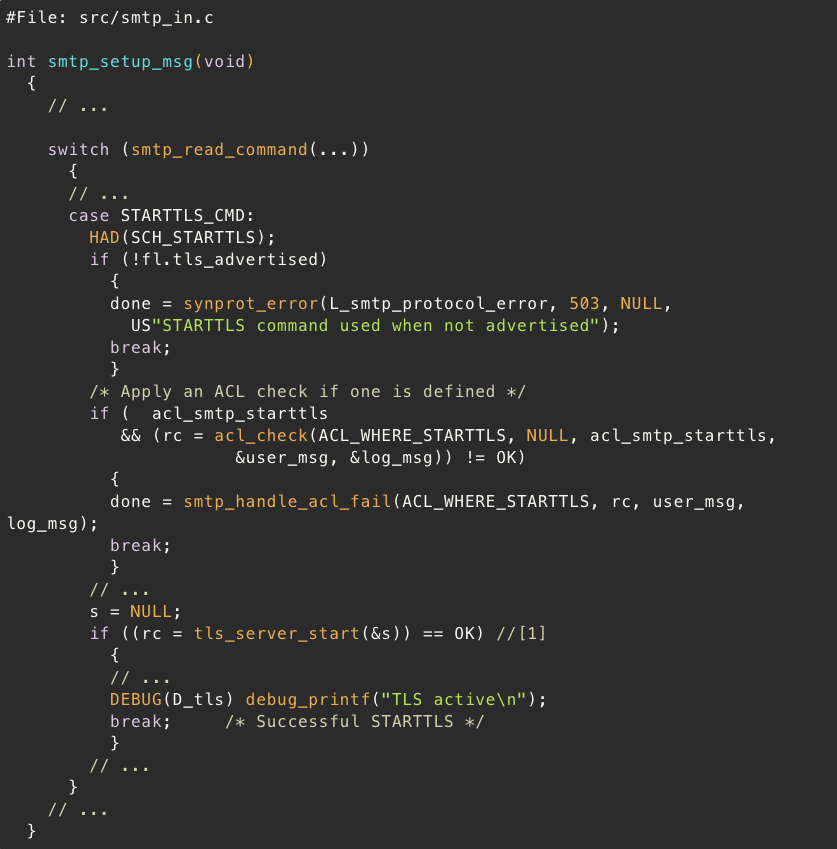
Linux334 A deep dive into CVE-2026-45185: an unauthenticated Exim RCE where one stale TLS/BDAT ungetc() byte corrupts freed memory and leads to exploitation.
kernel-mode422 Dirty Frag is a Linux kernel local privilege escalation class abusing zero-copy networking, skb fragments, and in-place crypto to corrupt page cache…
Exploit Development293 A DiceCTF write-up showing how an RCU double-free race in a Linux kernel module can be turned into a cross-cache exploit by…
Exploit Development346 The article introduces the Out-of-Cancel vulnerability class in the Linux kernel, where workqueue cancellation APIs fail to guarantee object lifetime. This race…
attaks289 The article analyzes CVE-2026-32746, a decades-old vulnerability in GNU Inetutils telnetd where a malformed LINEMODE SLC option triggers an out-of-bounds write, enabling…