Cisco243 CVE-2026-20093: Unauthenticated Admin Reset on Cisco IMC
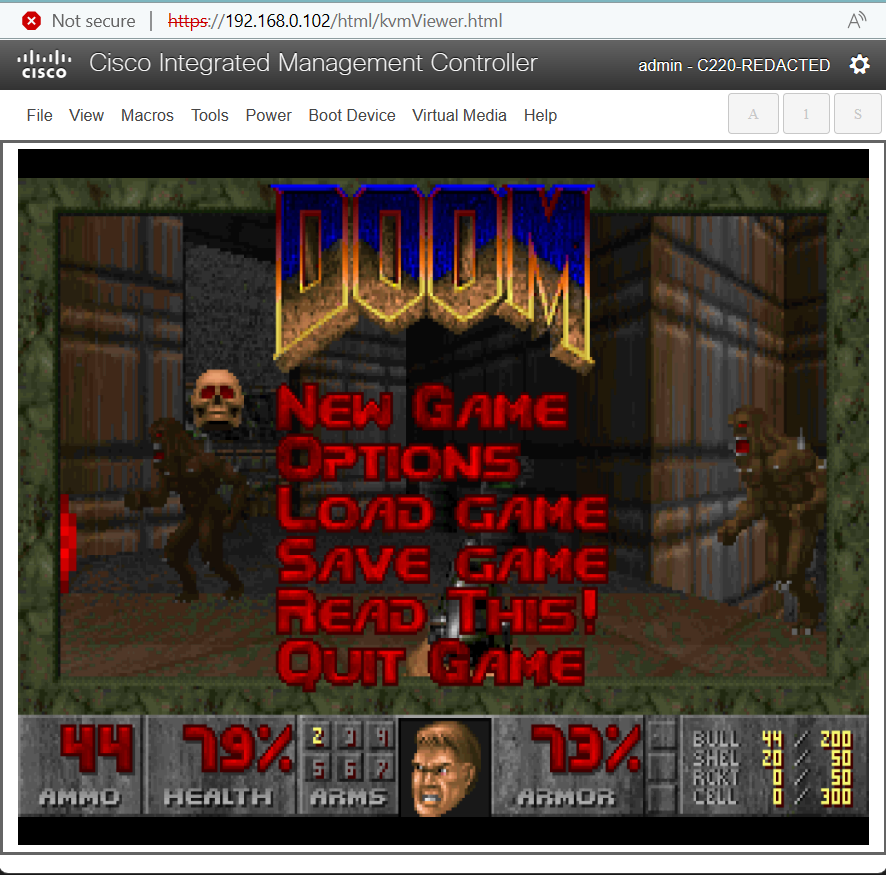
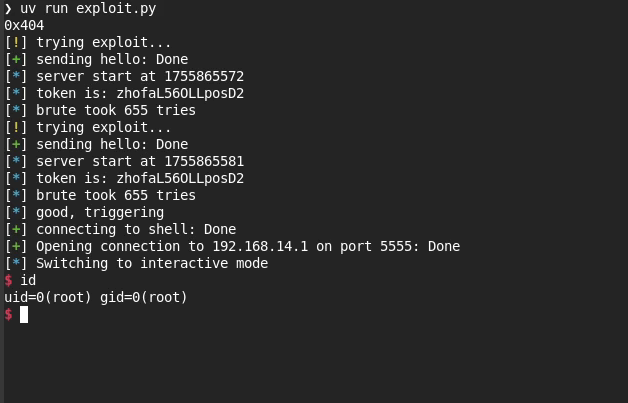
CVE-2026-20093 is a CVSS 9.8 pre-auth password change on Cisco IMC via configConfMo/aaaUser. Lab notes unpack HUU 4.3.2.250063 vs 4.3.2.260007: nginx /nuova,…
Cisco243 CVE-2026-20093 is a CVSS 9.8 pre-auth password change on Cisco IMC via configConfMo/aaaUser. Lab notes unpack HUU 4.3.2.250063 vs 4.3.2.260007: nginx /nuova,…
Bluetooth151 Praetorian's Caeruleus is one Go binary on Linux/BlueZ that replaces hcitool, gatttool, bettercap BLE, and throwaway Bleak scripts: scan, enumerate, assess unpaired…
Cisco202 Aaron Thacker jailbroke a Cisco C195 ESA by splicing a newer BIOS so CIMC came online, exploiting command injection in expRemoteFwUpdate (CVE-2024-20356)…
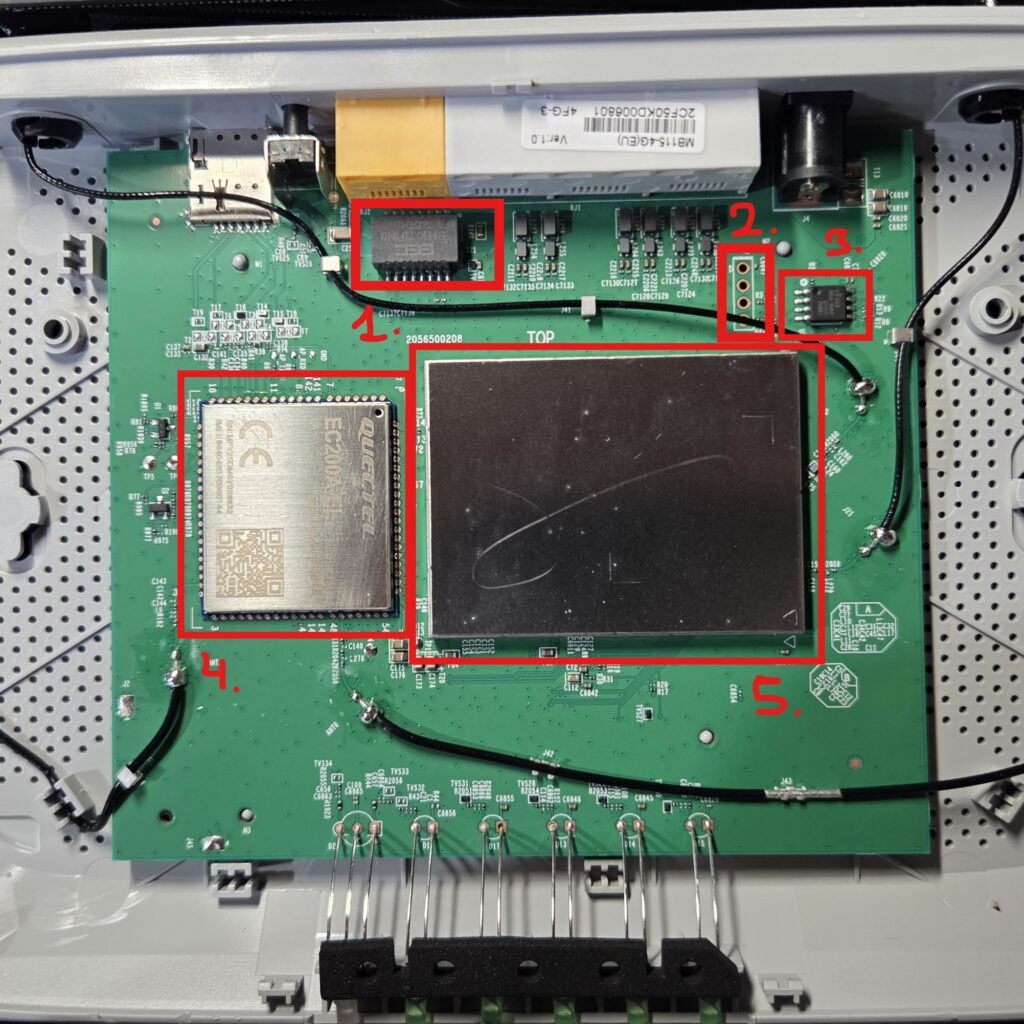
buffer overflow397 A complete hardware-to-firmware walkthrough of the Mercusys MB115-4G, the best-selling router on Amazon Spain: pre-purchase firmware recon, PCB teardown, UART pinout discovery…
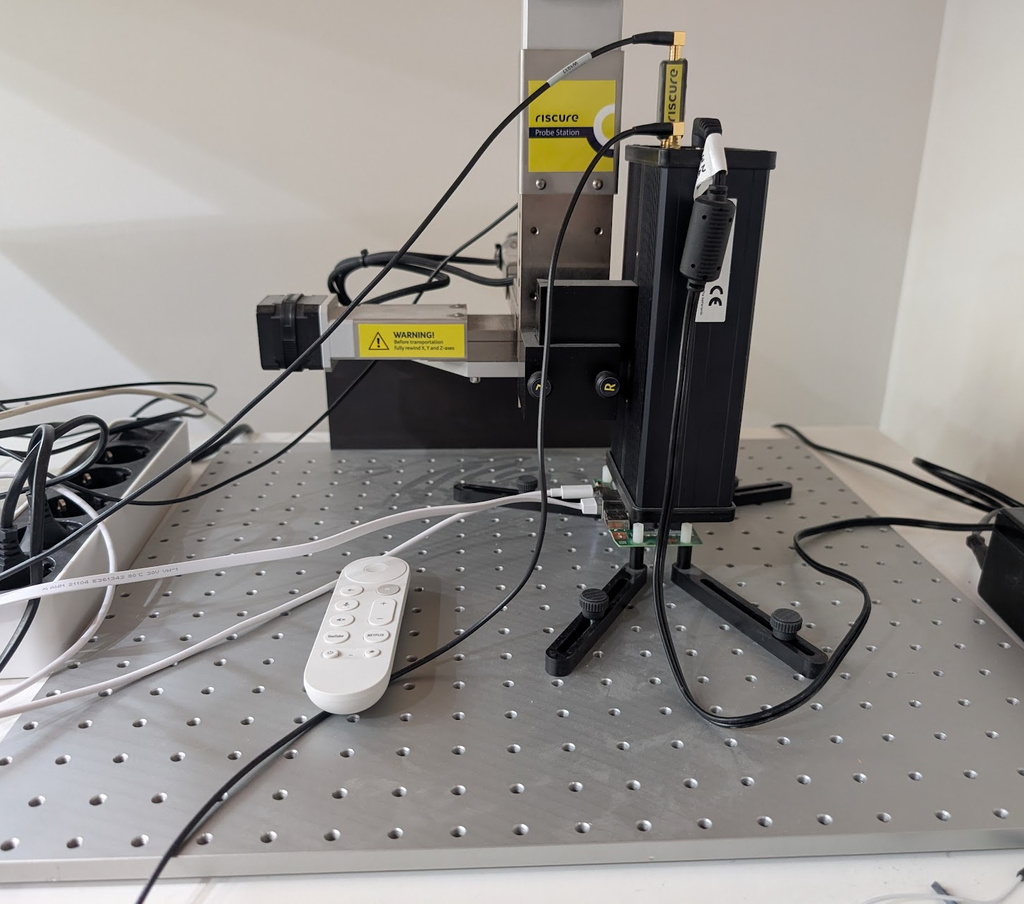
Android301 Raelize B.V. researchers demonstrated a practical electromagnetic fault injection (EMFI) attack on Google's TV Streamer 4K, corrupting the MT8696 SoC's execution of…
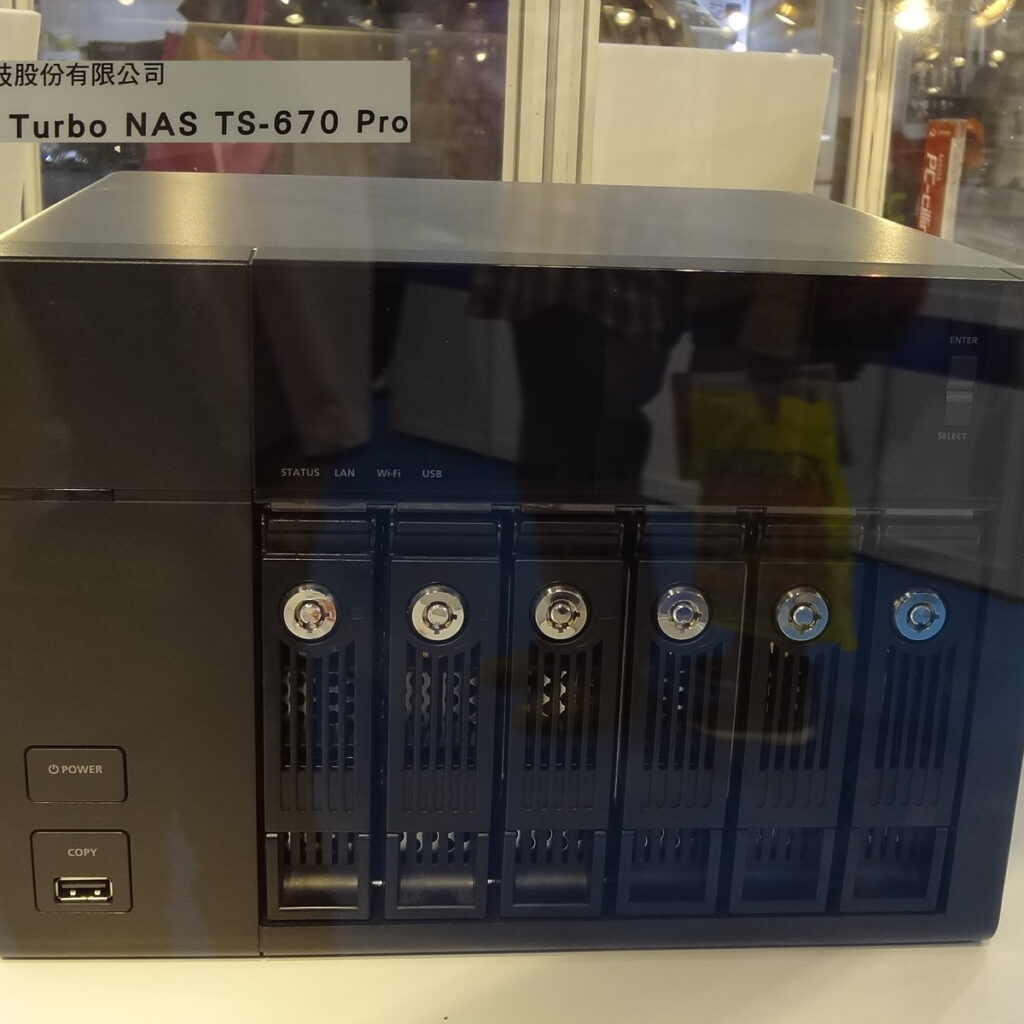
Exploit Development222 CVE-2026-34007 and CVE-2026-34008 expose a systemic pattern in QNAP QTS: header injection into shell_exec, hand-rolled SQL escaping, and unremapped container namespaces that…
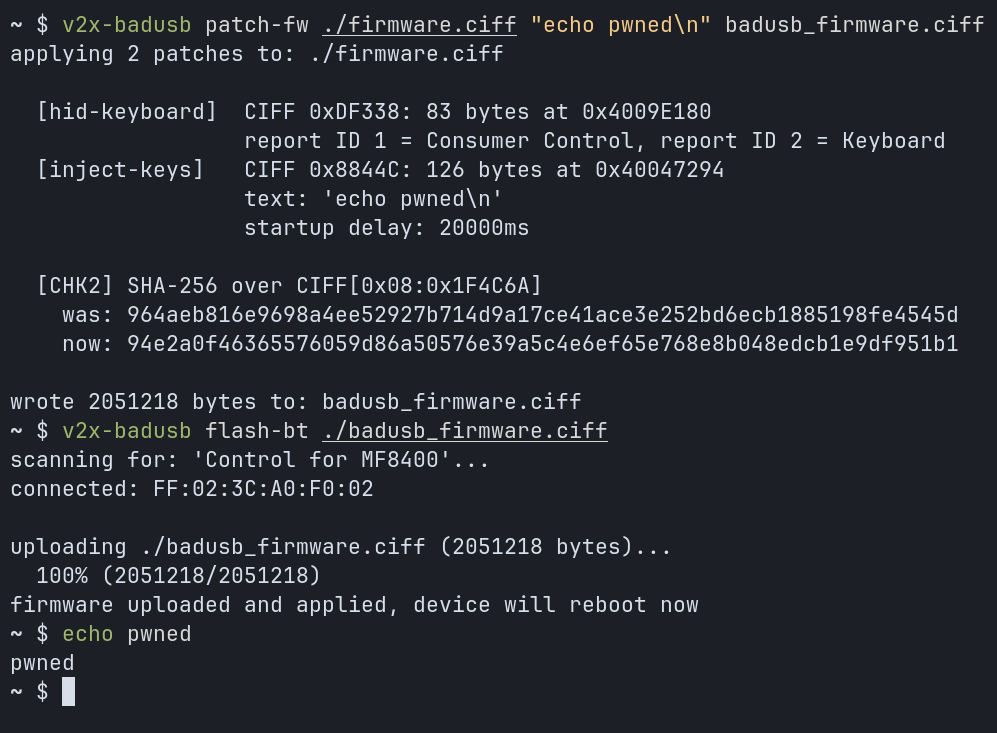
Hardware217 Walk-through of Rasmus Moorats' Pwnd Blaster disclosure: the Creative Sound Blaster Katana V2X soundbar accepts the Creative Transport Protocol over Bluetooth Low…
Cybersecurity236 A deep dive into CVE-2021-21735 on the ZTE ZXHN H168N home gateway, where two unauthenticated wizard endpoints (wizard_pppoe_lua.lua and wizard_wlan_config_lua.lua) leaked PPPoE…
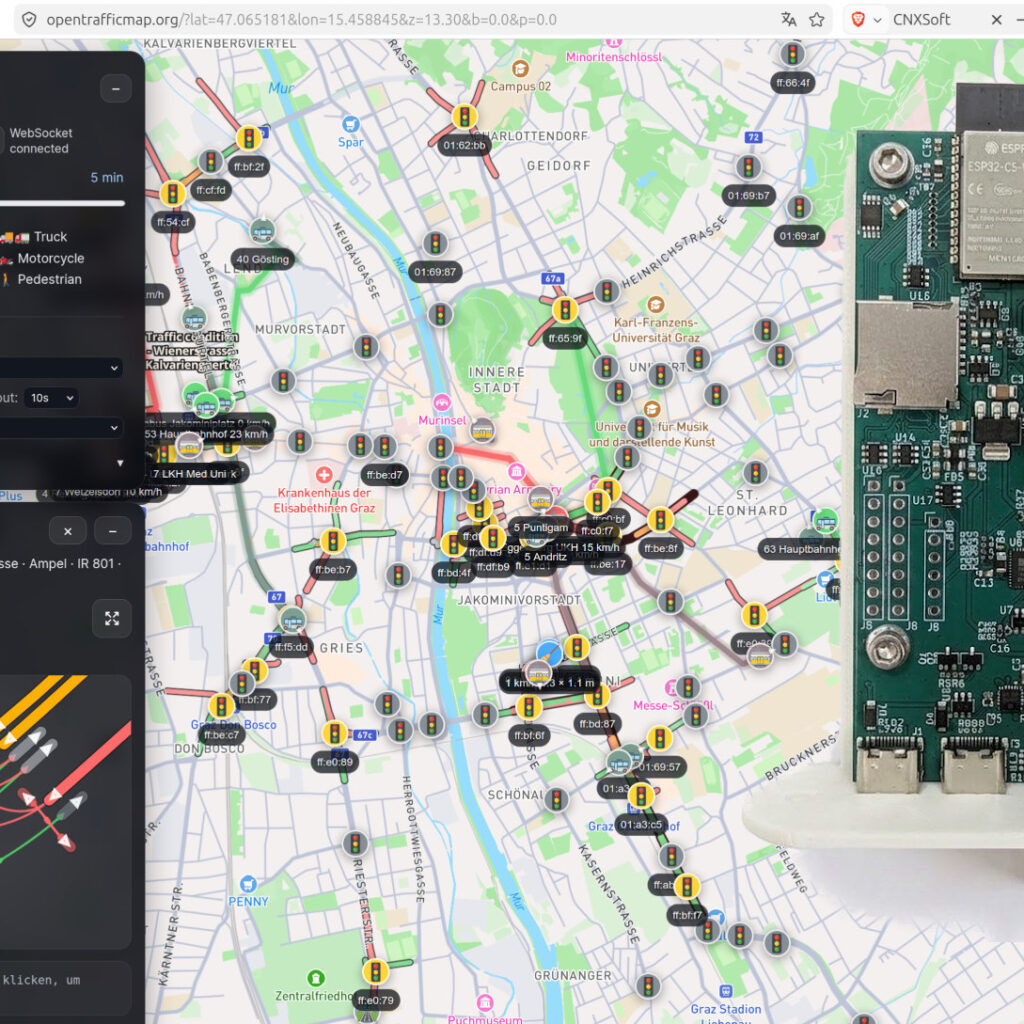
Hardware184 CNX Software write-up on the OpenTrafficMap project — a €20 open-source ESP32-C5 receiver board that taps the 5.9 GHz 802.11p ITS-G5 V2X…
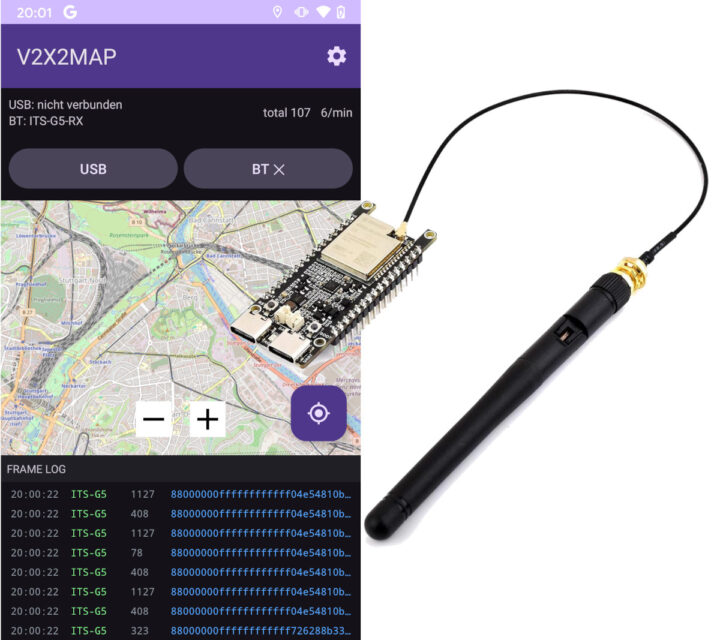
Hardware124 An English rewrite of Jean-Luc Aufranc’s May 25, 2026 CNX Software piece on V2X2MAP — an MIT-licensed Android app by Peter Holzhauser (Pit711)…
Active Directory140 Printers are not harmless office boxes. Misconfigured LDAP, SMTP, SMB or SNMP can leak domain creds, enabling AD enumeration, relay attacks and…
Camera230 Researchers exploited weaknesses in Xiaomi’s miIO protocol to bypass authentication, predict cryptographic values, and trigger memory corruption, ultimately achieving remote code execution…