AI Security Research443 AI-Assisted Fuzzing: Generating libFuzzer Harnesses with a Local LLM
Writing the harness is the friction that keeps most codebases from ever being fuzzed. This walkthrough puts an offline open-weights model behind…
AI Security Research443 Writing the harness is the friction that keeps most codebases from ever being fuzzed. This walkthrough puts an offline open-weights model behind…
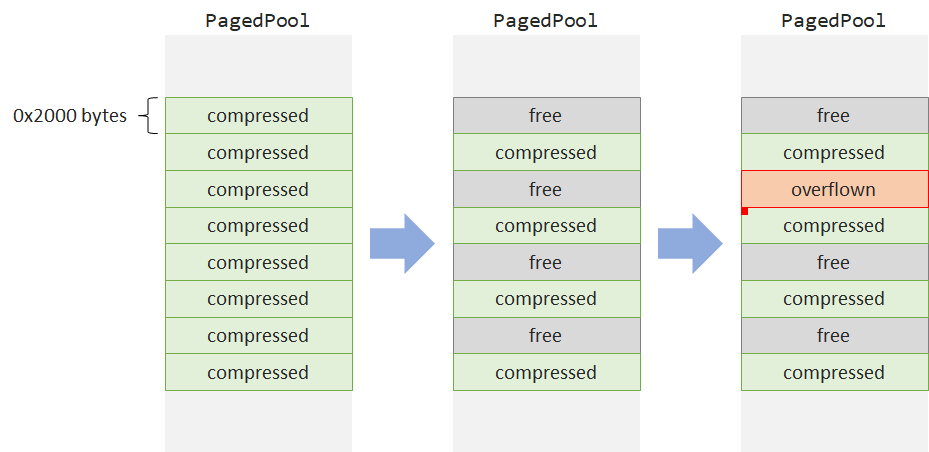
buffer overflow395 A single byte written past the end of a PagedPool allocation in a Windows 10 x64 kernel driver, followed all the way…
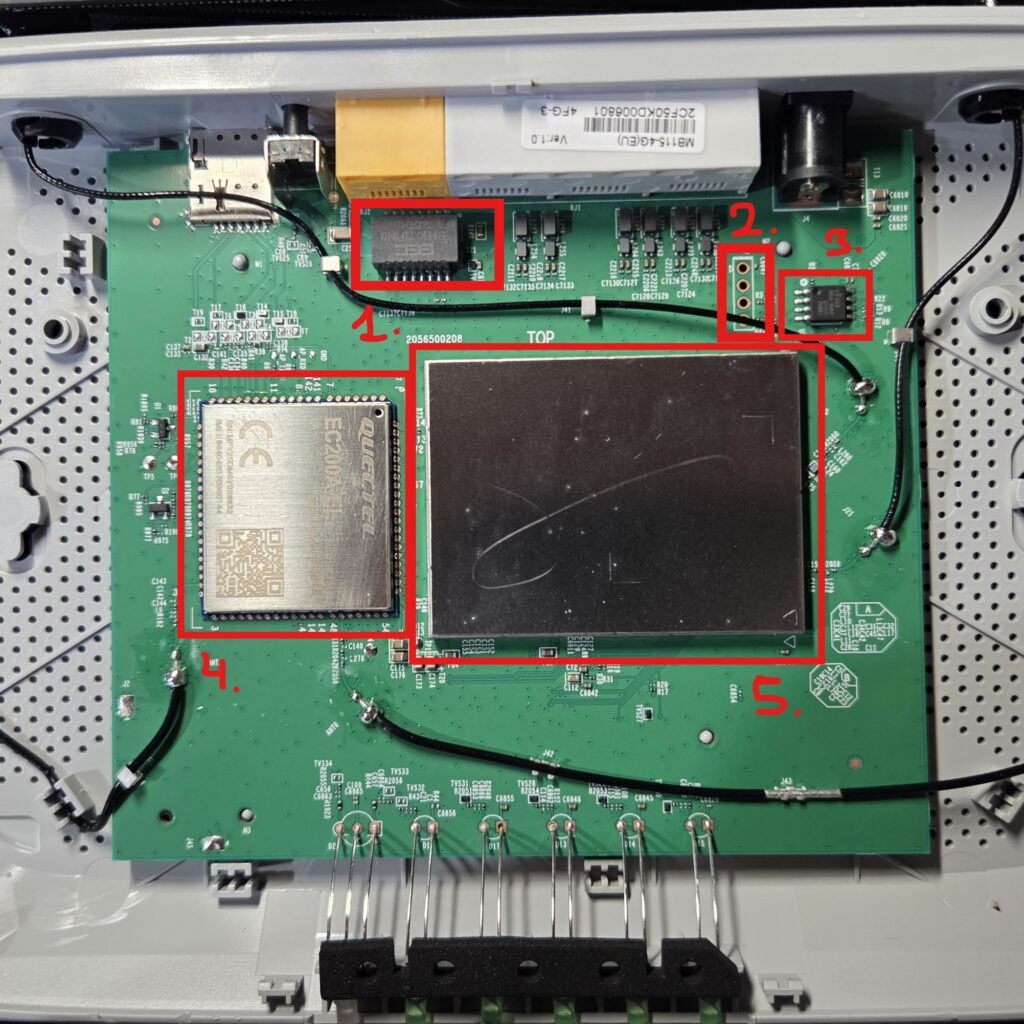
buffer overflow402 A complete hardware-to-firmware walkthrough of the Mercusys MB115-4G, the best-selling router on Amazon Spain: pre-purchase firmware recon, PCB teardown, UART pinout discovery…
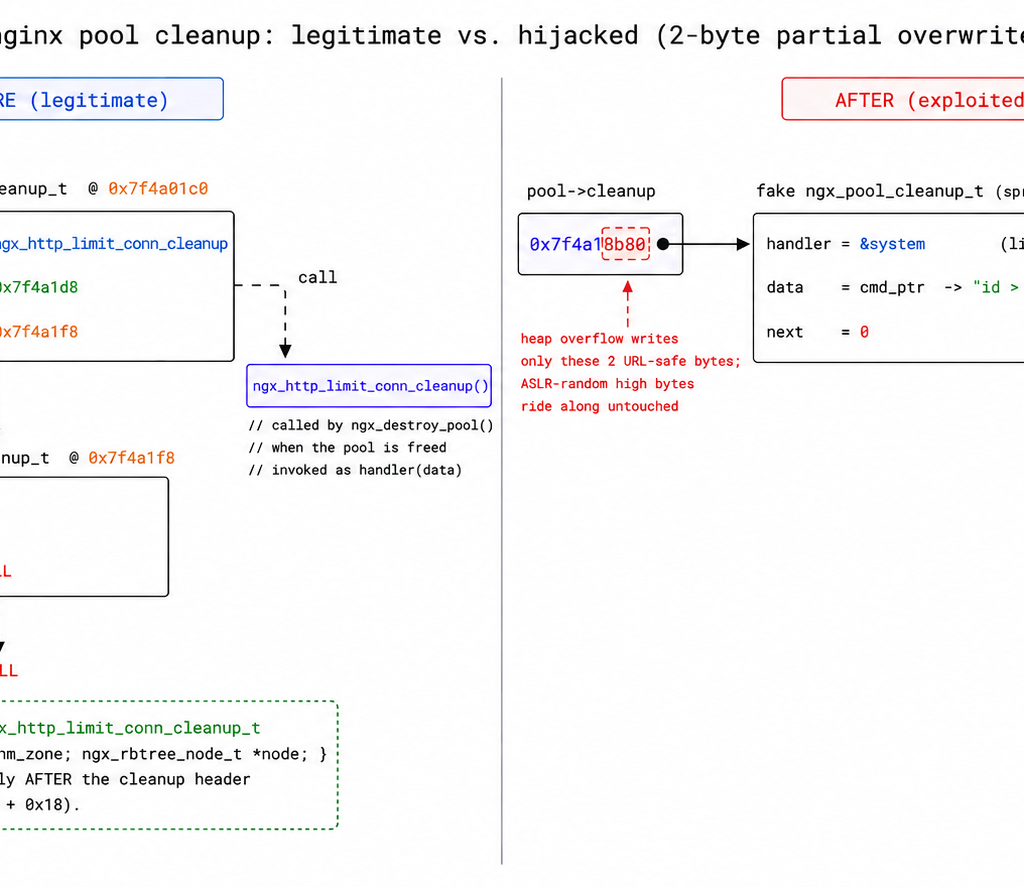
buffer overflow390 A two-bug nginx 1.30.0 chain: CVE-2026-42945 (Rift) heap overflow + CVE-2026-9256 (PoolSlip) heap over-read combine into an ASLR-independent remote system() call at…
buffer overflow393 CVE-2026-47291 is a critical unauthenticated RCE vulnerability in Windows HTTP.sys caused by a 16-bit integer overflow in the buffer reference array growth…
ALPC264 CVE-2020-1027 is a heap buffer overflow in the Windows CSRSS SxS assembly component. A missing bounds check on UNICODE_STRING.MaximumLength in an ALPC…
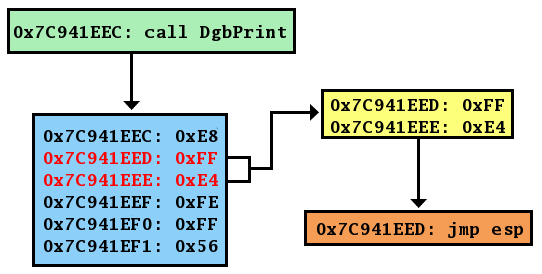
buffer overflow209 When a Windows stack overflow gives you ~250 bytes of crash-buffer space but a useful Meterpreter payload is 400+ bytes, the answer…
buffer overflow237 Uses manual Return-Oriented Programming (ROP) to chain existing code fragments and call VirtualAlloc, changing memory permissions to bypass Windows DEP and then…
ASM173 Article details exploiting a stack buffer overflow on an STM32H5. It demonstrates basic shellcode injection, then bypassing a non-executable stack (XN/MPU) using…