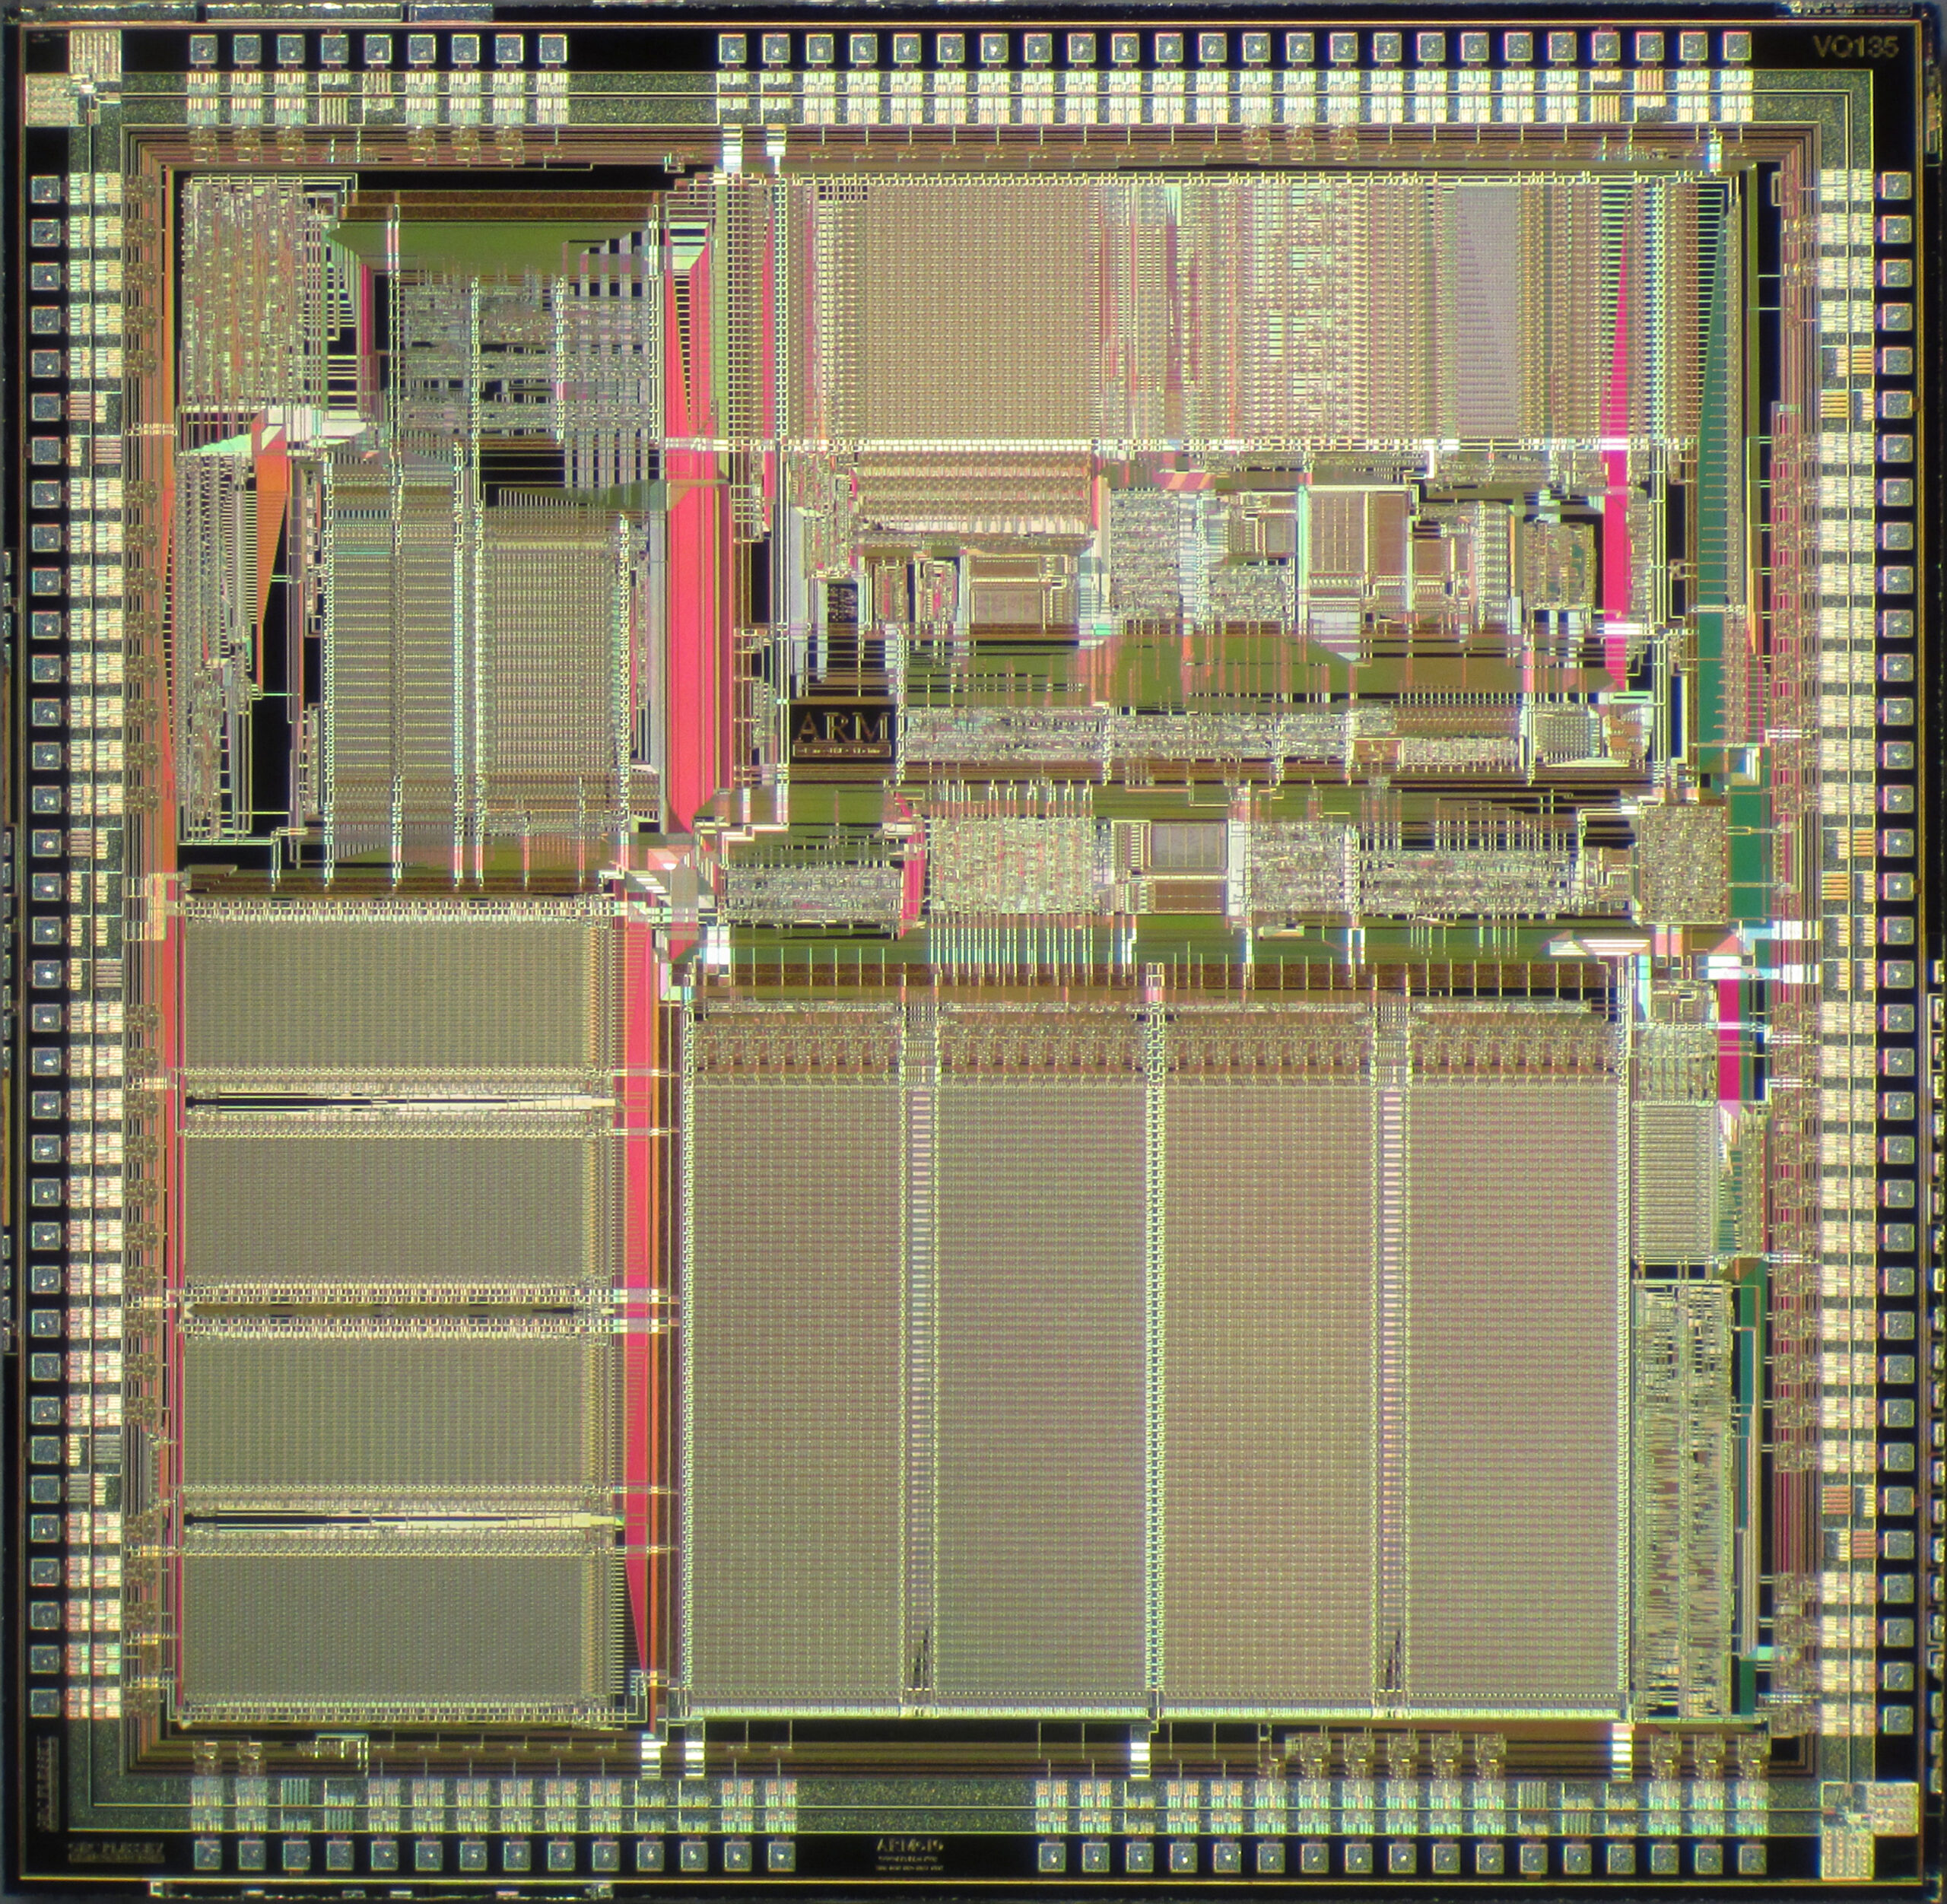
Hardware524 Black Box Probing: Security Analysis of Xiaomi’s MJA1 Secure Chip
Quarkslab's black-box teardown of Xiaomi's undocumented MJA1 secure chip: I2C sniffing, SPI NAND flash dumping, MIPS firmware reverse engineering, full command protocol…
Hardware524 Quarkslab's black-box teardown of Xiaomi's undocumented MJA1 secure chip: I2C sniffing, SPI NAND flash dumping, MIPS firmware reverse engineering, full command protocol…
Hardware464 Walk-through of Rasmus Moorats' Pwnd Blaster disclosure: the Creative Sound Blaster Katana V2X soundbar accepts the Creative Transport Protocol over Bluetooth Low…
Hypervisor299 Aidan Khoury’s Part 2 of the revers.engineering PatchGuard series — two LSTAR-focused checks. KiErrata420Present briefly overwrites LSTAR with a one-byte RET stub…
Hypervisor285 Nick Peterson’s revers.engineering deep-dive on three PatchGuard routines disguised as CPU-errata checks but actually built to catch hypervisor introspection — KiErrata704Present (reads…
Exploit Development362 CVE-2026-41096 is a remotely-triggerable heap overflow in dnsapi.dll. A single crafted UDP DNS response with QDCOUNT=0 corrupts 604 bytes past a heap…
Apple Silicon631 usbliter8 is a new BootROM exploit chain against Apple A12, S4/S5 and A13 SoCs. It chains a 12-byte buffer-underflow primitive in the…
kernel452 A deep technical walkthrough of how Windows on ARM (WoA) discovers, initializes and dispatches interrupts through the Generic Interrupt Controller (GIC) —…
Exploit Development398 A full-pipeline walkthrough: build a vulnerable Windows console program, take RIP with a strcpy overflow, then use rop_scanner — an offline ROP…
Reverse Engineering283 mrexodia publishes Striga: a deliberately small Python lifter that translates x86_64 instructions to LLVM IR using Capstone and a new set of…
Exploit Development464 Calif’s AI-assisted security team published a write-up of their FreeBSD kernel engagement: "15 bugs total" — 3 RCEs, 5 LPEs, 1 bhyve…
Exploit Development457 CVE-2025-61622 is an unauthenticated remote code execution in PyFory (formerly PyFury) 0.12.0–0.12.2 reachable through the library’s fallback path for unregistered types: "handle_unsupported_read()"…
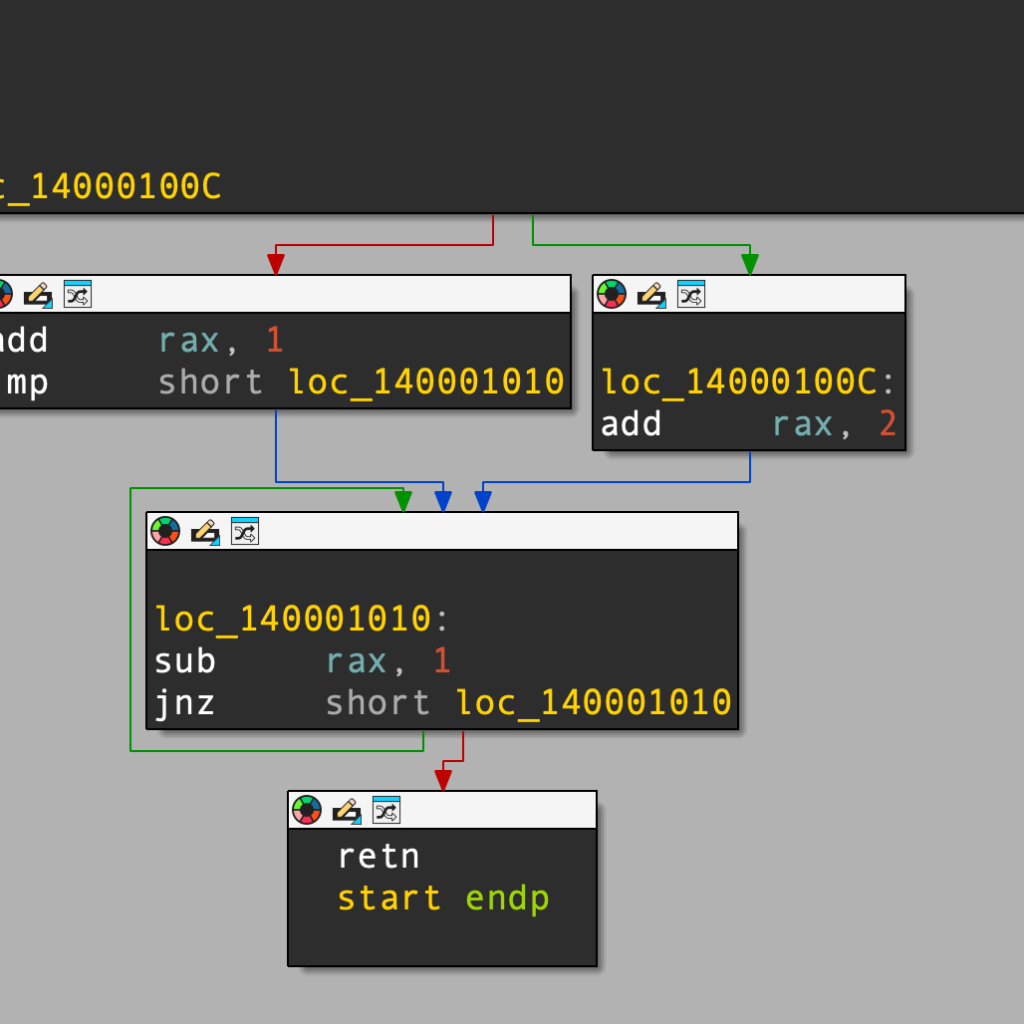
Reverse Engineering460 A step-by-step walkthrough of reverse-engineering a Windows x64 crackme that XORs its input against a hard-coded 10-byte key before comparing it to…