Bypassing189 Abusing WinML for In-Memory Staging and EDR Evasion
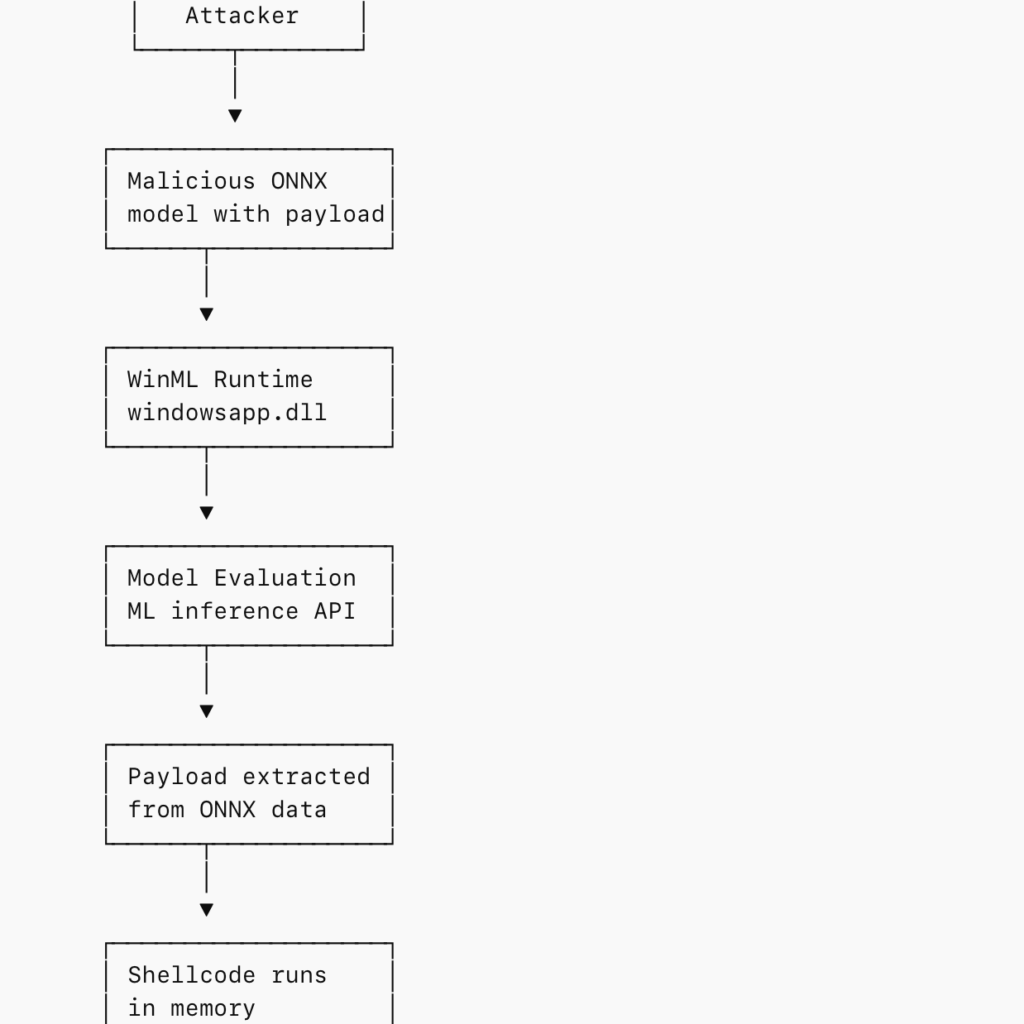
The research shows how attackers can embed payloads inside ONNX ML models and load them via Windows WinML APIs, staging malware entirely…
Bypassing189 The research shows how attackers can embed payloads inside ONNX ML models and load them via Windows WinML APIs, staging malware entirely…
Bypassing699 COMouflage is a stealthy Windows injection technique that abuses COM DLL Surrogates to execute malicious DLLs inside dllhost.exe, making svchost.exe appear as…
BYOVD213 The article shows how BYOVD techniques bypass Windows Code Integrity by loading a vulnerable signed driver and exploiting its IOCTL interface to…
BYOVD860 KslKatz is a Windows credential-dumping tool that reads LSASS memory using a kernel driver to bypass user-mode protections. It merges techniques from…
Bypassing204 The article demonstrates how to bypass the Winsock layer by communicating directly with the Windows AFD driver using Native API calls. It…
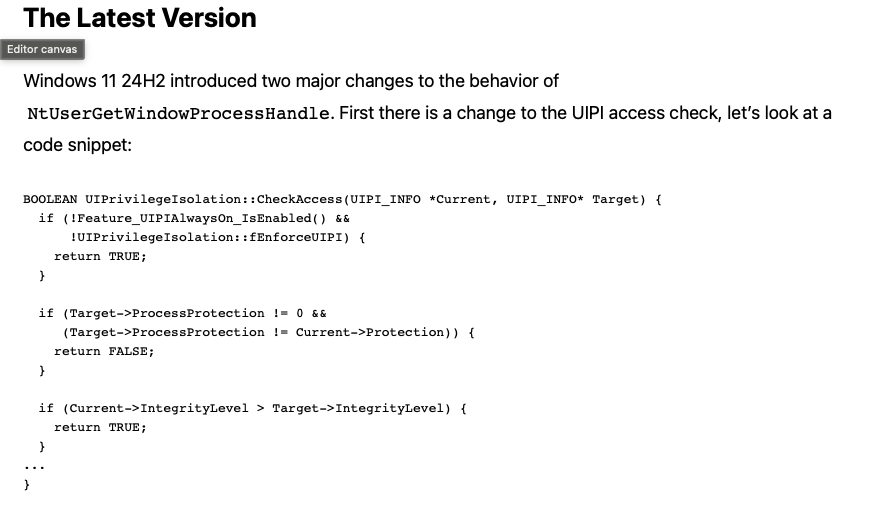
Bypassing108 The article analyzes the Windows GetProcessHandleFromHwnd API and its evolution from a hook-based implementation to a kernel Win32k function that could open…
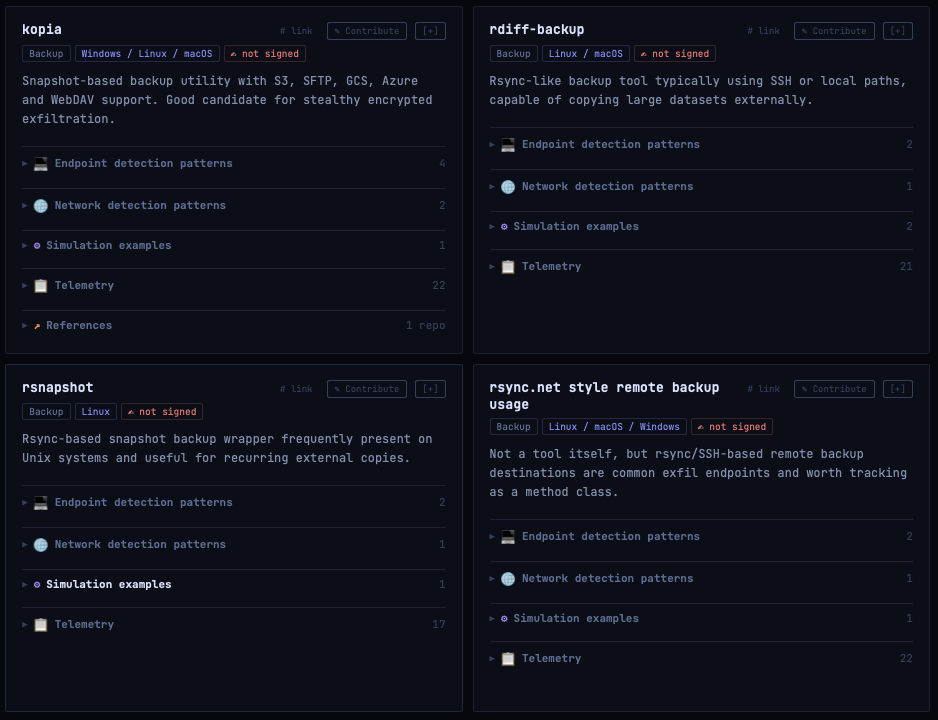
Bypassing98 The article introduces LOLExfil, a Living-Off-the-Land data exfiltration technique that abuses legitimate system tools and trusted services to stealthily extract data, blending…
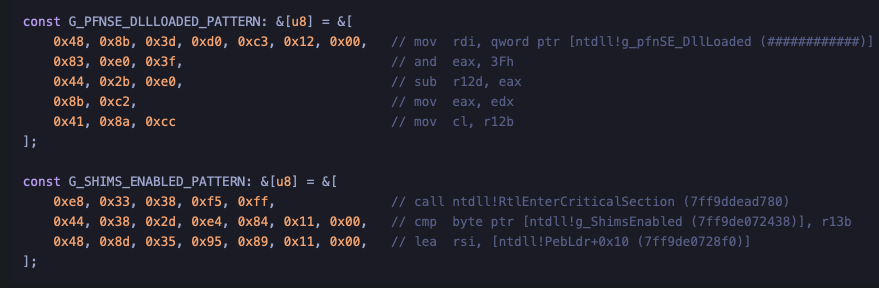
attaks103 How to implement Early Cascade Injection in Rust, a stealthy Windows process injection technique that hijacks shim engine callbacks in ntdll to…
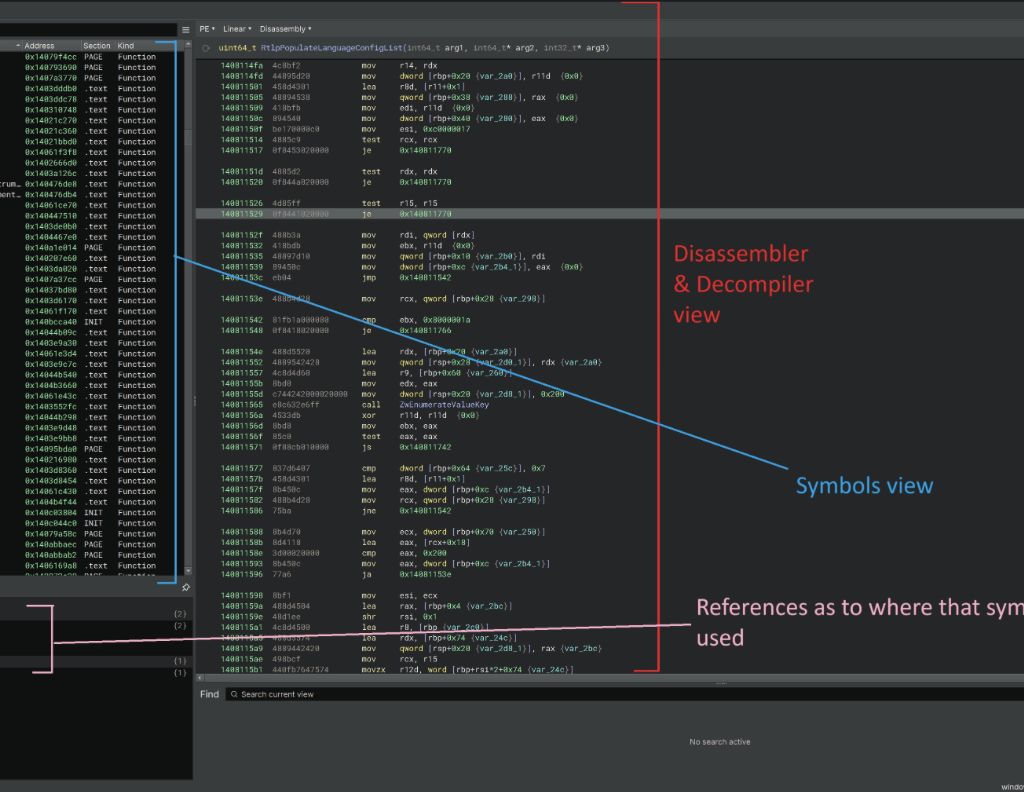
Antivirus221 This article demonstrates how to reverse engineer the Windows 11 kernel to understand undocumented internals behind memory operations and ETW Threat Intelligence…
Bypassing96 “Silent Harvest” explains how attackers can quietly extract sensitive Windows secrets such as credentials and security keys by abusing legitimate registry and…
access157 The article analyzes a technique that disables Microsoft Defender by modifying file ACLs to block security services from accessing critical system DLLs.…
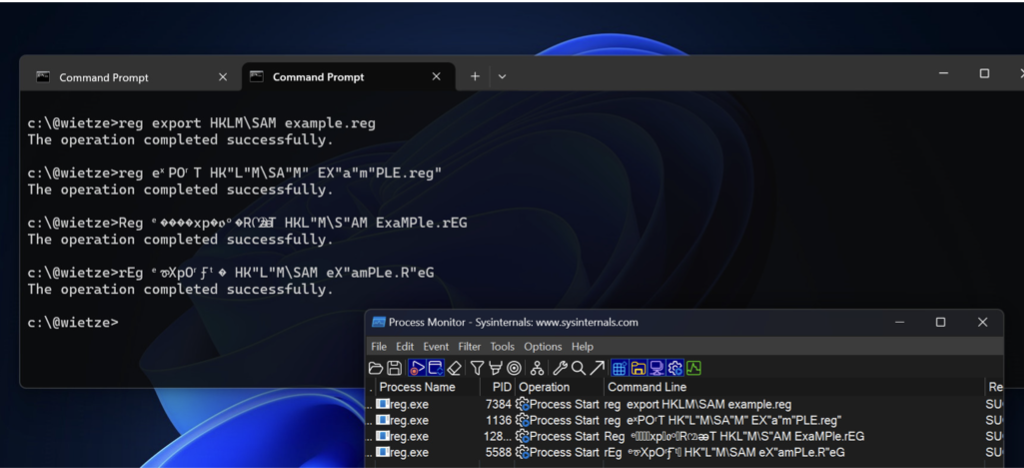
Antivirus244 How attackers can bypass AV and EDR detections by obfuscating command-line arguments. By exploiting parsing quirks in executables, small changes to parameters…