ALPC430 CVE-2020-1027: Windows CSRSS Heap Buffer Overflow and Sandbox Escape
CVE-2020-1027 is a heap buffer overflow in the Windows CSRSS SxS assembly component. A missing bounds check on UNICODE_STRING.MaximumLength in an ALPC…
ALPC430 CVE-2020-1027 is a heap buffer overflow in the Windows CSRSS SxS assembly component. A missing bounds check on UNICODE_STRING.MaximumLength in an ALPC…
Hardware432 Quarkslab's black-box teardown of Xiaomi's undocumented MJA1 secure chip: I2C sniffing, SPI NAND flash dumping, MIPS firmware reverse engineering, full command protocol…
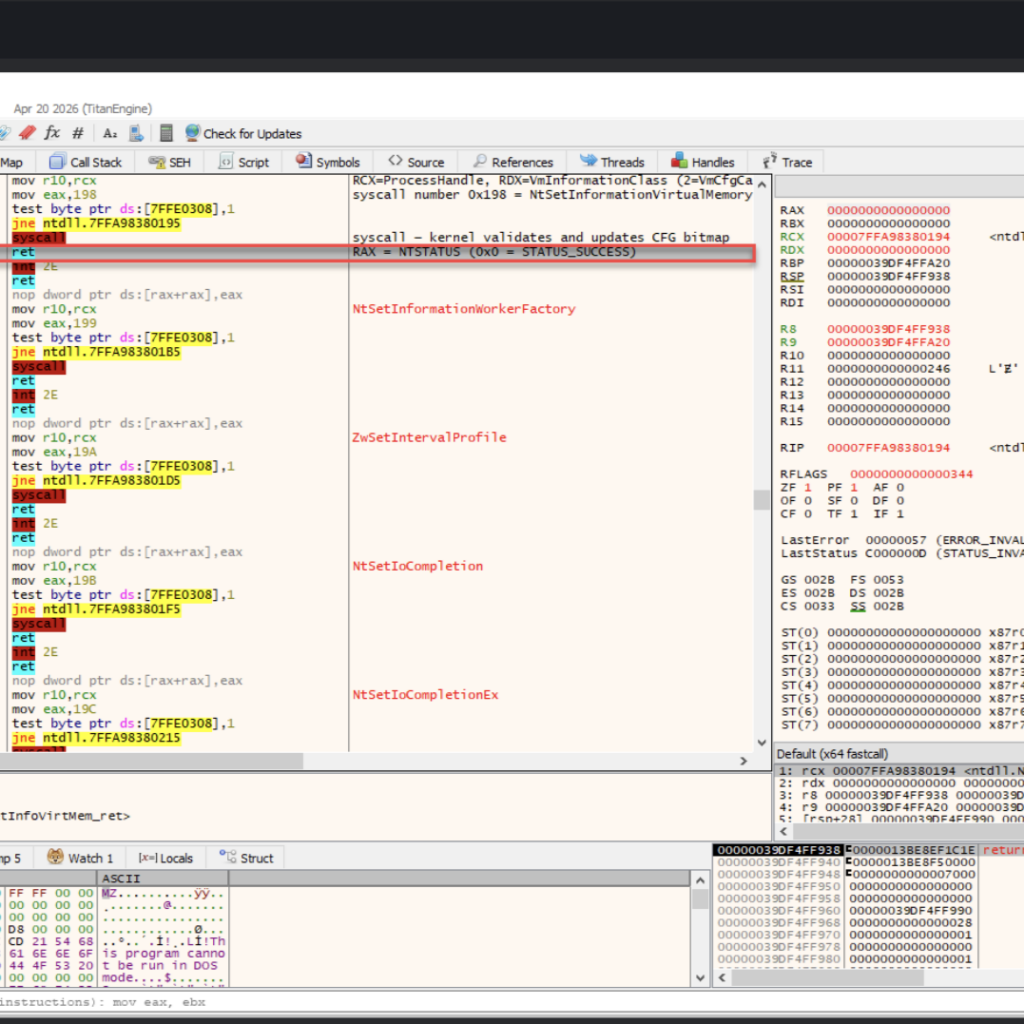
Debug467 This post tackles CFG and CET/Shadow Stack bypasses for sleep obfuscation. It registers ROP gadgets via NtSetInformationVirtualMemory, swaps TIB stack bounds instead…
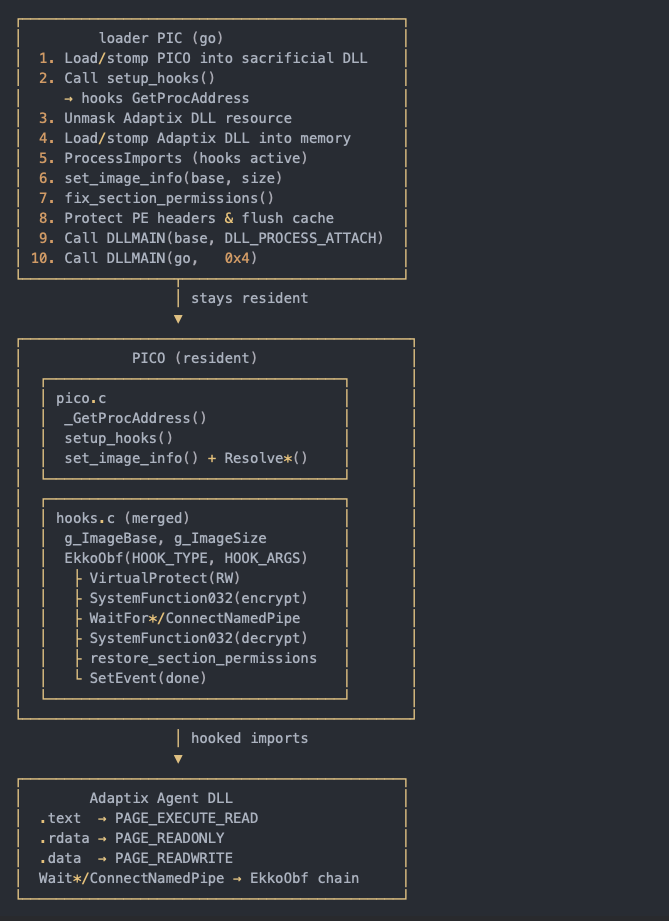
Malware405 This post details the journey of hardening Adaptix C2's default agent DLL using Crystal Palace's Reflective DLL loader. It implements IAT hooking,…
Deep dive into Windows PE file format—headers, sections, and loader mechanics. Explains how security products (AV/EDR) detect malware via static analysis: entropy,…
RPC382 Many Windows RPC servers expose several context-handle types under one interface. When the IDL marks a handle as FC_BIND_CONTEXT (0x70) instead of…
Network347 A length-confusion bug in OpenBSD's PAP handler let an unauthenticated attacker on the same broadcast domain pass authentication with zero-length credentials —…
Security395 Squidbleed (CVE-2026-47729) is a heap buffer over-read in the Squid proxy's FTP gateway, rooted in a missing NUL-terminator check before strchr() that…
Linux461 Scales is a Linux supply-chain malware that pairs an embedded eBPF rootkit with a built-in Tor client and aggressive credential theft. This…
Hardware386 Walk-through of Rasmus Moorats' Pwnd Blaster disclosure: the Creative Sound Blaster Katana V2X soundbar accepts the Creative Transport Protocol over Bluetooth Low…
Credential Attacks394 Windows Sandbox is supposed to be the safe place to open untrusted files — but the .wsb configuration file is parsed by…
Hypervisor262 Aidan Khoury’s Part 2 of the revers.engineering PatchGuard series — two LSTAR-focused checks. KiErrata420Present briefly overwrites LSTAR with a one-byte RET stub…
Hypervisor245 Nick Peterson’s revers.engineering deep-dive on three PatchGuard routines disguised as CPU-errata checks but actually built to catch hypervisor introspection — KiErrata704Present (reads…
EDR Evasion510 Two Python shellcode stagers from g3tsyst3m that hit 0/63 on VirusTotal — Variant #1 uses string-reversed NT APIs (NtAllocateVirtualMemory, NtCreateThreadEx) plus RWX…
Exploit Development309 CVE-2026-41096 is a remotely-triggerable heap overflow in dnsapi.dll. A single crafted UDP DNS response with QDCOUNT=0 corrupts 604 bytes past a heap…
Apple Silicon509 usbliter8 is a new BootROM exploit chain against Apple A12, S4/S5 and A13 SoCs. It chains a 12-byte buffer-underflow primitive in the…
Blue team465 Distributed COM (DCOM) lets one Windows host instantiate and drive COM objects on another over the network — and that same capability…