Browser Security563 Wipeload Step 6: Escaping the Chrome Sandbox via an ALPC Use-After-File
How the Wipeload chain turns an ALPC use-after-free into a stable cross-process read/write primitive and escapes the Chrome renderer sandbox — reclaiming…
Browser Security563 How the Wipeload chain turns an ALPC use-after-free into a stable cross-process read/write primitive and escapes the Chrome renderer sandbox — reclaiming…
Exploit Development525 COFF mixing combines capability code with benign functions and links them as PE-ready COFF objects, eliminating memory-injection IOCs while preserving agent capabilities…
Browser Security1.1k CVE-2026-40369 is an unprivileged twelve-byte arbitrary kernel write in nt!ExpGetProcessInformation, reachable via NtQuerySystemInformation from browser renderer sandboxes. Root-cause analysis and a full…
Exploit Development1.3k GhostLock (CVE-2026-43499) is a 15-year-old use-after-free in the Linux kernel's rtmutex/futex requeue-PI code. When a proxy lock hits a deadlock and rolls…
Browser Security811 CVE-2026-10702 is a miscompilation bug in Firefox's SpiderMonkey Ion/Warp JIT. The MObjectToIterator instruction produced by scalar-replacing Object.keys() declares a load-only alias set,…
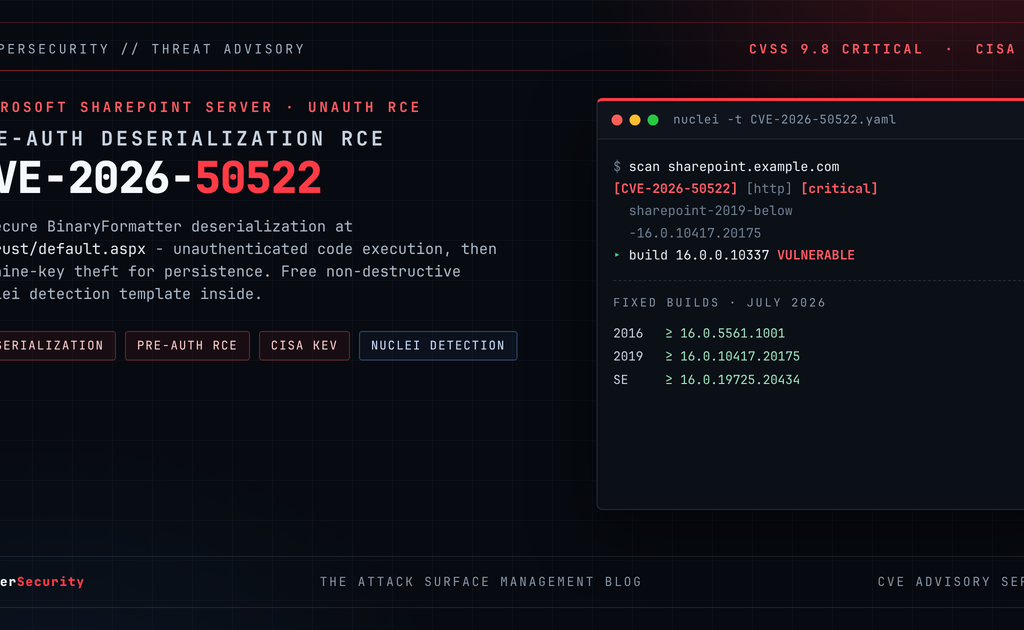
Threat Intelligence655 CVE-2026-50522 is a critical (CVSS 9.8) unauthenticated, pre-auth deserialization RCE in on-premises Microsoft SharePoint Server. A single crafted WS-Federation POST to /_trust/default.aspx…
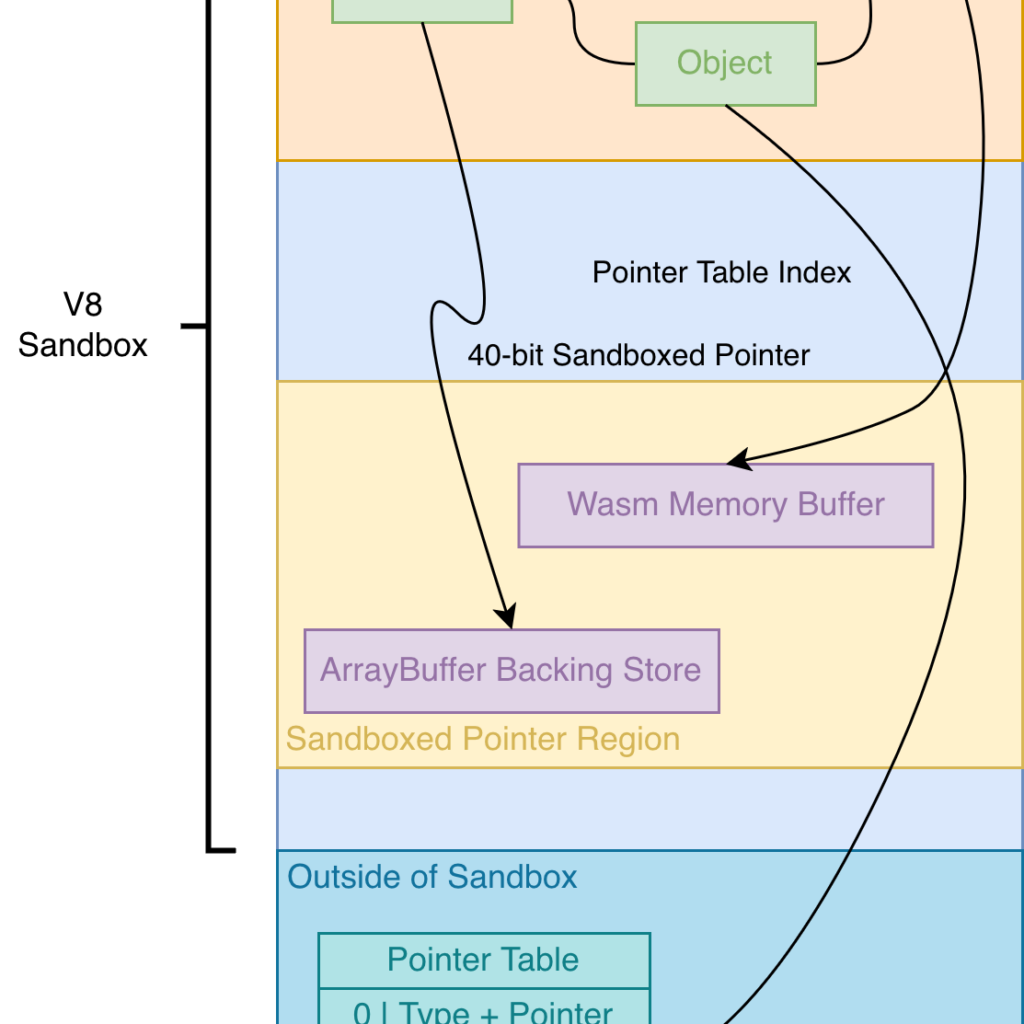
Browser Security817 CVE-2026-6307 is a single V8 vulnerability that pierces two security boundaries at once. A missing signature comparison lets TurboFan's global value numbering…
Malware2.2k A reverse-engineering walkthrough of SakDriver, a Windows kernel-mode rootkit first mistaken for a Cobalt Strike Beacon. It patches ETW, hides processes via…
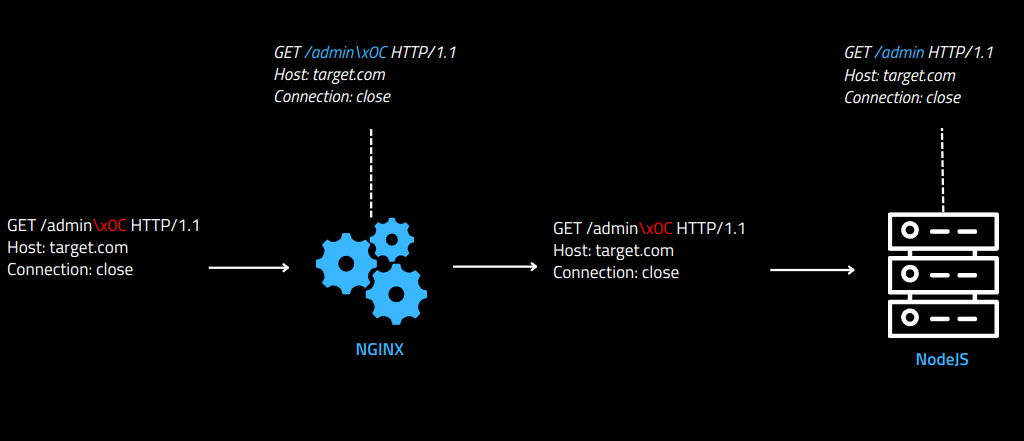
Application Security770 A deep tour of HTTP parser inconsistencies: how trim/fold/header disagreements between Nginx, WAFs, caches and frameworks (Node.js, Flask, Spring Boot, PHP) enable…
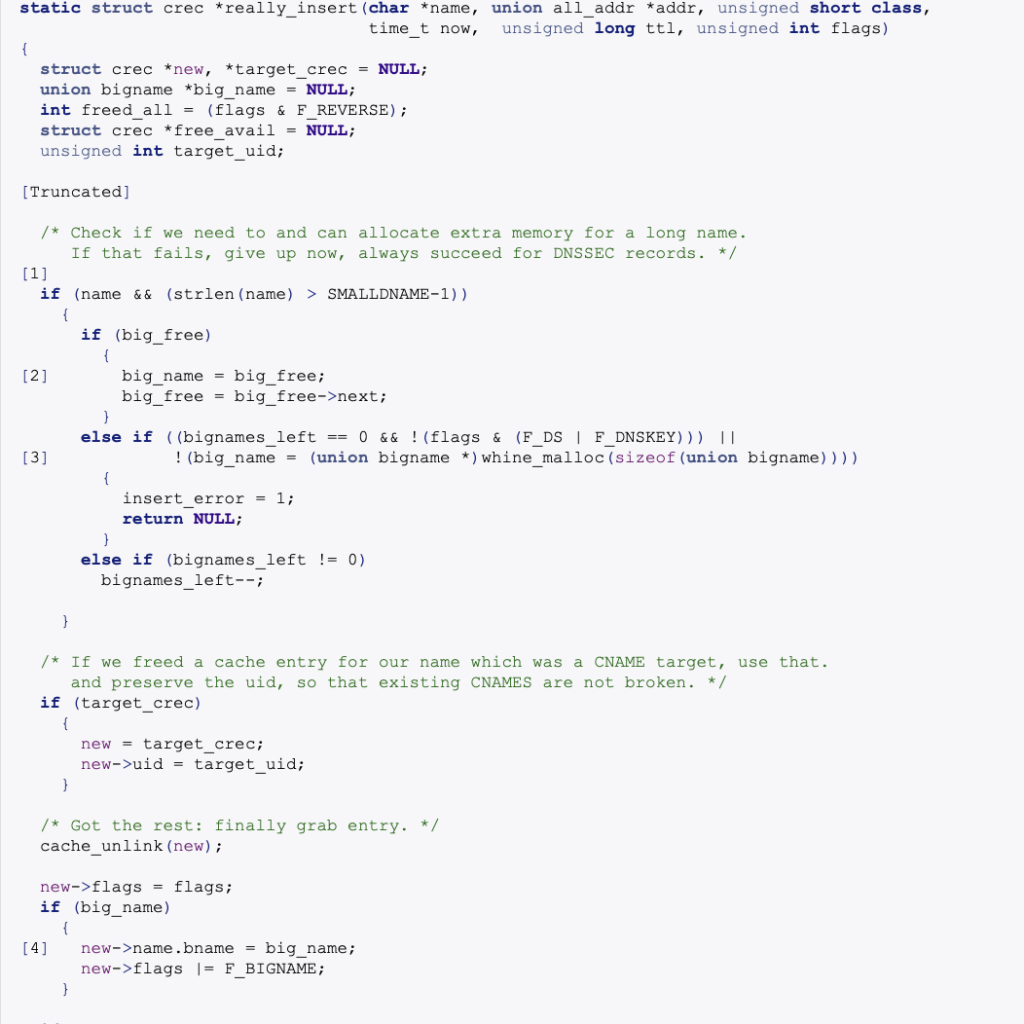
Uncategorized970 Technical analysis of CVE-2026-2291, a critical heap buffer overflow vulnerability in dnsmasq that enables remote code execution through malicious DNS responses. Includes…
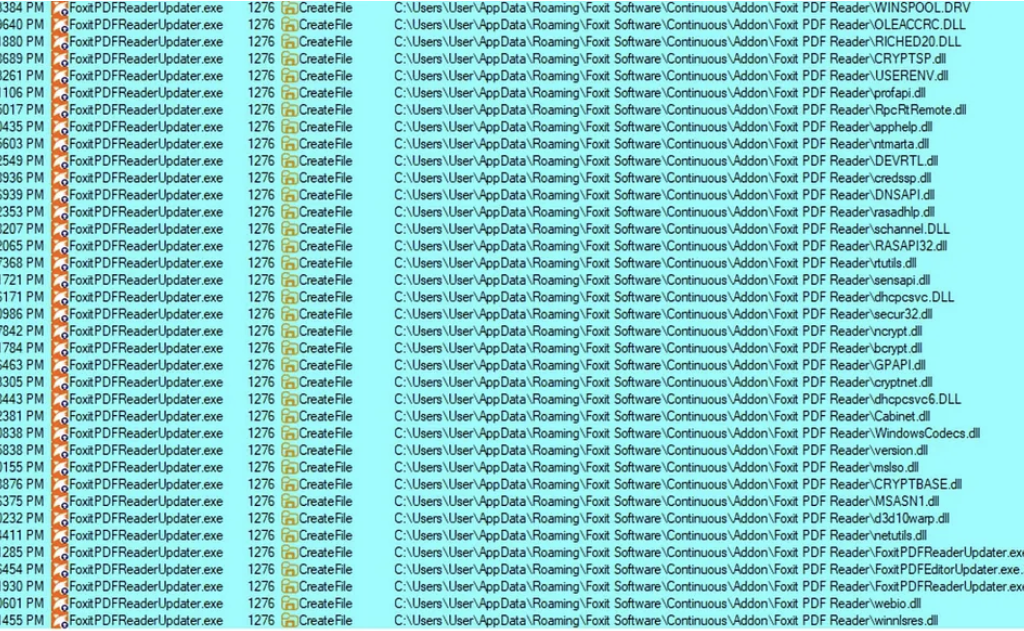
Privilege Escalation844 A comprehensive technical analysis of CVE-2026-57239, a privilege escalation vulnerability in Foxit PDF Reader that allows unprivileged users to escalate to NT…
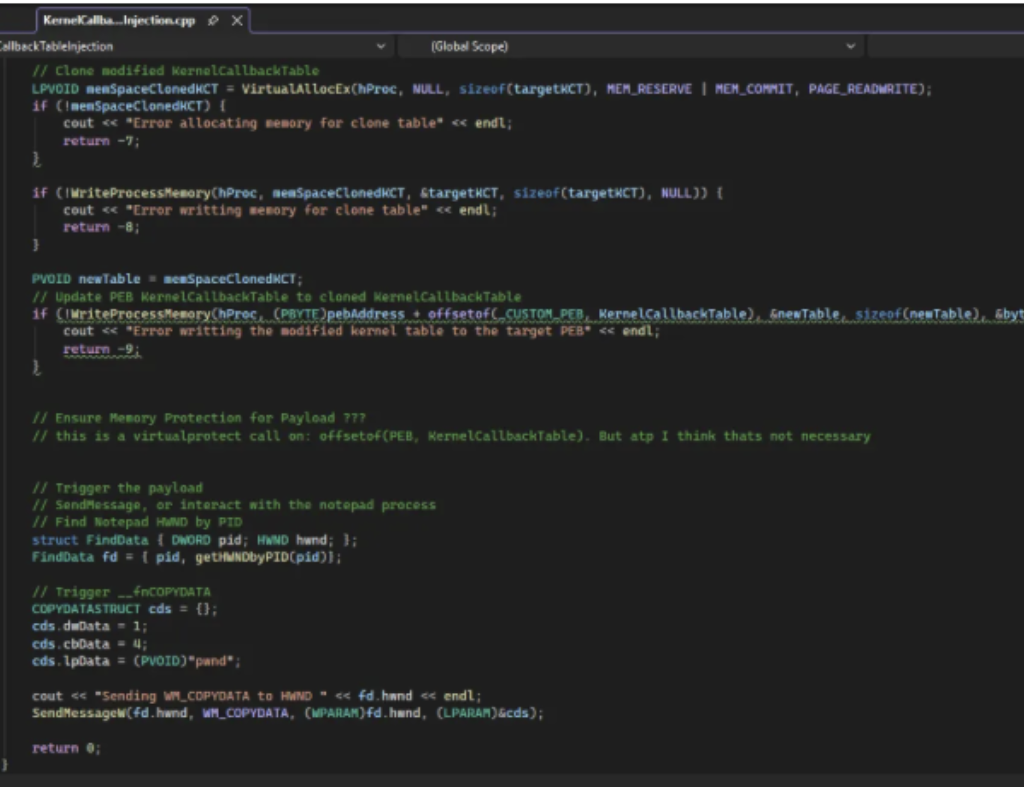
Uncategorized716 Deep dive into KernelCallbackTable process injection, a technique that abuses the PEB's callback table to intercept and redirect Windows message handling, achieving…
RCE721 Technical breakdown of OnlyShells — a five-vulnerability chain in ONLYOFFICE Desktop Editors combining zero-click XSS, a Chromium V8 RCE, and an update-service…
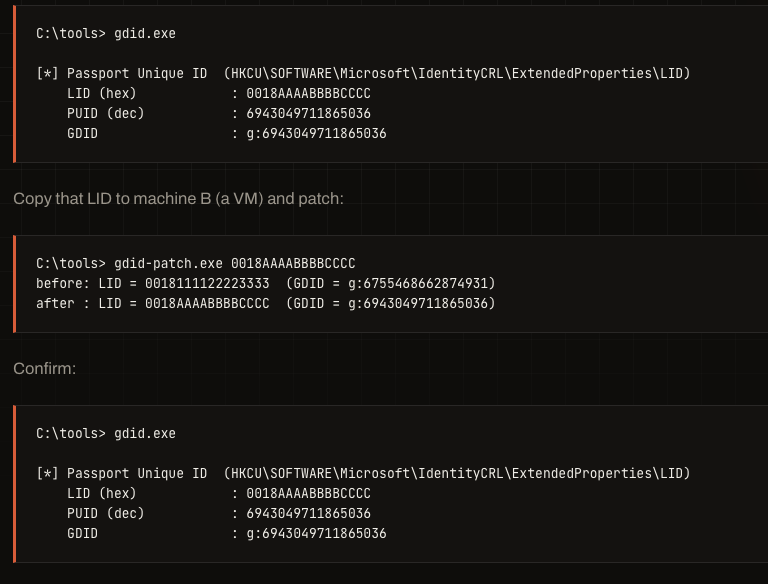
windows1.5k Deep technical analysis of Windows Global Device Identifier (GDID), a persistent 64-bit device identifier stored in HKCU and used by Microsoft for…
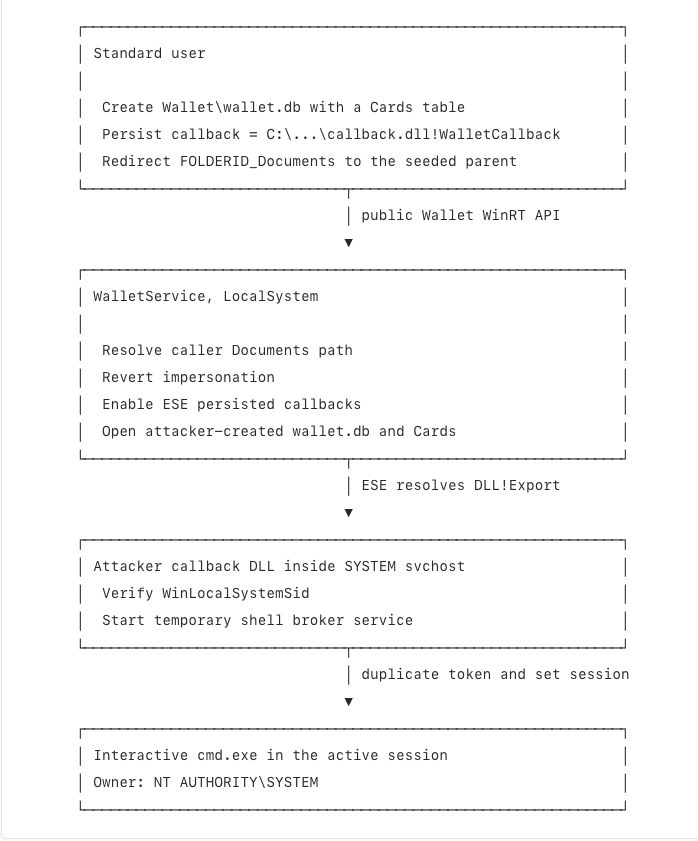
Vulnerability Analysis1.9k A detailed technical analysis of CVE-2026-49176, a local privilege escalation vulnerability in Windows WalletService that allows standard users to achieve SYSTEM access…
Malware673 Comprehensive analysis of SolidPDFCreator.dll, a Mustang Panda stage-1 backdoor targeting India. This DLL-based loader drops malicious payloads to C:ProgramDataIDMlogs, registers persistent scheduled…
Exploit Development613 CVE-2026-58629 is a double-fetch bug in the Windows graphics kernel (dxgkrnl). When D3DKMTCreateAllocation rolls back a failed create, it re-reads a user-controlled…