attaks209 Crimes against NTDLL – Implementing Early Cascade Injection
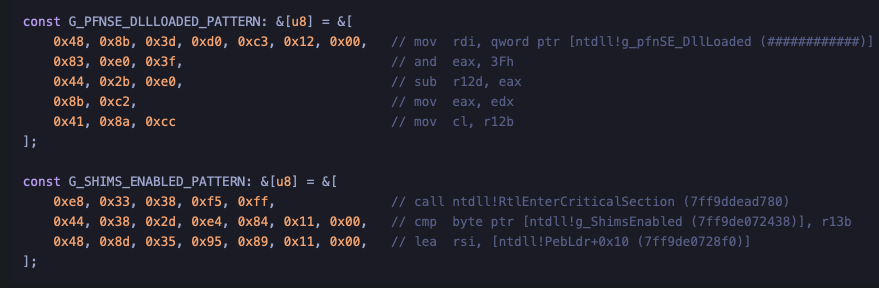
How to implement Early Cascade Injection in Rust, a stealthy Windows process injection technique that hijacks shim engine callbacks in ntdll to…
attaks209 How to implement Early Cascade Injection in Rust, a stealthy Windows process injection technique that hijacks shim engine callbacks in ntdll to…
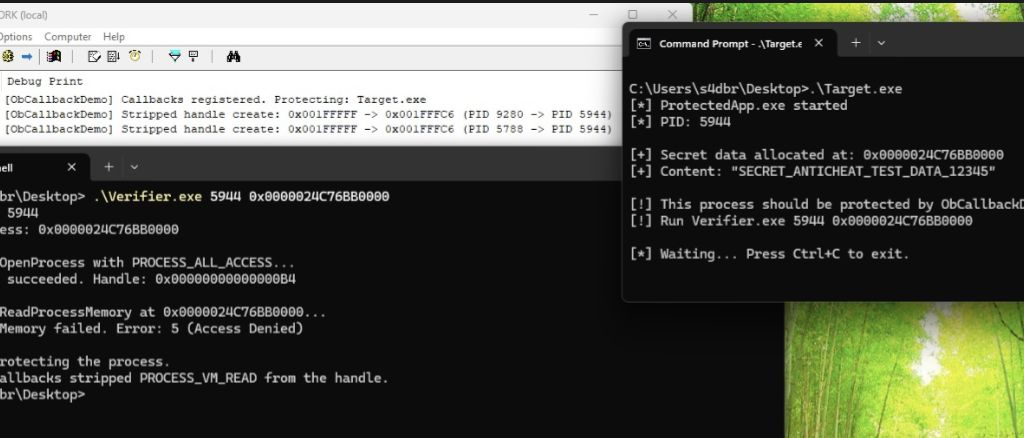
Debug721 The article explains how modern kernel-level anti-cheat systems work, describing their driver architecture, callbacks, memory monitoring, and detection methods used to identify…
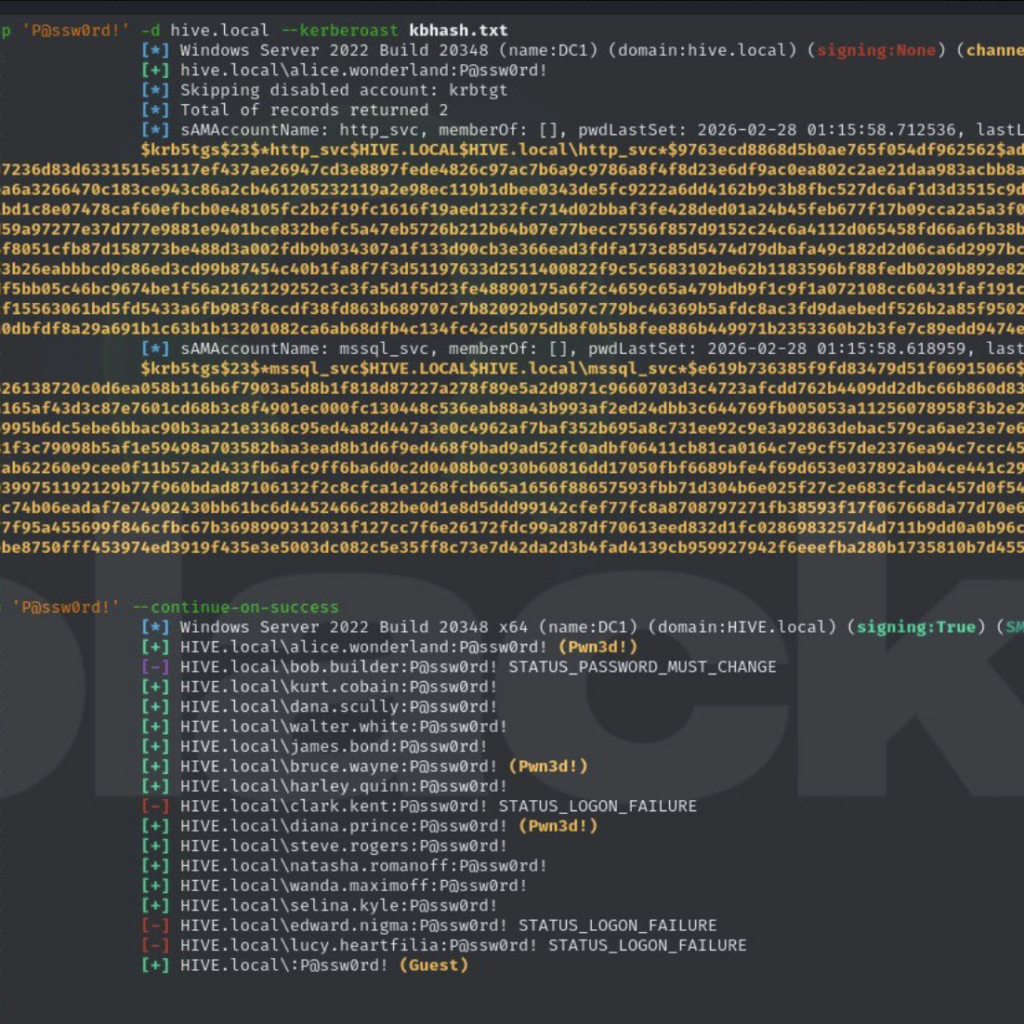
Active Directory285 This article analyzes an Active Directory attack chain where password spraying reveals valid credentials, privileged accounts enable escalation, and Kerberoasting exposes service…
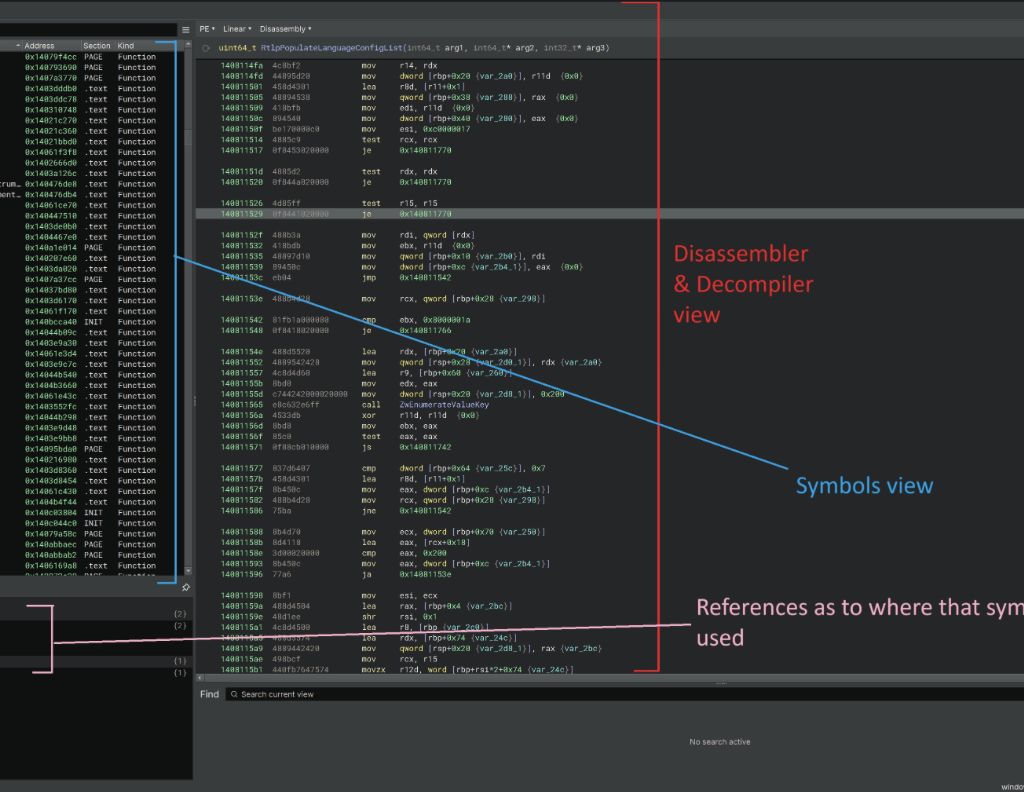
Antivirus391 This article demonstrates how to reverse engineer the Windows 11 kernel to understand undocumented internals behind memory operations and ETW Threat Intelligence…
Bypassing192 “Silent Harvest” explains how attackers can quietly extract sensitive Windows secrets such as credentials and security keys by abusing legitimate registry and…
Escalation230 The article explores a red-team research project called “RegPwn,” showing how weaknesses in Windows registry handling can be abused to achieve privilege…
Telegram218 It’s great to see that our website now has its own Telegram channel! Follow us at @core-jmp.org to stay updated with the…
Bluetooth188 Reverse engineering a Bluetooth printer server reveals multiple security flaws, including exposed debug interfaces and insecure GATT services, enabling unauthenticated remote code…
Bluetooth174 Reverse engineering a cheap smartwatch and reviving the classic “blinkenlights” attack to extract firmware through screen update patterns, revealing weaknesses in OTA…
firmware346 The article explains how to reverse engineer embedded firmware using Ghidra, covering techniques for loading firmware, identifying CPU architectures, analyzing functions, and…
BYOVD513 The article explains how attackers exploit a vulnerable signed driver (BYOVD) to obtain a kernel read/write primitive. It shows how unsafe IOCTL…
Hardware160 The article demonstrates how Ethernet traffic can be passively intercepted at the physical layer using simple tools like alligator clips attached to…
access282 The article analyzes a technique that disables Microsoft Defender by modifying file ACLs to block security services from accessing critical system DLLs.…
Cache327 The article explains why modern CPUs use multiple cache levels (L1, L2, L3) instead of a single large cache. It discusses the…
cpp215 Demonstration how malware can encrypt and decrypt payloads using the Discrete Fourier Transform (DFT). It provides a simple C example showing how…
ASM170 Reverse engineering a vintage hardware copy-protection dongle used by 1980s enterprise software. By analyzing the DOS program and emulator environment, the author…
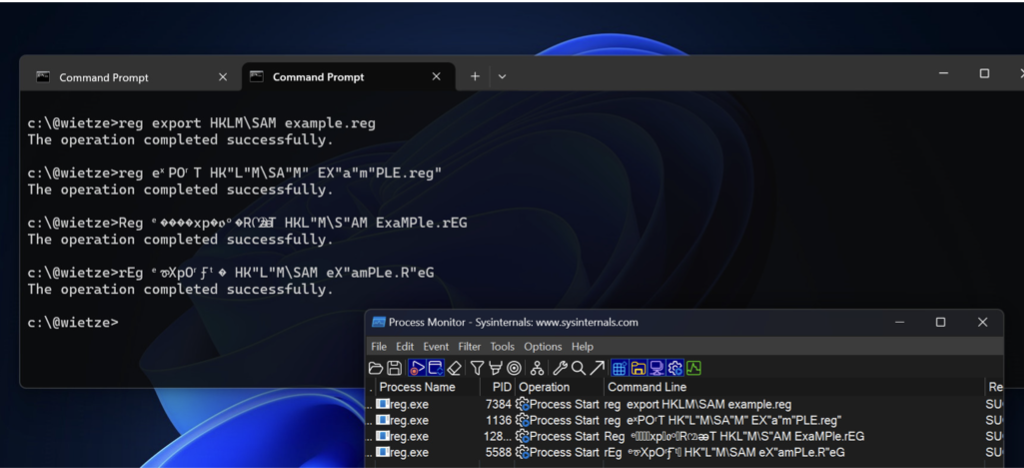
Antivirus381 How attackers can bypass AV and EDR detections by obfuscating command-line arguments. By exploiting parsing quirks in executables, small changes to parameters…