 EDR768
SyscallRevenant: Clean Indirect Syscalls with Trap-Flag Tracing
Clean indirect syscalls on Windows x64. It single-steps a hooked ntdll stub with the CPU trap flag to learn the live System…
oxfemale·
Oct 19·
31 min
·768
EDR768 Clean indirect syscalls on Windows x64. It single-steps a hooked ntdll stub with the CPU trap flag to learn the live System…
 Exploit Development853
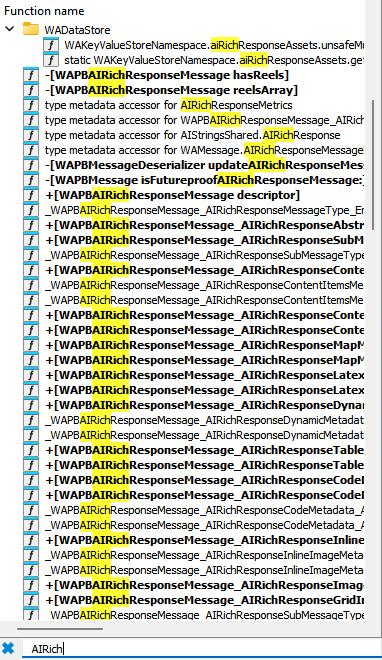
CVE-2026-23866 described incomplete validation of WhatsApp AI-rich Instagram Reel messages that could make another device fetch an arbitrary URL. numb3rs used only…
 Embedded660
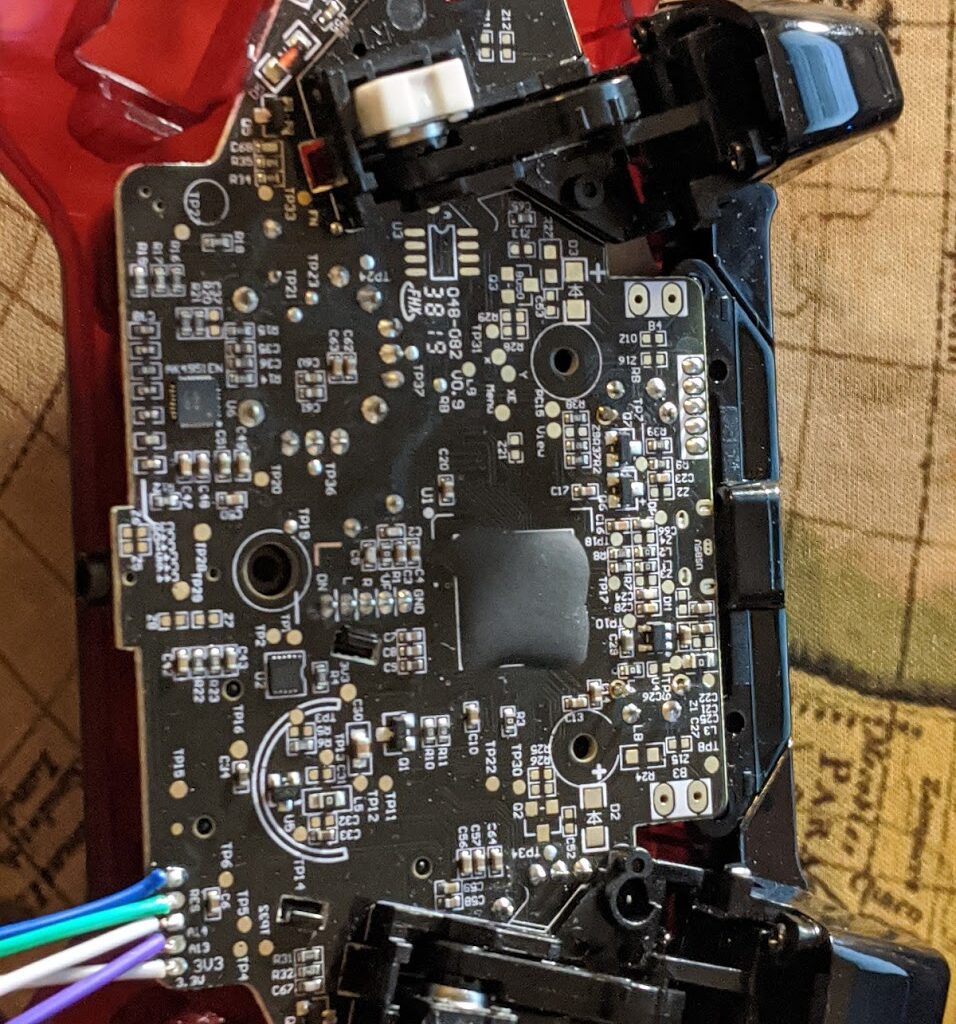
STM32F401 Xbox One controller from “we have SWD” to a live CoreSight instruction trace. ETM and TPIU are programmed from OpenOCD, SWO…
 Cisco984
Cisco published CVE-2026-76504, a critical authentication bypass in Catalyst SD-WAN Manager. Landon Rice at VulnCheck showed that a single percent-encoded POST to…
 Embedded711
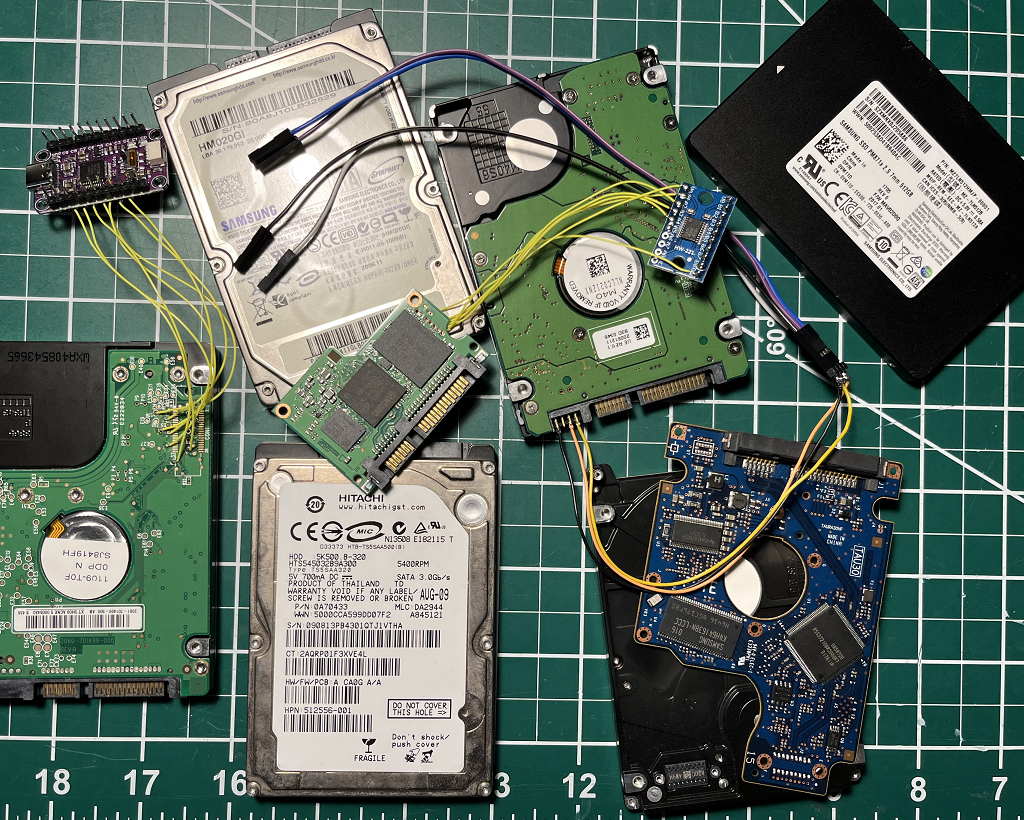
Ryan Miceli (grimdoomer) dumps WD and Samsung drive firmware, debugs a live HDD over JTAG, hot-patches overlay RAM to stall DMA READ…
 Exploit Development568
Joe Grand (Kingpin) reverse-engineered a real Ledger Nano X hardware implant for HARDWEAR.IO 2026 in Santa Clara. The add-on board does not…
 Exploit Development579
Simon Koeck's Google DevSite write-up: a pre-auth Flask session cookie on developers.google.com carried a pickled OAuth flow whose client_secret was also the…
 Command Injection1.5k
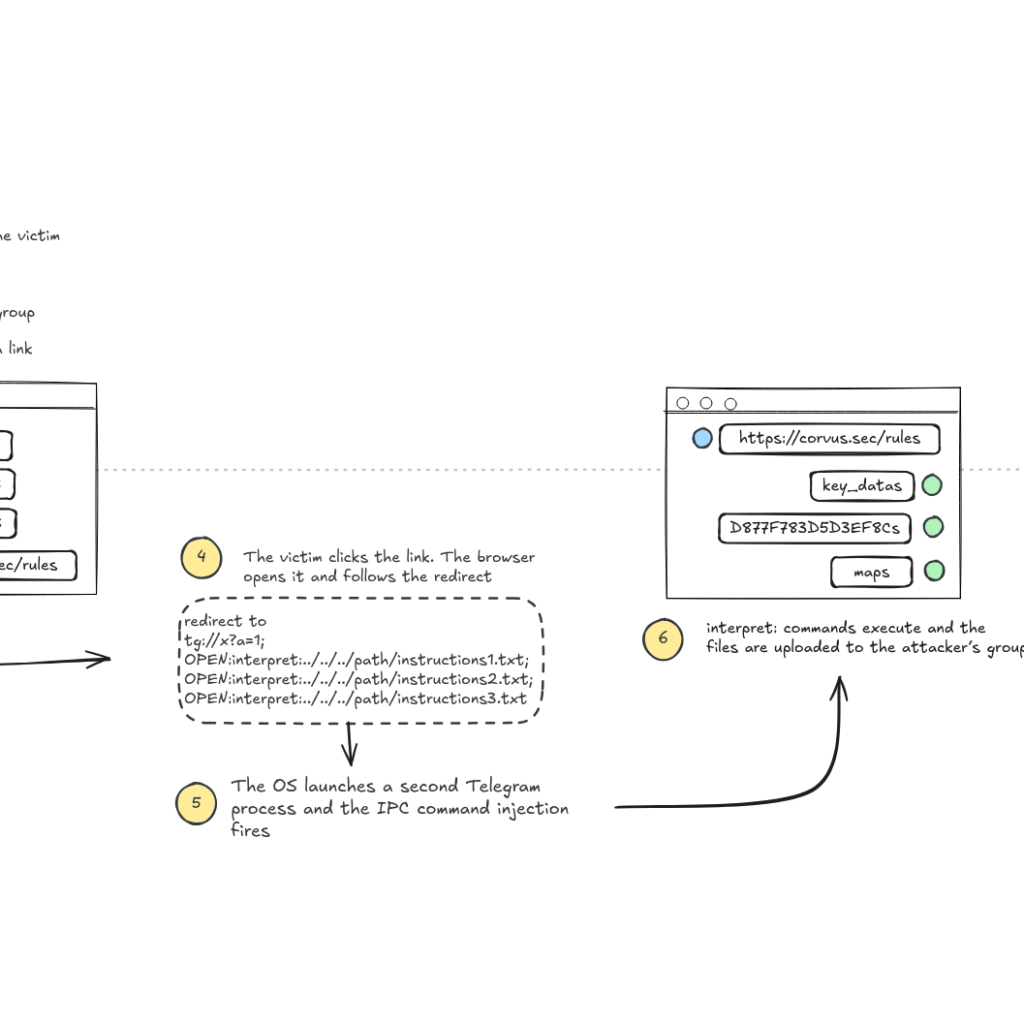
BeakSec's CVE-2026-107181: Telegram Desktop through 7.2.8 handed clicked links to the running instance over a local socket and never escaped the semicolon…
 AnyDesk589
AnyPwn is a pre-approval remote code execution bug in AnyDesk Linux 8.0.2. The session protocol's mode-5 handler trusts a remote payload length,…
 kernel1.7k
Aftermath Labs statically recover 815 of 865 Tencent-VM virtualized functions across four ACE kernel drivers (94.2 percent). Architecture, CET RDSSPQ/INCSSPQ, phantom SEH…
 AI Agents938
Eddie Zhang / Project Black: Claude refuses an LSASS dumper; DeepSeek builds one EDR still catches; uncensored Qwen 3.8 27B on two…
 RCE777
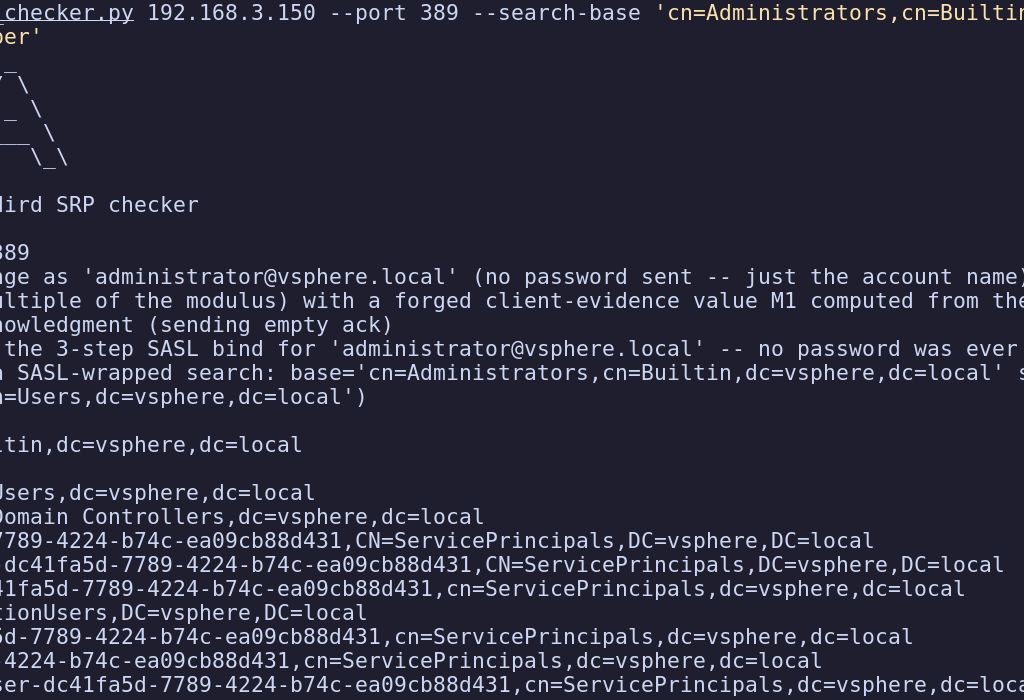
Mobeta patch-diff of VMSA-2026-0006: vCenter 8.0.3 syslog dynafile traversal (CVE-2026-59310) and SASL SRP A=N auth bypass (CVE-2026-59309), both pre-auth 9.8. Templates, Ghidra,…