
 EDR485
SyscallRevenant: Clean Indirect Syscalls with Trap-Flag Tracing
Clean indirect syscalls on Windows x64. It single-steps a hooked ntdll stub with the CPU trap flag to learn the live System…
oxfemale·
Oct 19·
31 min
·485
EDR485 Clean indirect syscalls on Windows x64. It single-steps a hooked ntdll stub with the CPU trap flag to learn the live System…
 Command Injection1.2k
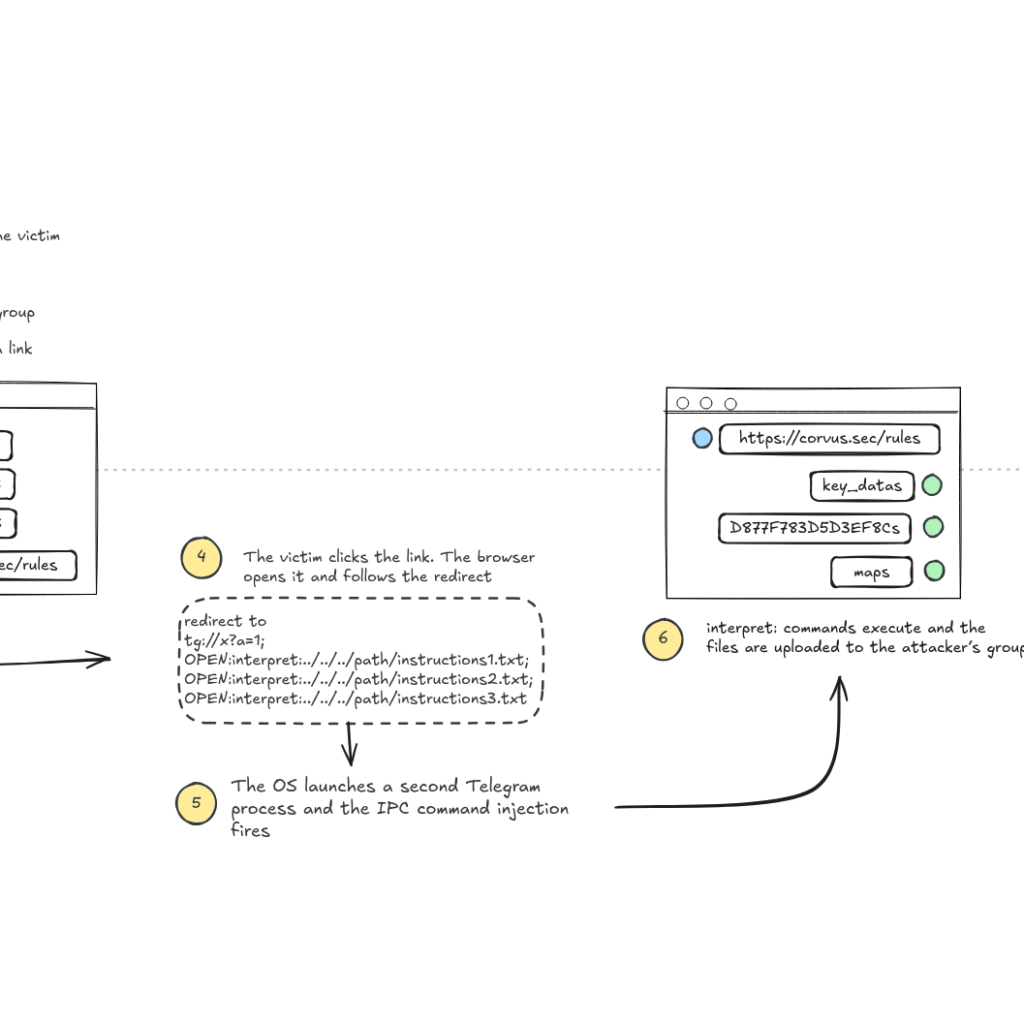
BeakSec's CVE-2026-107181: Telegram Desktop through 7.2.8 handed clicked links to the running instance over a local socket and never escaped the semicolon…
 kernel1.2k
Aftermath Labs statically recover 815 of 865 Tencent-VM virtualized functions across four ACE kernel drivers (94.2 percent). Architecture, CET RDSSPQ/INCSSPQ, phantom SEH…
 AI Agents733
Eddie Zhang / Project Black: Claude refuses an LSASS dumper; DeepSeek builds one EDR still catches; uncensored Qwen 3.8 27B on two…
 RCE529
Mobeta patch-diff of VMSA-2026-0006: vCenter 8.0.3 syslog dynafile traversal (CVE-2026-59310) and SASL SRP A=N auth bypass (CVE-2026-59309), both pre-auth 9.8. Templates, Ghidra,…
 RCE528
CVE-2026-65660 SharePoint EditingPageParser bypass via RegisterDirective.GetHtml quote rewrite, XamlServices memshell, and ToolPane on AddGallery.aspx for pre-auth RCE when anonymous view is on.…
 kernel708
Connor McGarr on ETW’s undocumented SecurityTrace bit: QUERY wants Antimalware-PPL, STOP does not, and a user-mode ControlTrace hook lets admin consume Threat-Intelligence…
 kernel1.1k
Asim Manizada’s four Linux LPEs: DirtyAH6, TUNderflow, PPPoEject, DiagSpill. Decade-old bugs, userns for three, DiagSpill needs only SCTP. Patch 5.10.270 / 6.6.157…
 Cisco931
Cisco Talos is tracking in-the-wild abuse of CVE-2026-20079 (FMC auth bypass, CVSS 10.0) and CVE-2026-20316 (static low-priv credentials, SIR High) on Cisco…
 Active Directory847
S12 points a notepad.exe File handle at ntds.dit, SYSTEM, and SECURITY on a live DC via BYOVD LowQword patch. No LSASS, no…
 kernel501
Patch EPROCESS.UniqueProcessId and every ETHREAD.Cid with a GIO kernel write, and Sysmon attributes file, DNS and child-process events to Notepad. PspCidTable still…
 kernel1.3k
Lazarus spent a Windows kernel zero-day in afd.sys on a fake recruiter PDF. CVE-2026-68820 is a local UAF that skips BYOVD controls;…