RPC522 Automating MS-RPC vulnerability research
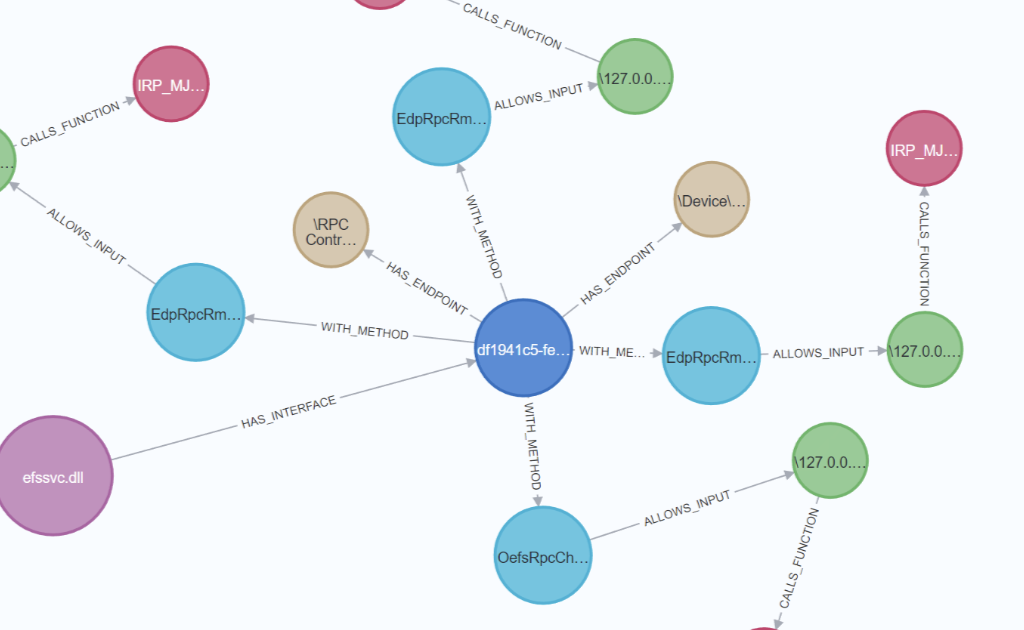
Automating MS-RPC research shows how NtObjectManager, dynamic RPC clients, fuzzing, canary tracing, ProcMon and Neo4j can map interfaces, test procedures, find crashes…
RPC522 Automating MS-RPC research shows how NtObjectManager, dynamic RPC clients, fuzzing, canary tracing, ProcMon and Neo4j can map interfaces, test procedures, find crashes…
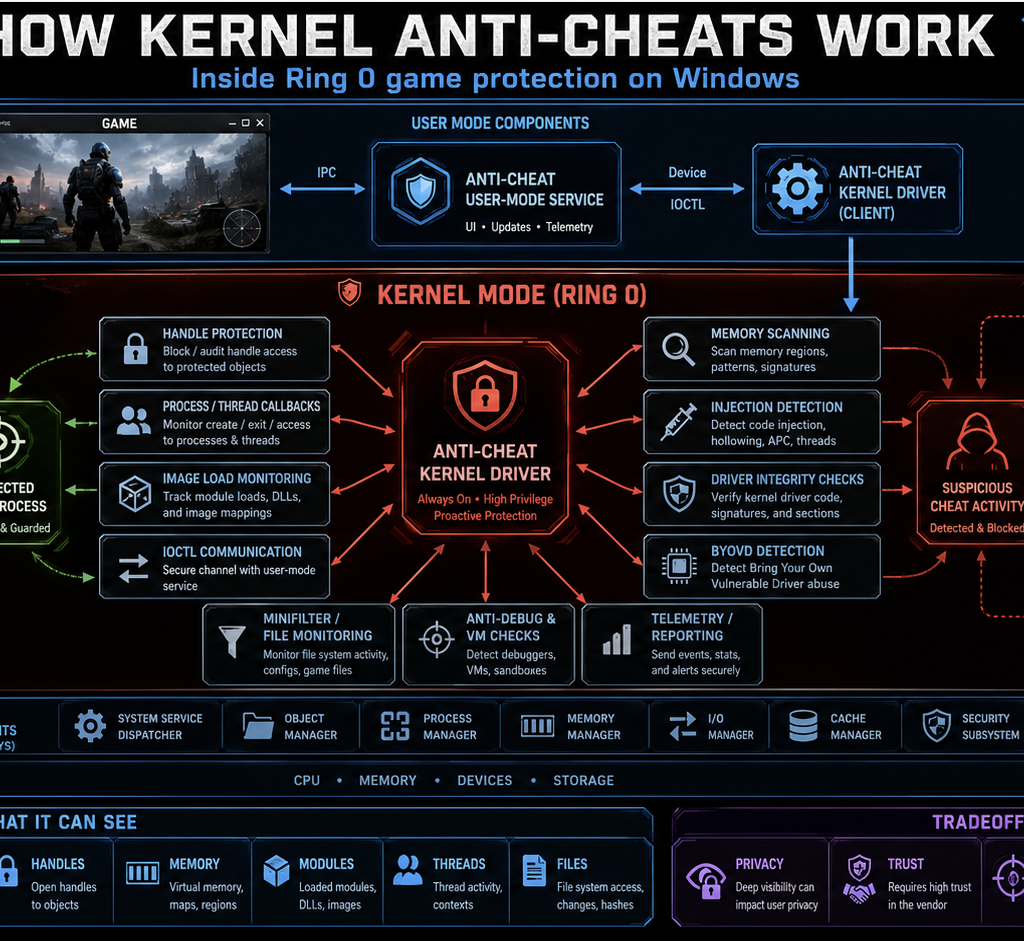
BYOVD2.3k The article explains how kernel anti-cheats monitor games from Ring 0 using callbacks, handle filtering, memory scans, driver checks, anti-debugging, VM detection,…
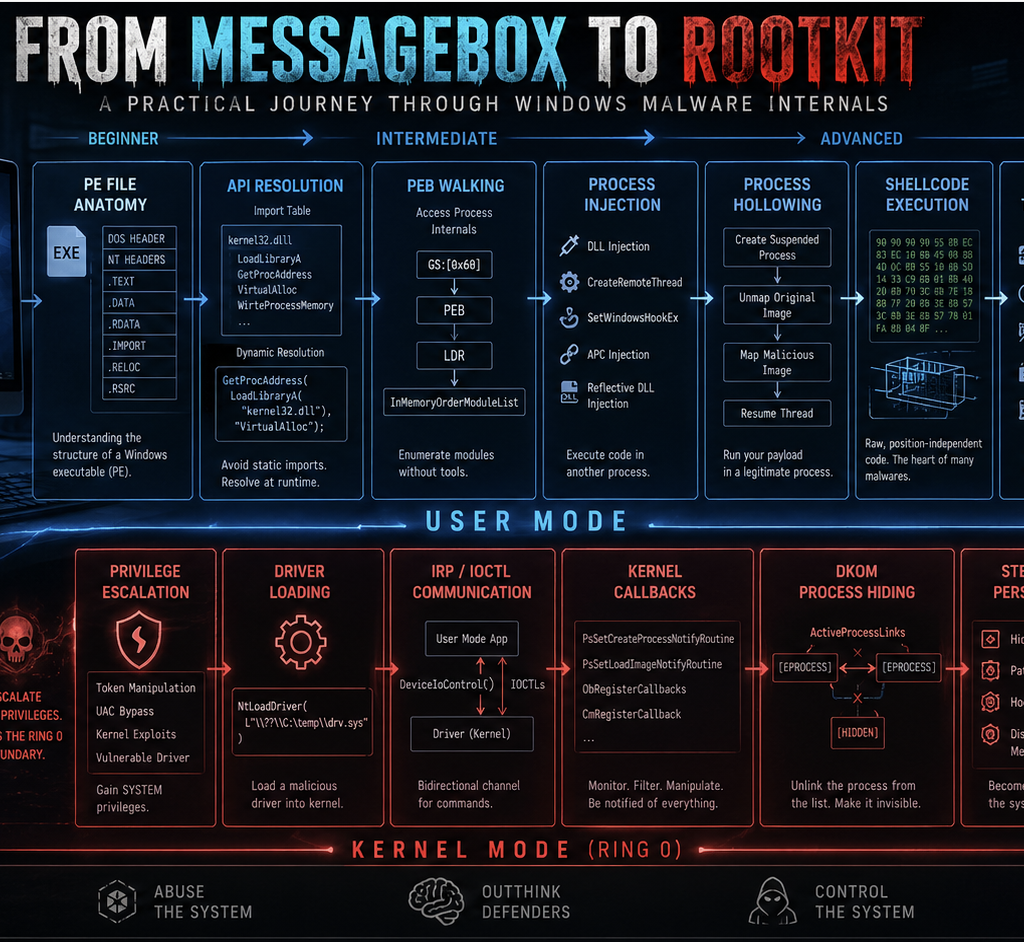
APC543 The article walks through Windows malware development from dynamic API resolution and PEB walking to injection, APC execution, driver basics, DKOM process…
Defender425 This vulnerability shows how Windows Defender file handling can be abused through filesystem races, Cloud Files APIs, and reparse points to redirect…
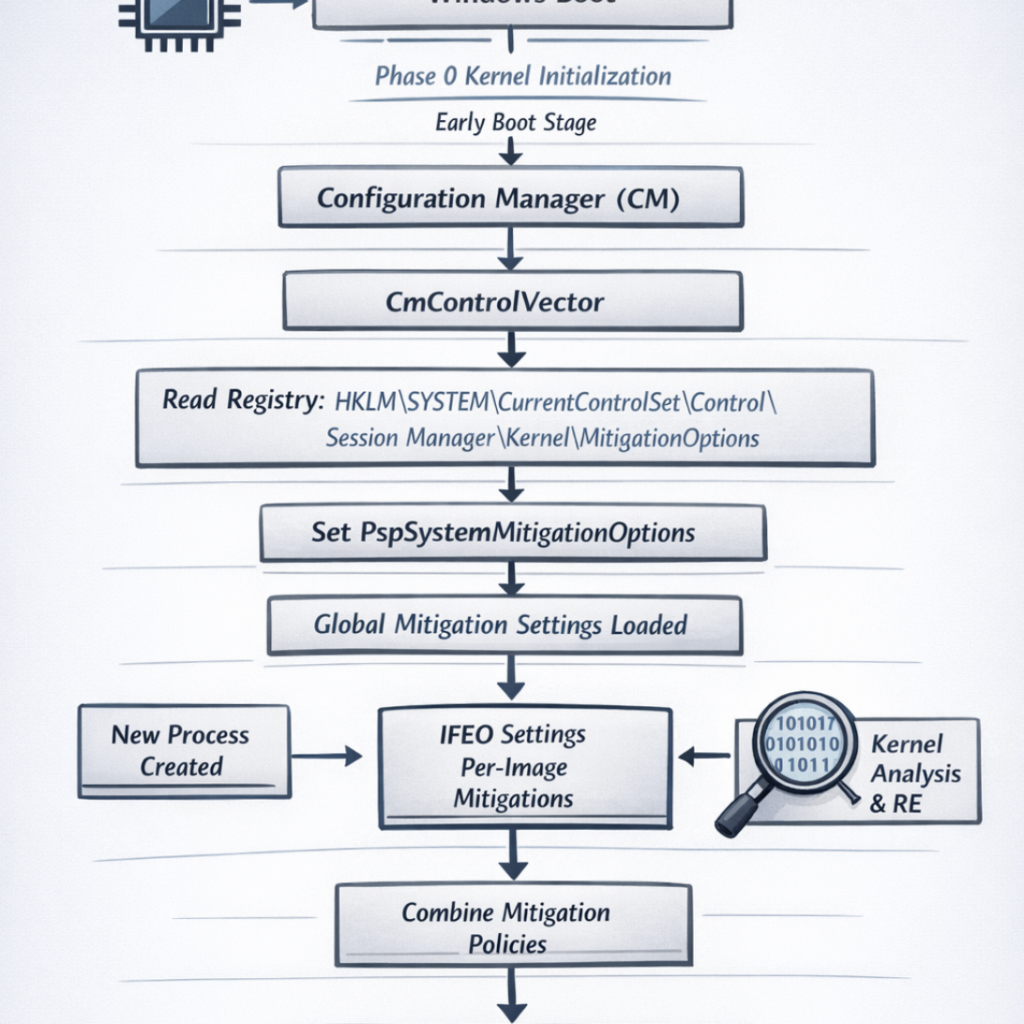
kernel270 The article explores how Windows loads system-wide exploit mitigation settings during early boot via CmControlVector, populating PspSystemMitigationOptions, which later influences process security…
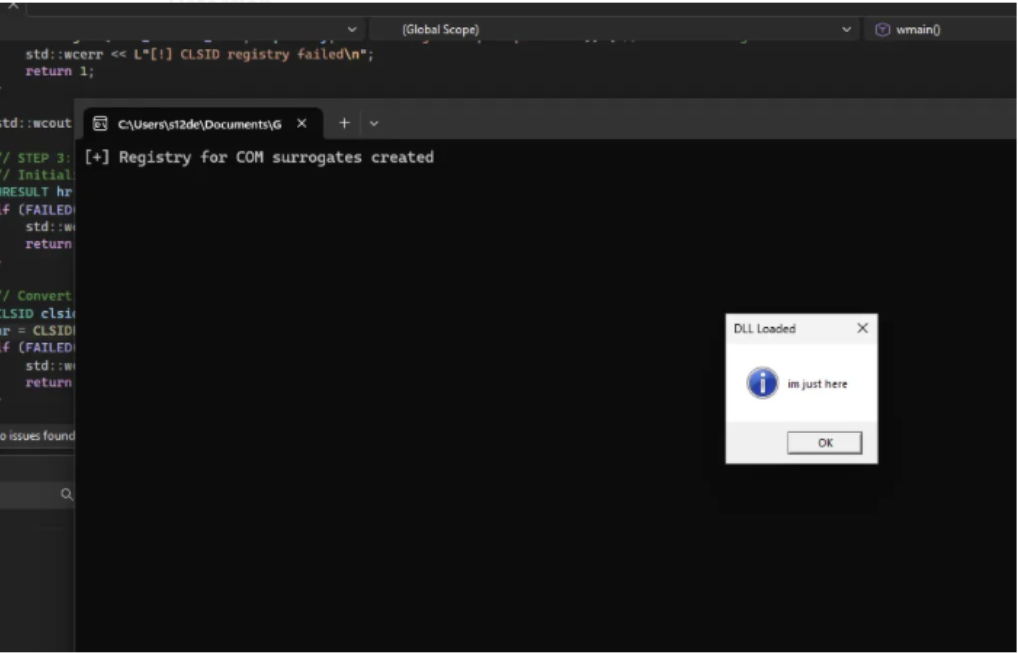
Bypassing927 COMouflage is a stealthy Windows injection technique that abuses COM DLL Surrogates to execute malicious DLLs inside dllhost.exe, making svchost.exe appear as…
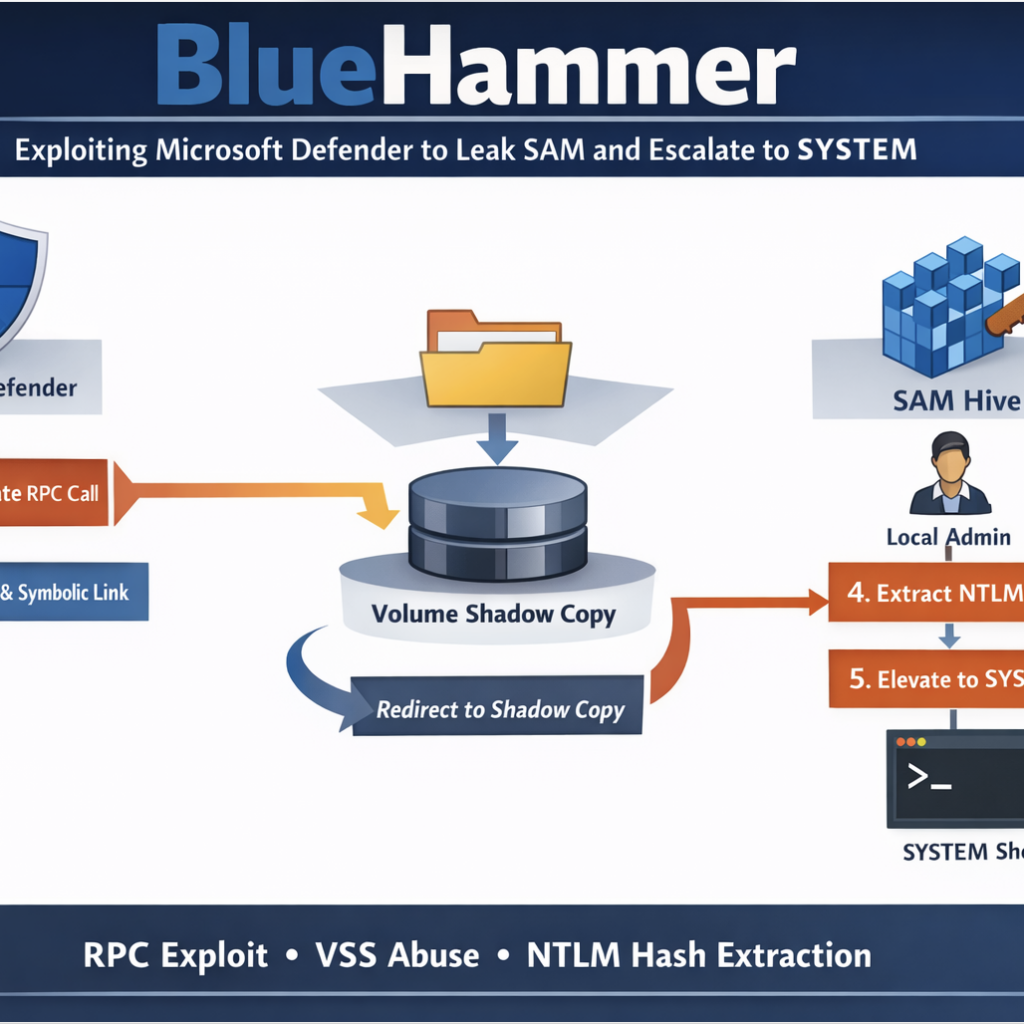
Antivirus451 BlueHammer shows how Microsoft Defender’s update workflow can be abused to redirect privileged file access to a Volume Shadow Copy. By exploiting…
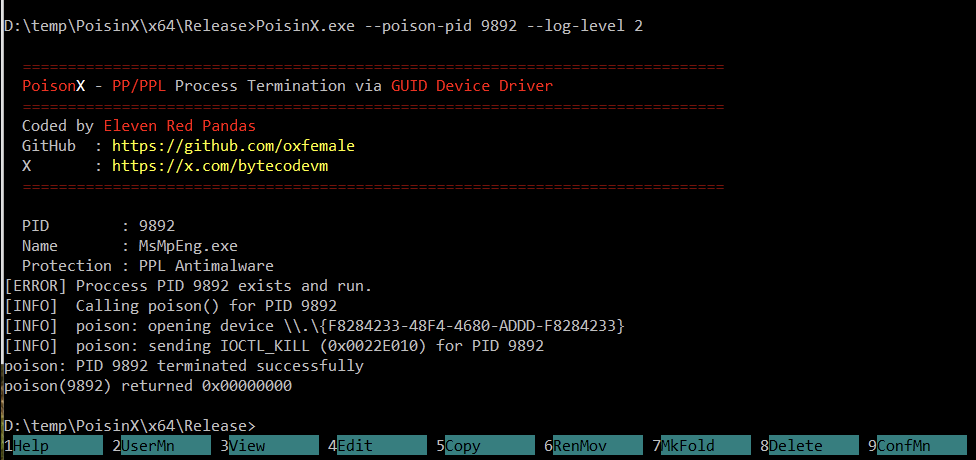
BYOUD1.2k PoisonX is a Bring Your Own Vulnerable Driver (BYOVD) research tool that leverages a signed Microsoft kernel driver to terminate any Windows…
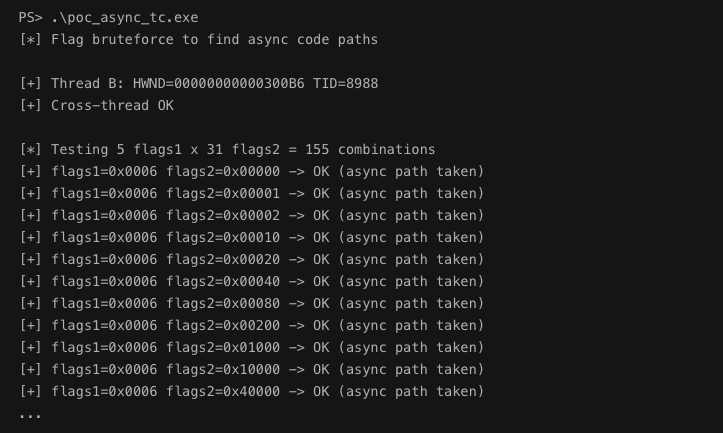
Driver325 The article analyzes a Win32k type confusion vulnerability in the async window action path of win32kfull.sys. Improper handling of window objects can…
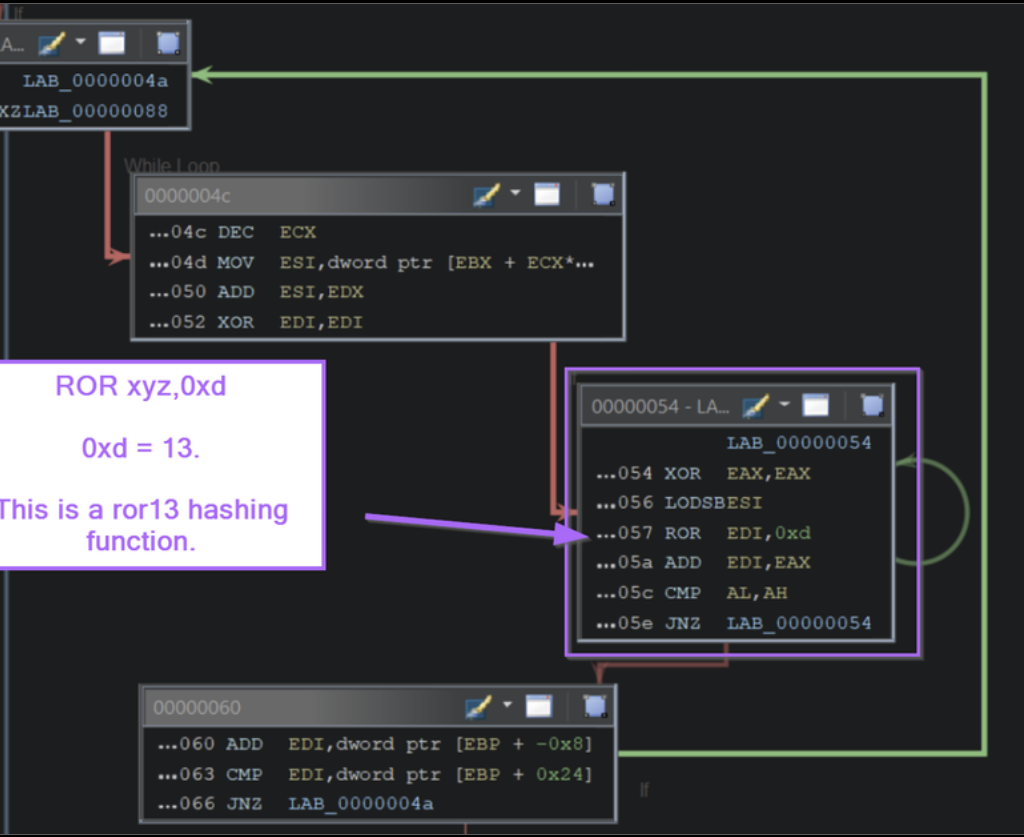
Debug384 The article demonstrates how to analyze Windows shellcode in Ghidra by identifying API-hashing routines, resolving hidden Windows API calls, and extracting C2…
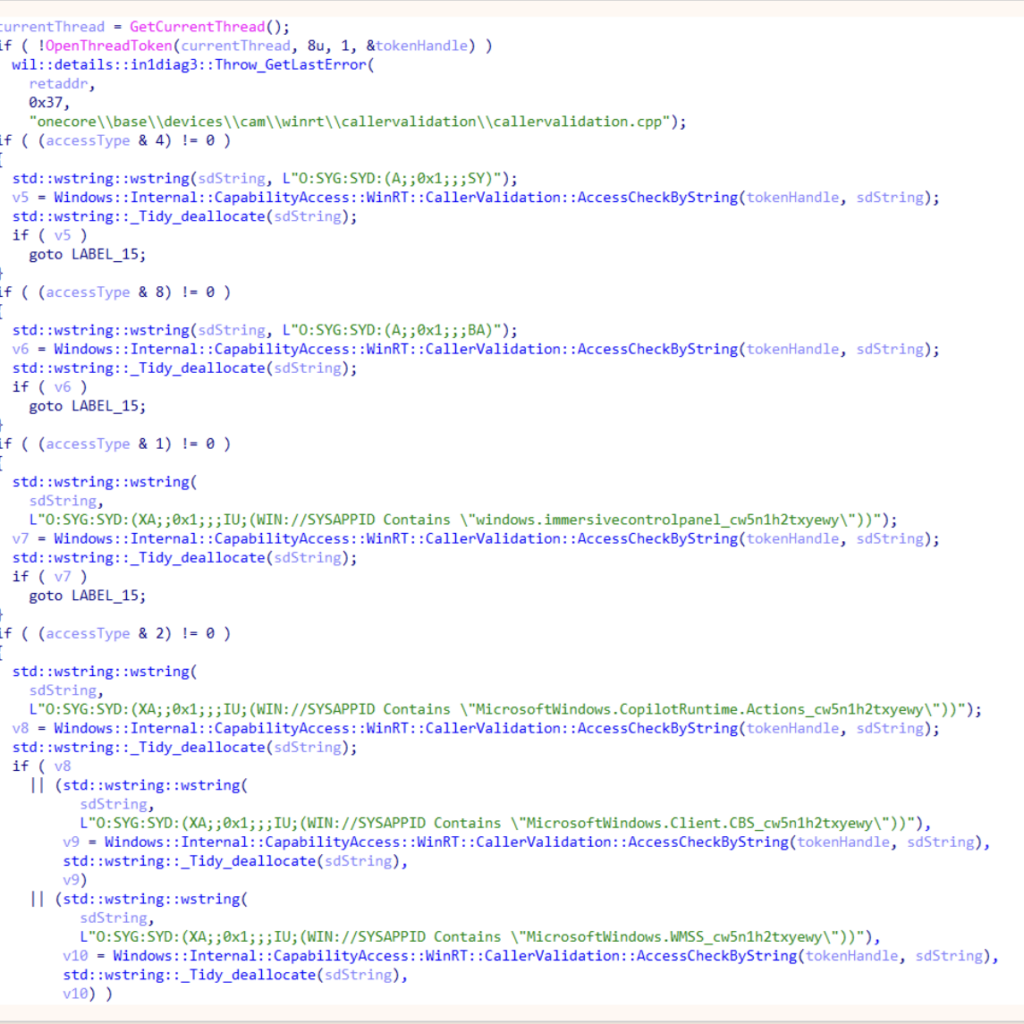
AI Agents327 The article explains Microsoft’s ODR mechanism for native MCP registration, enabling AI agents to discover and invoke system tools through the Model…
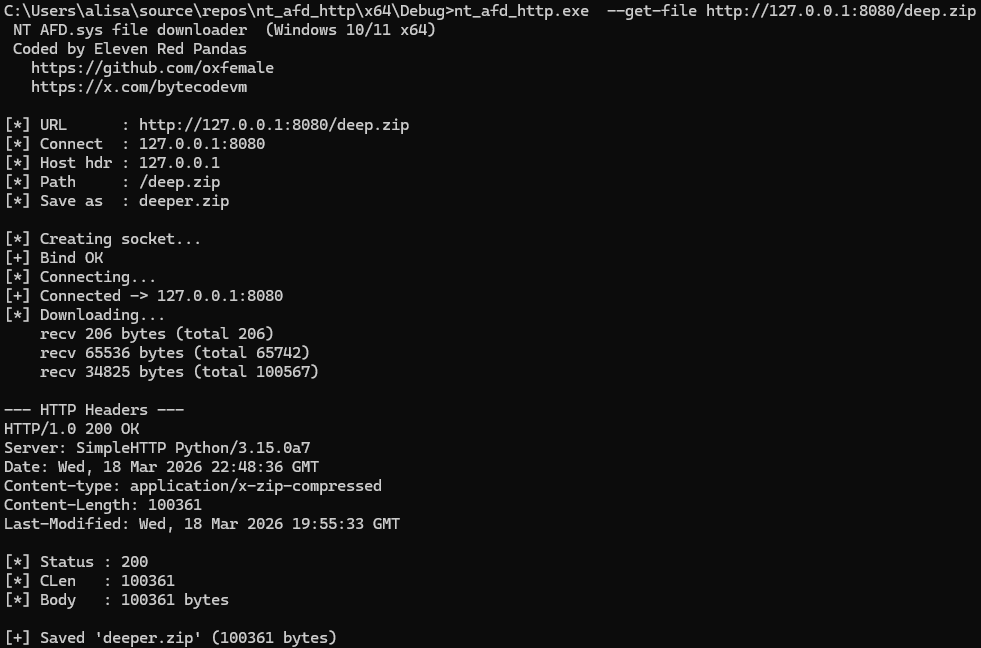
Bypassing389 The article demonstrates how to bypass the Winsock layer by communicating directly with the Windows AFD driver using Native API calls. It…