BSoD257 Won’t Fix: Kernel DoS in clfs.sys via NULL FastMutex Dereference
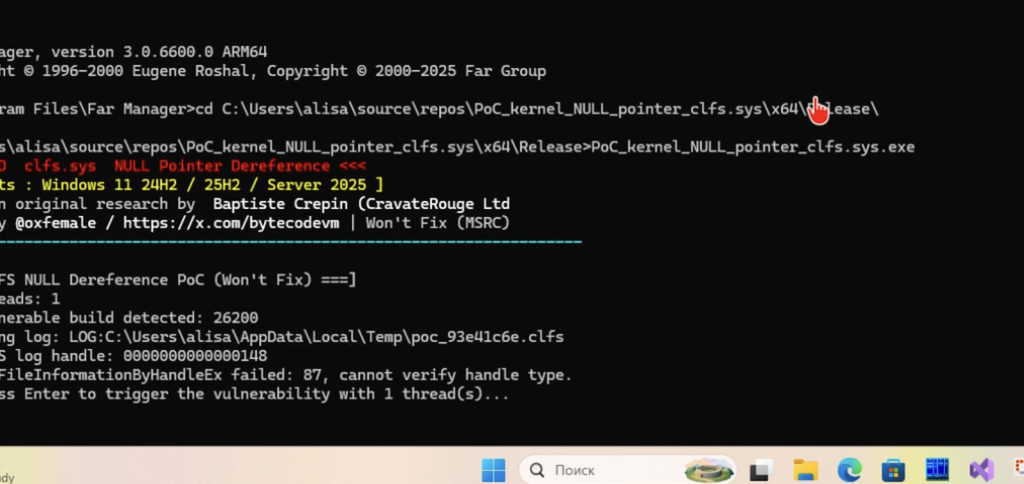
The article examines a Windows kernel bug in clfs.sys where a NULL pointer is dereferenced during fast mutex acquisition, causing a kernel…
BSoD257 The article examines a Windows kernel bug in clfs.sys where a NULL pointer is dereferenced during fast mutex acquisition, causing a kernel…
COM356 The article demonstrates how to hook COM methods in Windows Subsystem for Linux by leveraging C++ RTTI metadata to reconstruct class layouts…
cpp552 The research reverse-engineers Windows AFD.sys, showing how TCP sockets can be created, connected, and used by sending handcrafted IOCTL requests directly to…
Bypassing222 The article introduces LOLExfil, a Living-Off-the-Land data exfiltration technique that abuses legitimate system tools and trusted services to stealthily extract data, blending…
Cortex XDR909 Research shows how Palo Alto Cortex XDR predefined BIOC behavioral rules can be decrypted and analyzed. By understanding rule logic and built-in…
Debug1.4k The article explains a technique for dumping memory from the protected LSASS process (PPL). It analyzes limitations of PPL protection and demonstrates…
attaks255 How to implement Early Cascade Injection in Rust, a stealthy Windows process injection technique that hijacks shim engine callbacks in ntdll to…
Debug843 The article explains how modern kernel-level anti-cheat systems work, describing their driver architecture, callbacks, memory monitoring, and detection methods used to identify…
Active Directory318 This article analyzes an Active Directory attack chain where password spraying reveals valid credentials, privileged accounts enable escalation, and Kerberoasting exposes service…
Antivirus435 This article demonstrates how to reverse engineer the Windows 11 kernel to understand undocumented internals behind memory operations and ETW Threat Intelligence…
Bypassing235 “Silent Harvest” explains how attackers can quietly extract sensitive Windows secrets such as credentials and security keys by abusing legitimate registry and…
Escalation265 The article explores a red-team research project called “RegPwn,” showing how weaknesses in Windows registry handling can be abused to achieve privilege…