Cisco351 Blinding the Defenders: Inside Qilin’s EDR-Killer Malware
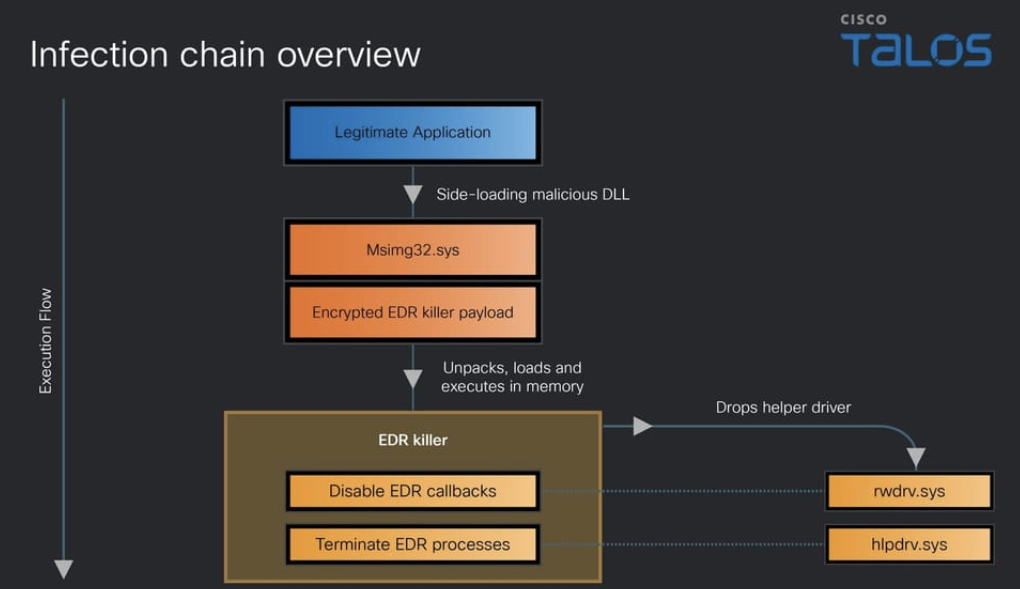
Cisco Talos analyzes a Qilin ransomware EDR-killer that disables over 300 security drivers. The multi-stage malware uses obfuscation and kernel-level techniques to…
Cisco351 Cisco Talos analyzes a Qilin ransomware EDR-killer that disables over 300 security drivers. The multi-stage malware uses obfuscation and kernel-level techniques to…
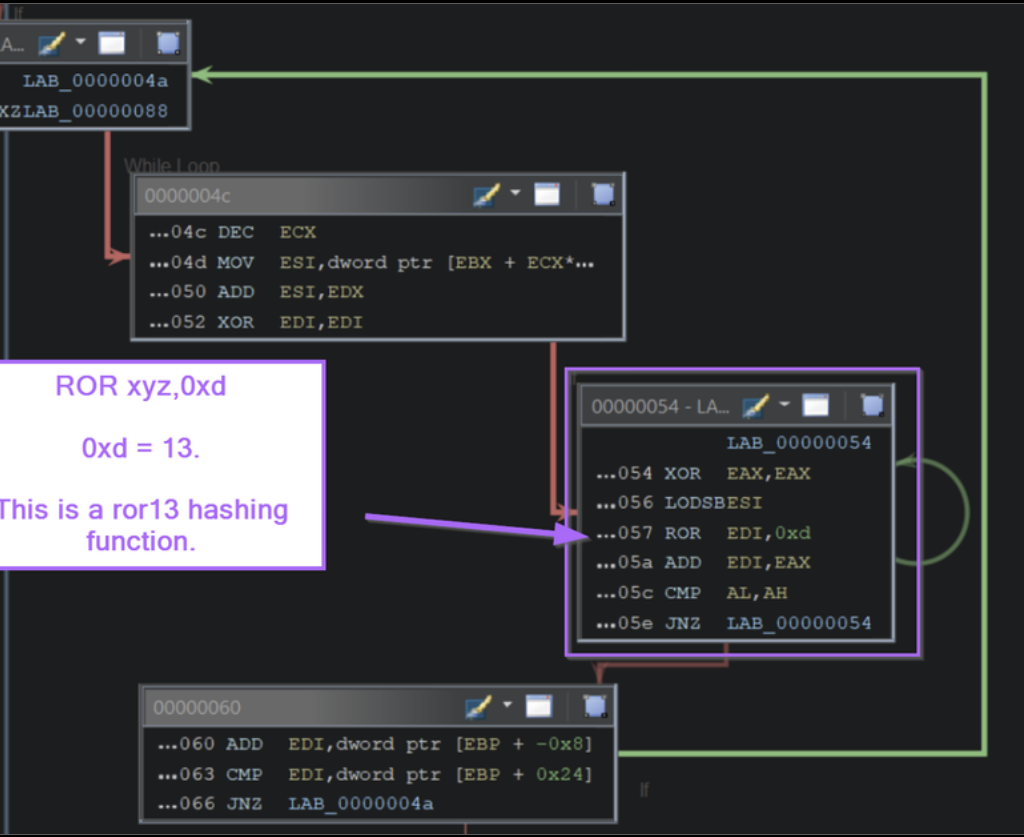
Debug385 The article demonstrates how to analyze Windows shellcode in Ghidra by identifying API-hashing routines, resolving hidden Windows API calls, and extracting C2…
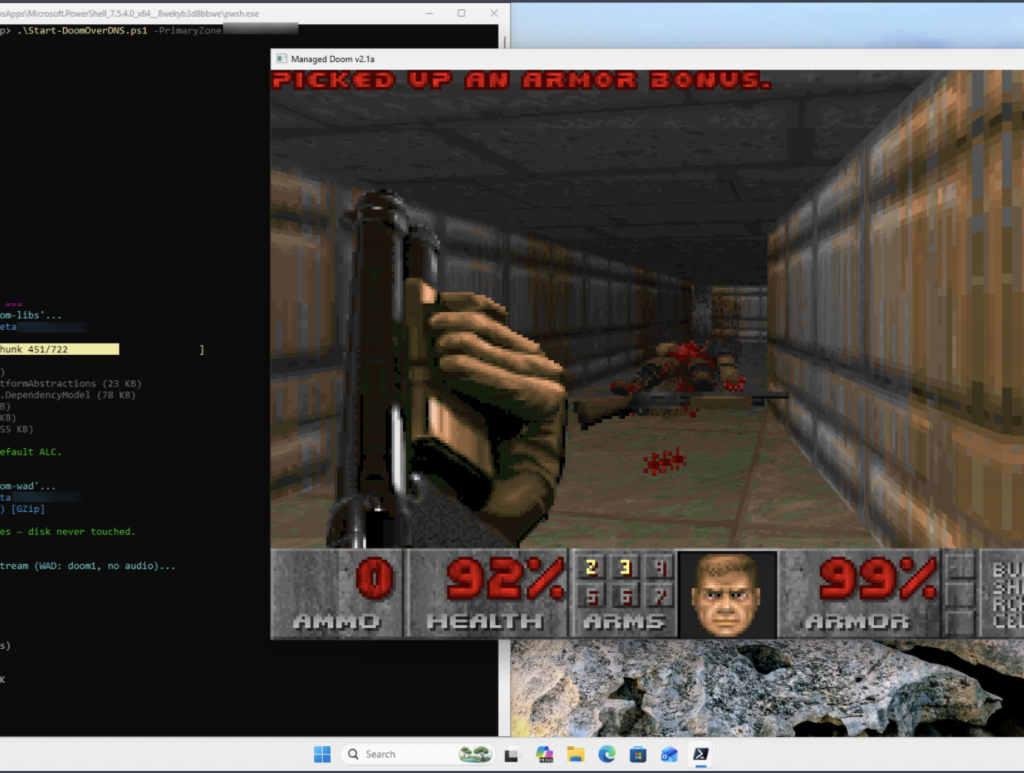
.NET4.5k The article shows a proof-of-concept where DOOM is stored across ~2,000 DNS TXT records and executed directly from memory. A PowerShell loader…
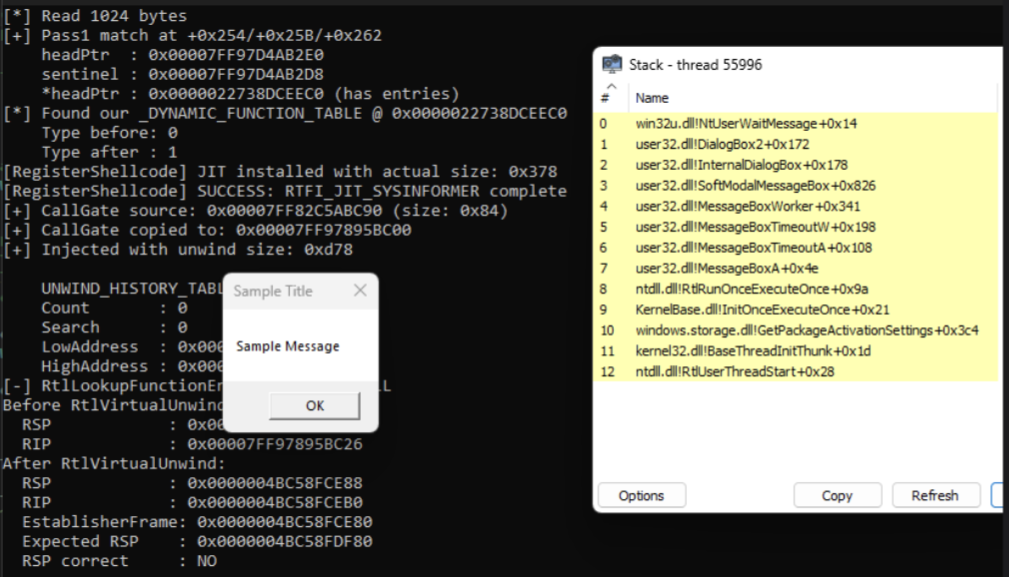
BYOUD334 The article introduces BYOUD, a Windows evasion technique that manipulates unwind metadata to spoof call stacks without altering return addresses, allowing malware…
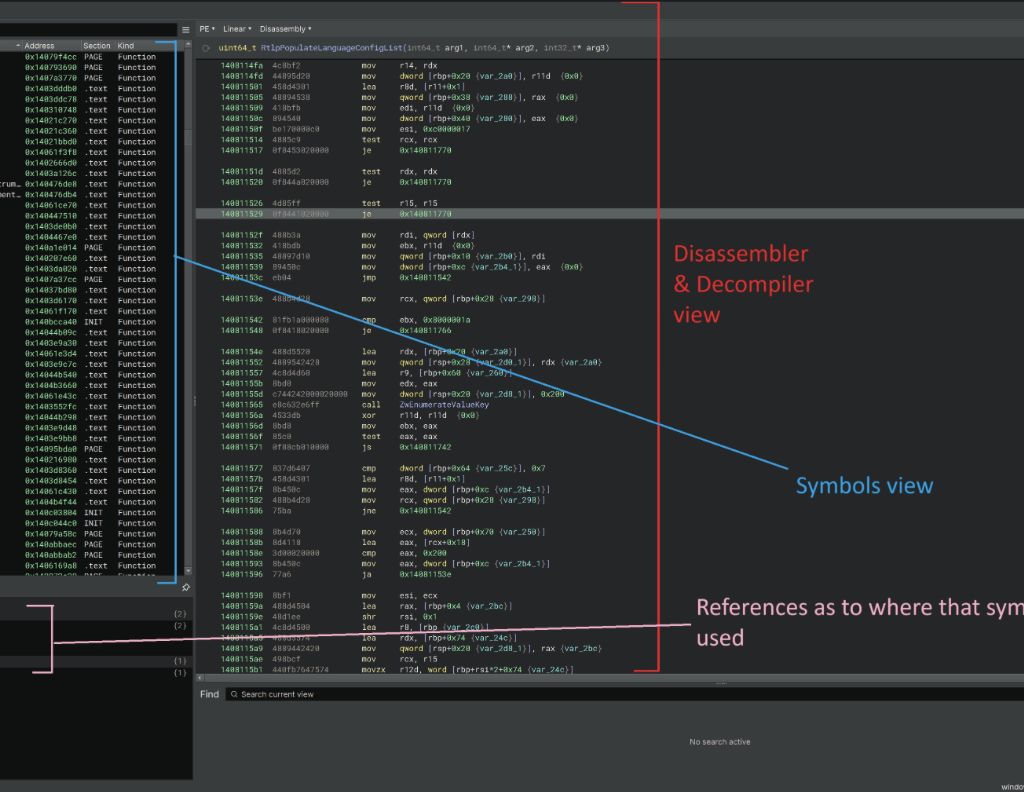
Antivirus435 This article demonstrates how to reverse engineer the Windows 11 kernel to understand undocumented internals behind memory operations and ETW Threat Intelligence…
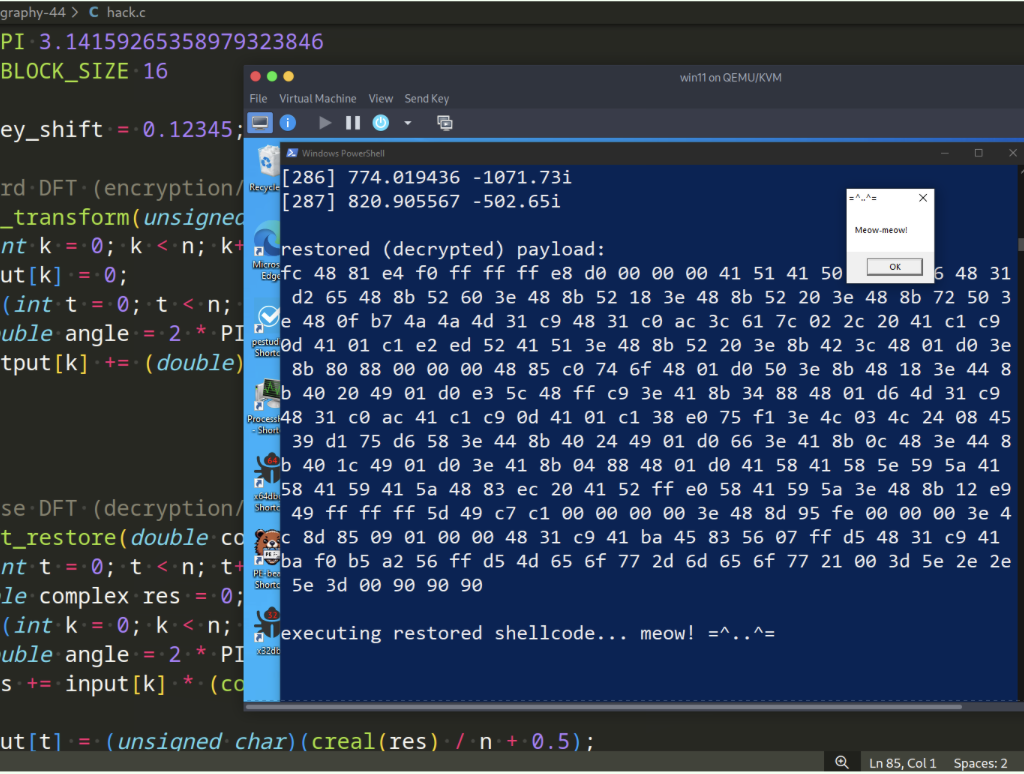
cpp254 Demonstration how malware can encrypt and decrypt payloads using the Discrete Fourier Transform (DFT). It provides a simple C example showing how…