Machine Learning62 From P-Code to GNN: Extracting Binary Code Semantics
Quarkslab’s pcode_graph lifts functions to Ghidra P-Code CDGs and a GINE embedding that matches GMN (AUC 0.87 XM) on Cisco-Talos, across ISA,…
Machine Learning62 Quarkslab’s pcode_graph lifts functions to Ghidra P-Code CDGs and a GINE embedding that matches GMN (AUC 0.87 XM) on Cisco-Talos, across ISA,…
iOS Security177 Yuval Hanoch Hirschenbein Sadde traced a DEF CON 34 demo crash to one character in XNU: unp_ino++ assigns inode 0 to the…
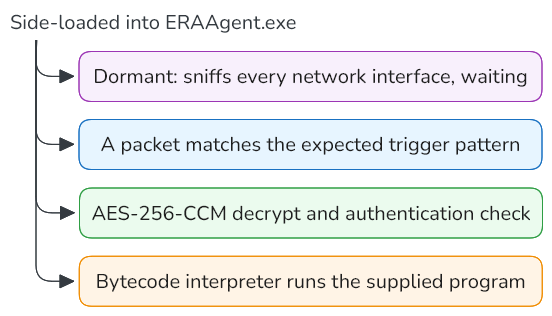
Malware549 SLEEPWALKER is a passive Windows backdoor that never beacons, opens no listening port and carries no payload. It side-loads into ESET Management…
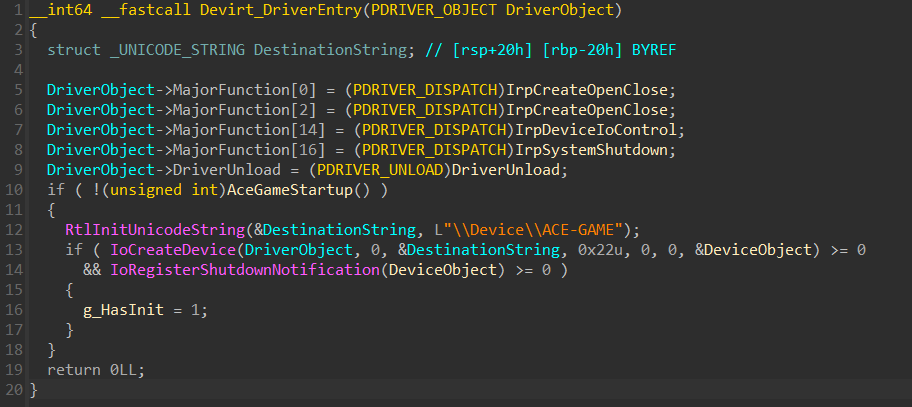
Obfuscation375 Tencent's virtual-machine obfuscation protects the ACE anti-cheat kernel drivers, complete with Intel CET shadow-stack handling and full SEH unwind support. This deep…
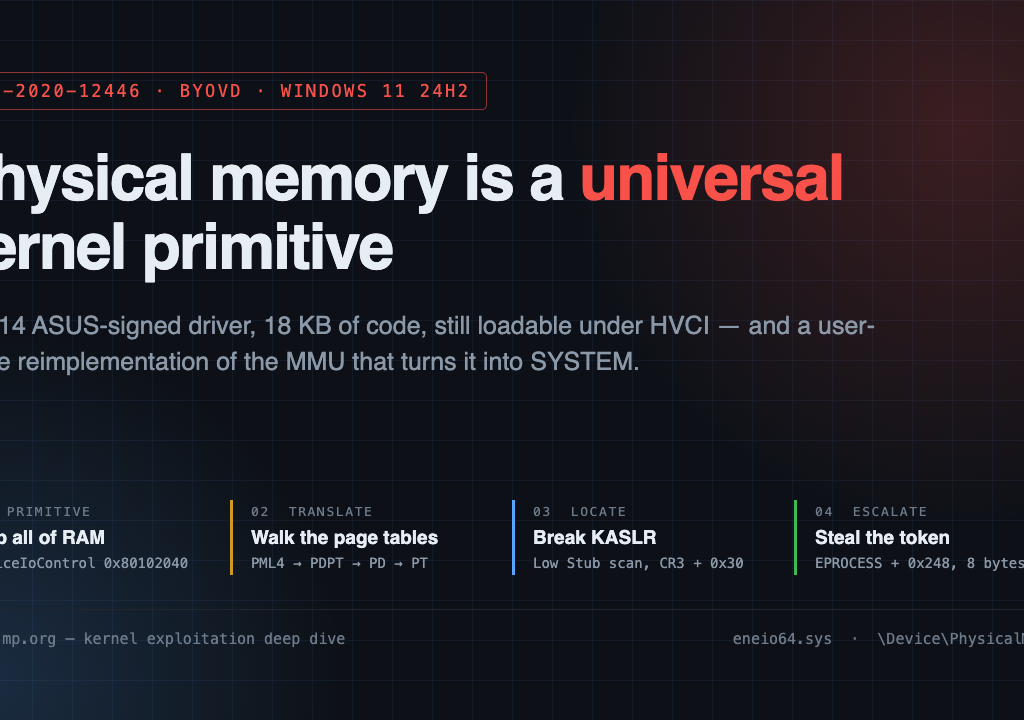
BYOVD433 CVE-2020-12446 in eneio64.sys does not corrupt anything. Its MAPPHYSTOLIN handler opens \Device\PhysicalMemory and maps the entire physical address space, read/write, into whichever…
Exploit Development430 Every hardware security boundary on a modern x86 platform — SMRAM, the AMD PSP's private DRAM, the C6 save area, the live…
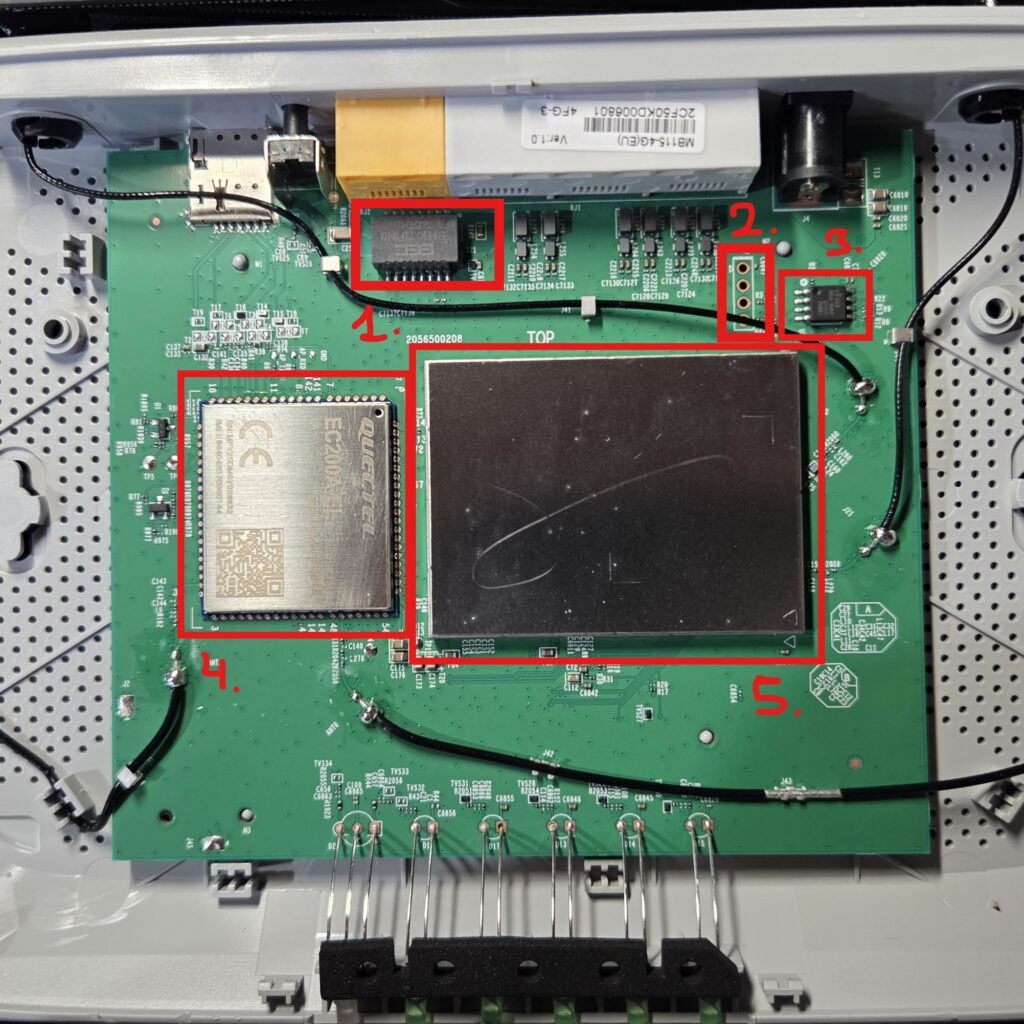
buffer overflow397 A complete hardware-to-firmware walkthrough of the Mercusys MB115-4G, the best-selling router on Amazon Spain: pre-purchase firmware recon, PCB teardown, UART pinout discovery…
Reverse Engineering397 A complete layer-by-layer teardown of the ionCube PHP loader (aarch64, v8.5): custom base64, hand-rolled PRNG stream ciphers, a five-source key-derivation routine, XOR-encrypted…
Malware1.8k A reverse-engineering walkthrough of SakDriver, a Windows kernel-mode rootkit first mistaken for a Cobalt Strike Beacon. It patches ETW, hides processes via…
Reverse Engineering653 A user-controlled 64-bit record count multiplied by the 0x228 record size wraps to zero in the Windows tcpip.sys WFP ALE deserialiser, defeating…
EDR Evasion504 Direct $MFT parsing walks the on-disk NTFS Master File Table through a raw volume handle, producing a full inventory of files, deleted…
Malware488 A complete walkthrough of loading, disassembling, and decompiling raw Cobalt Strike shellcode in Ghidra, resolving ROR13 API hashes via Google lookup and…