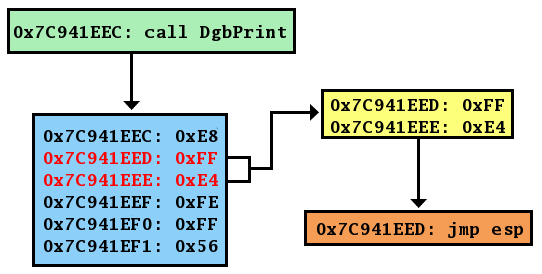
buffer overflow395 Exploiting a Windows 10 PagedPool Off-by-One Overflow (WCTF 2018)
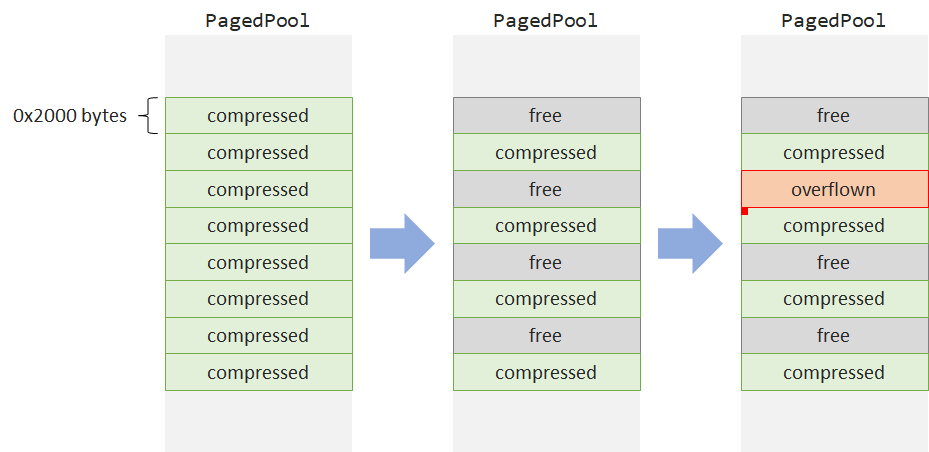
A single byte written past the end of a PagedPool allocation in a Windows 10 x64 kernel driver, followed all the way…
buffer overflow395 A single byte written past the end of a PagedPool allocation in a Windows 10 x64 kernel driver, followed all the way…
buffer overflow393 CVE-2026-47291 is a critical unauthenticated RCE vulnerability in Windows HTTP.sys caused by a 16-bit integer overflow in the buffer reference array growth…
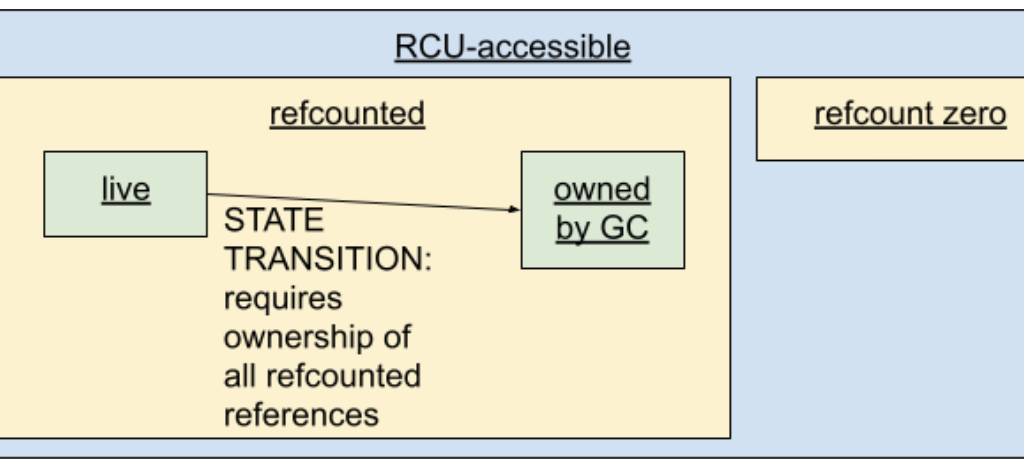
Exploit Development196 Deep-dive writeup on a Linux kernel use-after-free in "fs/eventpoll.c". A 2023 optimisation traded a global "epmutex" for per-instance reference counting in epoll’s…
kernel-mode198 Dirty Frag is a Linux kernel local privilege escalation class abusing zero-copy networking, skb fragments, and in-place crypto to corrupt page cache…
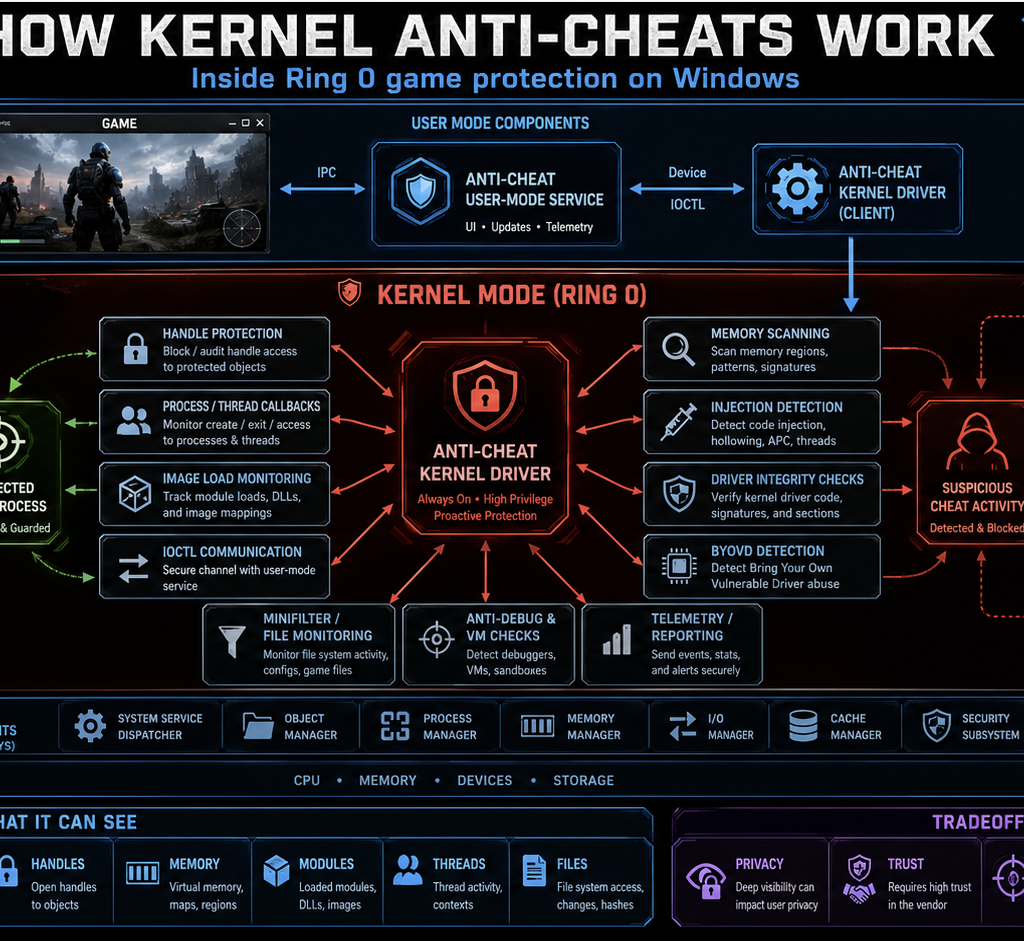
BYOVD1.1k The article explains how kernel anti-cheats monitor games from Ring 0 using callbacks, handle filtering, memory scans, driver checks, anti-debugging, VM detection,…
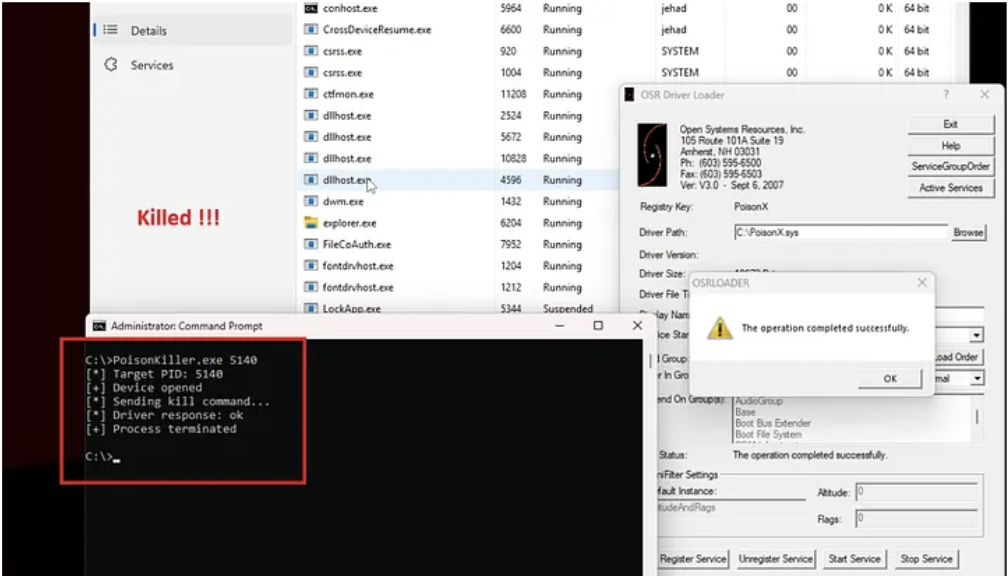
BYOVD4.1k The article analyzes a Microsoft-signed vulnerable driver used in a BYOVD attack to kill security processes. By sending crafted IOCTL requests with…
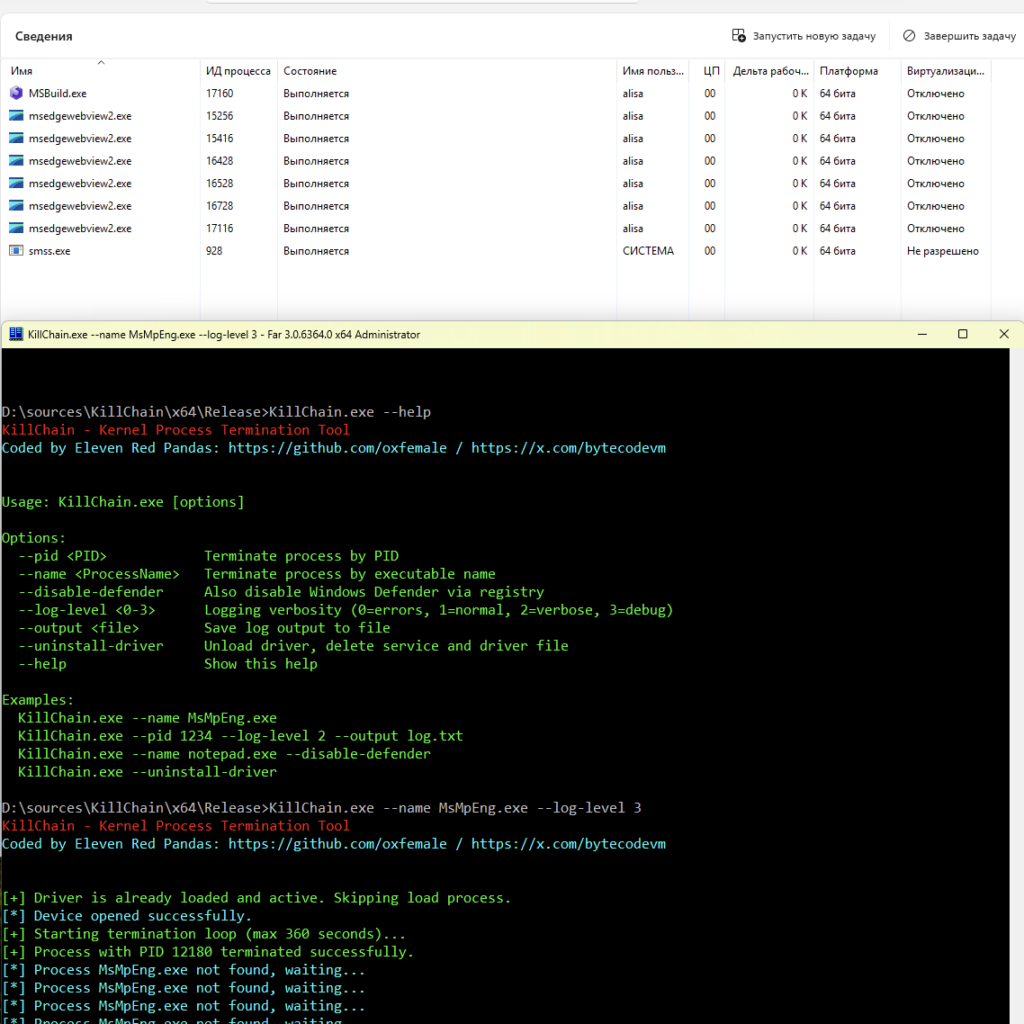
BYOVD212 The KillChain exploit leverages a vulnerability in ProcessMonitorDriver.sys (CVE-2026-0828) by abusing an exposed IOCTL that allows a user-mode application to terminate arbitrary…
AI Security Research242 Researchers showed that the Claude AI model could generate a working exploit for a FreeBSD kernel vulnerability (CVE-2026-4747), producing a remote root…
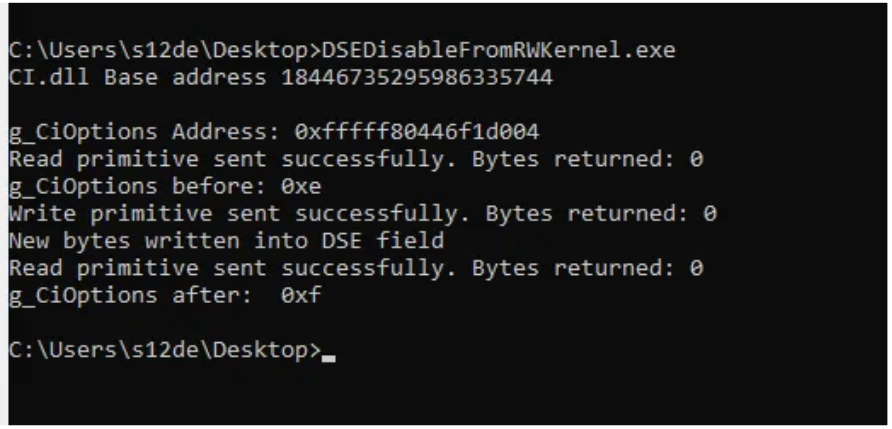
BYOVD213 The article shows how BYOVD techniques bypass Windows Code Integrity by loading a vulnerable signed driver and exploiting its IOCTL interface to…
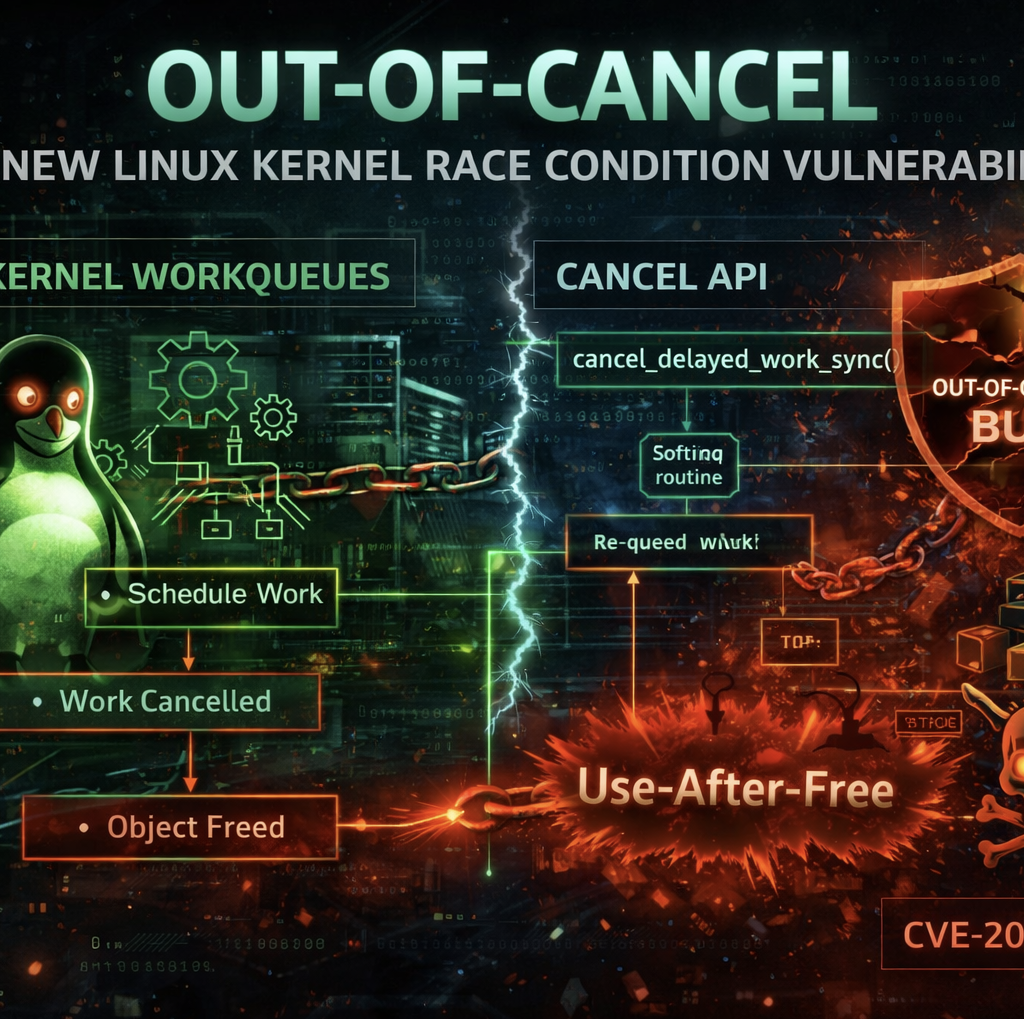
Exploit Development133 The article introduces the Out-of-Cancel vulnerability class in the Linux kernel, where workqueue cancellation APIs fail to guarantee object lifetime. This race…
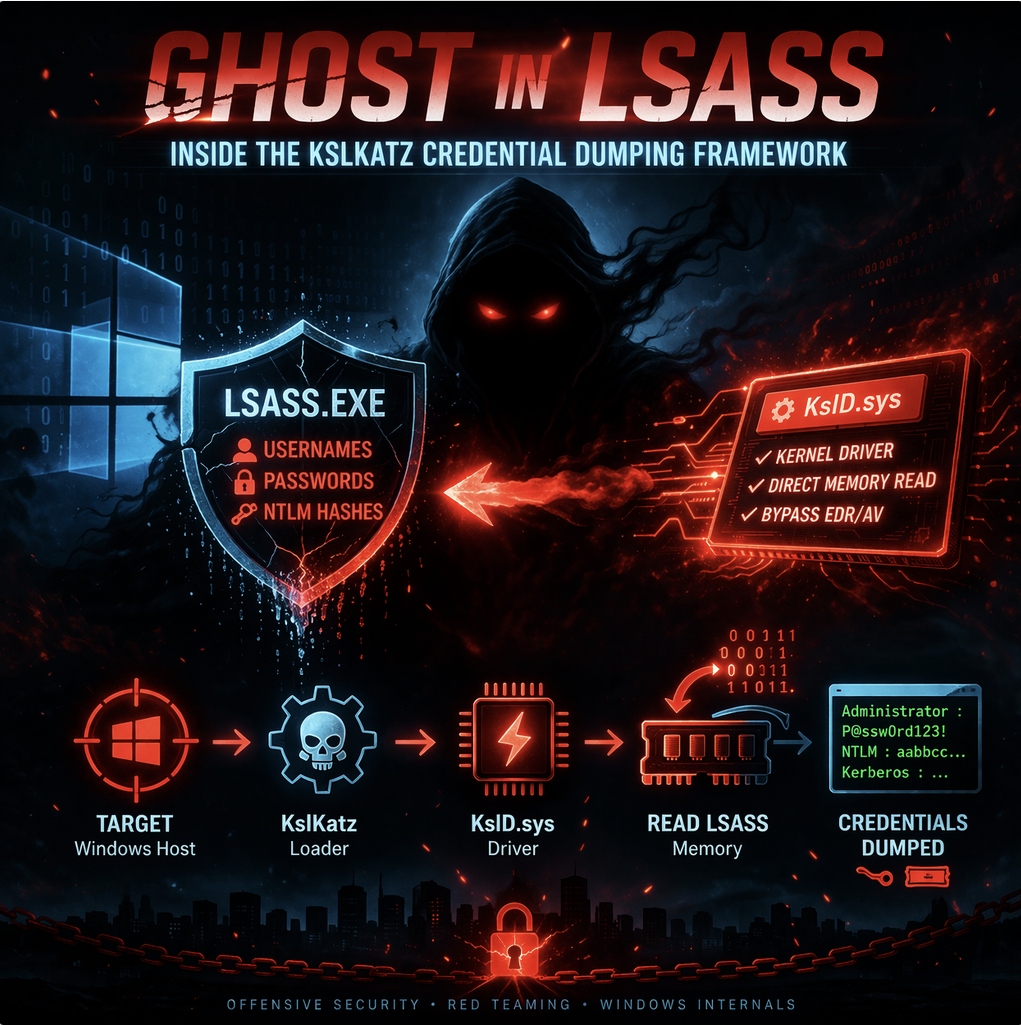
BYOVD860 KslKatz is a Windows credential-dumping tool that reads LSASS memory using a kernel driver to bypass user-mode protections. It merges techniques from…
Debug274 A technical walkthrough showing how to unpack a VMProtected Windows kernel driver using WinDbg and dynamic analysis. The guide demonstrates restoring the…