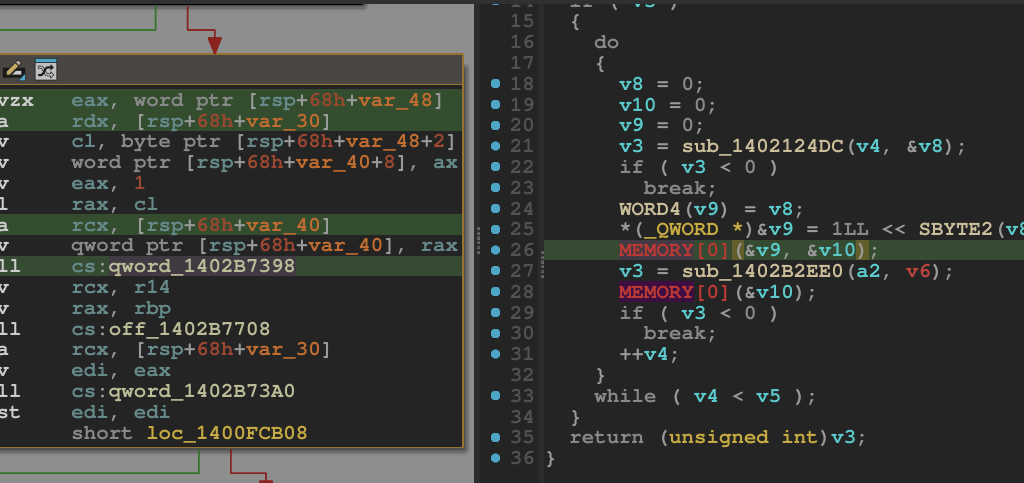
Debug606 Breaking the Shield: Unpacking a VMProtected Windows Kernel Driver
A technical walkthrough showing how to unpack a VMProtected Windows kernel driver using WinDbg and dynamic analysis. The guide demonstrates restoring the…
Debug606 A technical walkthrough showing how to unpack a VMProtected Windows kernel driver using WinDbg and dynamic analysis. The guide demonstrates restoring the…
Apple Silicon587 The article analyzes the macOS secure boot chain on Apple Silicon, showing how Boot ROM, cryptographic verification, Secure Enclave, and staged bootloaders…
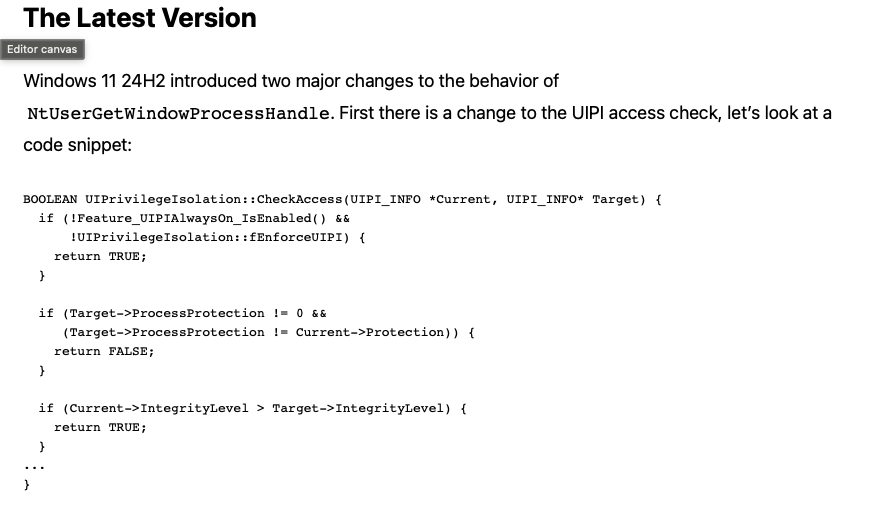
Bypassing243 The article analyzes the Windows GetProcessHandleFromHwnd API and its evolution from a hook-based implementation to a kernel Win32k function that could open…
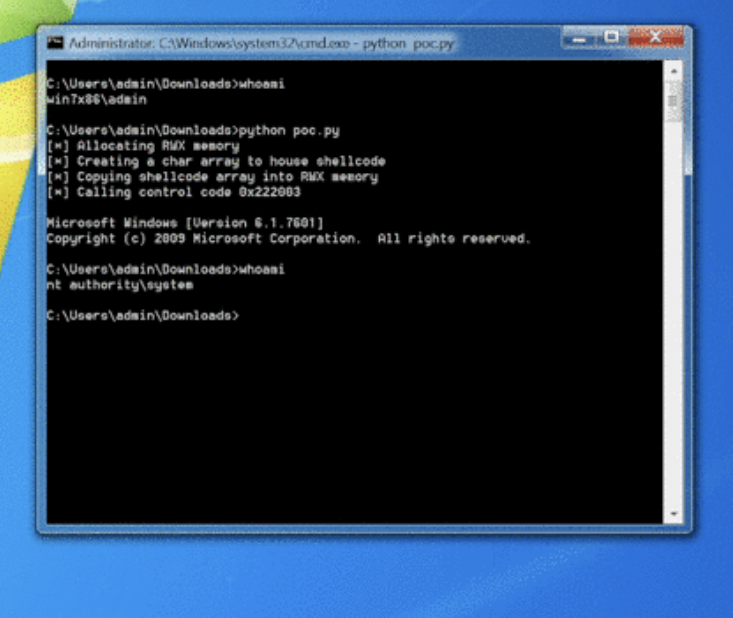
Debug400 The article introduces Windows kernel exploitation and explains how to build a research lab using tools like WinDbg and the HackSys Extreme…
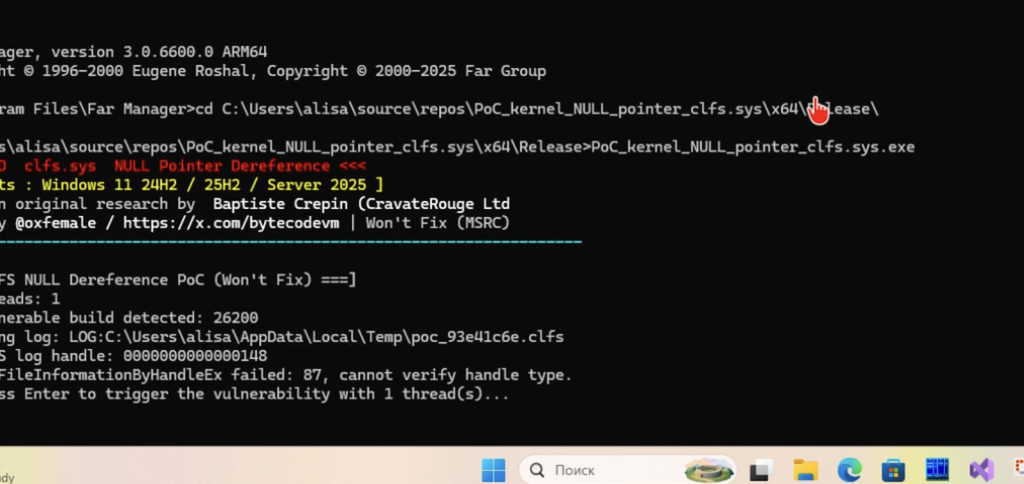
BSoD263 The article examines a Windows kernel bug in clfs.sys where a NULL pointer is dereferenced during fast mutex acquisition, causing a kernel…
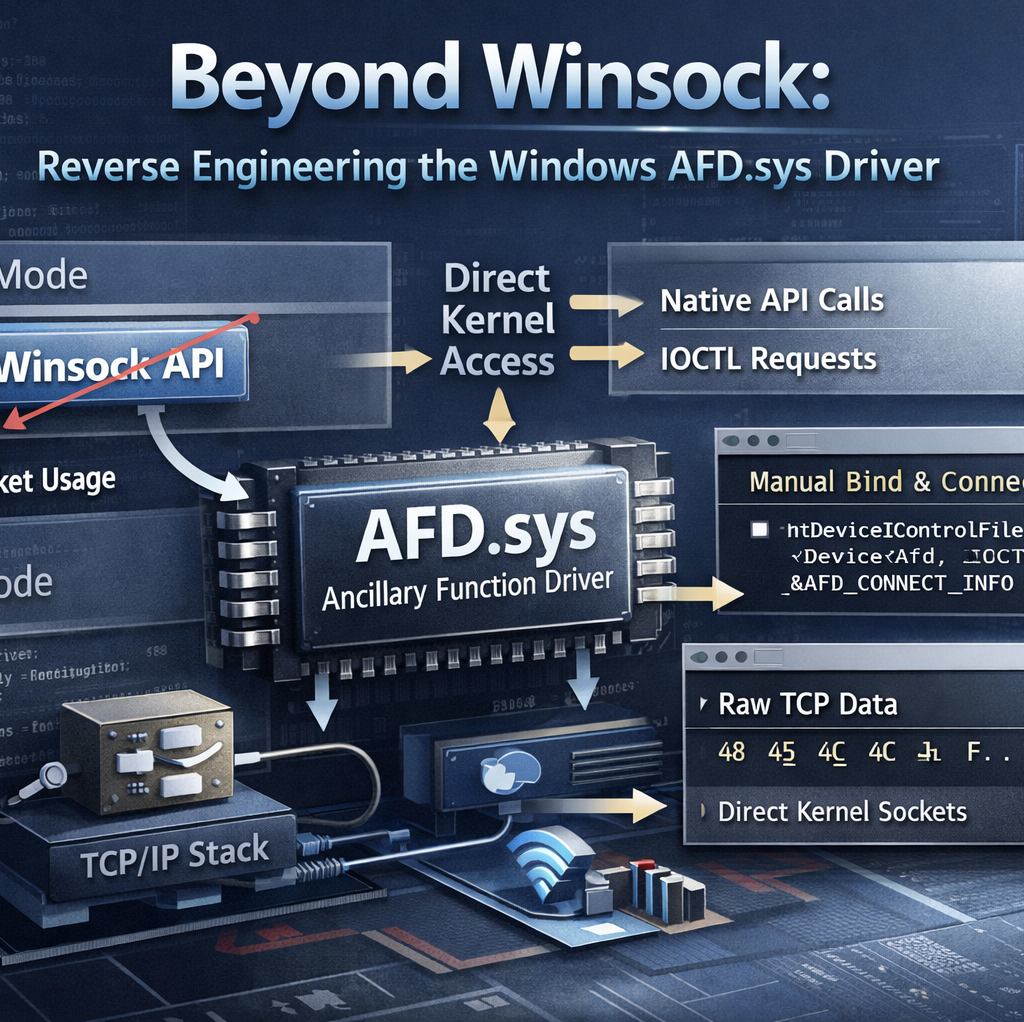
cpp561 The research reverse-engineers Windows AFD.sys, showing how TCP sockets can be created, connected, and used by sending handcrafted IOCTL requests directly to…
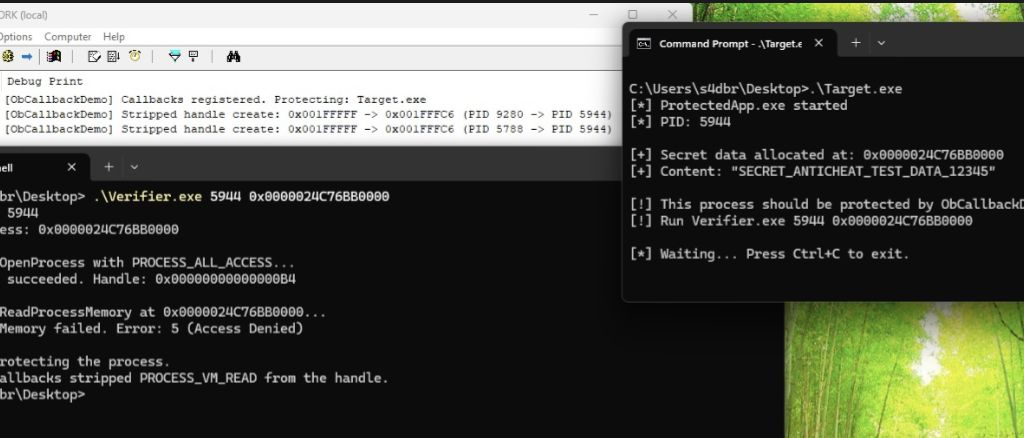
Debug862 The article explains how modern kernel-level anti-cheat systems work, describing their driver architecture, callbacks, memory monitoring, and detection methods used to identify…
BYOVD590 The article explains how attackers exploit a vulnerable signed driver (BYOVD) to obtain a kernel read/write primitive. It shows how unsafe IOCTL…
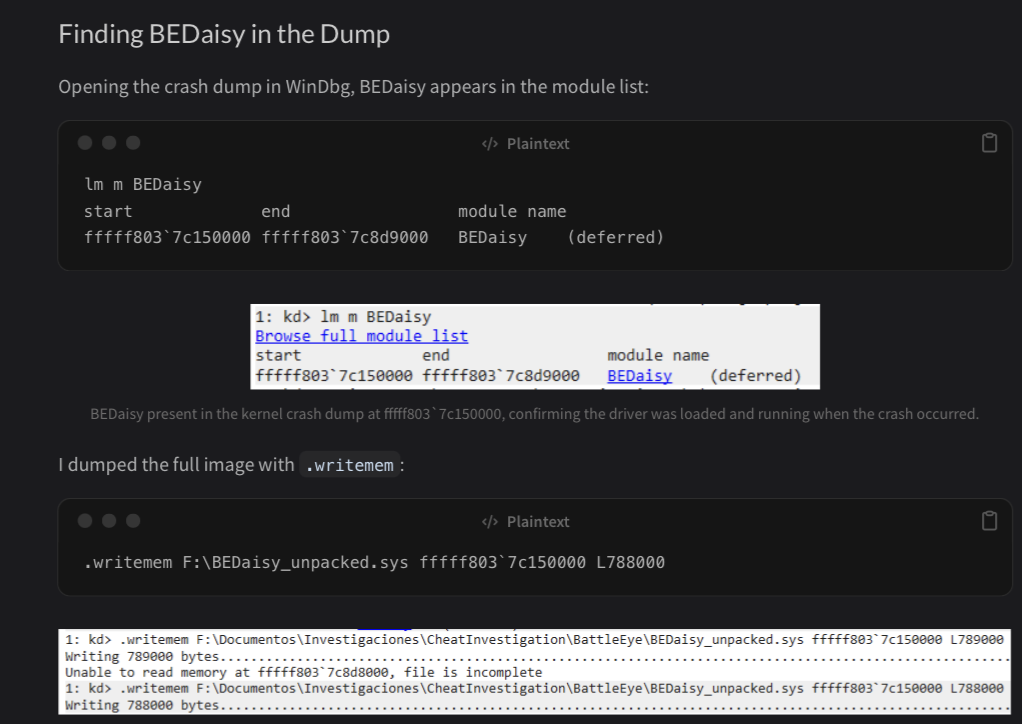
APC511 The article analyzes the Windows kernel driver BEDaisy.sys, used by BattlEye anti-cheat. Through static reverse engineering, it explores driver architecture, APC usage,…
Debug266 The article explains how to set up Windows kernel debugging over a network using WinDBG and a host/target configuration. It covers enabling…