BYOVD4.5k Signed to Kill: Reverse Engineering a 0-Day Used to Disable CrowdStrike EDR
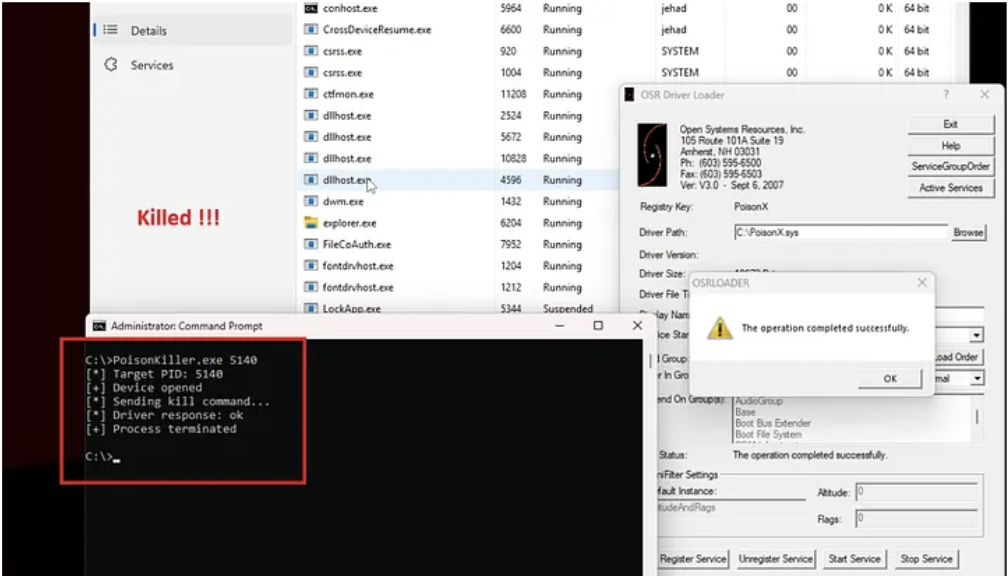
The article analyzes a Microsoft-signed vulnerable driver used in a BYOVD attack to kill security processes. By sending crafted IOCTL requests with…
BYOVD4.5k The article analyzes a Microsoft-signed vulnerable driver used in a BYOVD attack to kill security processes. By sending crafted IOCTL requests with…
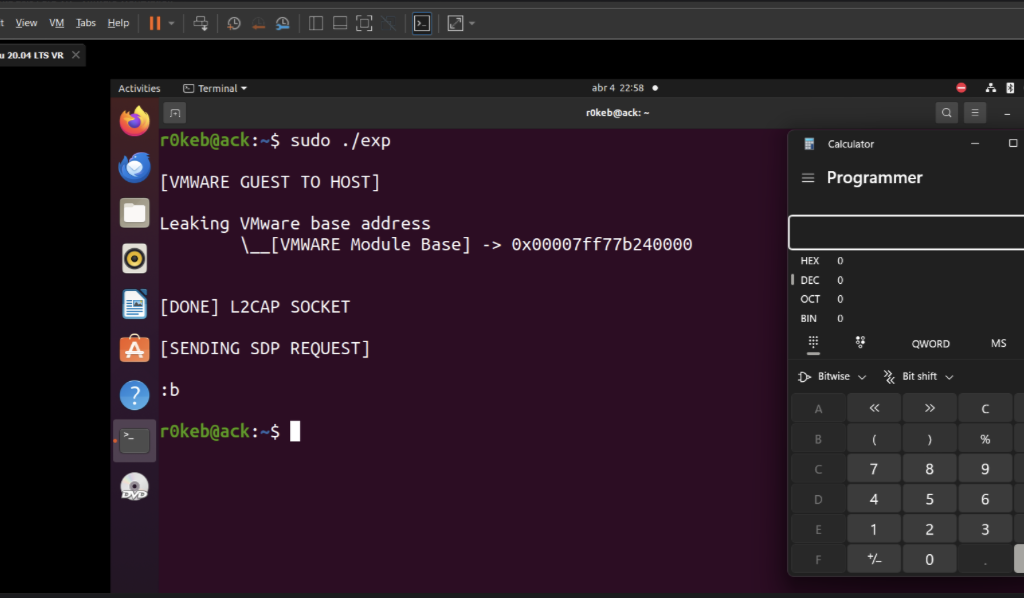
Exploit Development462 The article explains how vulnerabilities in VMware Workstation can enable a guest-to-host escape, allowing malicious code running inside a VM to exploit…
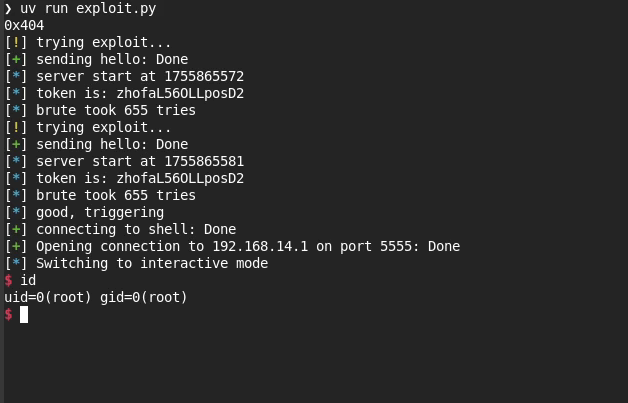
Camera455 Researchers exploited weaknesses in Xiaomi’s miIO protocol to bypass authentication, predict cryptographic values, and trigger memory corruption, ultimately achieving remote code execution…
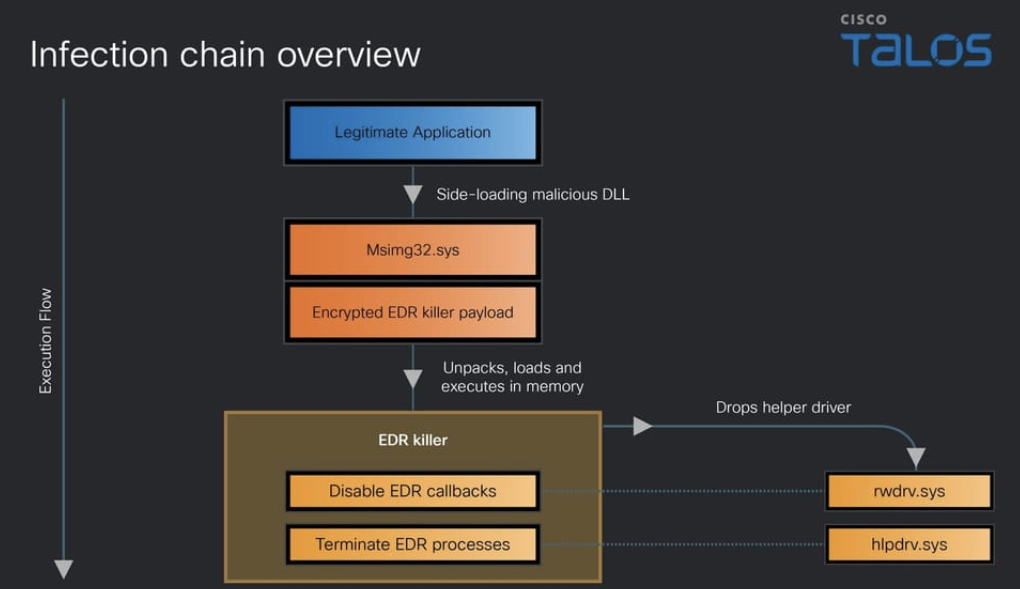
Cisco351 Cisco Talos analyzes a Qilin ransomware EDR-killer that disables over 300 security drivers. The multi-stage malware uses obfuscation and kernel-level techniques to…
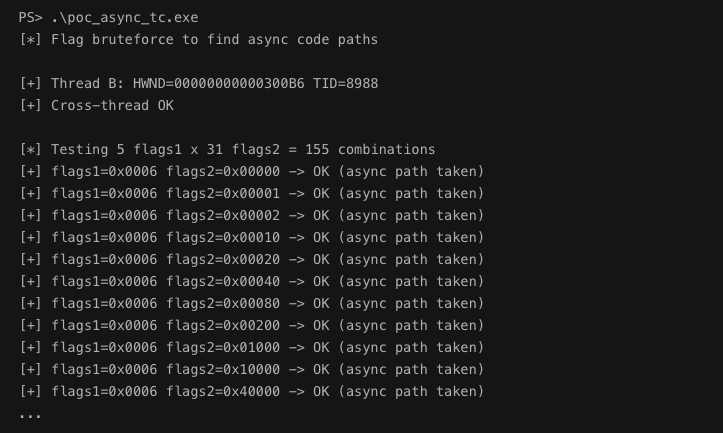
Driver325 The article analyzes a Win32k type confusion vulnerability in the async window action path of win32kfull.sys. Improper handling of window objects can…
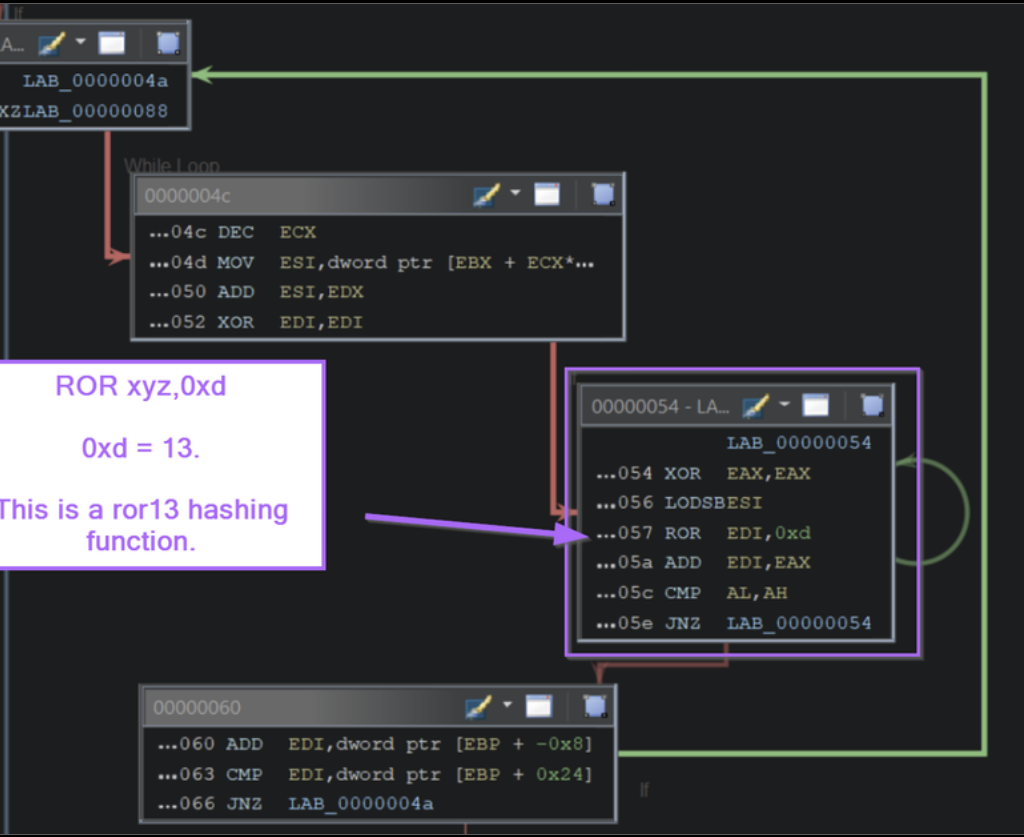
Debug384 The article demonstrates how to analyze Windows shellcode in Ghidra by identifying API-hashing routines, resolving hidden Windows API calls, and extracting C2…
Debug589 A technical walkthrough showing how to unpack a VMProtected Windows kernel driver using WinDbg and dynamic analysis. The guide demonstrates restoring the…
Debug346 A beginner-friendly guide to debugging Windows programs using WinDbg and WinDbgX. It explains debugger basics, breakpoints, symbols, memory inspection, and execution control—key…
attaks289 The article analyzes CVE-2026-32746, a decades-old vulnerability in GNU Inetutils telnetd where a malformed LINEMODE SLC option triggers an out-of-bounds write, enabling…
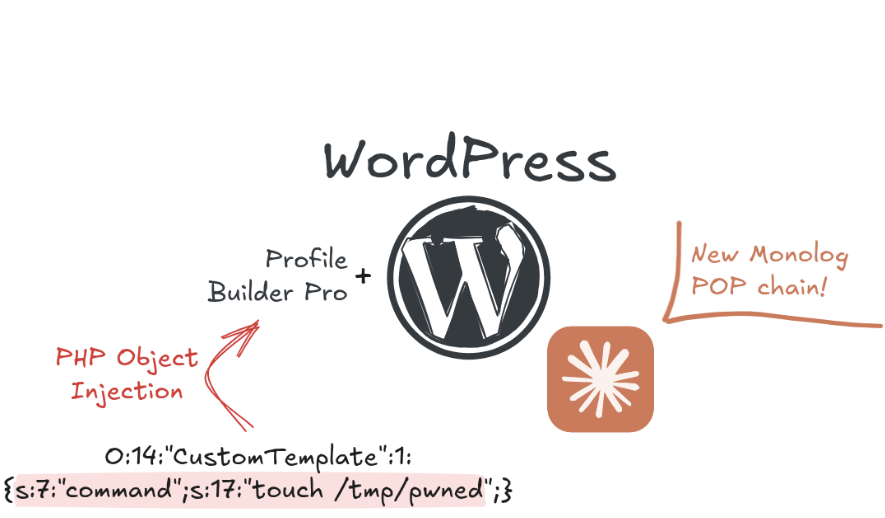
AI Agents394 The article explains how researchers exploited an unauthenticated PHP Object Injection in the WordPress plugin Profile Builder Pro, showing how AI tools…
AI Agents505 The article shows how AI-assisted reverse engineering of the TP-Link Tapo C200 firmware uncovered hardcoded keys, buffer overflows, and insecure APIs, demonstrating…
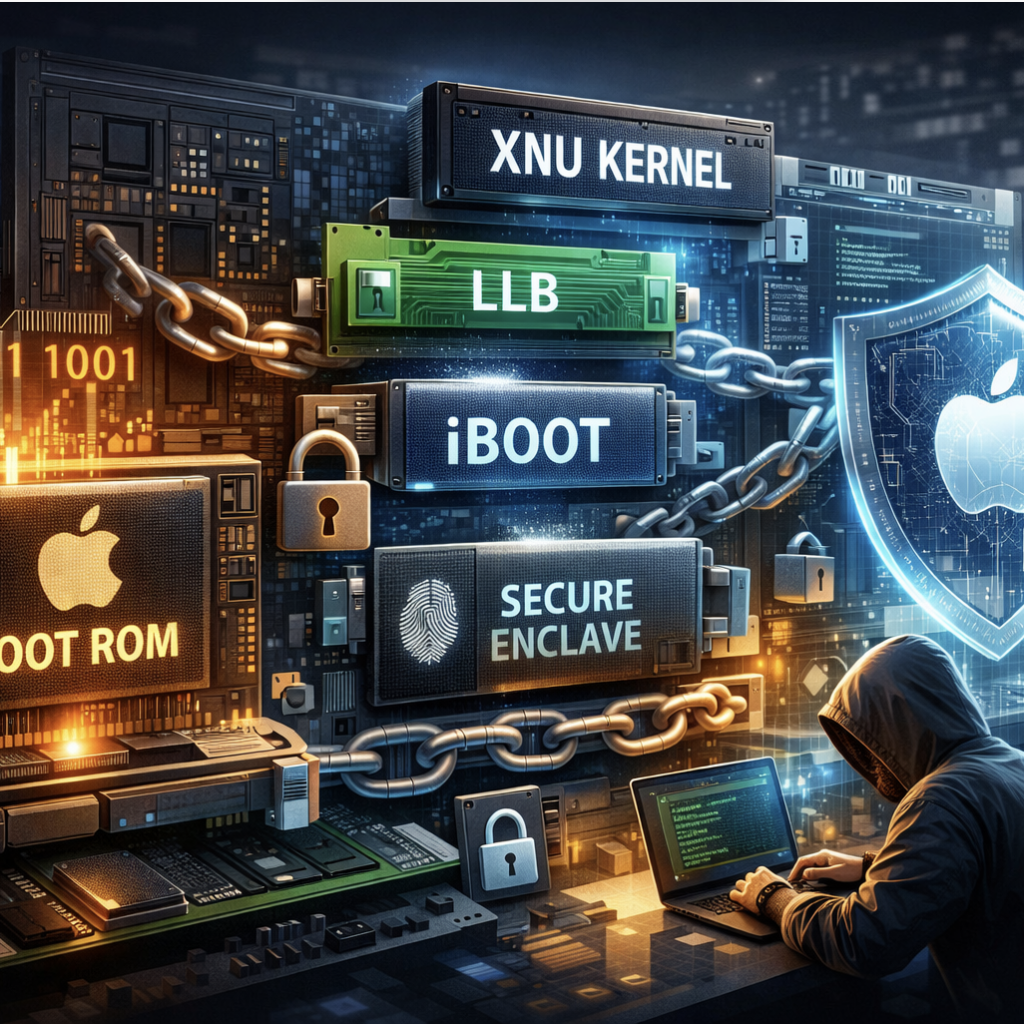
Apple Silicon569 The article analyzes the macOS secure boot chain on Apple Silicon, showing how Boot ROM, cryptographic verification, Secure Enclave, and staged bootloaders…