Apple Silicon663 iBoot SMMU Bypass and Kernelcache Struct Forgery on Apple Silicon
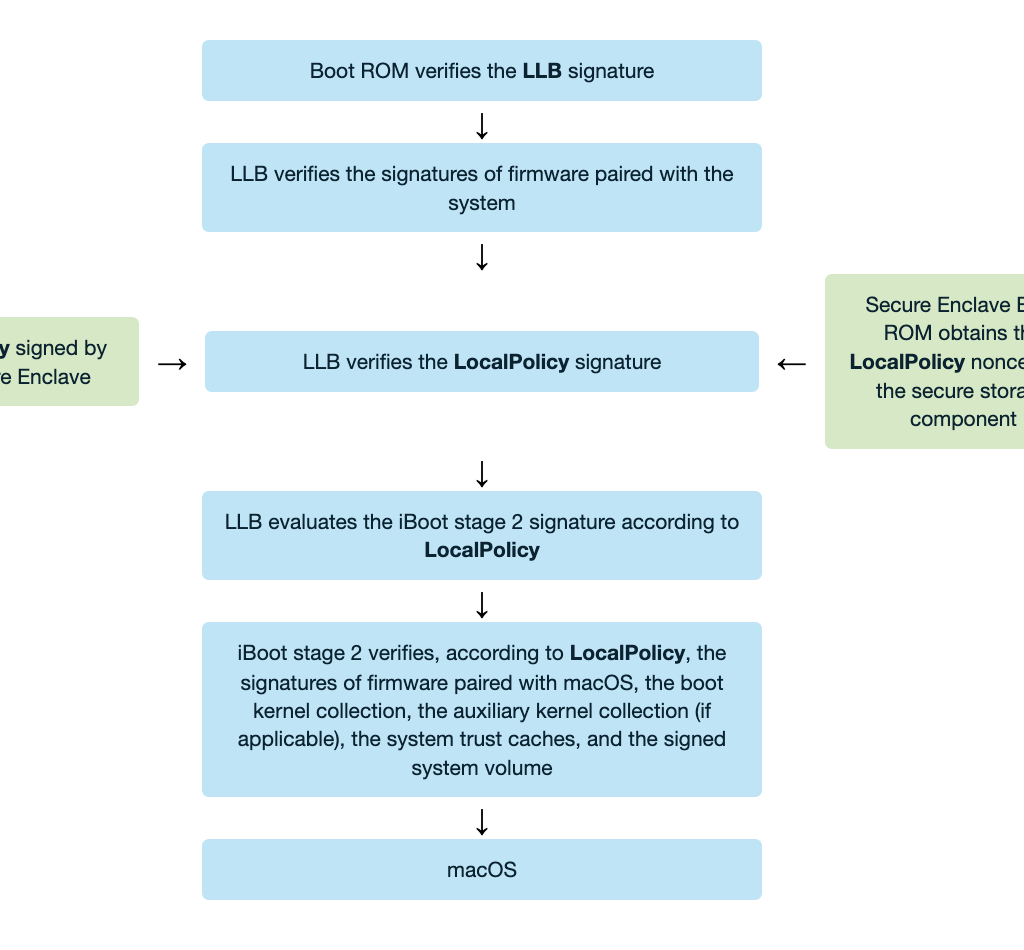
Apple Silicon's chain of trust hands the XNU kernel an SMMU/IOMMU configuration that iBoot builds once and the OS never re-verifies. An…
Apple Silicon663 Apple Silicon's chain of trust hands the XNU kernel an SMMU/IOMMU configuration that iBoot builds once and the OS never re-verifies. An…
Containers558 A deep technical walkthrough of ipv6_frag_escape, a public proof-of-concept exploit that converts a Linux kernel IPv6 fragmentation linear overflow into a reliable…
ALPC491 CVE-2020-1027 is a heap buffer overflow in the Windows CSRSS SxS assembly component. A missing bounds check on UNICODE_STRING.MaximumLength in an ALPC…
Exploit Development362 CVE-2026-41096 is a remotely-triggerable heap overflow in dnsapi.dll. A single crafted UDP DNS response with QDCOUNT=0 corrupts 604 bytes past a heap…
Apple Silicon631 usbliter8 is a new BootROM exploit chain against Apple A12, S4/S5 and A13 SoCs. It chains a 12-byte buffer-underflow primitive in the…
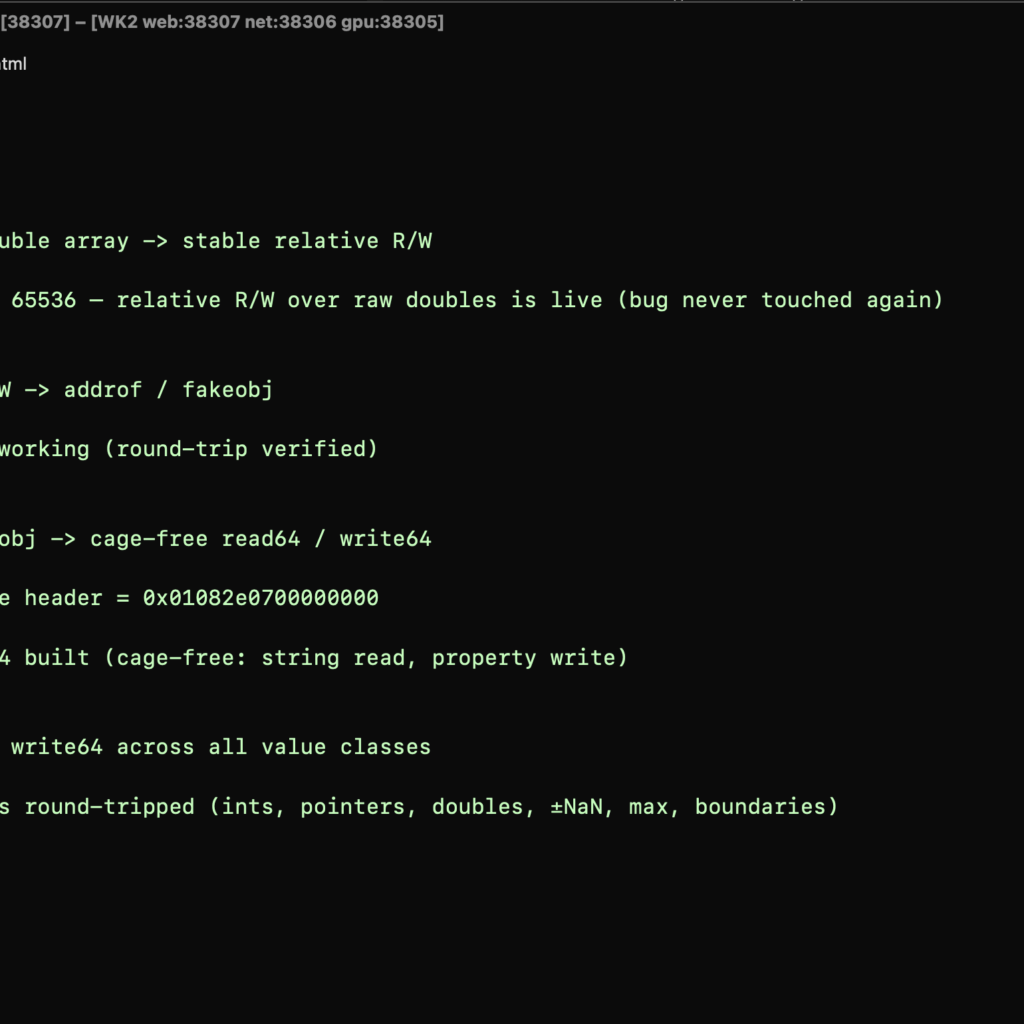
Exploit Development281 Varik Matevosyan's step-by-step ladder from a single artificial OOB on a double-array butterfly to stable cage-free read64/write64 in JavaScriptCore. Covers heap grooming,…
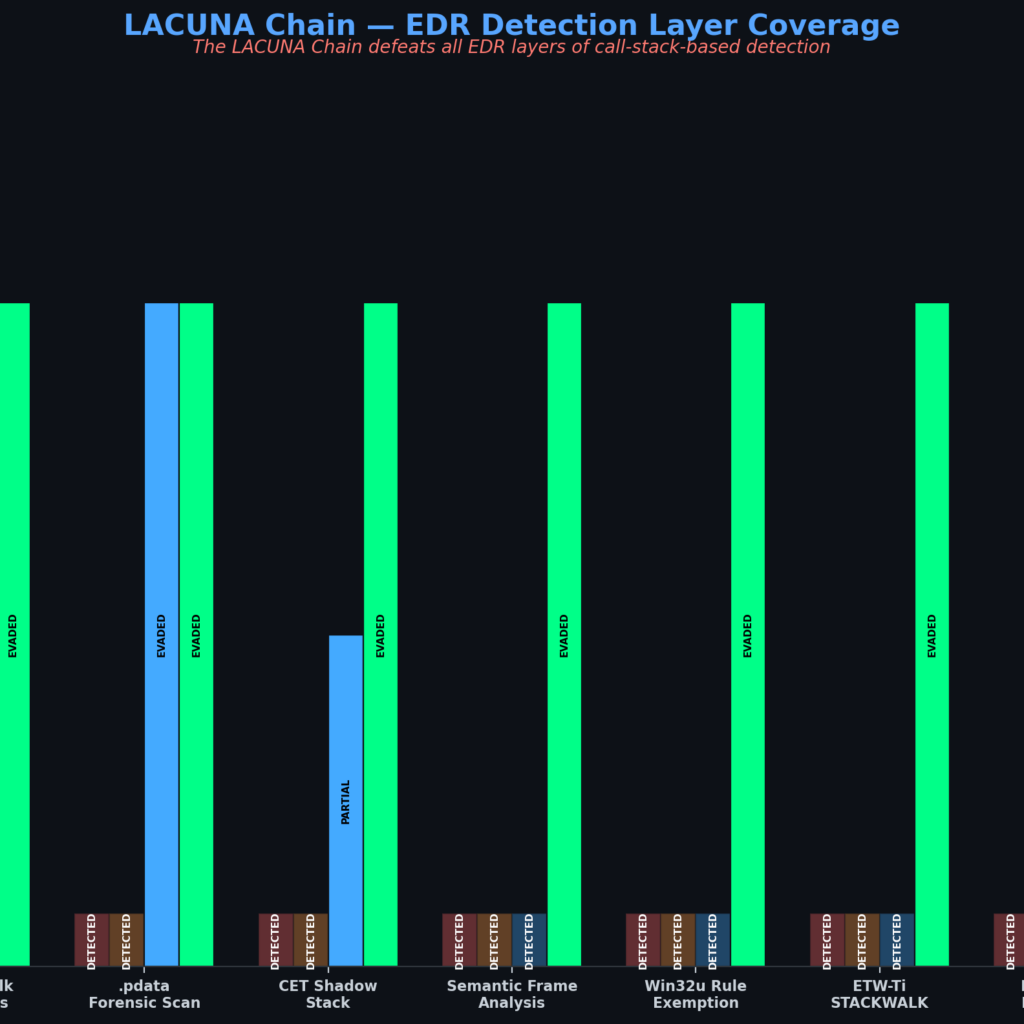
EDR Evasion658 Mohamed Alzhrani's LACUNA Chain combines BYOUD-Gap, the ETW-Ti APC window, win32u's 1,242 NOP gaps, ntdll/kernelbase ghost functions, BYOUD-MF machine-frame RSP teleport, BYOUD-RT…
Exploit Development398 A full-pipeline walkthrough: build a vulnerable Windows console program, take RIP with a strcpy overflow, then use rop_scanner — an offline ROP…
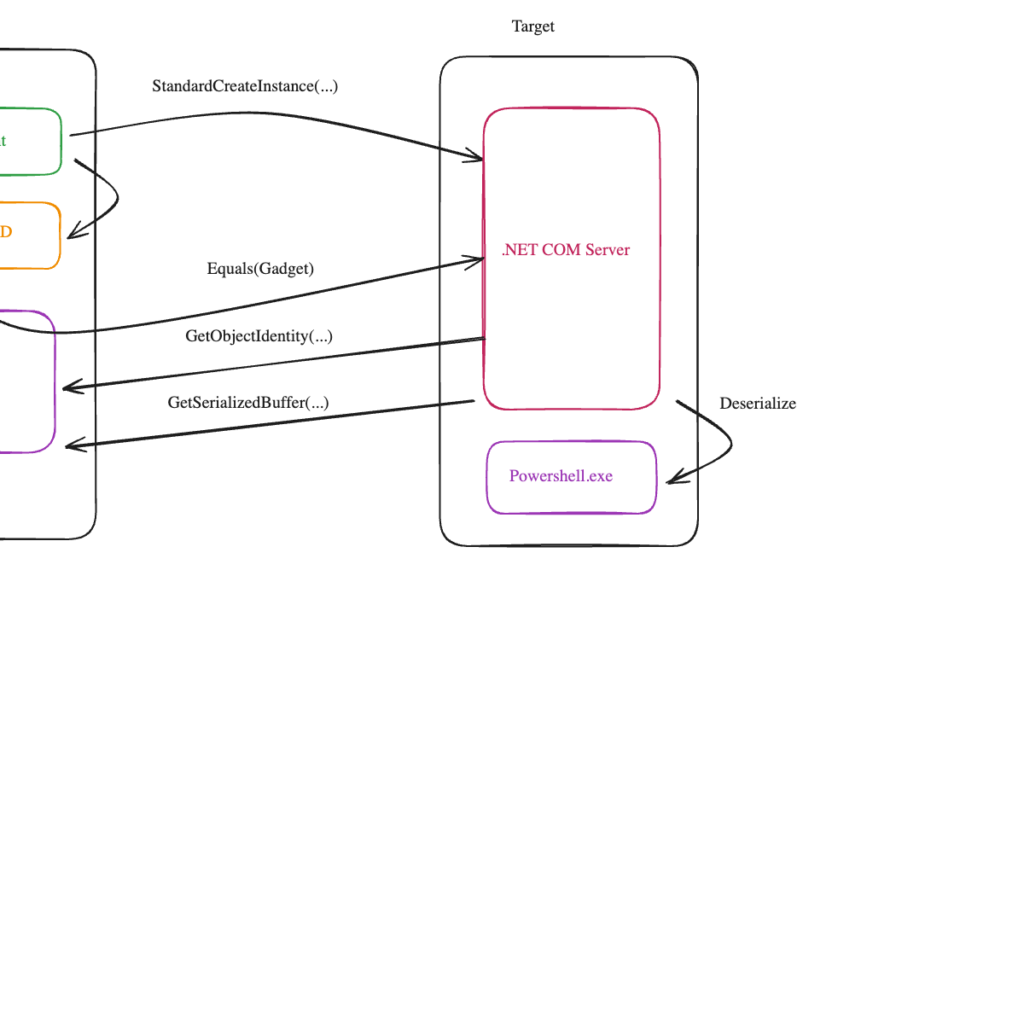
Exploit Development545 Synacktiv’s open-source DCOMIllusionist takes James Forshaw’s .NET DCOM deserialization primitive — the same one that seeded the “Potato” family — and turns…
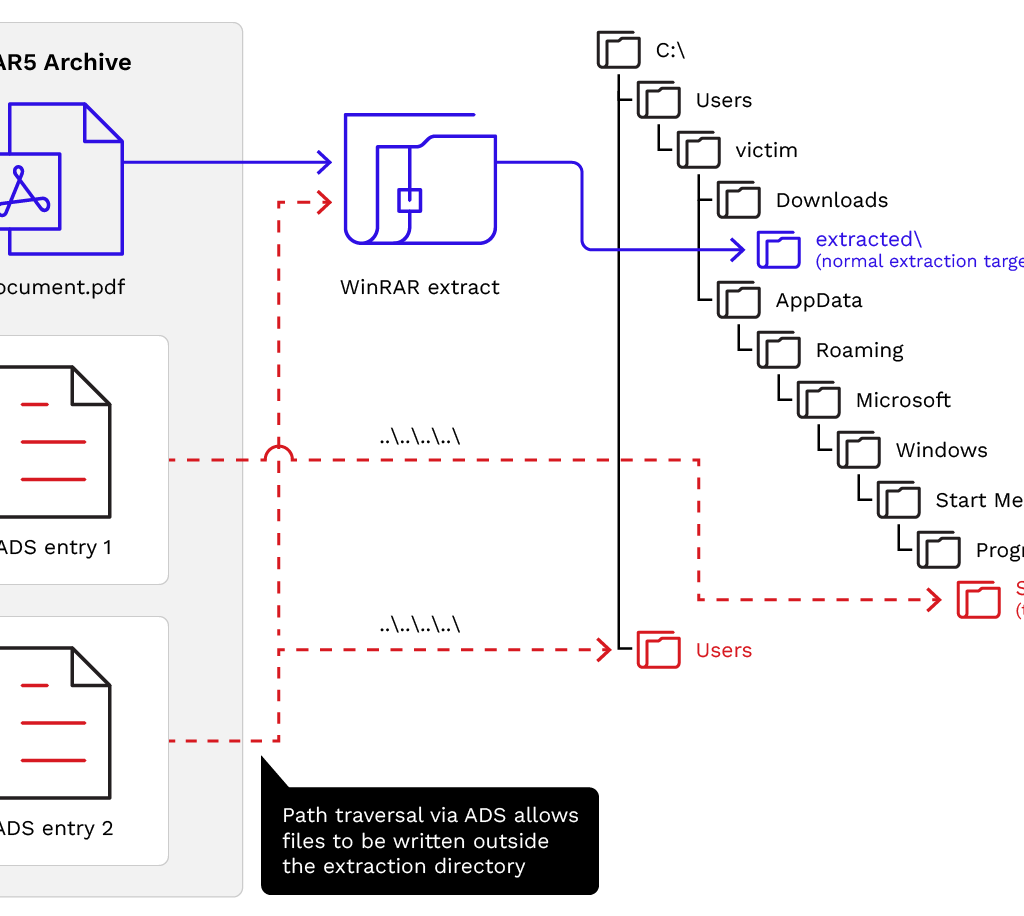
Exploit Development424 Eleven months after RarLab shipped WinRAR 7.13 to fix CVE-2025-8088, two Russia-aligned APT clusters (Earth Dahu / Gamaredon and SHADOW-EARTH-066 / UAC-0226)…
Exploit Development206 Meeting-room cameras and conference-room tablets are some of the least-monitored, most insecurely-configured attack surfaces in an enterprise. Spaceraccoon (Eugene Lim) walks through…
Exploit Development490 CVE-2026-40369 is an unprivileged arbitrary 12-byte kernel write in nt!ExpGetProcessInformation, reachable from Chrome/Edge/Firefox renderer sandboxes via NtQuerySystemInformation. A walk through the unchecked…