Application Security408 CVE-2026-71320: Nuxt Server Island Template Injection Leads to Server-Side RCE
CVE-2026-71320 lets an attacker inject a template key into Nuxt server island props and have Vue's runtime compiler execute it inside the…
Application Security408 CVE-2026-71320 lets an attacker inject a template key into Nuxt server island props and have Vue's runtime compiler execute it inside the…
RCE517 Technical breakdown of OnlyShells — a five-vulnerability chain in ONLYOFFICE Desktop Editors combining zero-click XSS, a Chromium V8 RCE, and an update-service…
Hardware395 Runic Labs dissects a QNAP QTS disclosure cycle — four bugs across three plugins (Notes Station 3, QmailAgent, QVPN) — and shows…
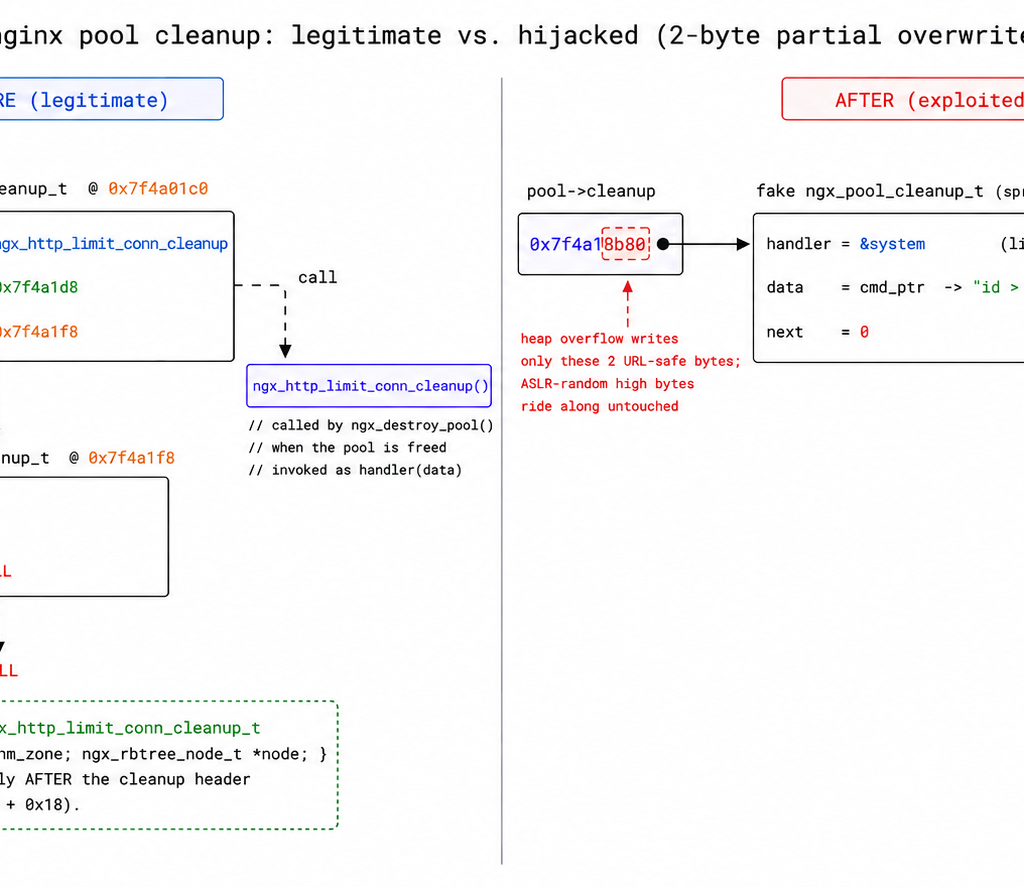
buffer overflow387 A two-bug nginx 1.30.0 chain: CVE-2026-42945 (Rift) heap overflow + CVE-2026-9256 (PoolSlip) heap over-read combine into an ASLR-independent remote system() call at…
buffer overflow388 CVE-2026-47291 is a critical unauthenticated RCE vulnerability in Windows HTTP.sys caused by a 16-bit integer overflow in the buffer reference array growth…
MacOS197 CVE-2024-32002 turns git clone --recursive into RCE on case-insensitive filesystems. A crafted submodule + symlink can plant a Git hook in .git…
Linux174 NGINX Rift is a heap overflow in the rewrite module that may crash workers or enable RCE under specific configs. Public PoC…
LLM229 A LiteLLM 1.83.14 exploit chain leaks the master key through callback metadata, then abuses non-sandboxed Jinja2 GitLab prompts to achieve server-side RCE.
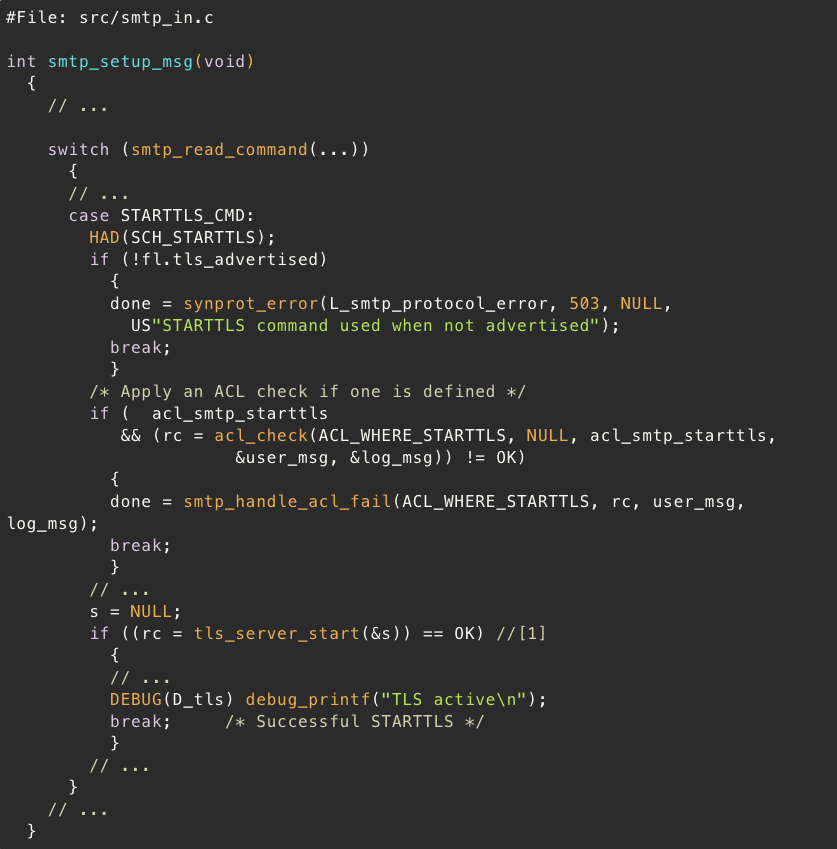
Linux192 A deep dive into CVE-2026-45185: an unauthenticated Exim RCE where one stale TLS/BDAT ungetc() byte corrupts freed memory and leads to exploitation.
Apache Tomcat224 A flaw in Apache Tomcat Tribes clustering allows attackers to send crafted cluster messages that bypass authentication and trigger unsafe deserialization, leading…
Camera230 Researchers exploited weaknesses in Xiaomi’s miIO protocol to bypass authentication, predict cryptographic values, and trigger memory corruption, ultimately achieving remote code execution…
AI Security Research239 Researchers showed that the Claude AI model could generate a working exploit for a FreeBSD kernel vulnerability (CVE-2026-4747), producing a remote root…