Exploit Development478 Two Bytes to RCE: Chaining nginx rift and PoolSlip into an ASLR-Independent Exploit
Two nginx rewrite-engine bugs share one root cause: an is_args flag computed in one pass and consumed in another. Pointed at r->args…
Exploit Development478 Two nginx rewrite-engine bugs share one root cause: an is_args flag computed in one pass and consumed in another. Pointed at r->args…
Application Security781 HTTP header injection has been under-rated for twenty years. This research shows how one injected CRLF sequence in an Nginx-normalised path escalates…
Application Security464 CVE-2026-71320 lets an attacker inject a template key into Nuxt server island props and have Vue's runtime compiler execute it inside the…
Application Security312 A multi-tenant document vault enforced a real server-side tenant-ownership check on its permission-grant endpoint - and it was still bypassable. The authorization…
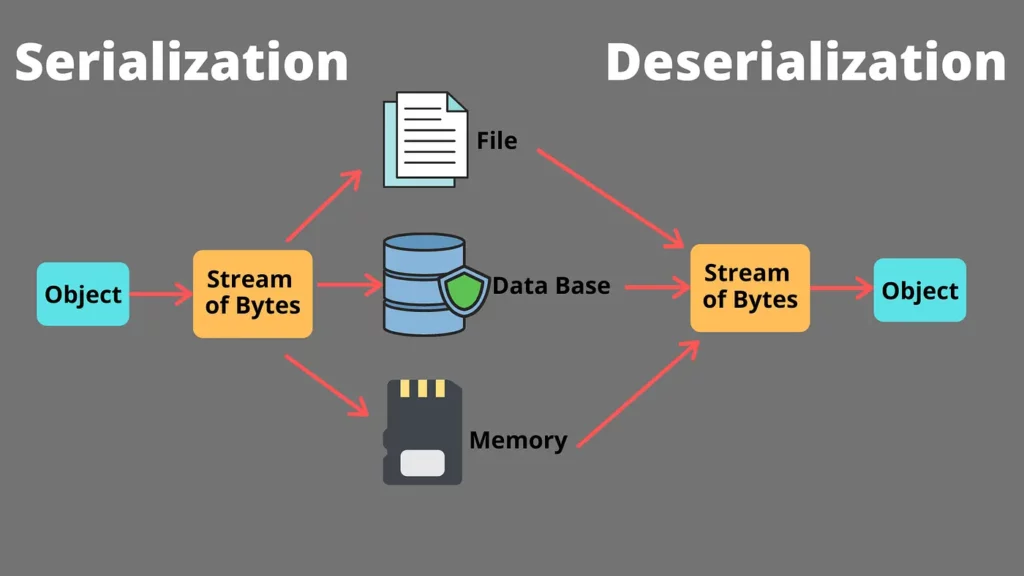
Threat Intelligence472 CVE-2026-50522 is a critical (CVSS 9.8) unauthenticated, pre-auth deserialization RCE in on-premises Microsoft SharePoint Server. A single crafted WS-Federation POST to /_trust/default.aspx…
Exploit Development252 STAR Labs’ advisory on CVE-2026-41873 in Apache Pony Mail by Li Jiantao and Tevel Sho (disclosed 28 April 2026). Two independent bugs…
Application Security286 CVE-2025-49113 is a critical authenticated remote-code-execution flaw in Roundcube webmail — the default in cPanel, Plesk, and many hosting stacks — caused…
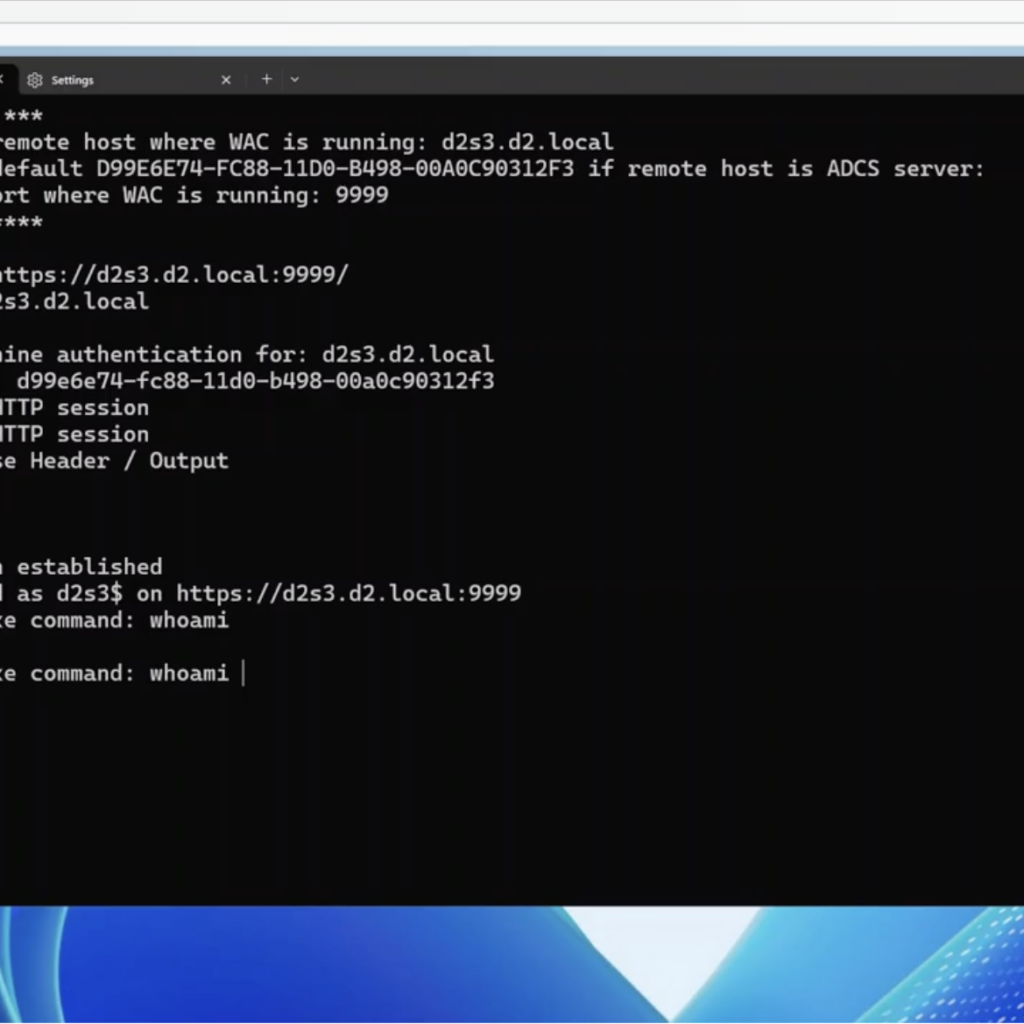
Escalation137 CVE-2026-26119 is a high-severity privilege-escalation flaw in Windows Admin Center caused by improper authentication. Attackers with low-privileged access could gain admin rights…
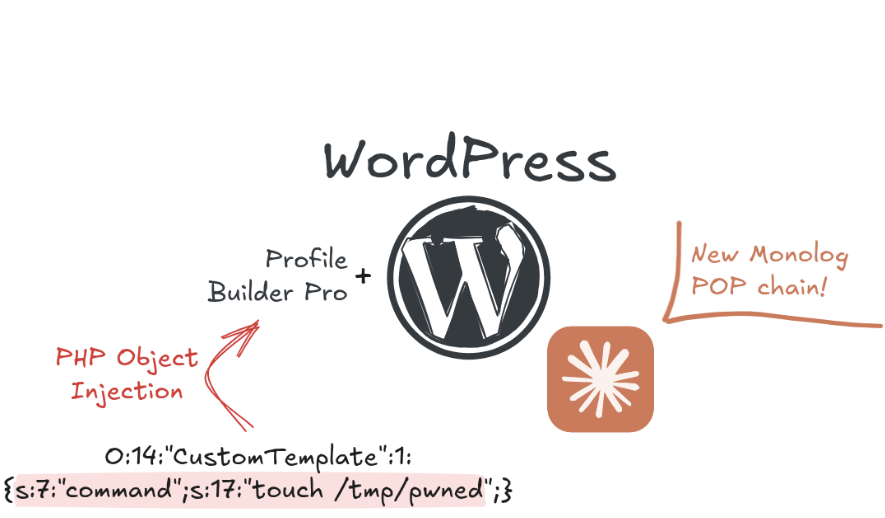
AI Agents199 The article explains how researchers exploited an unauthenticated PHP Object Injection in the WordPress plugin Profile Builder Pro, showing how AI tools…
Broadcom191 The article examines vulnerabilities in VMware Aria Operations that enable credential disclosure and privilege escalation. Attackers with limited access can escalate privileges…