Application Security1.2k CRLF-Powered Desync Attacks: Beheading HTTP Streams
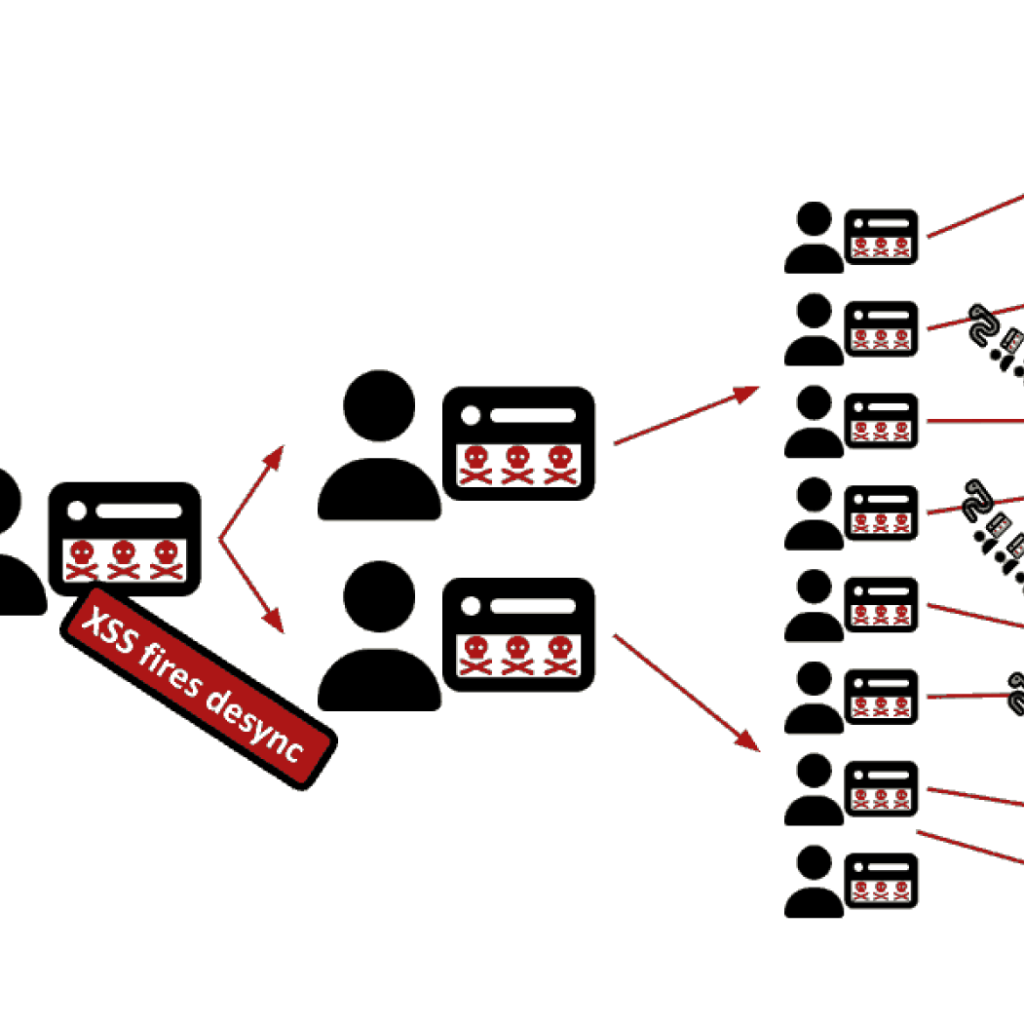
HTTP header injection has been under-rated for twenty years. This research shows how one injected CRLF sequence in an Nginx-normalised path escalates…
Application Security1.2k HTTP header injection has been under-rated for twenty years. This research shows how one injected CRLF sequence in an Nginx-normalised path escalates…
AI Security Research799 Writing the harness is the friction that keeps most codebases from ever being fuzzed. This walkthrough puts an offline open-weights model behind…
buffer overflow685 A single byte written past the end of a PagedPool allocation in a Windows 10 x64 kernel driver, followed all the way…
buffer overflow824 A complete hardware-to-firmware walkthrough of the Mercusys MB115-4G, the best-selling router on Amazon Spain: pre-purchase firmware recon, PCB teardown, UART pinout discovery…
Application Security787 CVE-2026-71320 lets an attacker inject a template key into Nuxt server island props and have Vue's runtime compiler execute it inside the…
Application Security476 A multi-tenant document vault enforced a real server-side tenant-ownership check on its permission-grant endpoint - and it was still bypassable. The authorization…
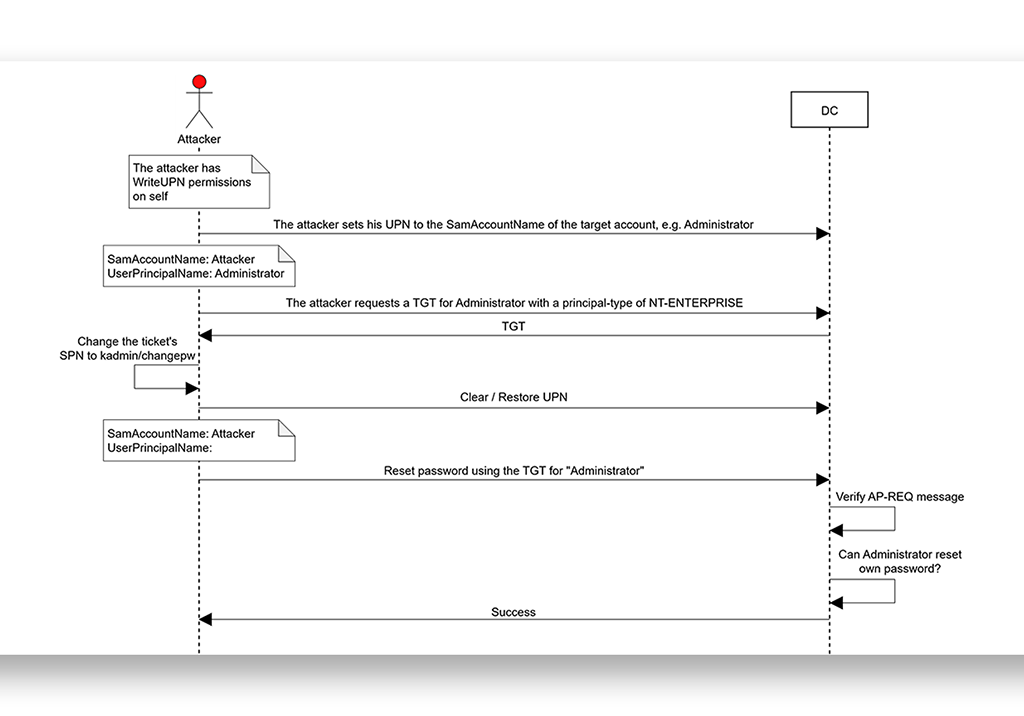
Active Directory973 Active Directory stores Unicode characters its own LDAP server cannot search for. Semperis researcher Shai Laron turned that gap into KerberLoss (CVE-2026-25177)…
.NET1.2k Windows Application Control (formerly WDAC) blocks binaries that are not signed by an approved authority — but a Microsoft-signed binary that deserialises…
Credential Attacks668 From a compromised session, a TPM-backed Windows Hello for Business key can be driven to sign arbitrary data with no PIN or…
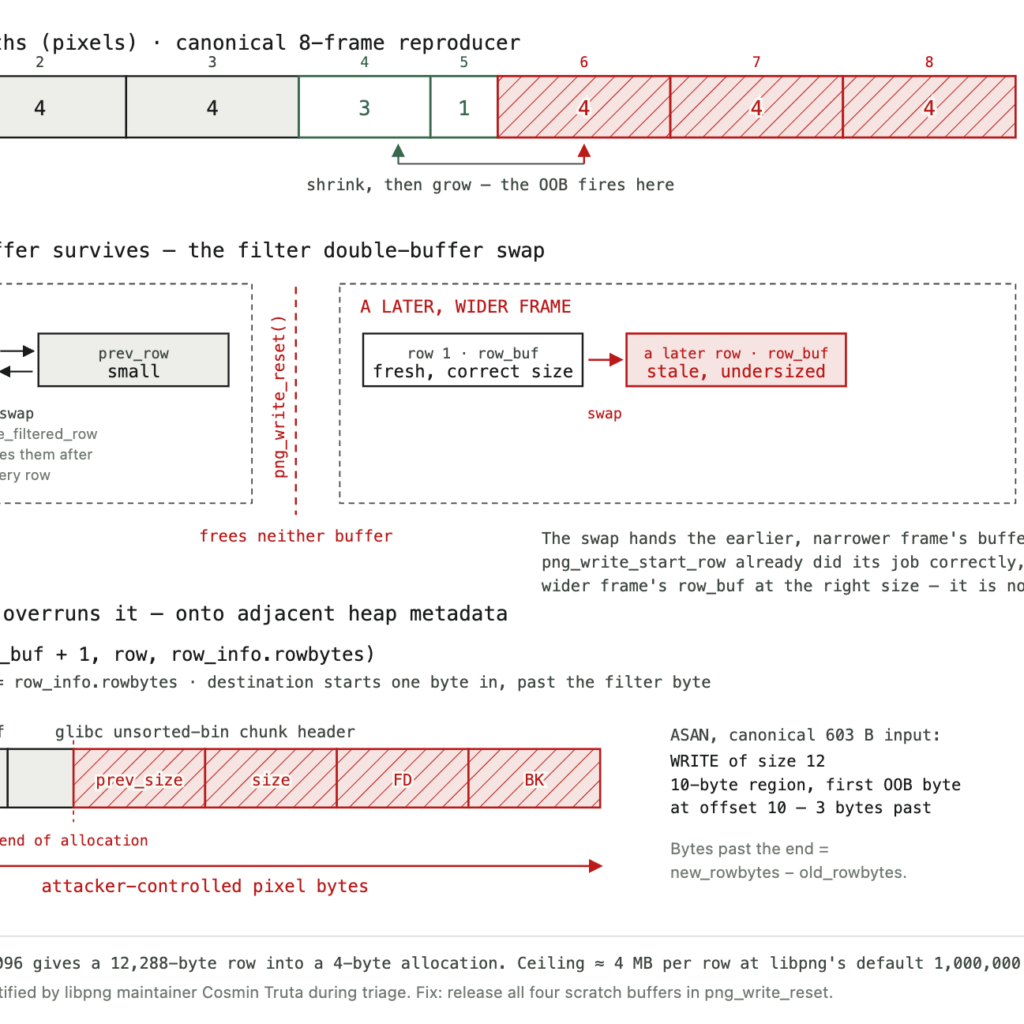
Exploit Development478 A write-side fuzzing campaign against libpng18's APNG re-encode path found a per-frame buffer lifecycle defect that yields both a memory leak (CWE-401)…
Memory Management693 A technical deep dive into NTDLL unhooking techniques using KnownDlls section mapping, Virtual Address Descriptors, and RWX page detection to bypass EDR…
Reverse Engineering716 A complete layer-by-layer teardown of the ionCube PHP loader (aarch64, v8.5): custom base64, hand-rolled PRNG stream ciphers, a five-source key-derivation routine, XOR-encrypted…