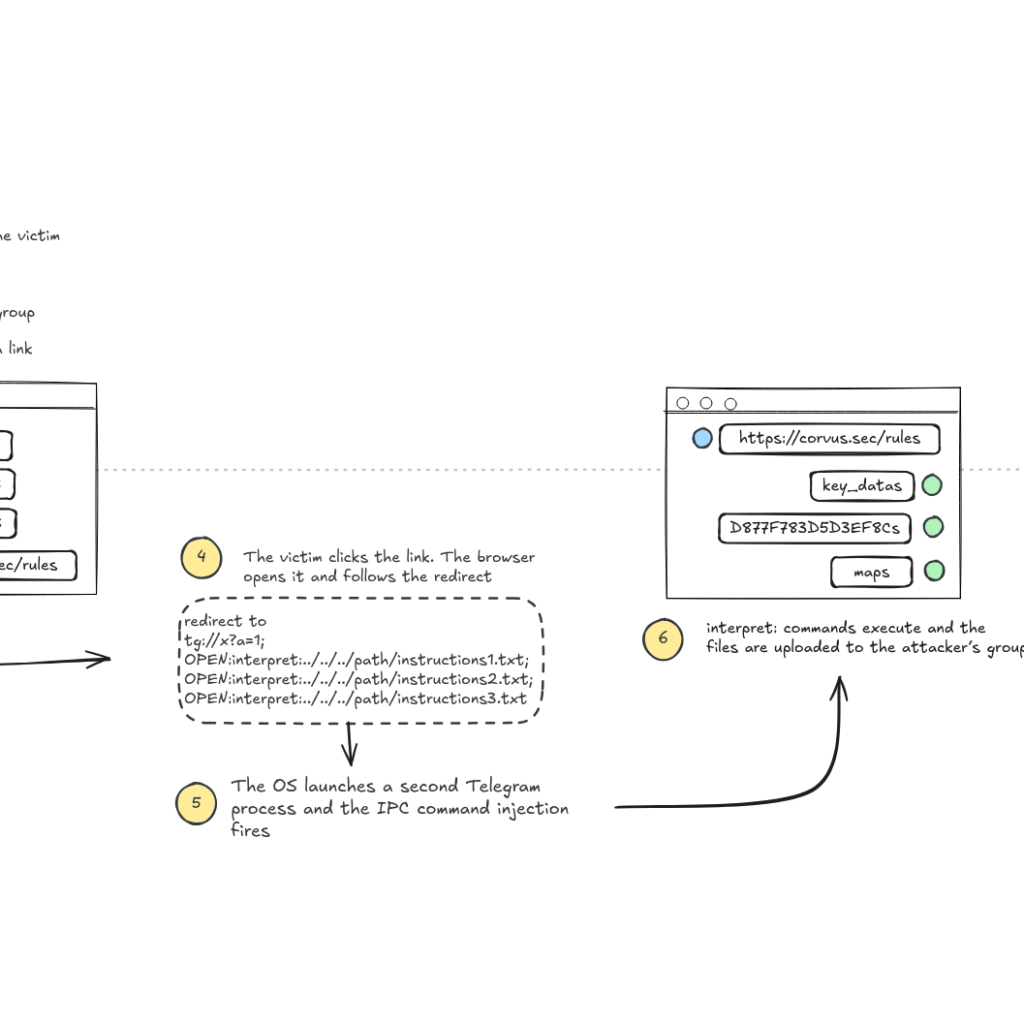
Command Injection119 Telegram Desktop: one-click account takeover via IPC injection
BeakSec's CVE-2026-107181: Telegram Desktop through 7.2.8 handed clicked links to the running instance over a local socket and never escaped the semicolon…
Command Injection119 BeakSec's CVE-2026-107181: Telegram Desktop through 7.2.8 handed clicked links to the running instance over a local socket and never escaped the semicolon…
AnyDesk76 AnyPwn is a pre-approval remote code execution bug in AnyDesk Linux 8.0.2. The session protocol's mode-5 handler trusts a remote payload length,…
RCE285 Mobeta patch-diff of VMSA-2026-0006: vCenter 8.0.3 syslog dynafile traversal (CVE-2026-59310) and SASL SRP A=N auth bypass (CVE-2026-59309), both pre-auth 9.8. Templates, Ghidra,…
RCE342 CVE-2026-65660 SharePoint EditingPageParser bypass via RegisterDirective.GetHtml quote rewrite, XamlServices memshell, and ToolPane on AddGallery.aspx for pre-auth RCE when anonymous view is on.…
kernel549 Connor McGarr on ETW’s undocumented SecurityTrace bit: QUERY wants Antimalware-PPL, STOP does not, and a user-mode ControlTrace hook lets admin consume Threat-Intelligence…
kernel604 Asim Manizada’s four Linux LPEs: DirtyAH6, TUNderflow, PPPoEject, DiagSpill. Decade-old bugs, userns for three, DiagSpill needs only SCTP. Patch 5.10.270 / 6.6.157…
Exploit Development607 Gen Threat Labs: CVE-2026-51990 one-click RCE in Sogou IME — sgbiz: argument injection, skincenter CEF, Chromium 80 unsandboxed. UNC3569 dropped GRAYRABBIT in…
Exploit Development978 Pruva REPRO-2026-00354: CVE-2026-85706 unauthenticated GitLab file read via commits.json defeating Workhorse, file.path sink, %zz echo, Files API trailing-slash variant. CVSS 10.0. Patch…
Exploit Development470 Jonathan Johnson’s first public RE of WESP on Insider 29661: wesp.sys + espclient.dll, EspFilterPort, WESP://Permission and AM-PPL, process-create queues, a working consumer…
Exploit Development636 QED’s CVE-2026-19174: three constants overflow in V8’s wasm deserializer, 102.4 MiB instead of 921.6, overlapping RWX JIT, renderer RCE without a heap-sandbox…
Exploit Development1k Acronis TRU: Red Heron turned CVE-2026-60004 into a Gitea steal-and-pivot factory within days of the PoC, hit five countries, and dropped JITTERLY…
Android403 Natalie Silvanovich’s Part 3: the Pixel 9 0-click was person-weeks, not a miracle. Rare codecs on transcription, missing seccomp, kASLR dead since…