Bypassing249 Writing Optimized Windows Shellcode (old but gold)
A deep dive into crafting ultra-compact Windows shellcode that walks the PEB, resolves APIs via export hashing, and runs fully self-contained without…
Bypassing249 A deep dive into crafting ultra-compact Windows shellcode that walks the PEB, resolves APIs via export hashing, and runs fully self-contained without…
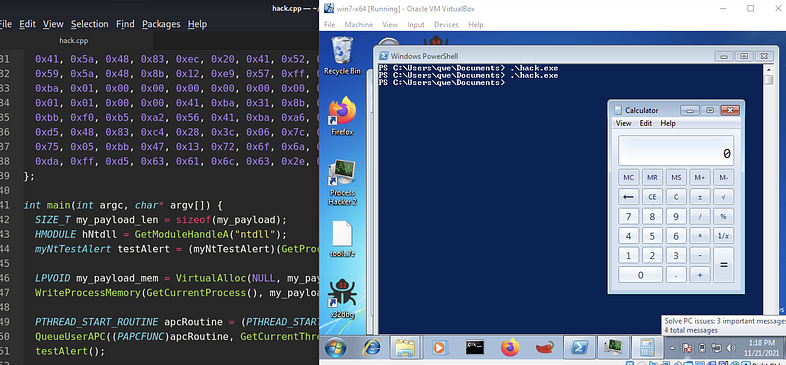
APC335 The EarlyBird APC technique creates a trusted process in a suspended state, allocates memory for shellcode, and writes the payload. It then…
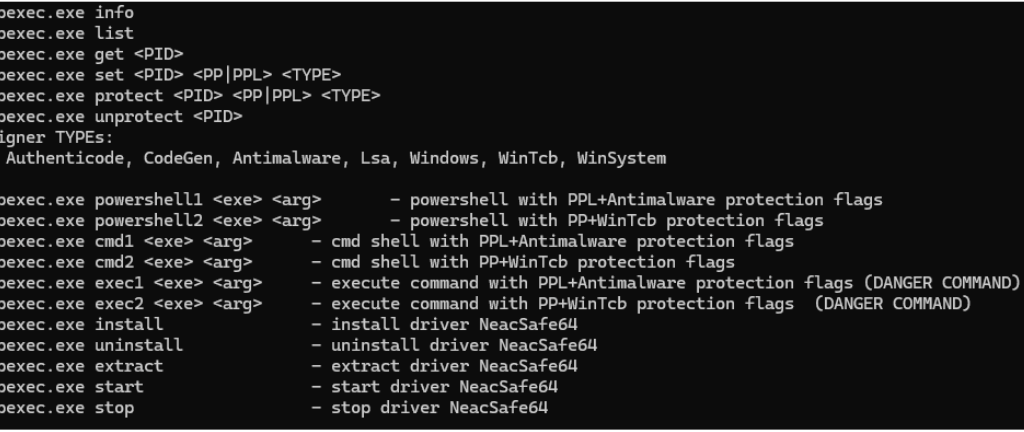
AV252 PPLControlShells (the ppexec console tool) is a native Windows PP/PPL experimentation and control utility (x64)designed to help researchers understand, test, and demonstrate…
A PoC/demo demonstrating code injection via COM (using the IRundown::DoCallback() mechanism) to execute a payload in the context of a selected process, including lsass.exe (or any…
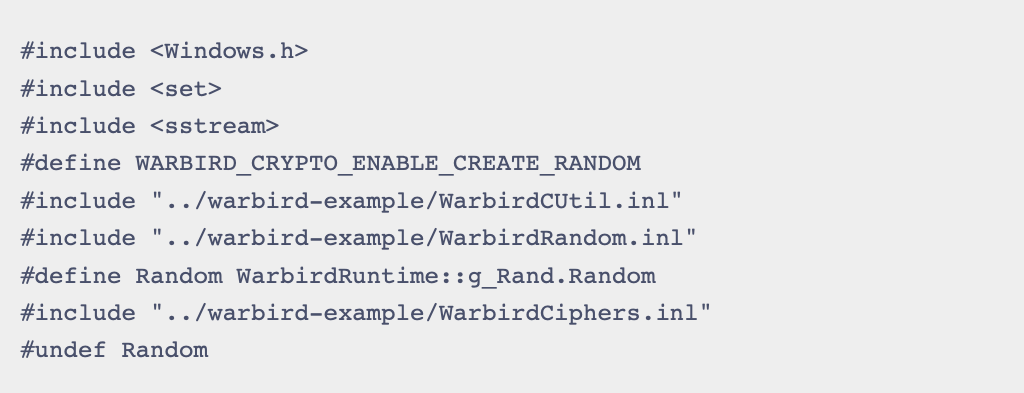
Bypassing288 The article demonstrates an EDR bypass by using an undocumented Warbird interface to stealthily load shellcode.
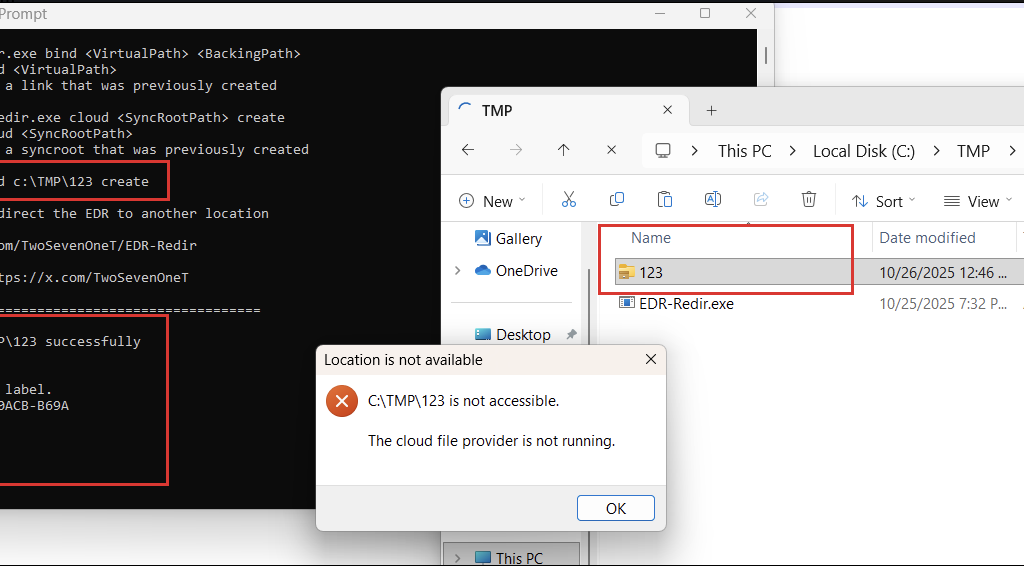
BYOVD243 the technique of exploiting the Bind Filter driver (bindflt.sys) to redirect folders containing the executable files of EDRs to a location that I completely…
AV388 av-edr-kill is a BYOVD (Bring Your Own Vulnerable Driver) proof-of-concept whose goal is to terminate security-product processes (AV/EDR), including Protected Process Light…