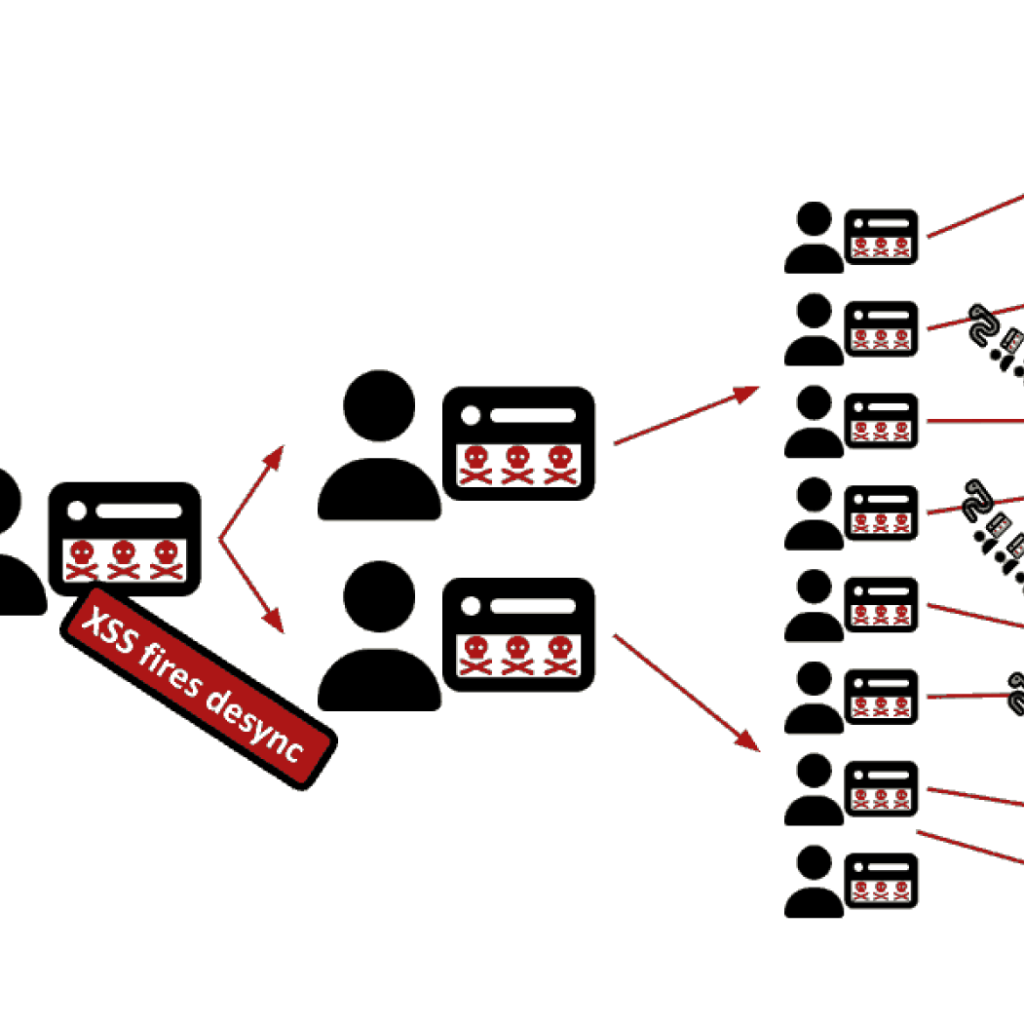
Application Security781 CRLF-Powered Desync Attacks: Beheading HTTP Streams
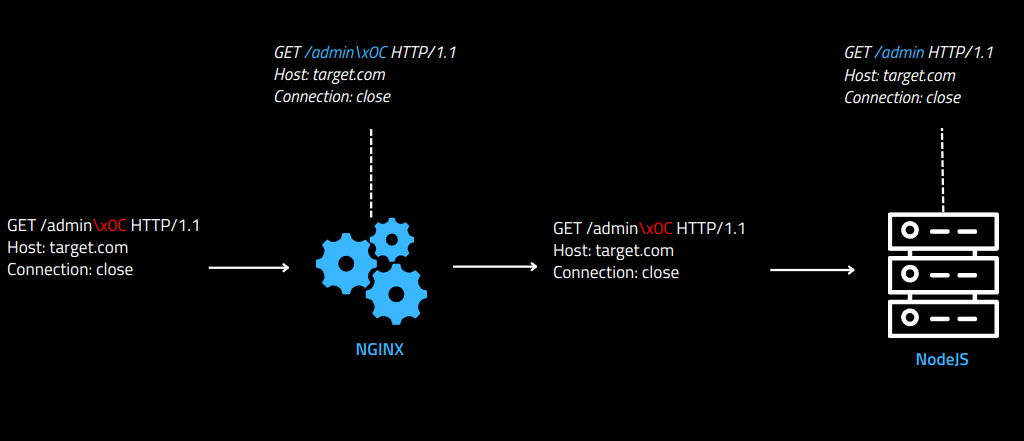
HTTP header injection has been under-rated for twenty years. This research shows how one injected CRLF sequence in an Nginx-normalised path escalates…
Application Security781 HTTP header injection has been under-rated for twenty years. This research shows how one injected CRLF sequence in an Nginx-normalised path escalates…
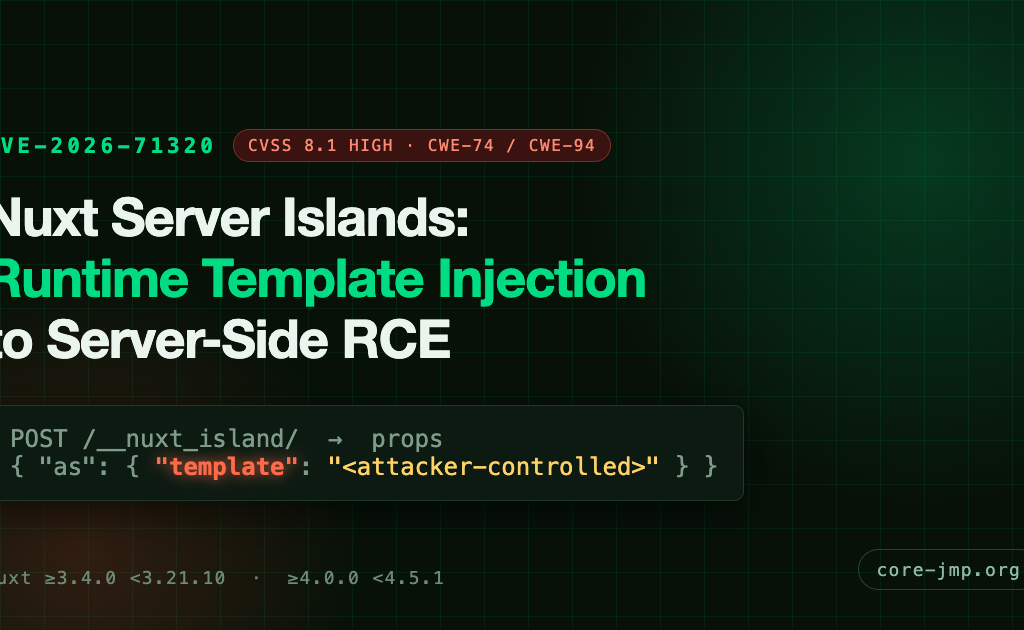
Application Security465 CVE-2026-71320 lets an attacker inject a template key into Nuxt server island props and have Vue's runtime compiler execute it inside the…
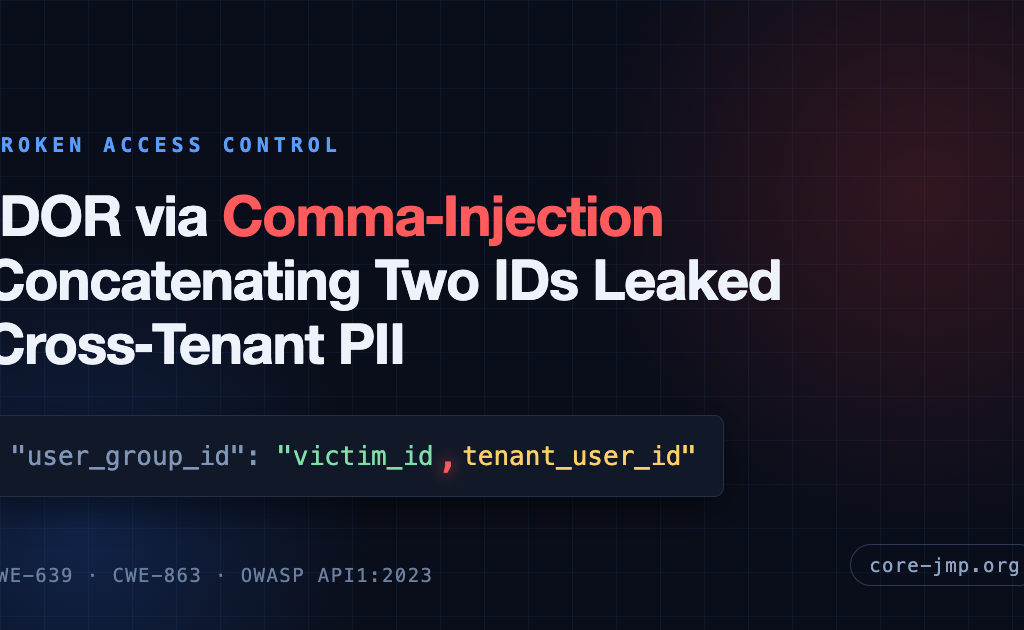
Application Security312 A multi-tenant document vault enforced a real server-side tenant-ownership check on its permission-grant endpoint - and it was still bypassable. The authorization…
Application Security642 A deep tour of HTTP parser inconsistencies: how trim/fold/header disagreements between Nginx, WAFs, caches and frameworks (Node.js, Flask, Spring Boot, PHP) enable…
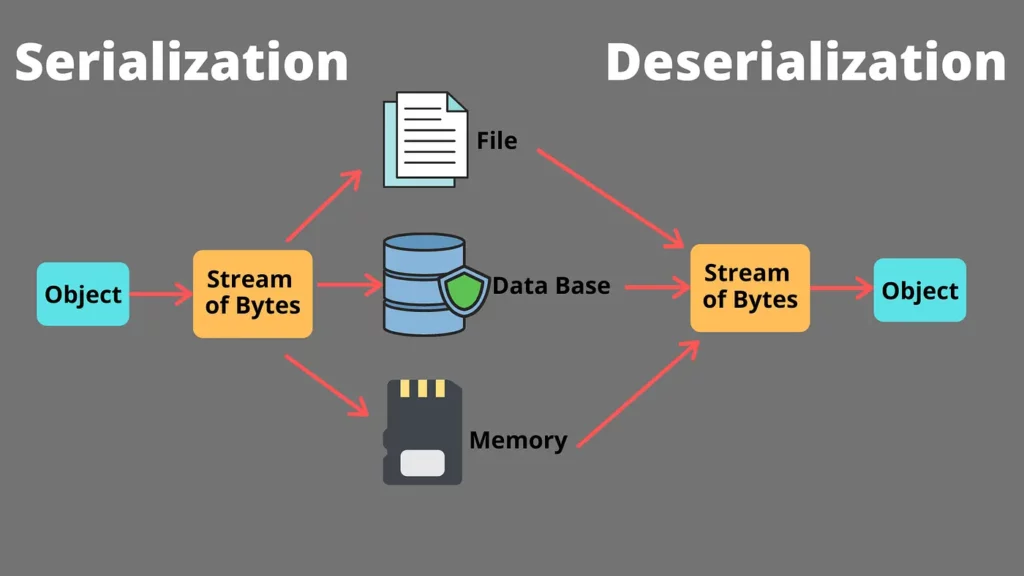
Application Security286 CVE-2025-49113 is a critical authenticated remote-code-execution flaw in Roundcube webmail — the default in cPanel, Plesk, and many hosting stacks — caused…
Application Security301 A practical, security-engineering view of the essential iOS hardening steps every iPhone user — and especially high-risk targets — should apply: Lockdown…